
 #1
Firmware extraction, unpacking, emulation, vulnerability discovery, and binary analysis tools.
Kitploit recommended
 eyjhb/blackvue-cve-2023
BlackVue DR750 CVE CVE-2023-27746 CVE-2023-27747 CVE-2023-27748
 joehquak/mi8e5-unlocker-by-cve-2026-43499
Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
 infobyte/ezviz_lan_rce
PoC exploits and Docker build environment for CVE-2023-34551 and CVE-2023-34552 targeting EZVIZ IP cameras, with DEF CON 31 Hardware Hacking Village…
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
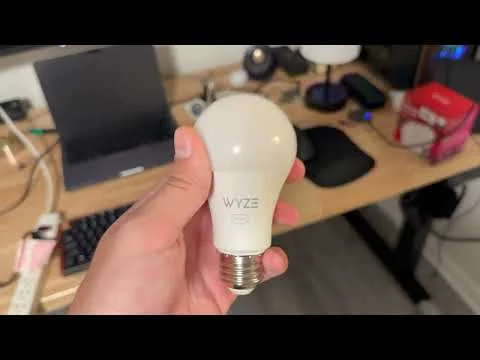 nickdaria/wyze-bulb-color-pwned
No-open firmware exploit for the Wyze WLPA19CV2 color bulb
 elbertavares/routers-exploit
Proof-of-concept exploits for TP-Link routers, including remote command execution and authentication bypass vulnerabilities.
 cryptoadvocate/dcsgonefirm
The firmware engineering home of the Circuit Crafters first electronic badge project.
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
 vl4dr/cve-2024-42642
Proof-of-concept exploits for three vulnerabilities in Crucial MX500 SSD firmware update mechanism, enabling buffer overflows and potential code…
 wack0/dubiousdisk
The Porygon-Z that's super effective against Secure Boot! (CVE-2022-30203, CVE-2023-21560, CVE-2023-28269, CVE-2023-28249, and more...)
 gopartner/realme-c53-unlock-root
Bootloader unlock (CVE-2022-38694) & root guide for Realme C53 / RMX3760 (Unisoc T612)
 bahaabdelwahed/st
IoT protocol threat detection tool that scans devices for vulnerabilities, searches CVEs/PoCs, analyzes firmware, and monitors MQTT/UPnP traffic to…
 exifdev/prineo_re
Reverse engineering of the engine powering the PriPara games on arcade.
 unsignedchad/bcm4360-wpa3
wpa3 functionality for the wifi chip in a 2014 macbook pro
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
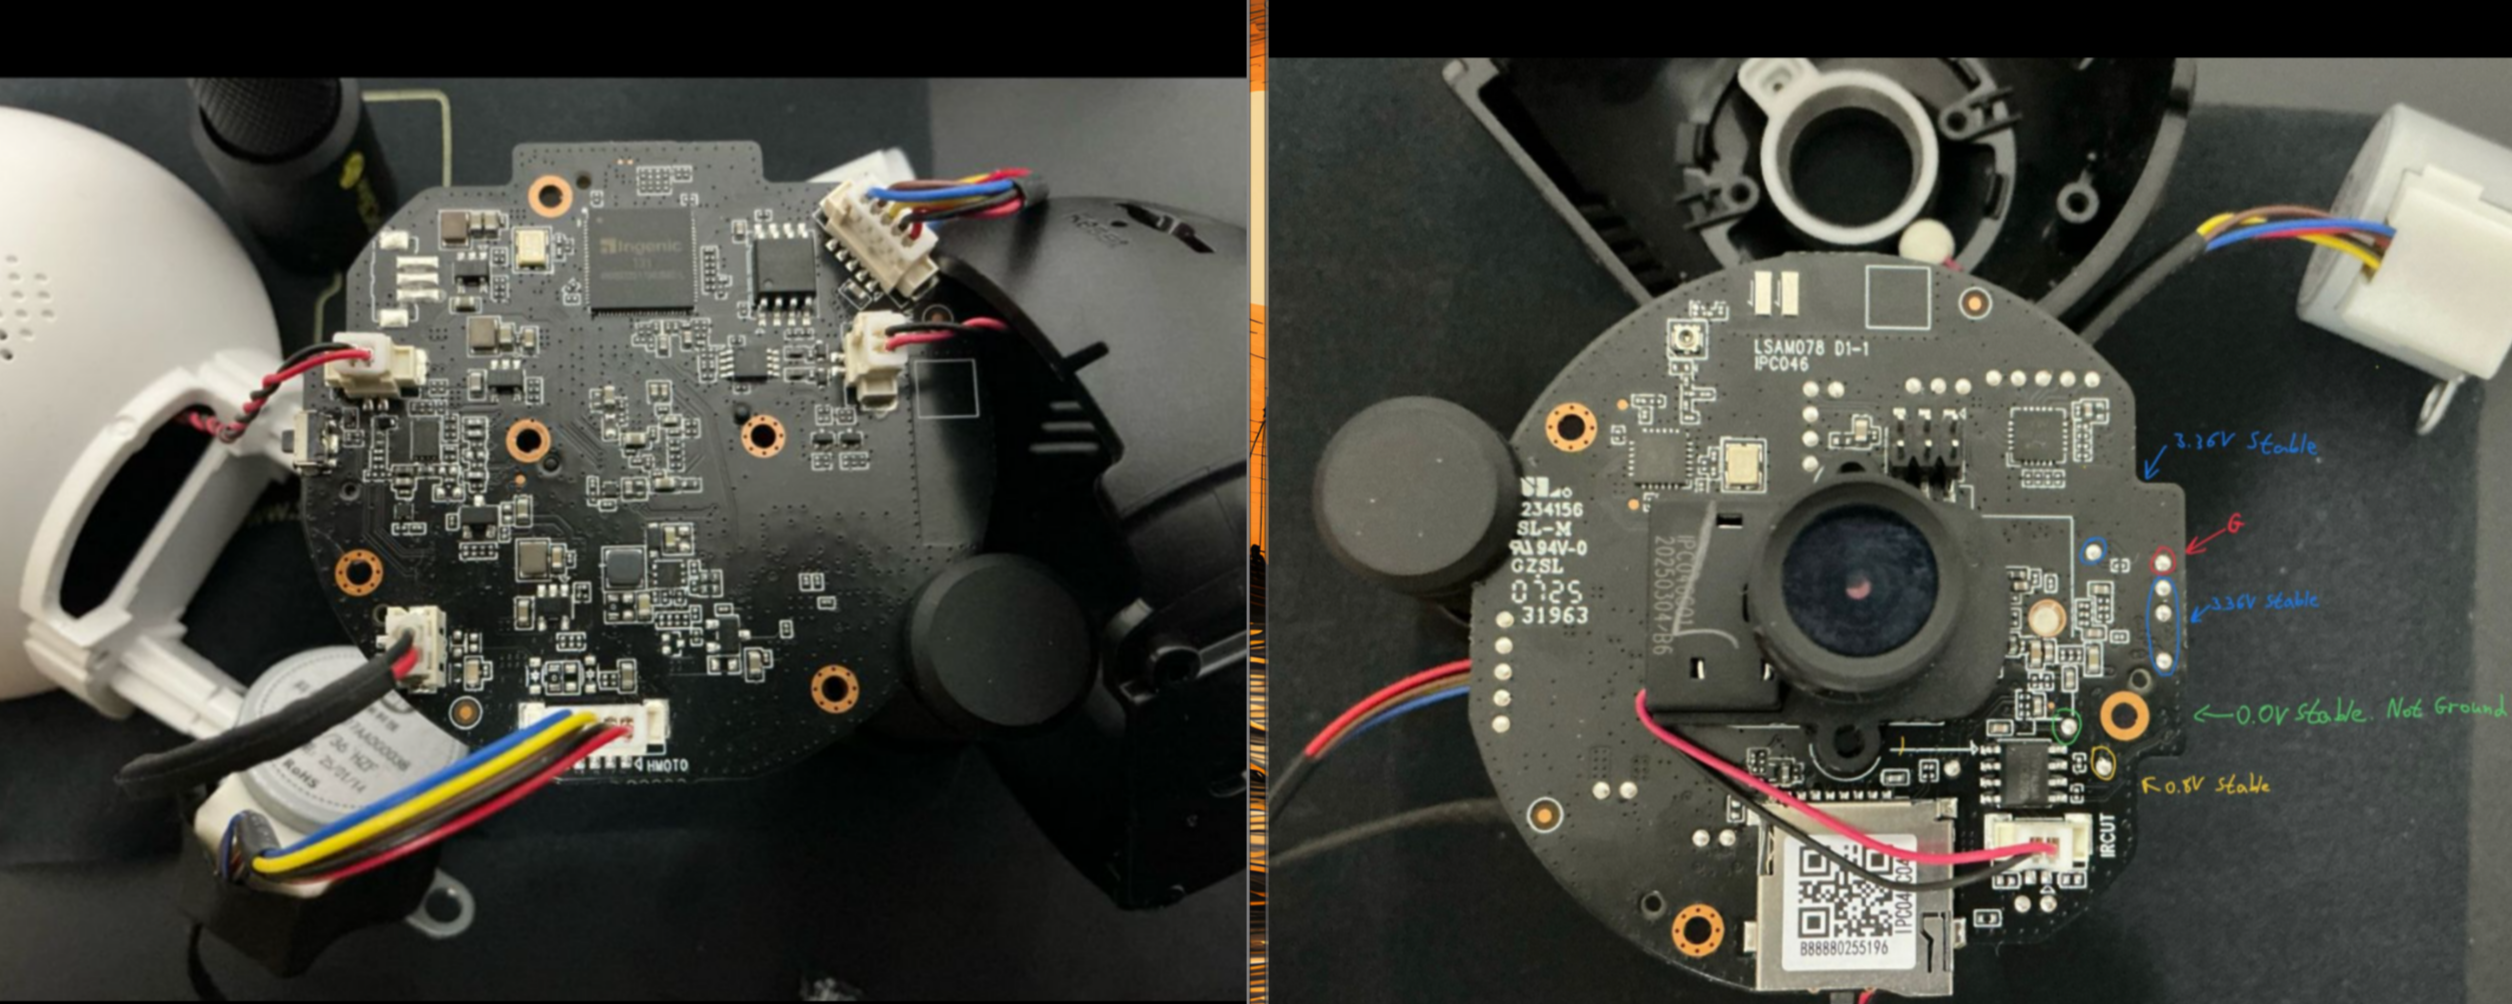 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…








