
 #1
Cybersecurity research, materials, labs, and learning paths, including CTFs and curated educational resources.
Kitploit recommended
 cobalt-strike/eden
A PoC UDRL for Cobalt Strike built with Crystal Palace that combines Raphael Mudge's page streaming technique with a modular call gate (Draugr)
 kingsabri/jwtear
Modular command-line tool to parse, create and manipulate JWT tokens for hackers
 owasp/owasp-mcp-governance-and-risk-project
Project focused on governance and risk in application security, providing resources and frameworks for security maturity and risk management.
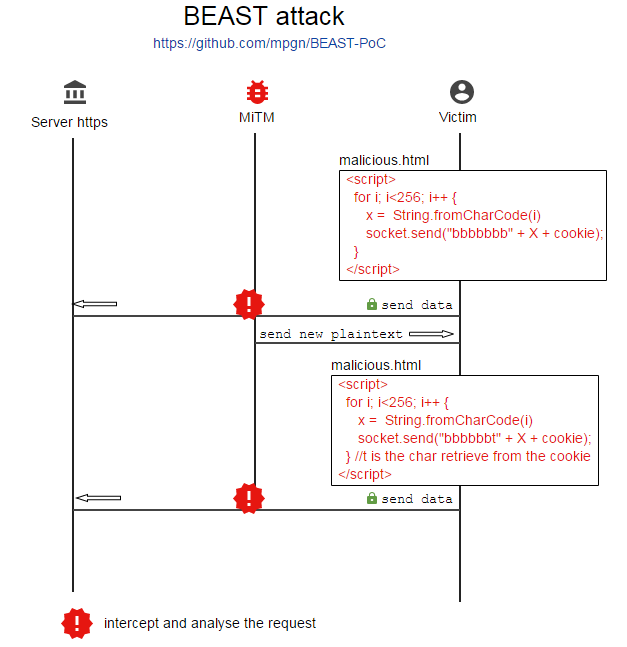 mpgn/beast-poc
:muscle: Proof Of Concept of the BEAST attack against SSL/TLS CVE-2011-3389 :muscle:
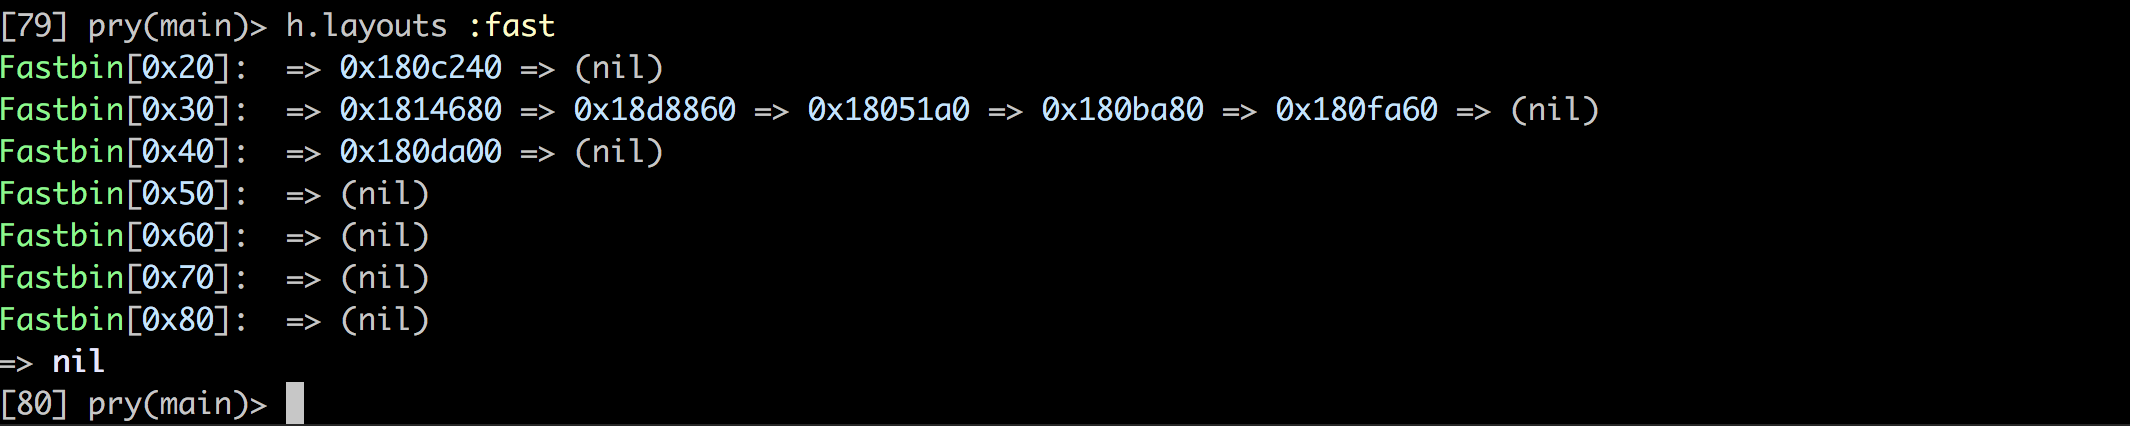 david942j/heapinfo
An interactive memory info for pwning / exploiting
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 heptagrams/heptagram
This project is used to collect the EXP/POC disclosed on the Internet and provide project support for Heptagram security team.
 ashemery/anti-forensics
A Repository to Track Anti-Forensic Techniques

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 vladko312/research_successful_errors
Whitepaper introducing Error-Based and Boolean Error-Based Blind techniques for SSTI and Code Injection, with universal payloads for six programming…
 haplessidiot/ageverificationbypass
Bypass age verification service from redhat
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 jonwiggins/xmloxide
A pure Rust reimplementation of libxml2
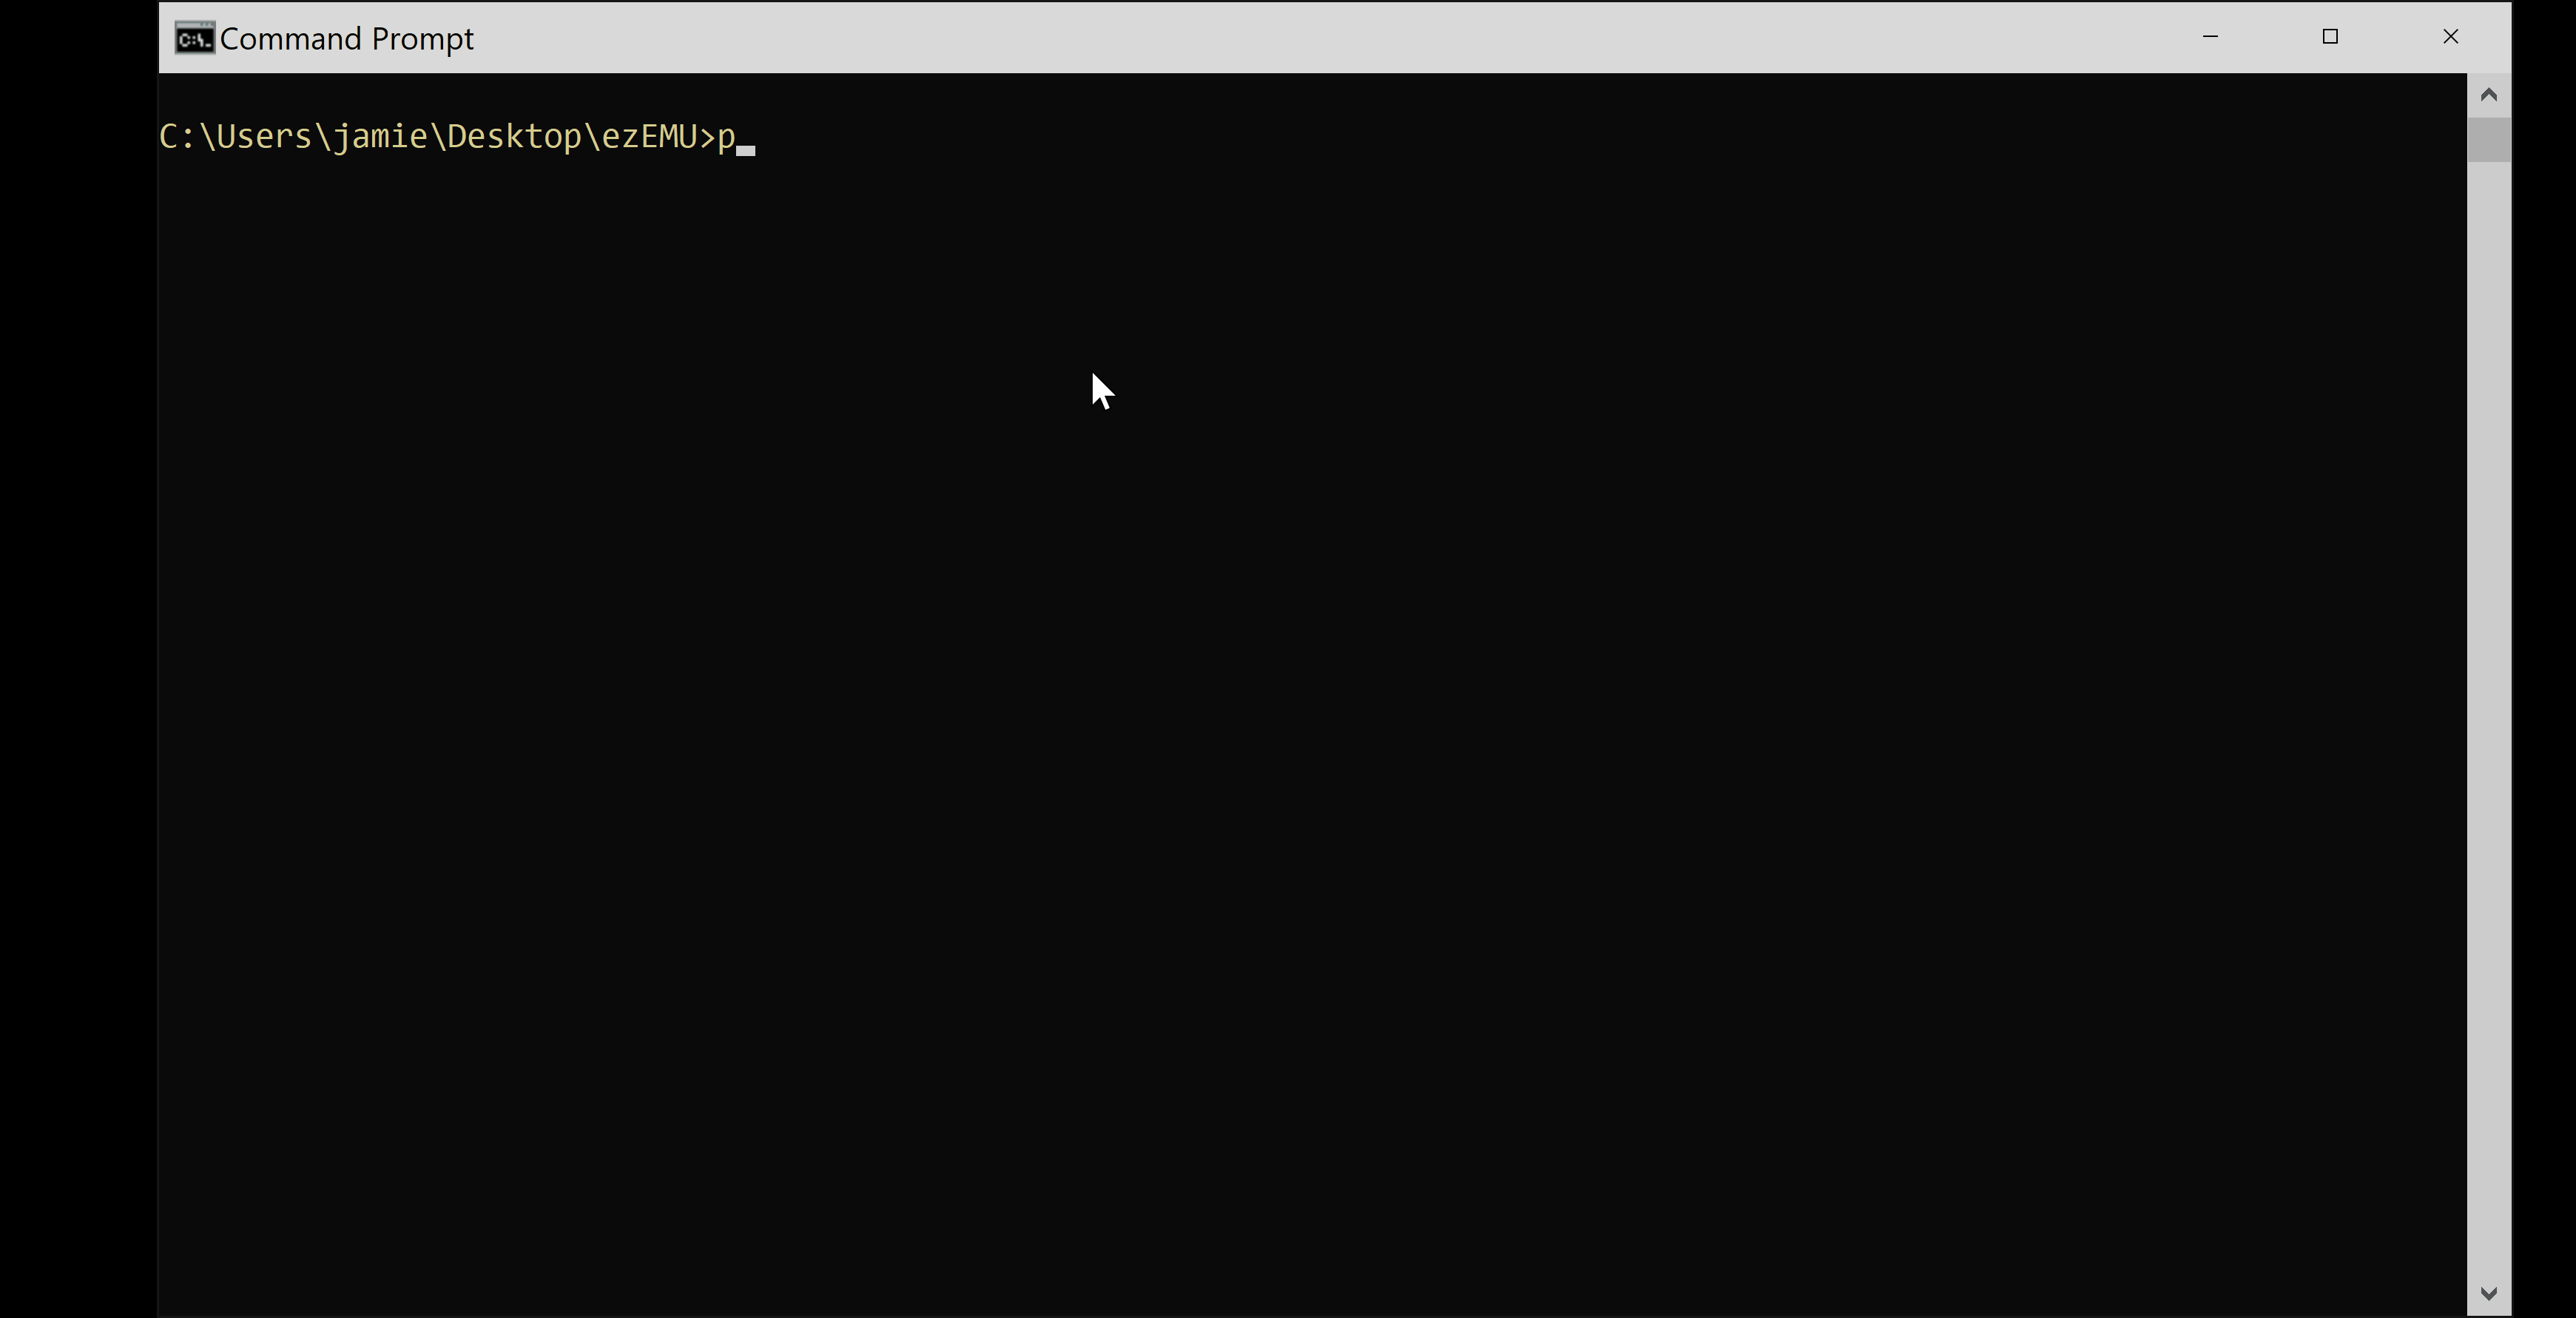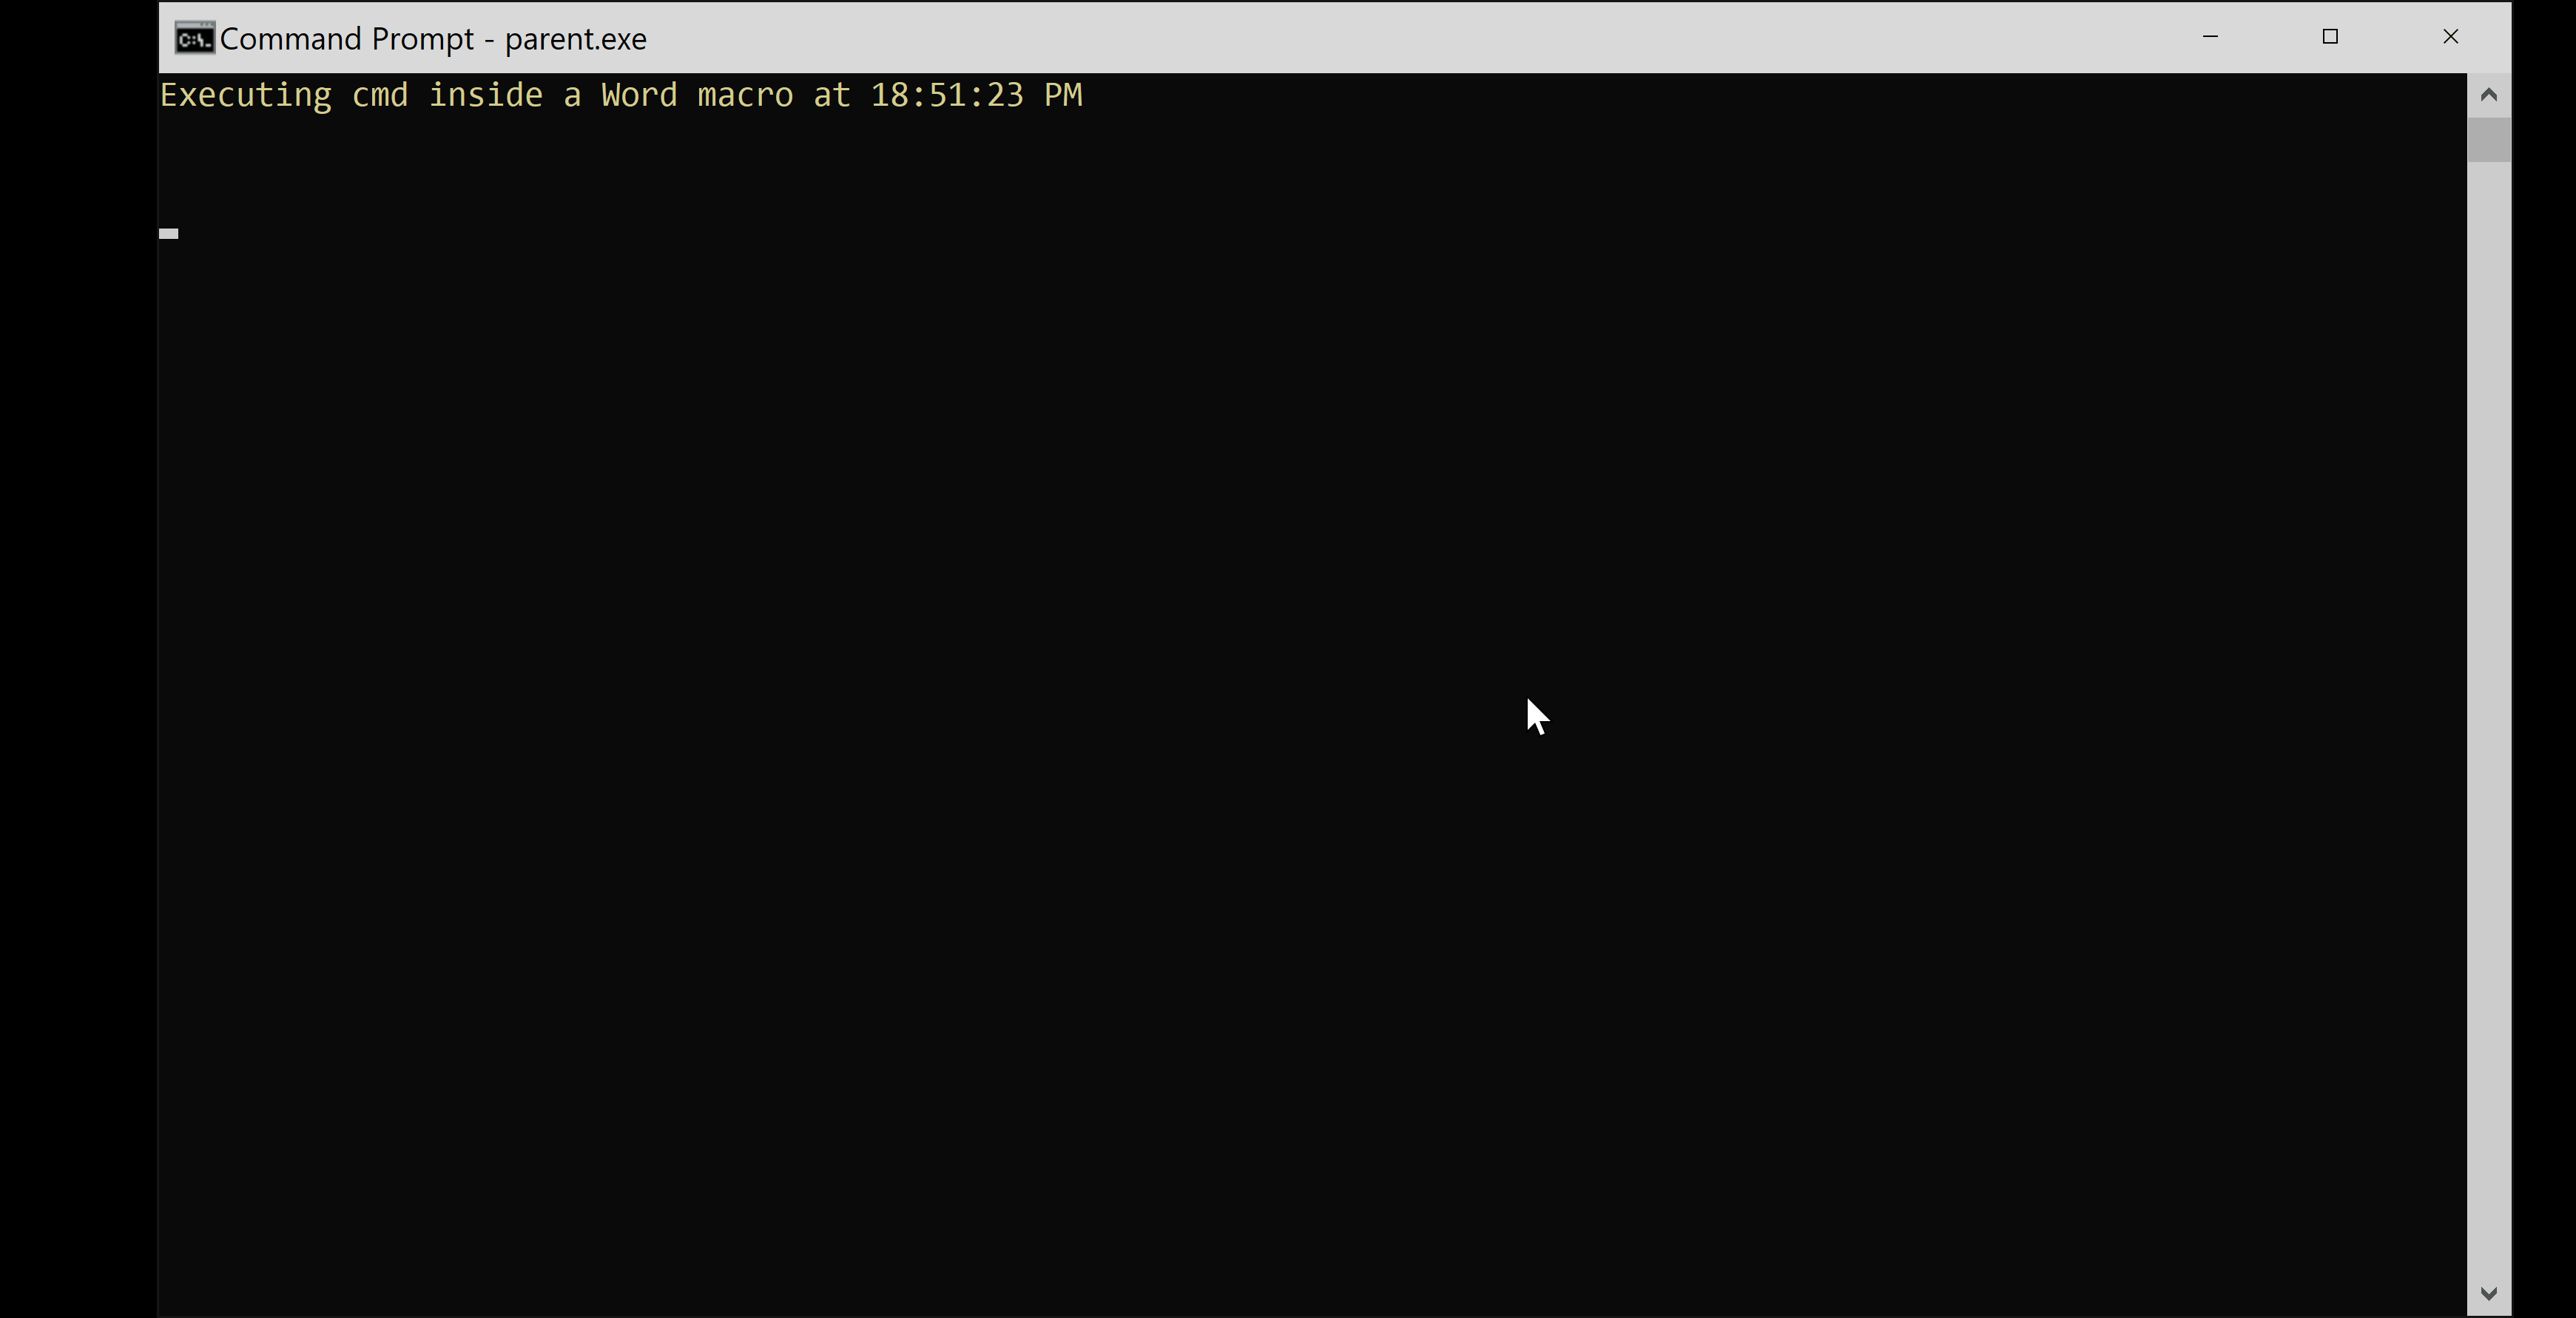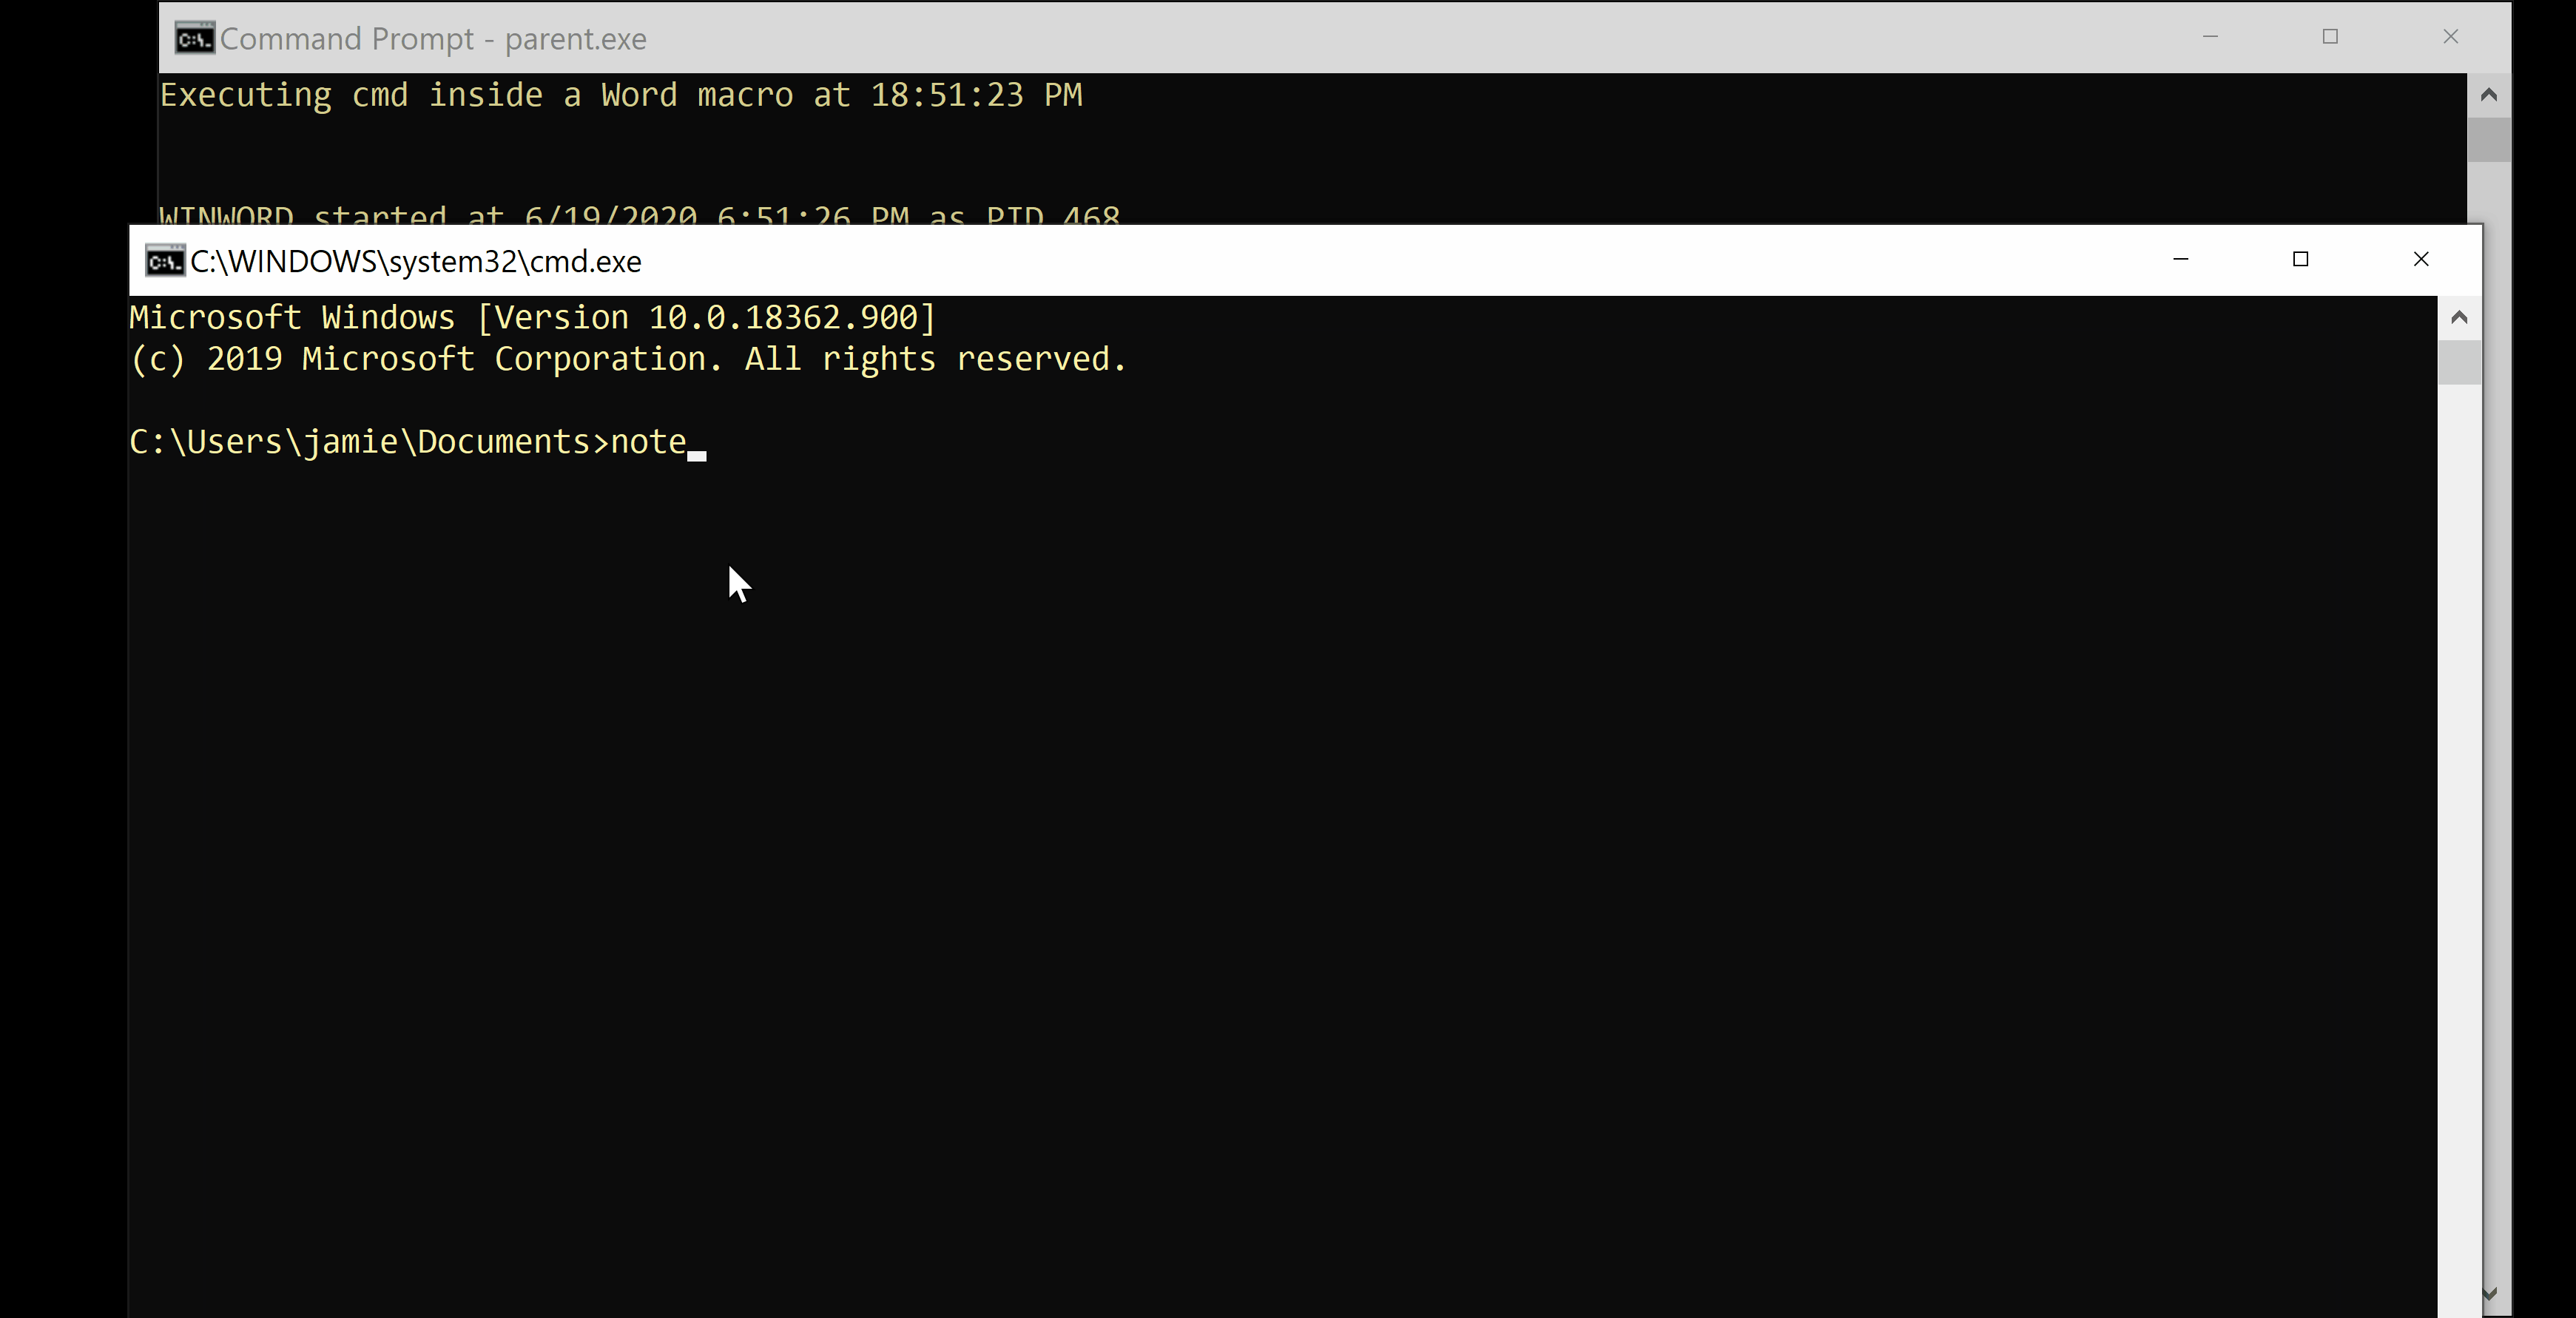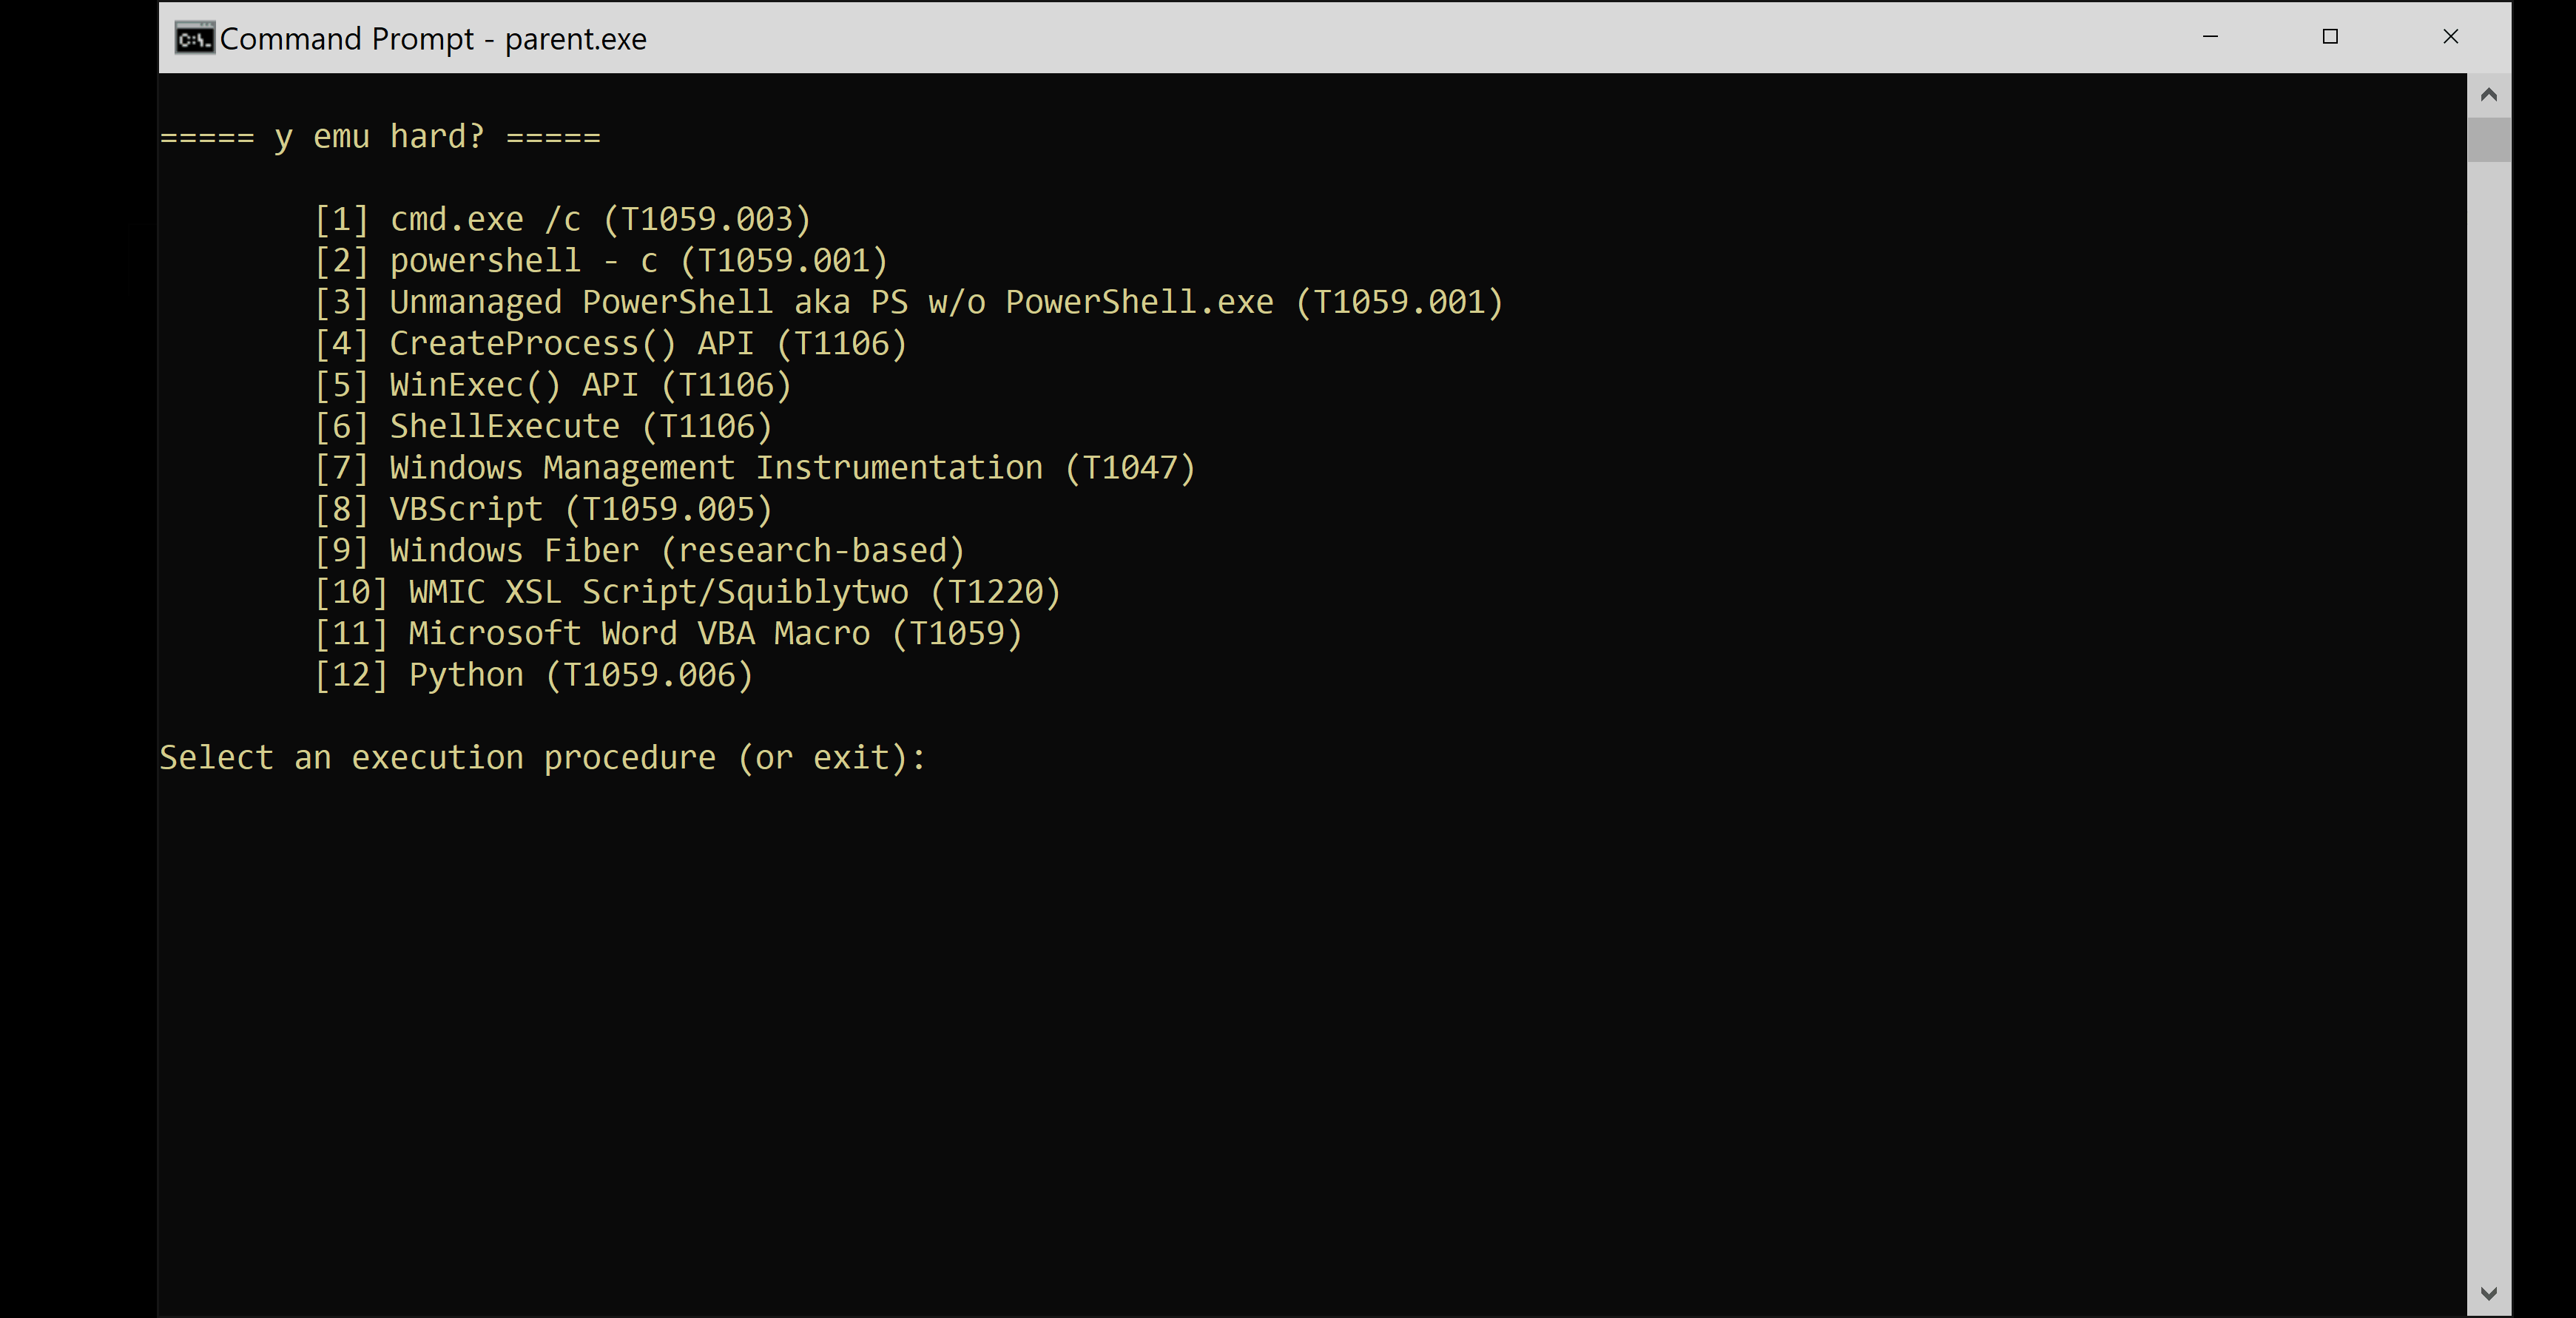 jwillyamz/ezemu
See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 opsxcq/exploit-cve-2016-6515
OpenSSH remote DOS exploit and vulnerable container
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 giancarlolelli/quantum
This repository contains the code and submission detail for the QDay prize challenge by https://www.projecteleven.com/








