
 #1
Cybersecurity research, materials, labs, and learning paths, including CTFs and curated educational resources.
Kitploit recommended
 threatcl/threatcl
Documenting your Threat Models with HCL
 rizemon/exploit-writing-for-oswe
Tips on how to write exploit scripts (faster!)
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 cybercx-sta/purpleops
An open-source self-hosted purple team management web application.
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 trailofbits/trailmark
Build and query a graph database representation of source code
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
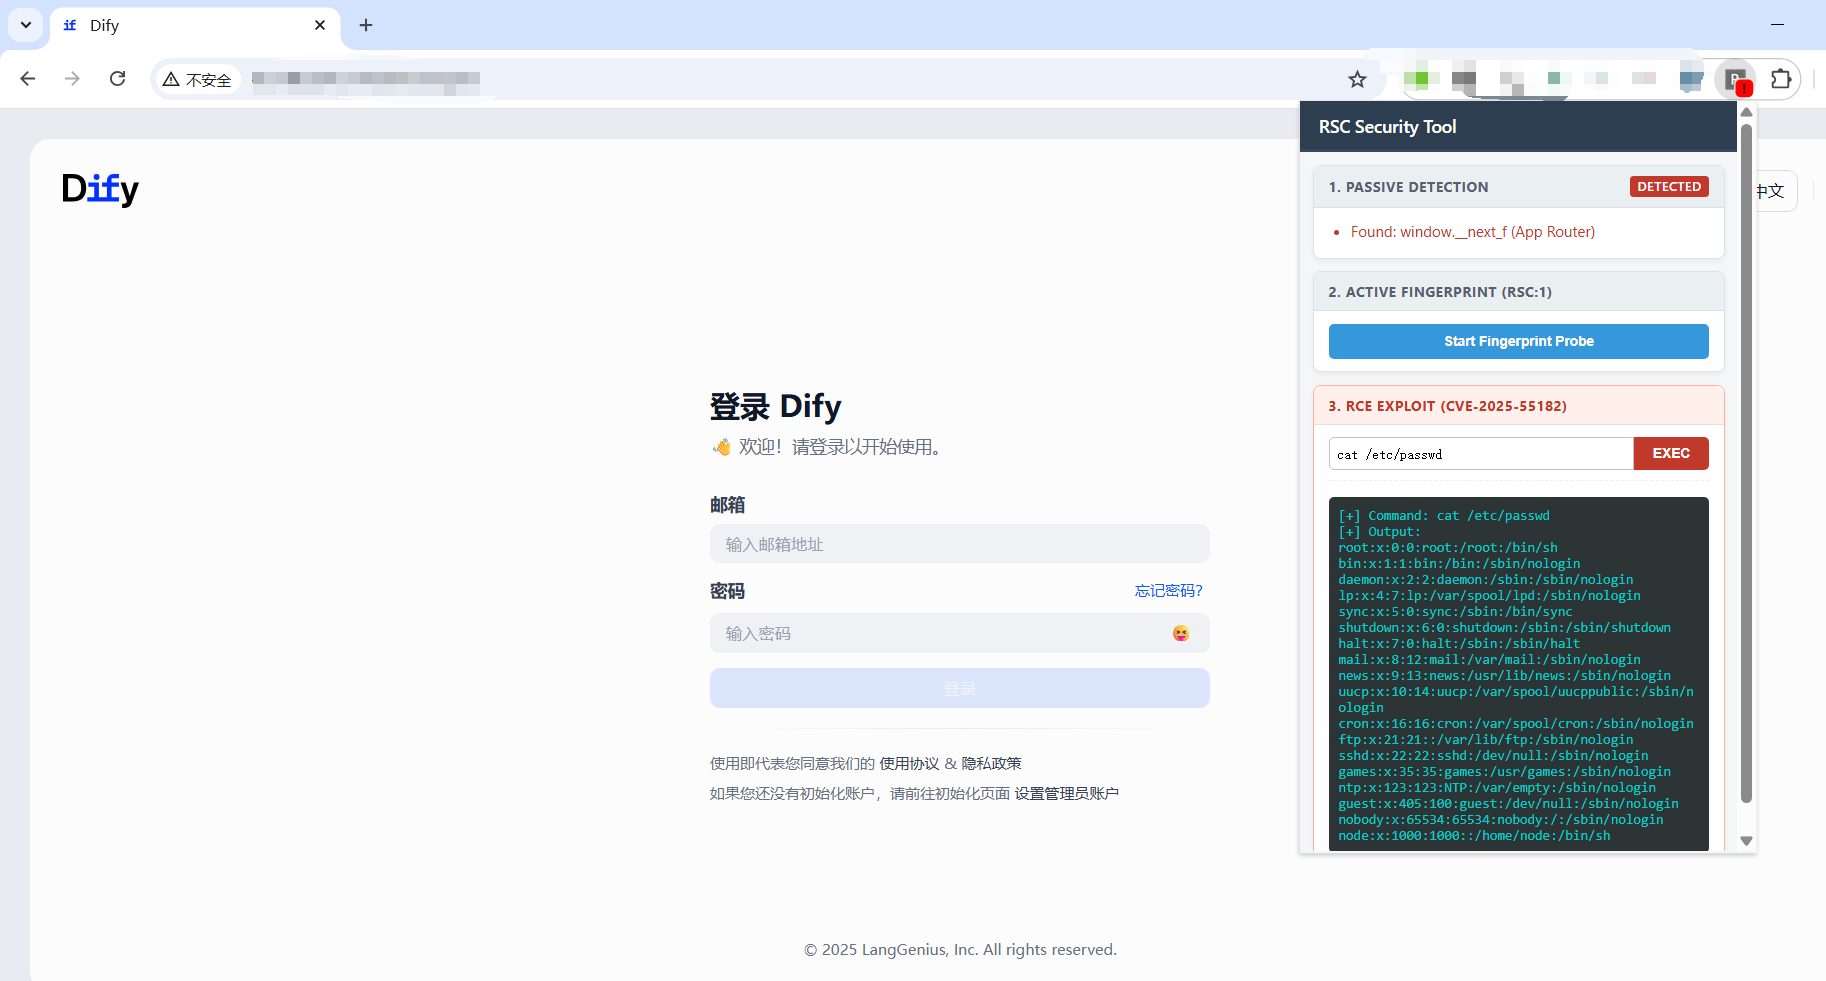 mrknow001/rsc_detector
Supports RSC fingerprinting and exploitation of the React component vulnerability CVE-2025-55182.
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 brannondorsey/dns-rebind-toolkit
A front-end JavaScript toolkit for creating DNS rebinding attacks.
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 zerkereod/krakenhashes
Distributed password cracking platform coordinating GPU/CPU agents via Hashcat for high-speed hash recovery, with real-time job management,…
 harendra-shakya/smart-contract-attack-vectors
A curated list of smart contract attack vectors
 edr4/xss-bypass-filters
Curated XSS payload collection and filter-bypass cheat sheet: WAF-specific evasion, JS/HTML injection vectors, encoding tricks, DOMPurify and…
 r-s0n/ars0n-framework
Modular bug bounty hunting framework automating reconnaissance, subdomain enumeration, and vulnerability scanning with an educational focus to help…








