
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended
 d4rksystem/vmwarecloak
A PowerShell script that attempts to help malware analysts hide their VMware Windows VM's from malware that may be trying to evade analysis.
 dinosn/fastjson-jsontype-rce-lab
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 nccgroup/umap2
Umap2 is the second revision of NCC Group's python based USB host security assessment tool.
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
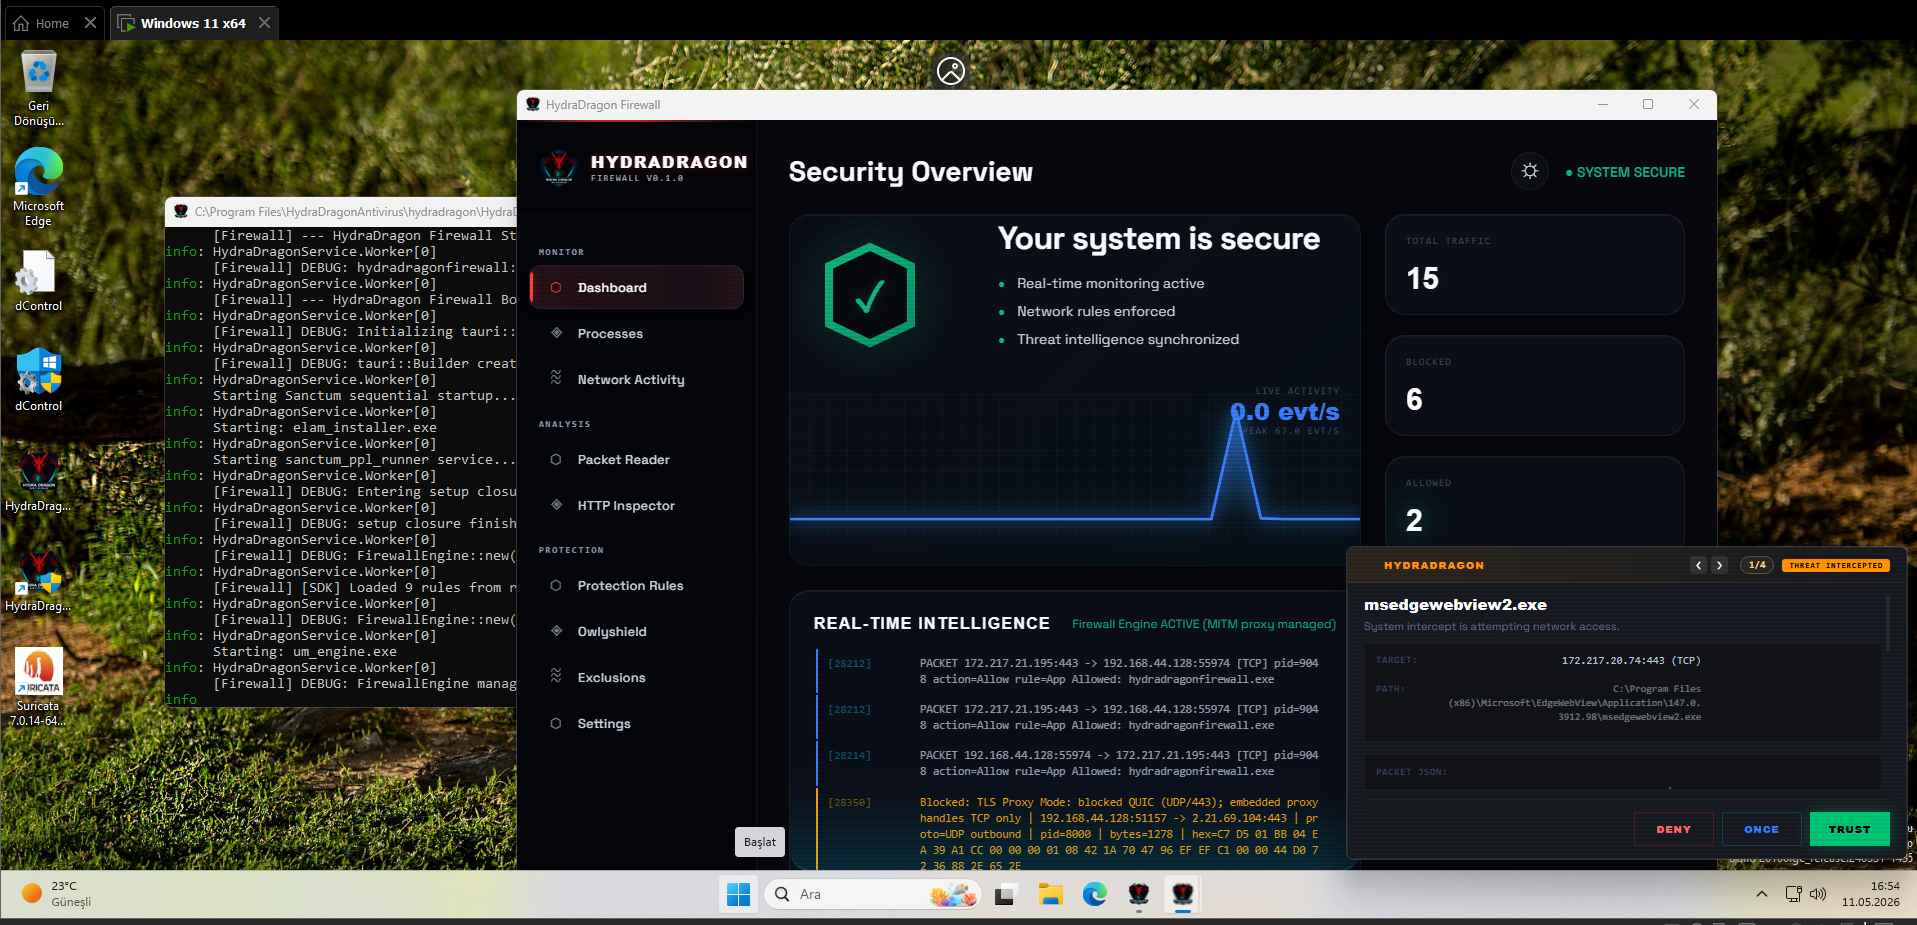 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 mfthomps/resim
Reverse engineering software using a full system simulator
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL








