#2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 cisco-ai-defense/skill-scanner
Security Scanner for Agent Skills
 ashishb/android-security-awesome
A collection of android security related resources
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
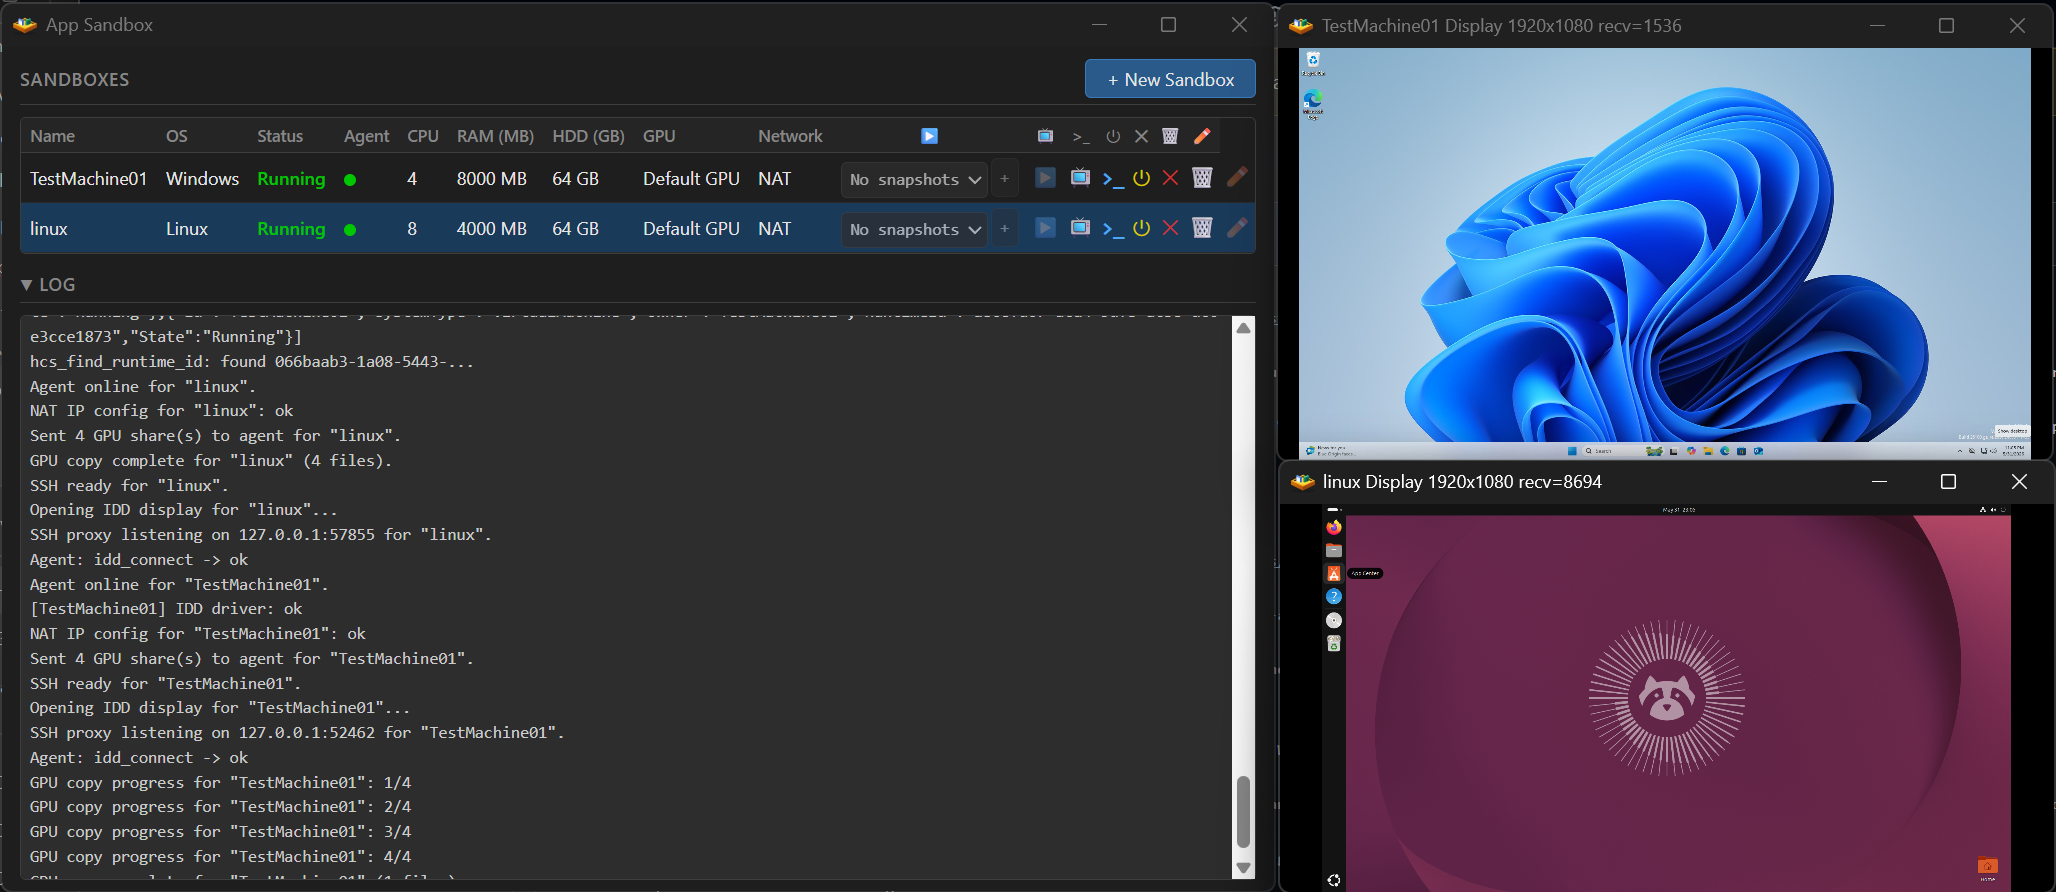 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 microsoft/mxc
Policy-driven, layered isolation and containment
 angr/angr
A powerful and user-friendly binary analysis platform!
 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
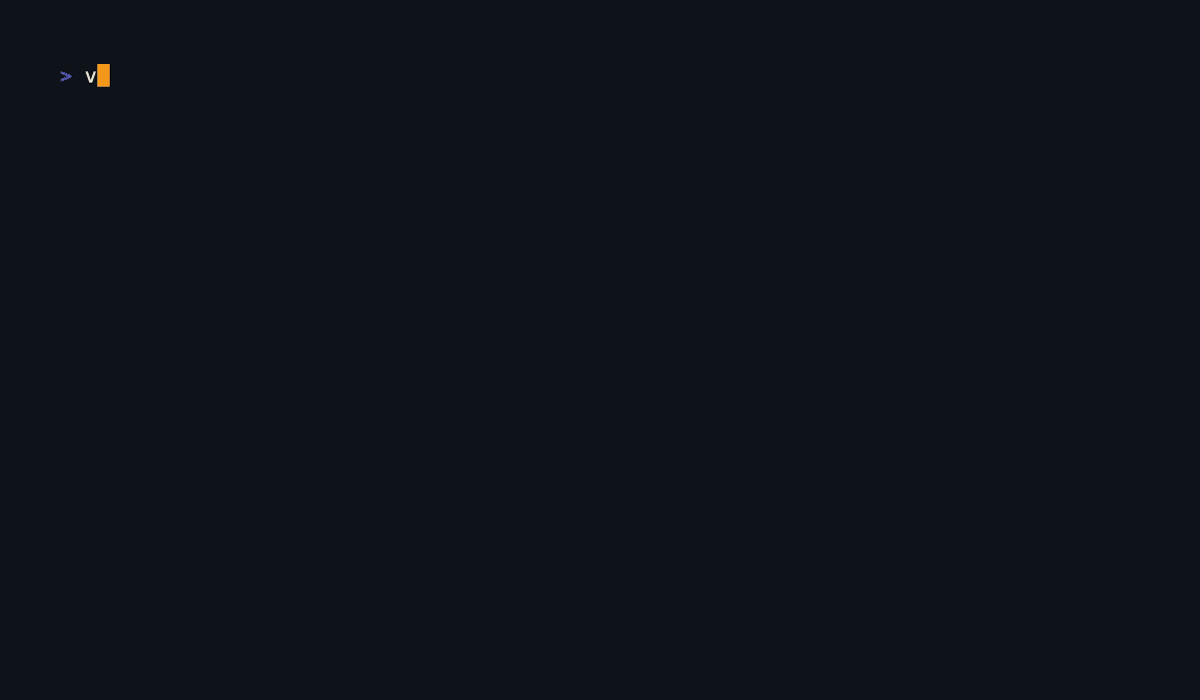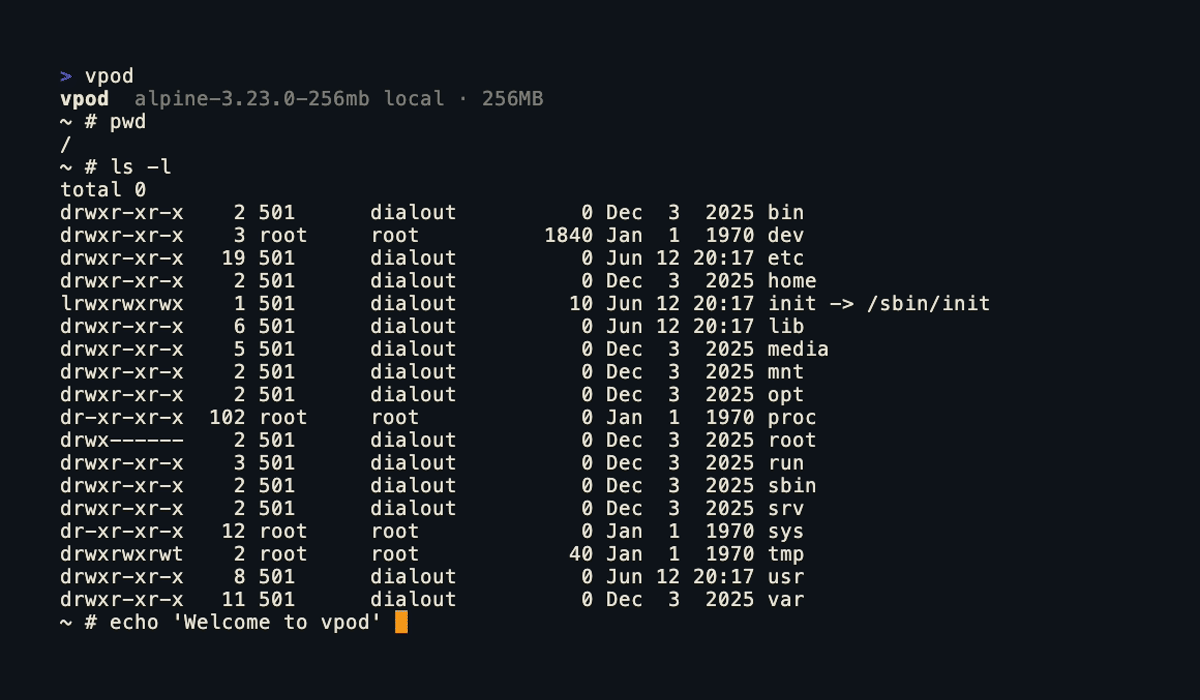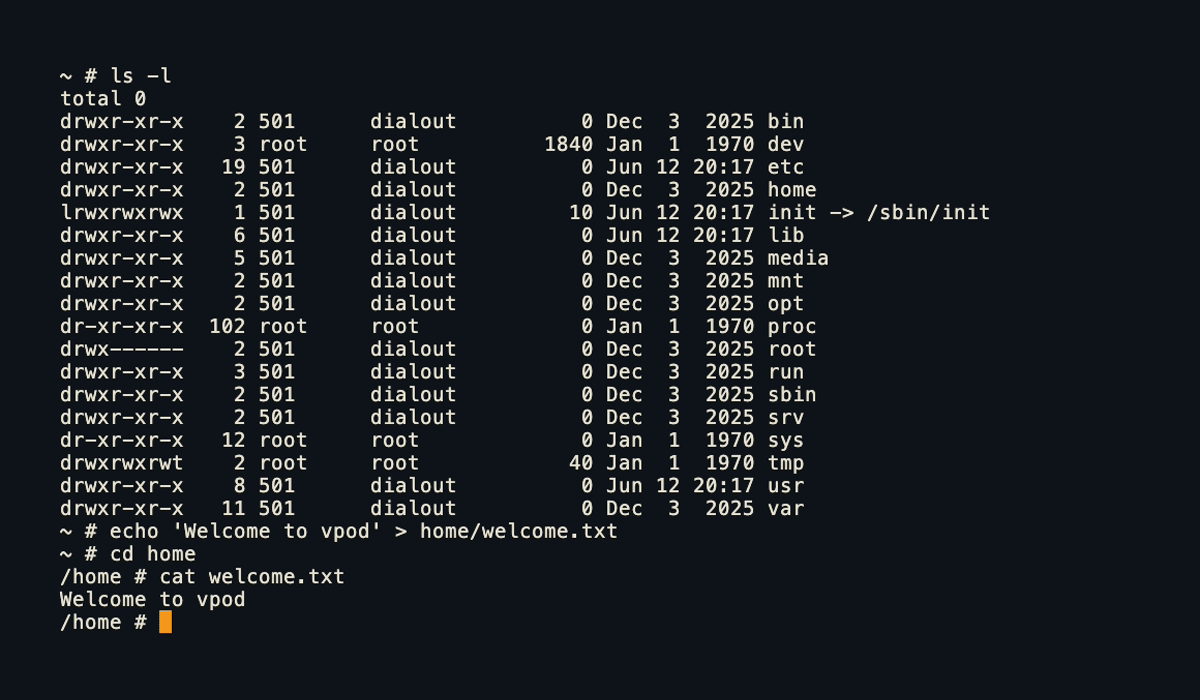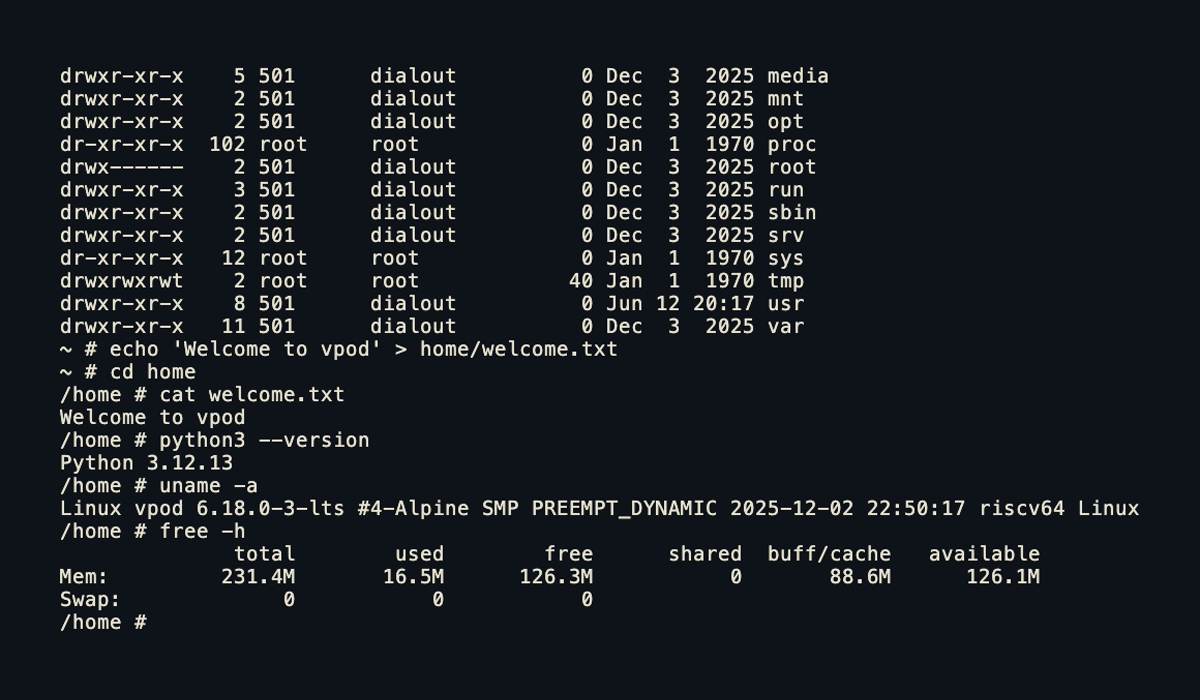 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 cea-sec/miasm
Reverse engineering framework in Python
 cert-polska/karton
Distributed malware processing framework based on Python, Redis and S3.
 openedx/codejail
Secure code execution