#1
Tools for discovering subdomains and DNS records associated with target domains.
Kitploit recommended

 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 am0nt31r0/osint-search
Useful for digital forensics investigations or initial black-box pentest footprinting.
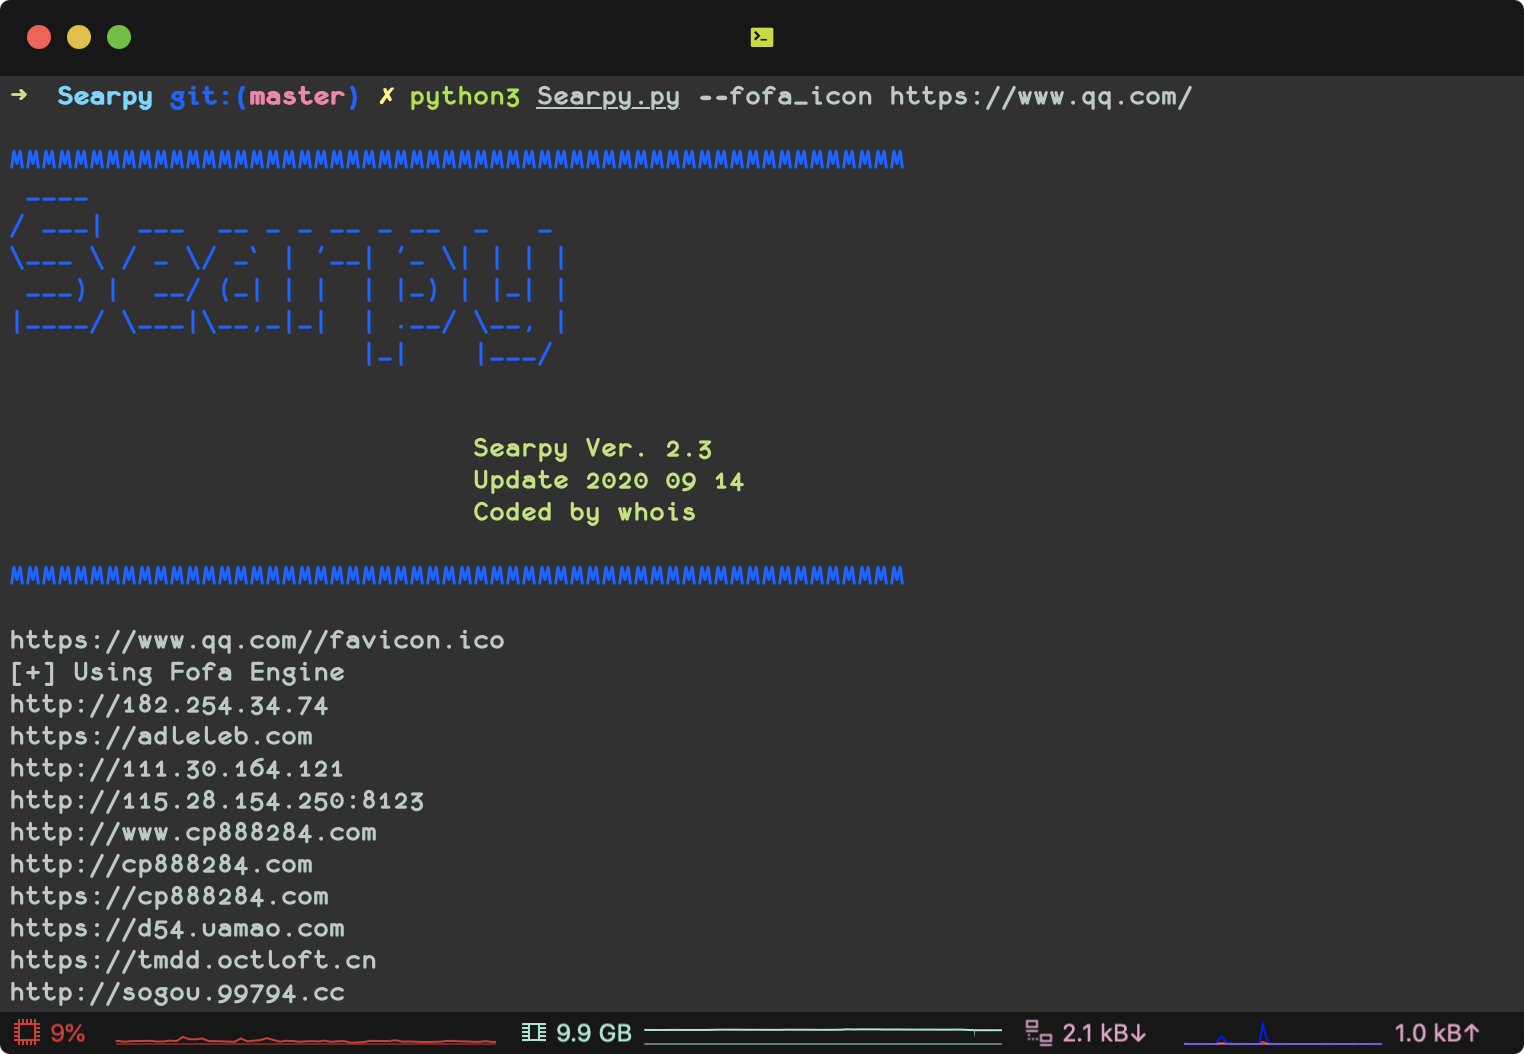 j3ers3/searpy
🥀 Search Engine Tookit,URL采集、Favicon哈希值查找真实IP、子域名查找
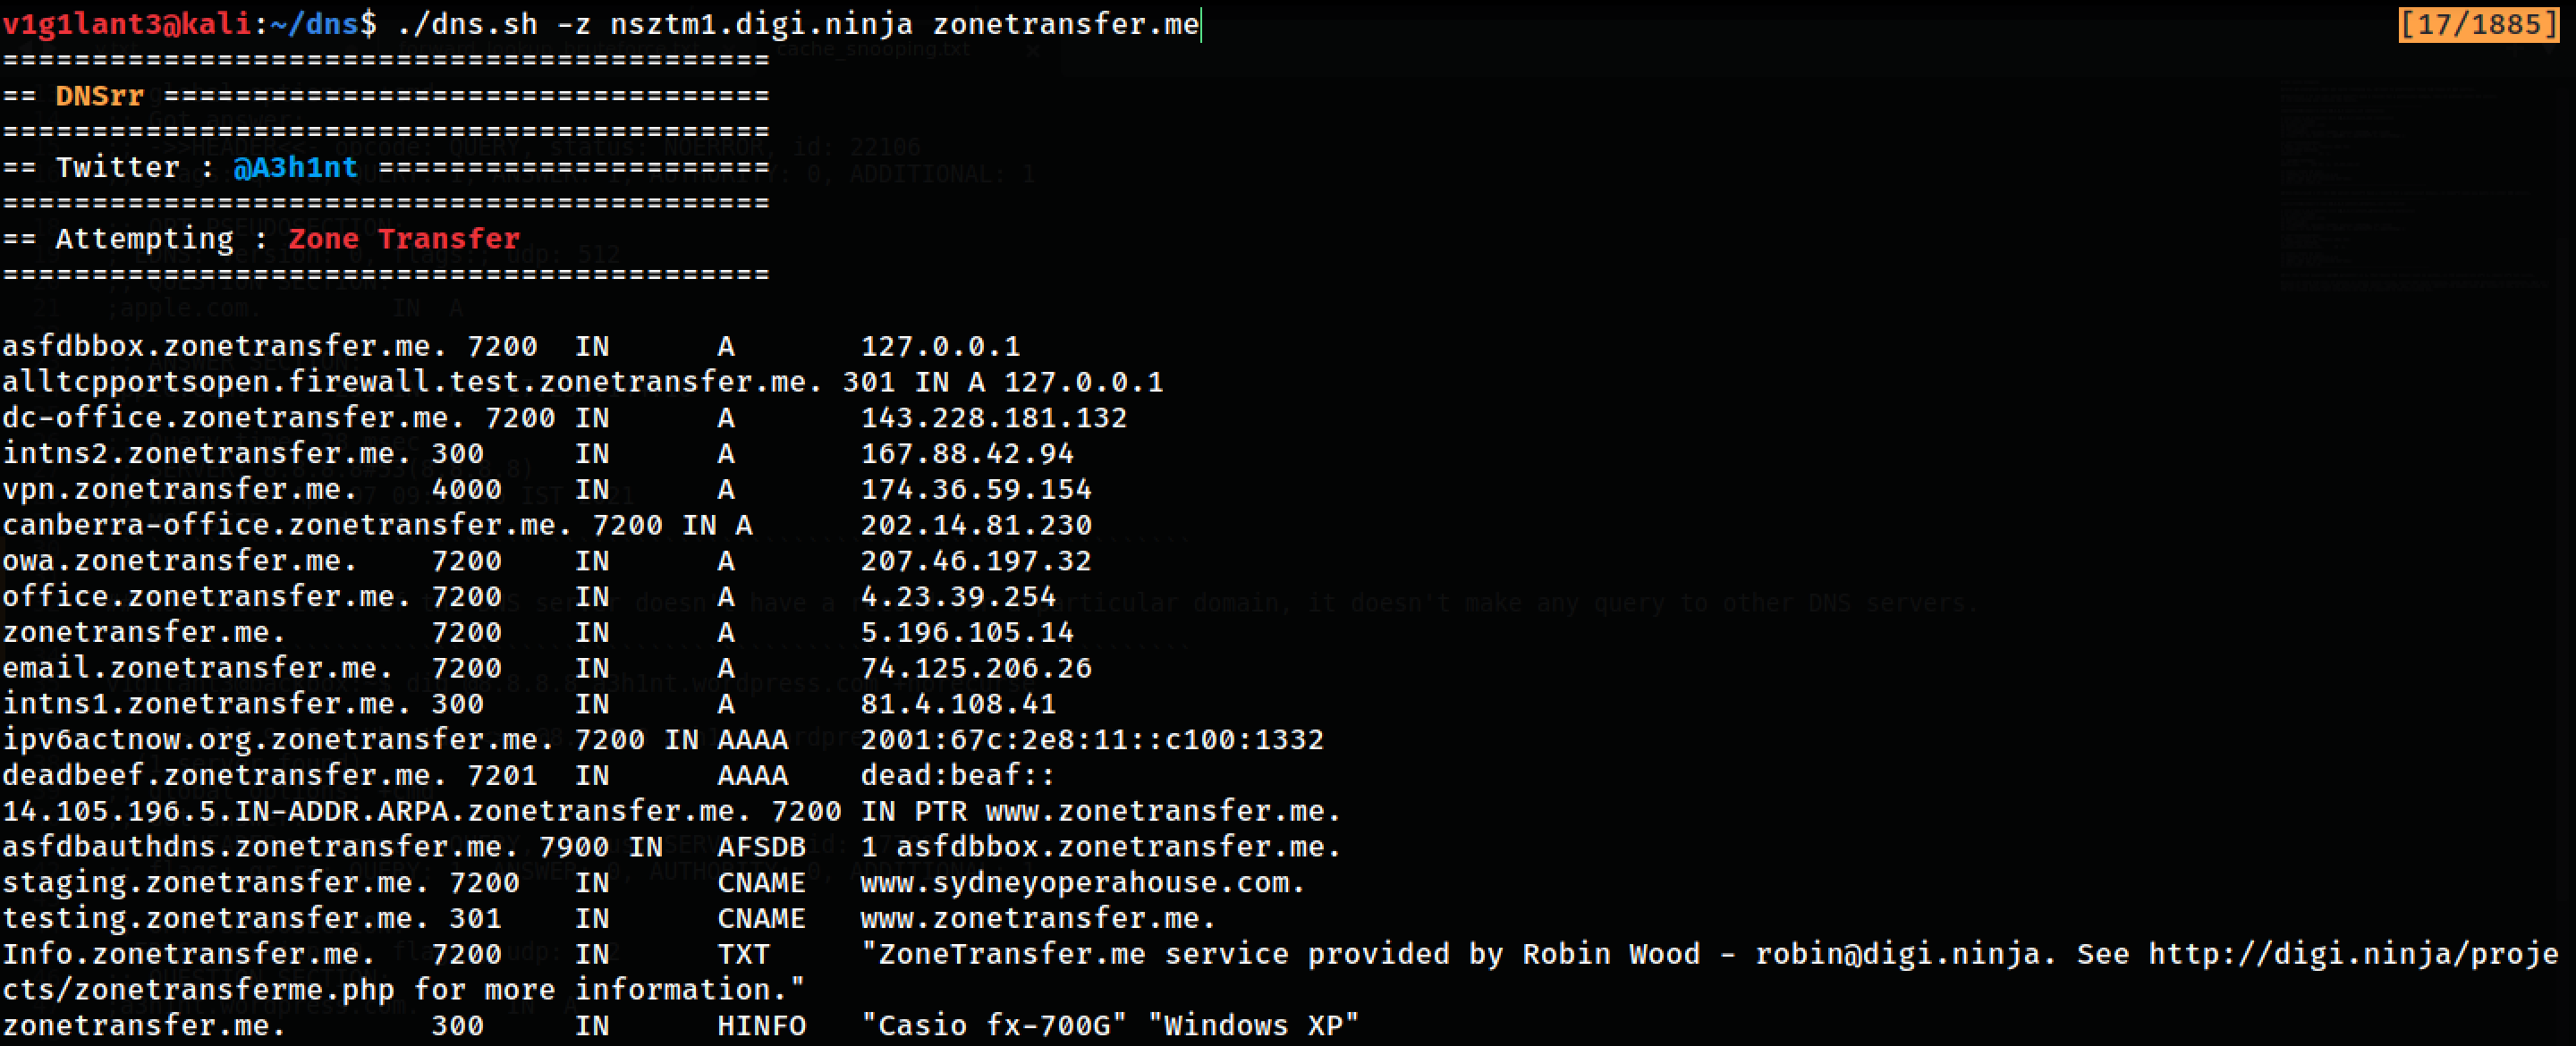 a3h1nt/dnsrr
Bash-based DNS enumeration tool performing forward/reverse bruteforce, cache snooping, and zone transfer to extract DNS records and subdomains.
 darryllane/bluto-old
Recon, Subdomain Bruting, Zone Transfers
 penafieljlm/inquisitor
Opinionated organisation-centric OSINT footprinting inspired from recon-ng and Maltego
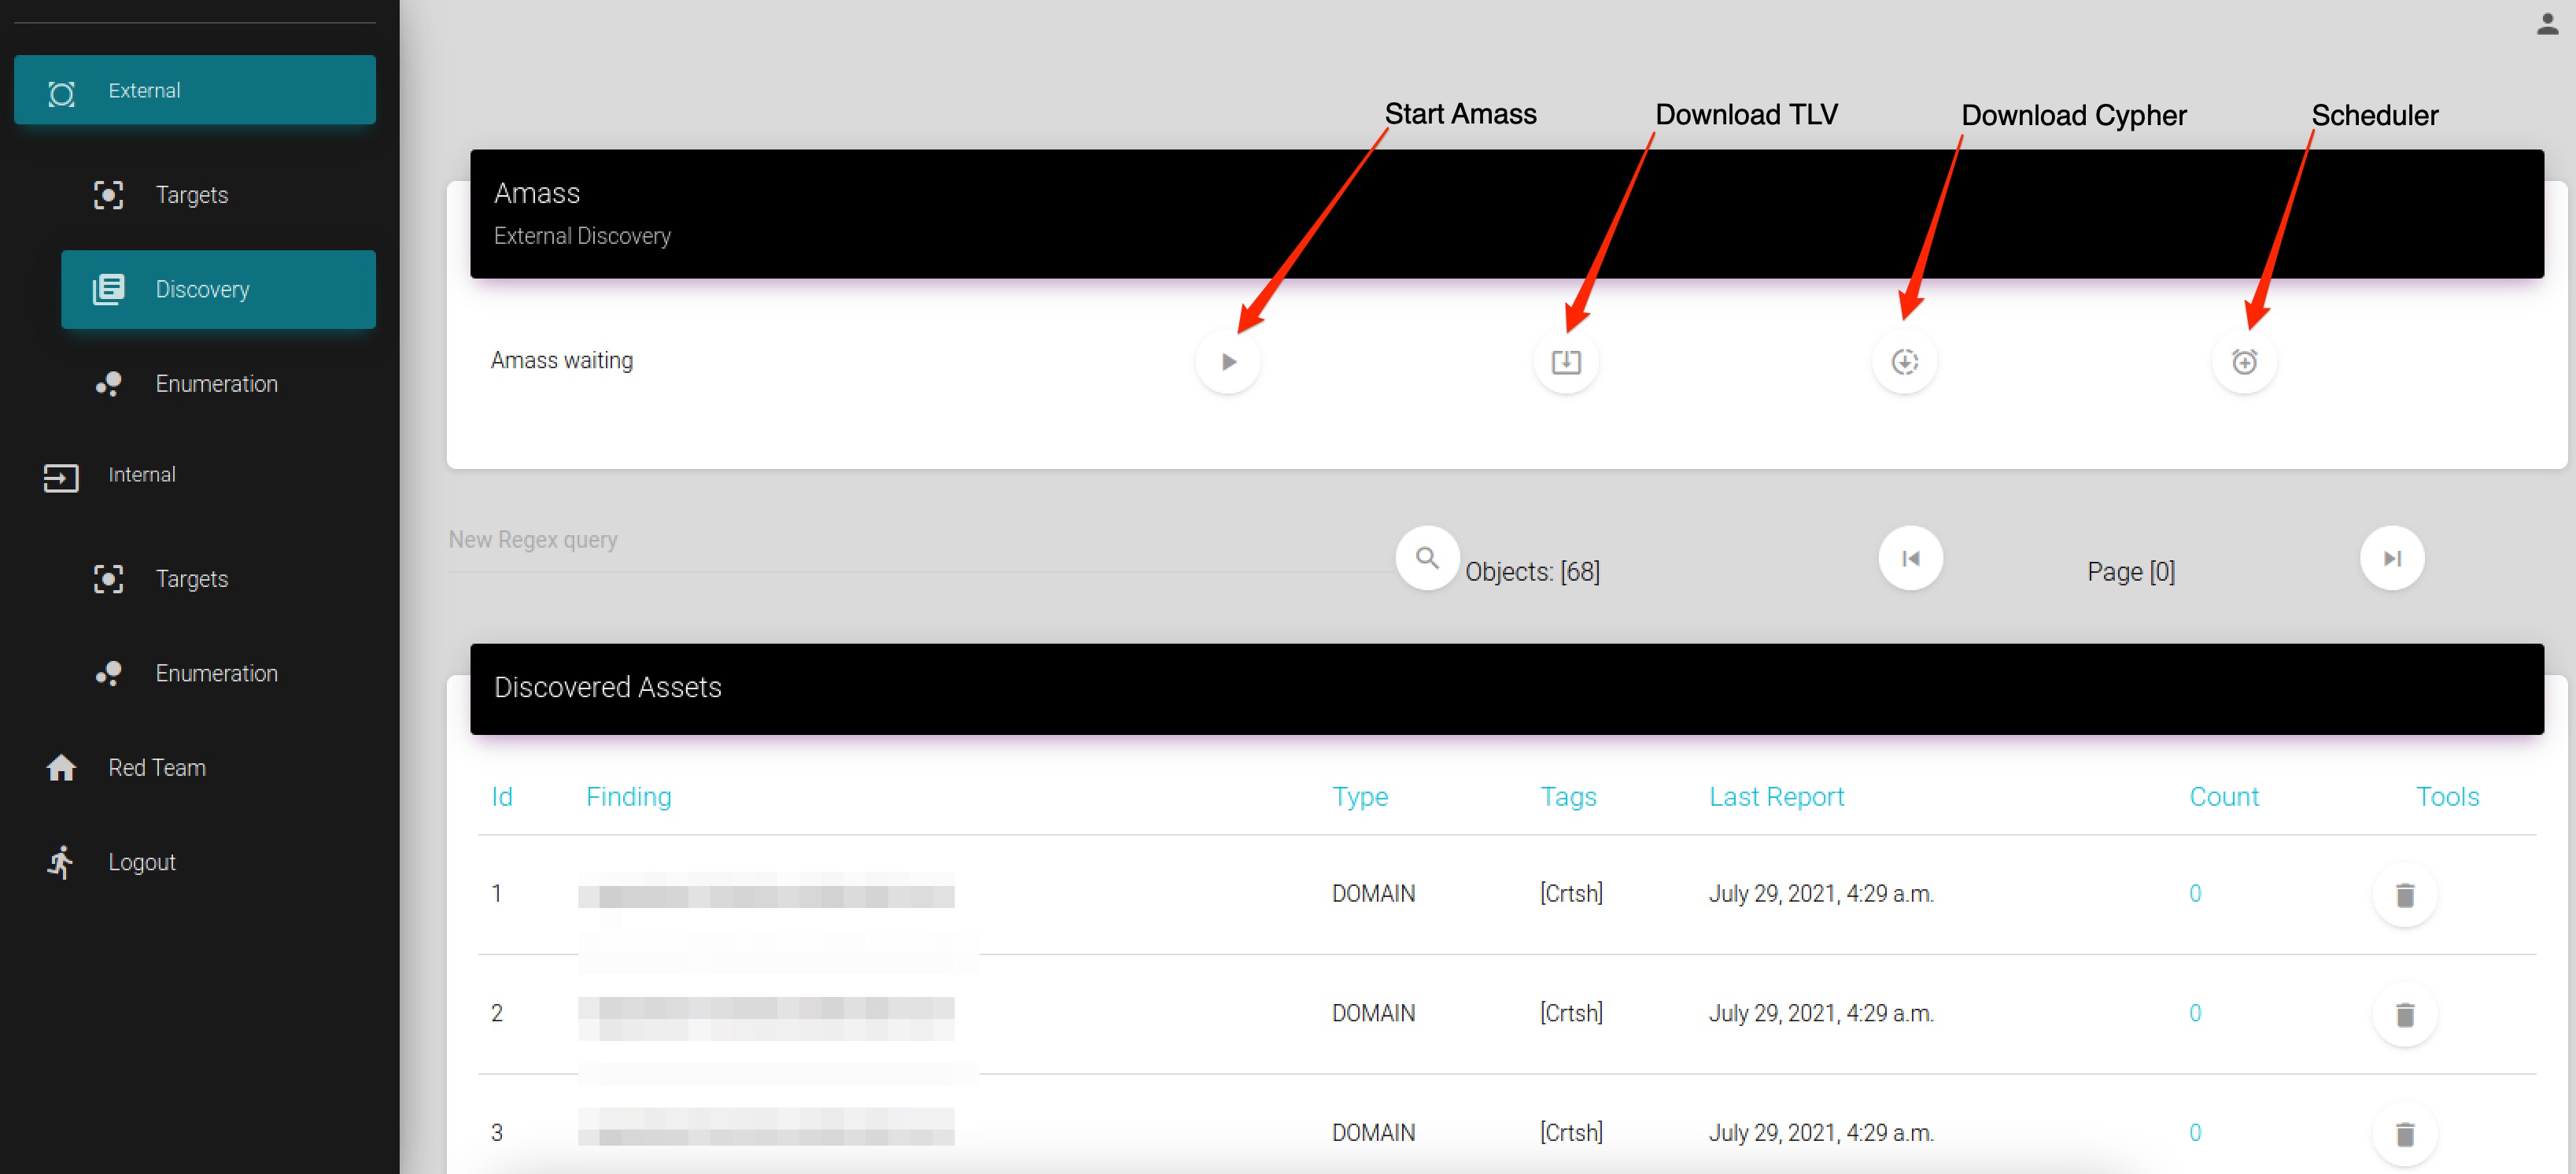 vmware-labs/attack-surface-framework
Tool to discover external and internal network attack surface
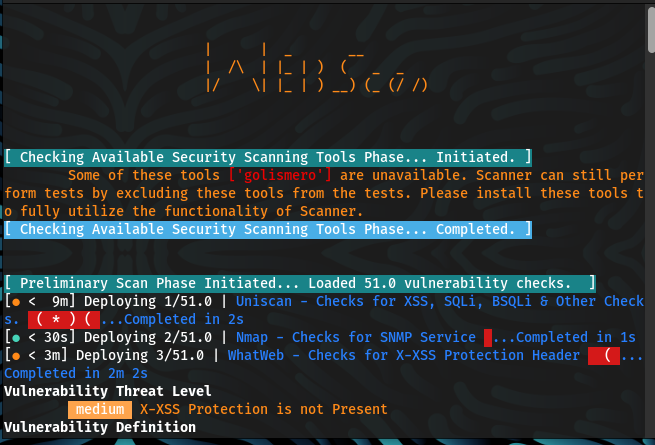 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
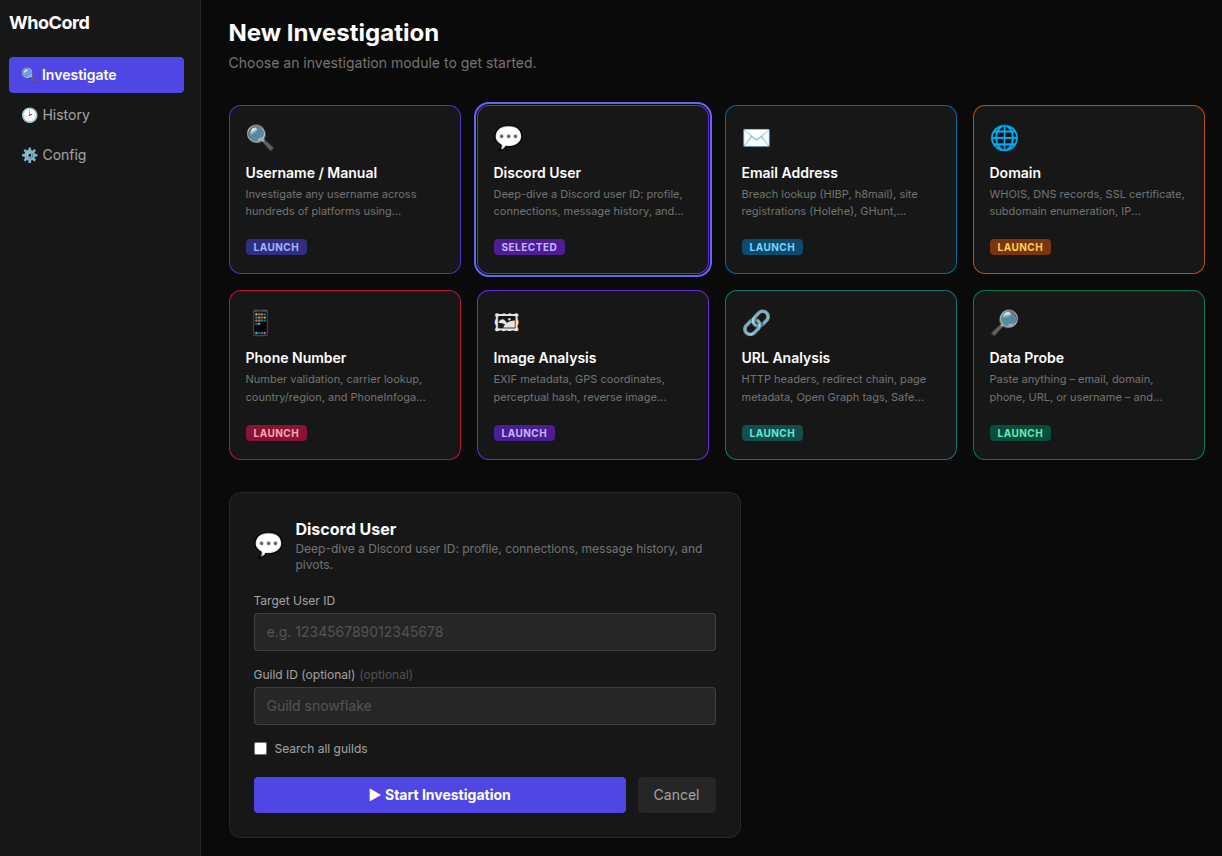 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
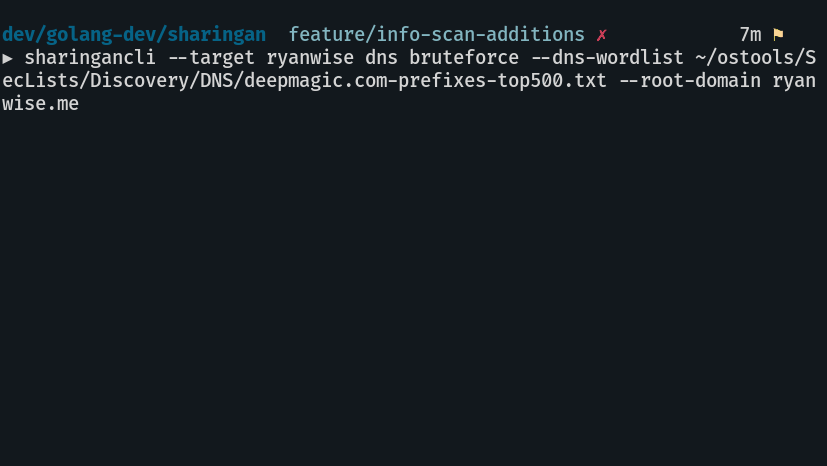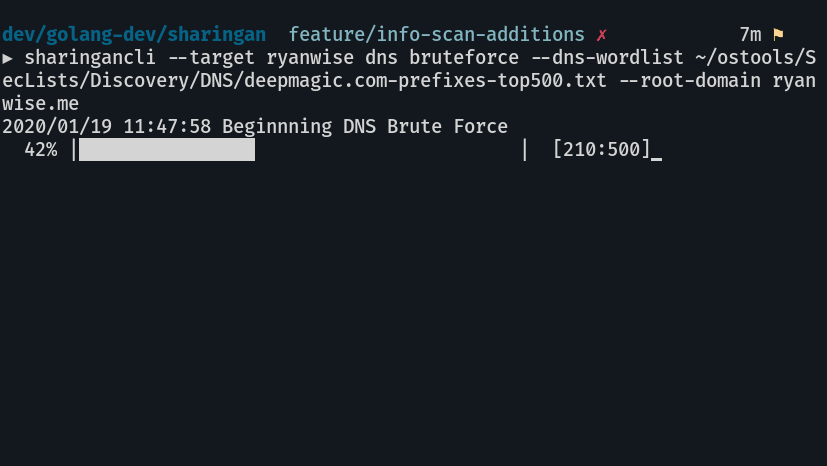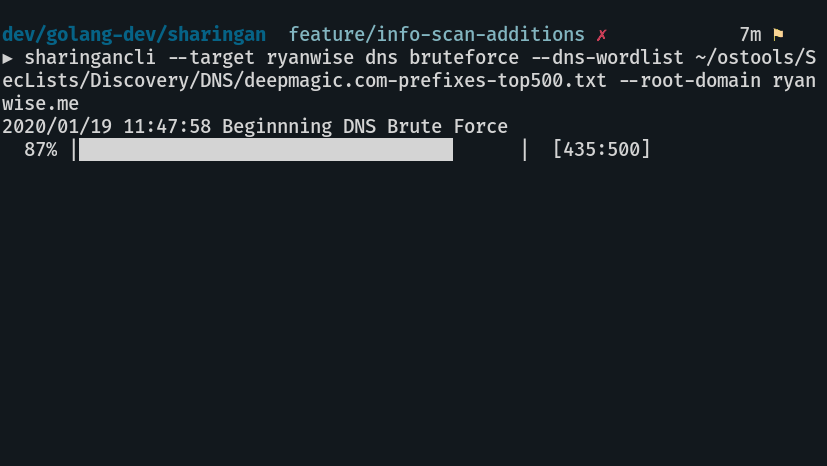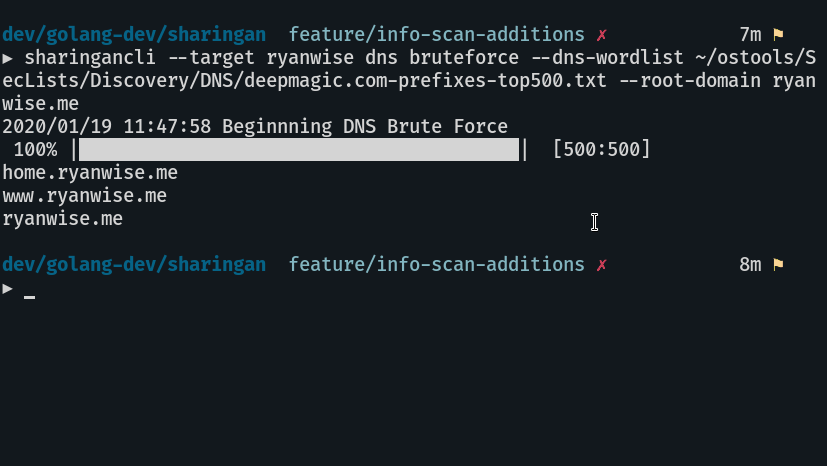 leobeosab/sharingan
Offensive Security recon tool
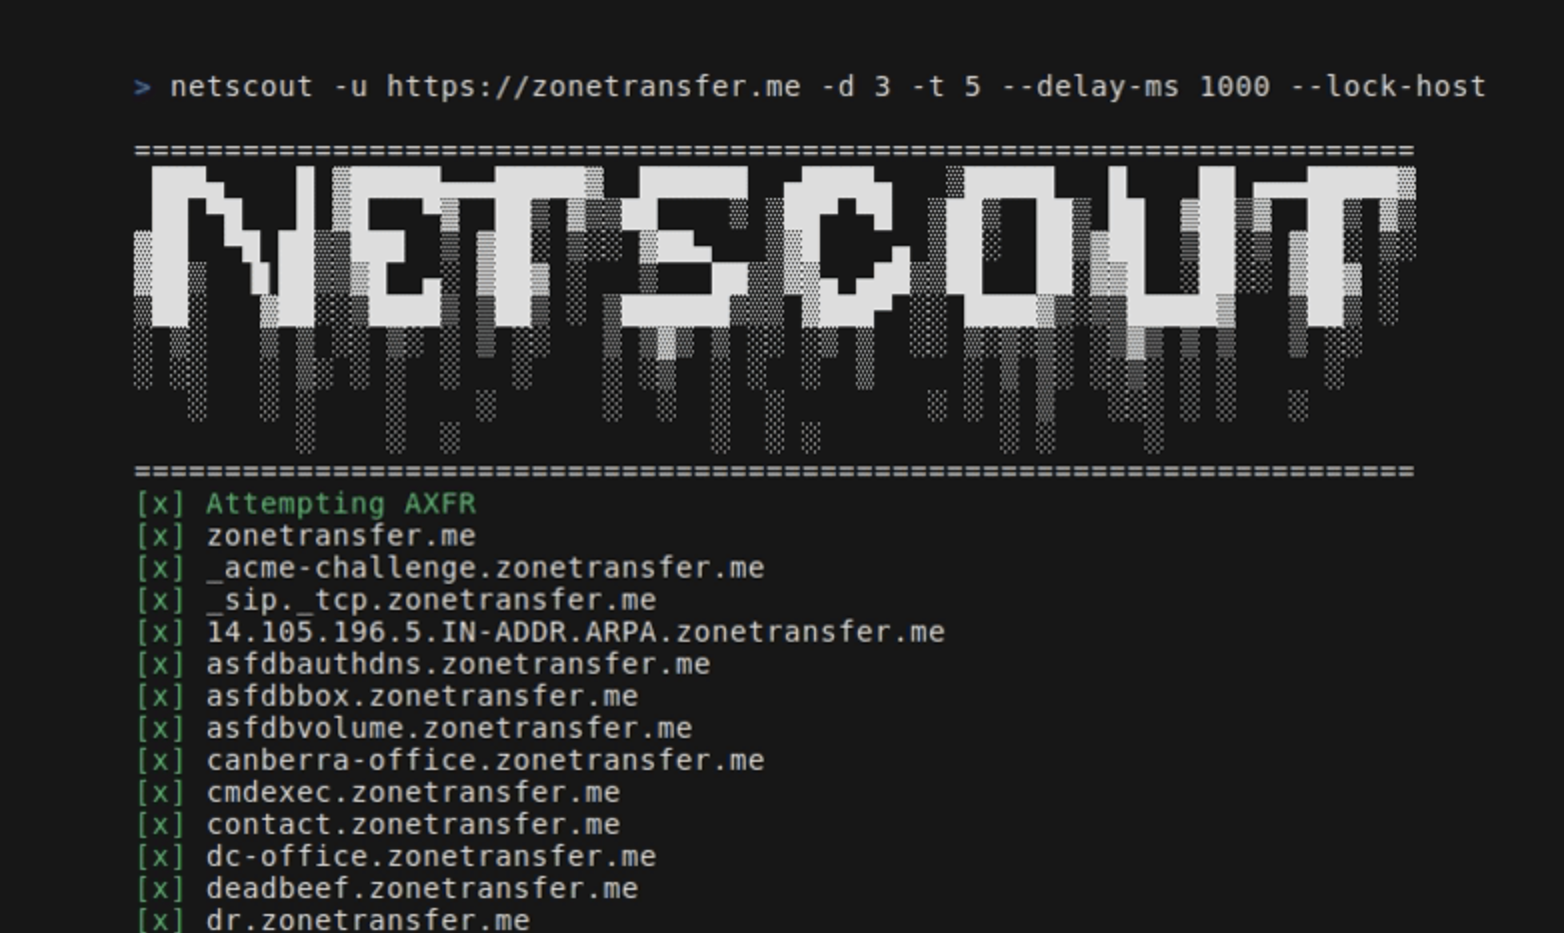 caio-ishikawa/netscout
OSINT tool that finds domains, subdomains, directories, endpoints and files for a given seed URL.
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
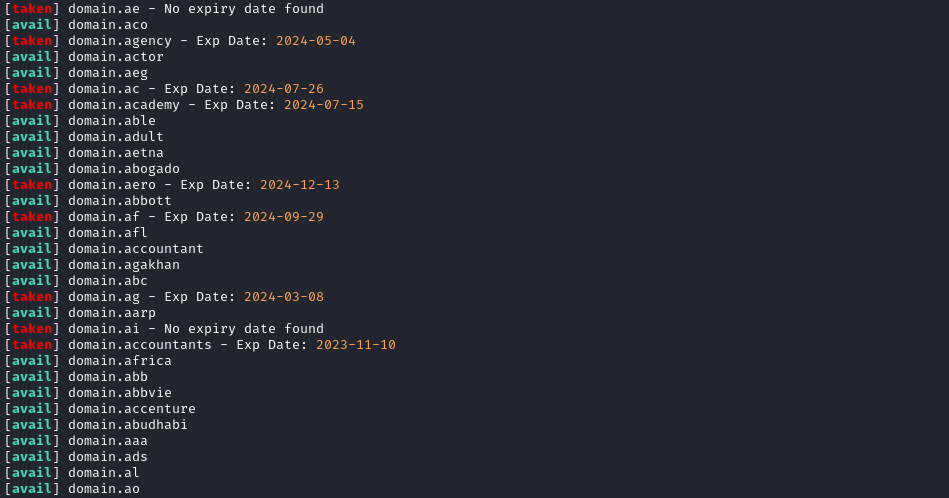 yuyudhn/tldhunt
Bash-based domain availability checker that scans WHOIS records across multiple TLDs to find unregistered domains for red teaming and phishing…
 makefu/dnsmap
fork of http://code.google.com/p/dnsmap/source/checkout
 researchanddestroy/dorxng
Next Generation DorX. Built by Dorks, for Dorks. 🤓
 mindcrypt/urideep
Unicode encoding attacks with machine learning
 ax-i-om/bitcrook
Centralized OSINT investigation platform with CLI and GUI, integrating email breach checks, domain lookups, phone search, and API key support for…
 pixelbubble/domainalerting
Daily alert when a new domain name is registered and contains your keywords