
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Digital Forensics — Page 6 | Kitploit
Categories

Digital Forensics

Tools for acquiring, preserving, and analyzing digital evidence for legal or investigative purposes.

Kitploit recommended
Top tools

10 selected
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k5 months ago
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k7 days ago
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k15 days ago
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k6h 35m ago
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k15 days ago
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k6h 29m ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k1 day ago
mvt preview#8

mvt

GitHubmvt-project/mvt
15.6k1 day ago
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
2307 days ago
avml preview#10

avml

GitHubmicrosoft/avml
1.1k3 days ago
NewestRelevanceMost popularRecently updated
1337 results
Notes preview

Notes

GitHubgracenolan/notes

Curated study notes and interview preparation guide for security engineering roles, covering networking, web security, cryptography, malware…

exploitationweb-securitymalware-analysis+6
2.7k8 months ago
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

OS X Auditor is a free Mac OS X computer forensics tool
disk-forensicsmemory-forensicsforensics+4
3.1k6 years ago
Wireshark preview

Wireshark

GitLabwireshark/wireshark

Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

packet-sniffing-analysisnetwork-mappingnetwork-forensics+3
1.6k15h 13m ago
Digital-Forensics-Guide preview

Digital-Forensics-Guide

GitHubmikeroyal/digital-forensics-guide

Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
memory-forensicsnetwork-forensicsforensics+7
3.1k2 years ago
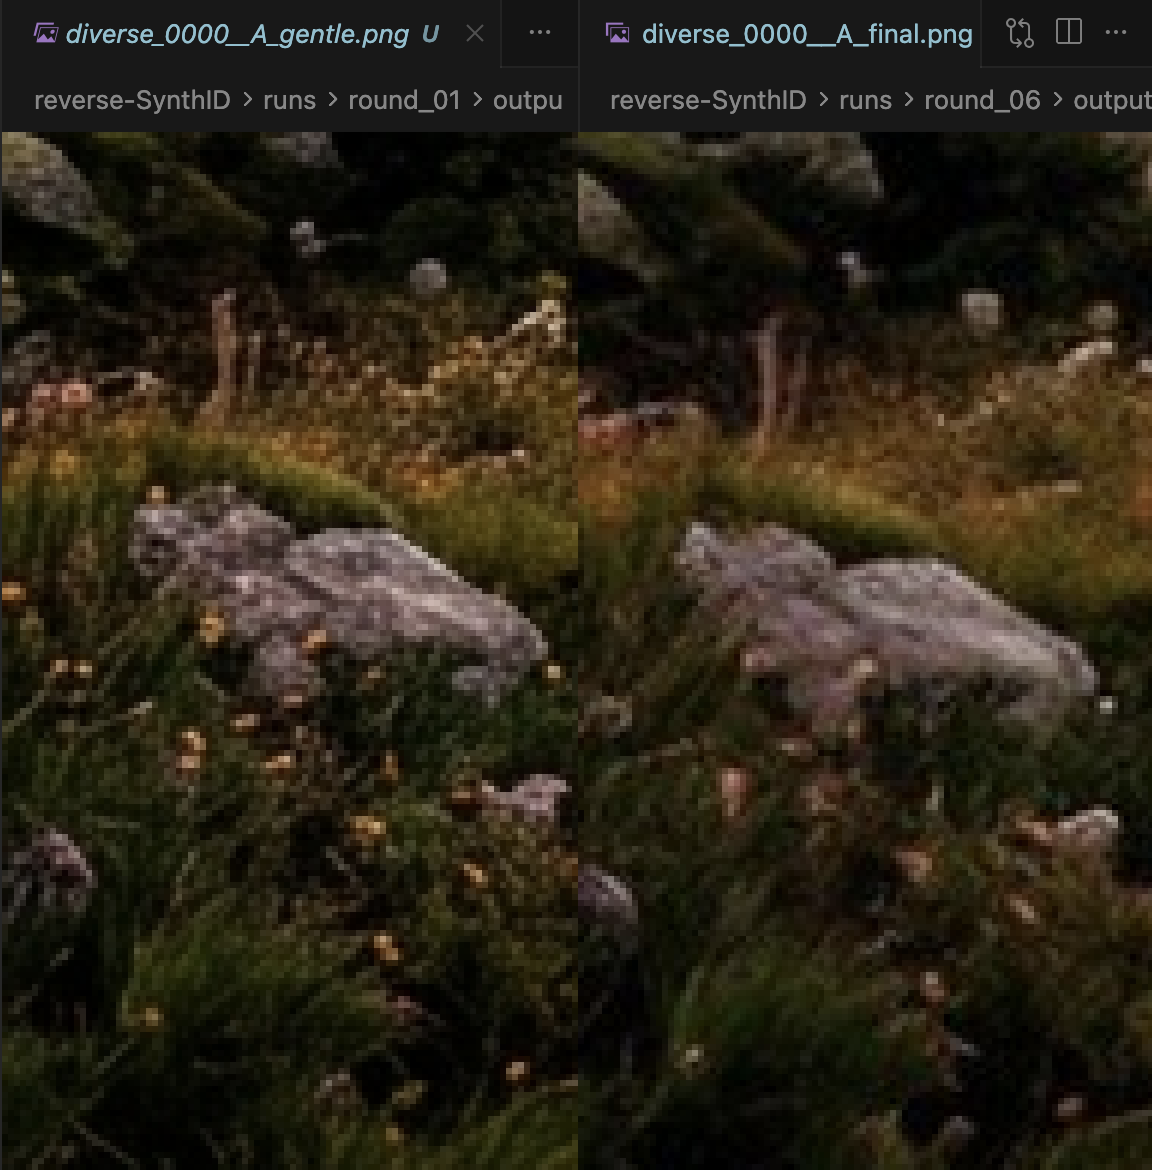
reverse-SynthID preview

reverse-SynthID

GitHubaloshdenny/reverse-synthid

reverse engineering Gemini's SynthID detection
reverse-engineeringsteganographydigital-forensics+6
4.7k3 months ago
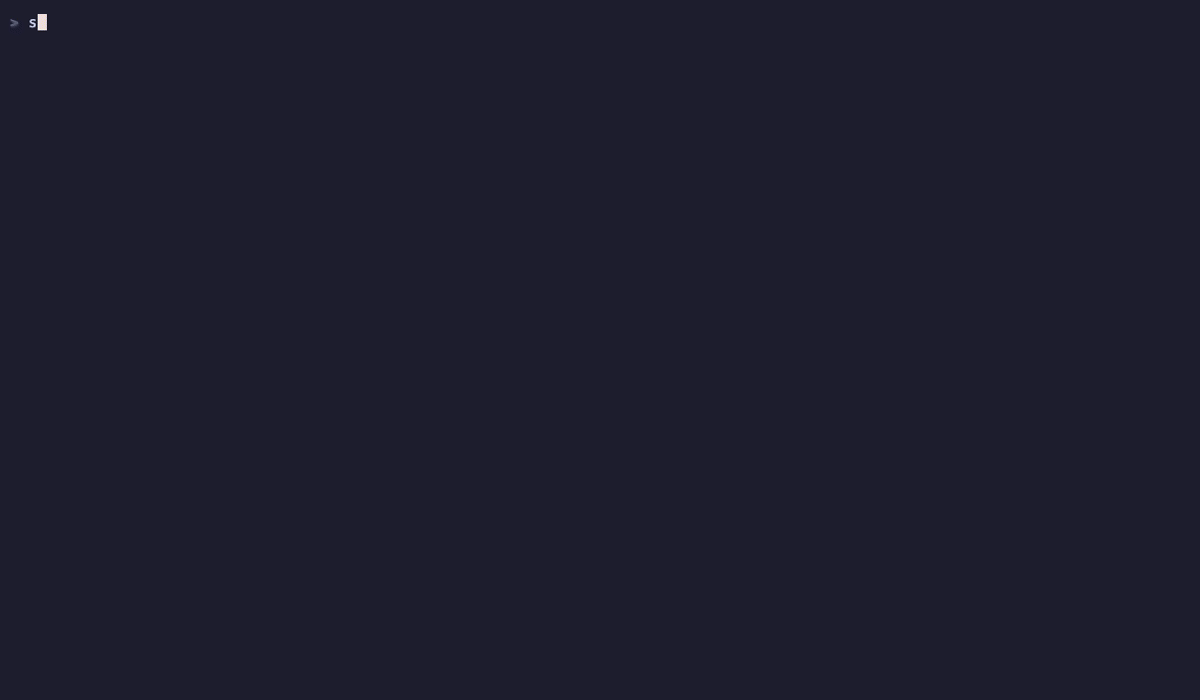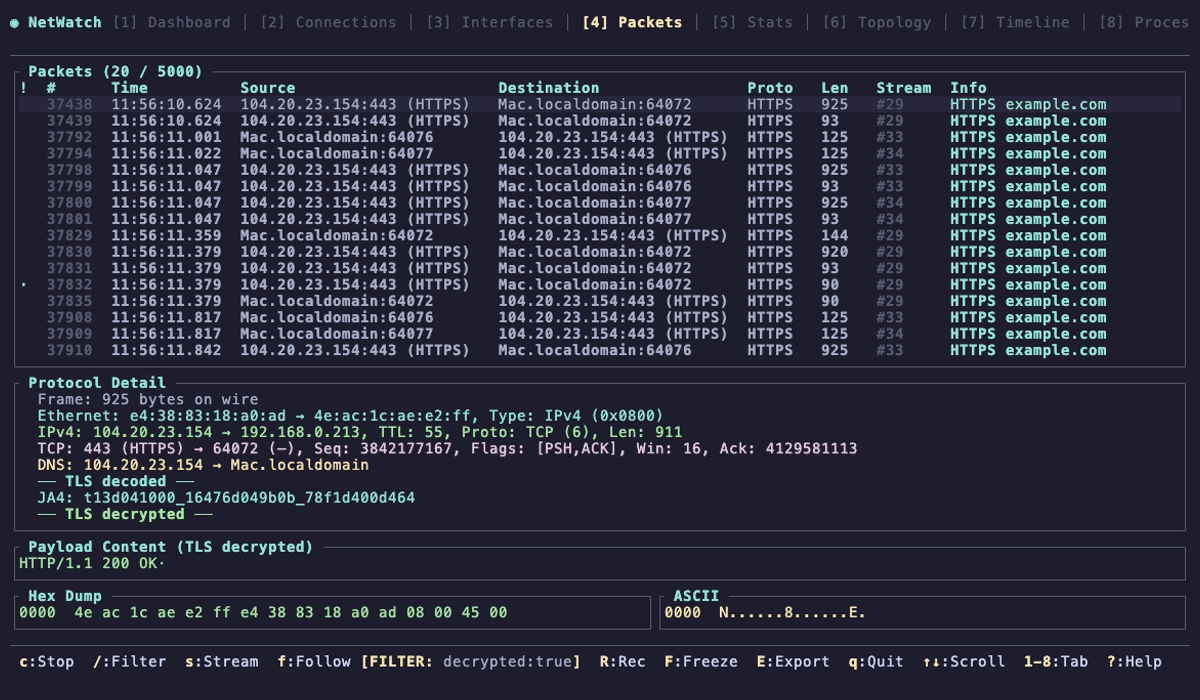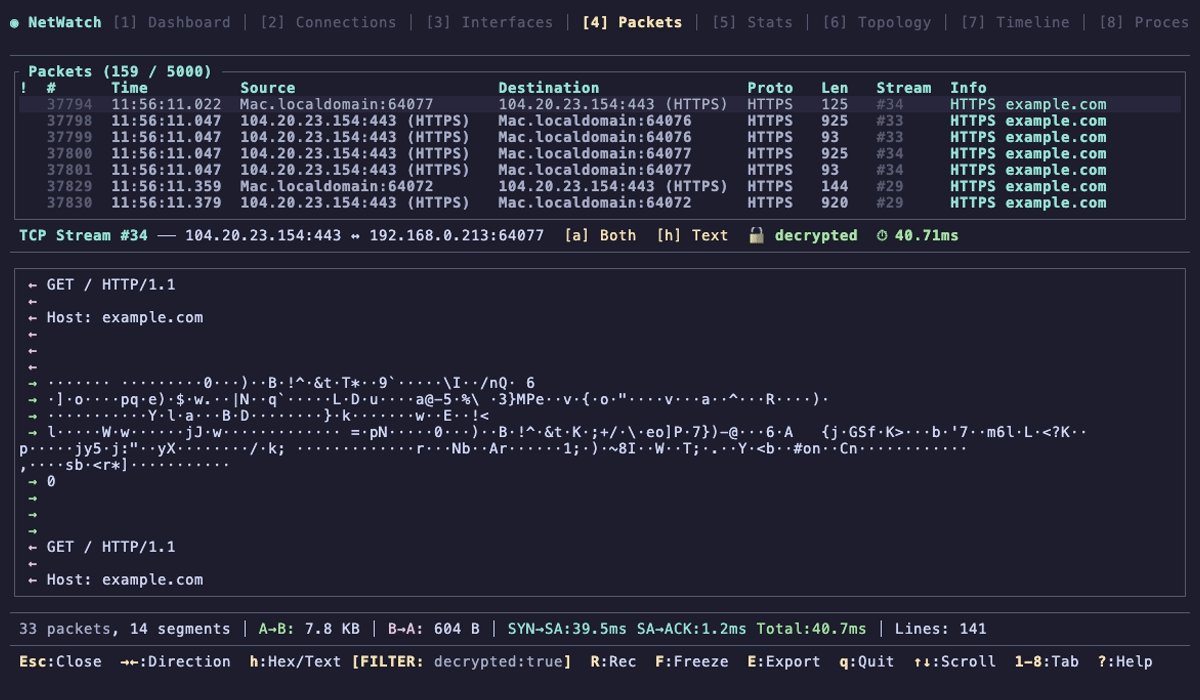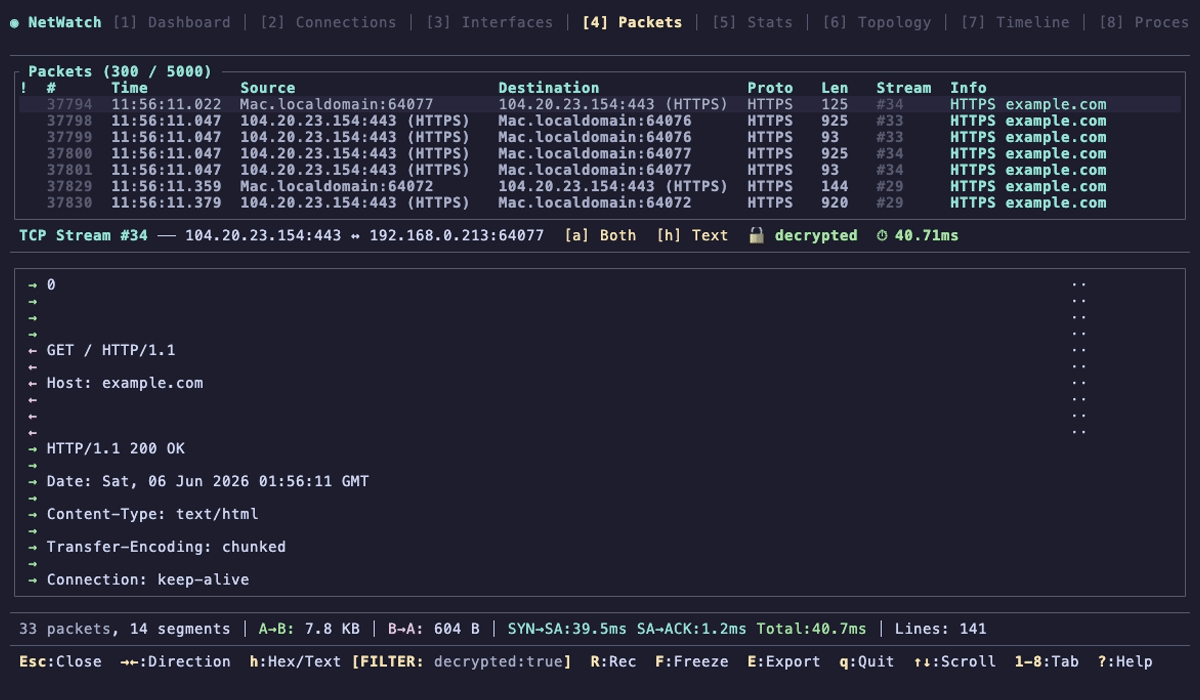
netwatch preview

netwatch

GitHubmatthart1983/netwatch

Real-time network diagnostics in your terminal. One command, zero config, instant visibility.

defensive-toolspacket-sniffing-analysisencryption-decryption-tools+8
2.3k1 day ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

memory-forensicspayload-generationexploitation+7
4.7k2 years ago
passivedns preview

passivedns

GitHubgamelinux/passivedns

A network sniffer that logs all DNS server replies for use in a passive DNS setup

network-forensicsforensicsinformation-gathering+3
1.7k9 days ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
memory-forensicspayload-generationexploitation+7
2.5k4 years ago
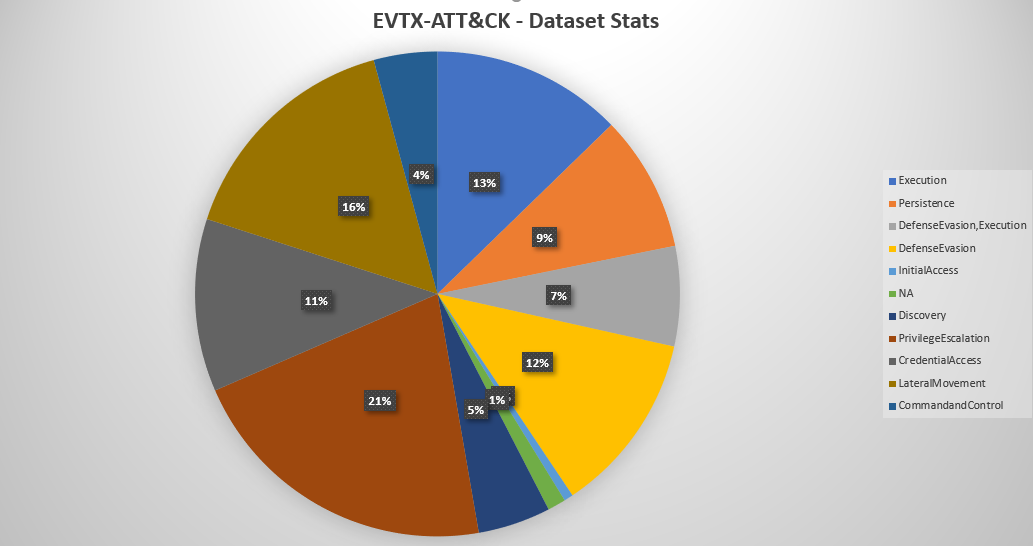
EVTX-ATTACK-SAMPLES preview

EVTX-ATTACK-SAMPLES

GitHubsbousseaden/evtx-attack-samples

Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…

digital-forensicsthreat-intelligenceeducation+2
2.6k3 years ago
seer preview

seer

GitHubepasveer/seer

Seer - a gui frontend to gdb

static-analysisdynamic-analysis-sandboxingmemory-forensics+3
3.4k2 days ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
memory-forensicsreverse-engineeringforensics+2
3.9k4 months ago
DeepBlueCLI preview

DeepBlueCLI

GitHubsans-blue-team/deepbluecli

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
malware-analysisdigital-forensicsintrusion-detection+2
2.4k3 years ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?
memory-forensicsnetwork-forensicsmalware-analysis+5
1.8k1 month ago
oletools preview

oletools

GitHubdecalage2/oletools

Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…

static-analysisvulnerability-analysiscode-analysis+3
3.4k9 months ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
disk-forensicsioc-managementvulnerability-scanners+11
3.8k9 months ago
KapeFiles preview

KapeFiles

GitHubericzimmerman/kapefiles

This repository serves as a place for community created Targets and Modules for use with KAPE.

disk-forensicsforensicsdigital-forensics+2
8647 days ago
ja4 preview

ja4

GitHubfoxio-llc/ja4

JA4+ is a suite of network fingerprinting standards

packet-sniffing-analysisencryption-decryption-toolsiot-security+9
2.0k21 days ago
Previous1…567…75Next









