
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 ajf8729/blacklotus
BlackLotus aka CVE-2023-24932 Detection/Remediation Scripts for Intune, ConfigMgr, and generic use
 mf-labs/witcher
Managing GitHub Advanced Security (GHAS) Controls at Scale
 aquasecurity/tfsec
Tfsec is now part of Trivy
 cybervixy/vulnerability-management
NGINX Security Hardening & Vulnerability Remediation Analysis of critical CVEs (CVE-2021-23017, HTTP/2 DoS flaws) in outdated NGINX versions, with…
 jaloon/spring-webmvc5
Fork spring-webmvc 5.3.39 to fix CVE-2024-38816, CVE-2024-38819
 murataydemir/aws-sam-cli-vulnerabilities
Issue with AWS SAM CLI (CVE-2025-3047, CVE-2025-3048)
 adriyansyah-mf/centralizedfirewall
provides a Firewall Manager API designed to centralize and streamline the management of firewall configurations
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 jduck/csw-slides-2024
Slides for Developing Secure Software in 2024 at CanSecWest
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
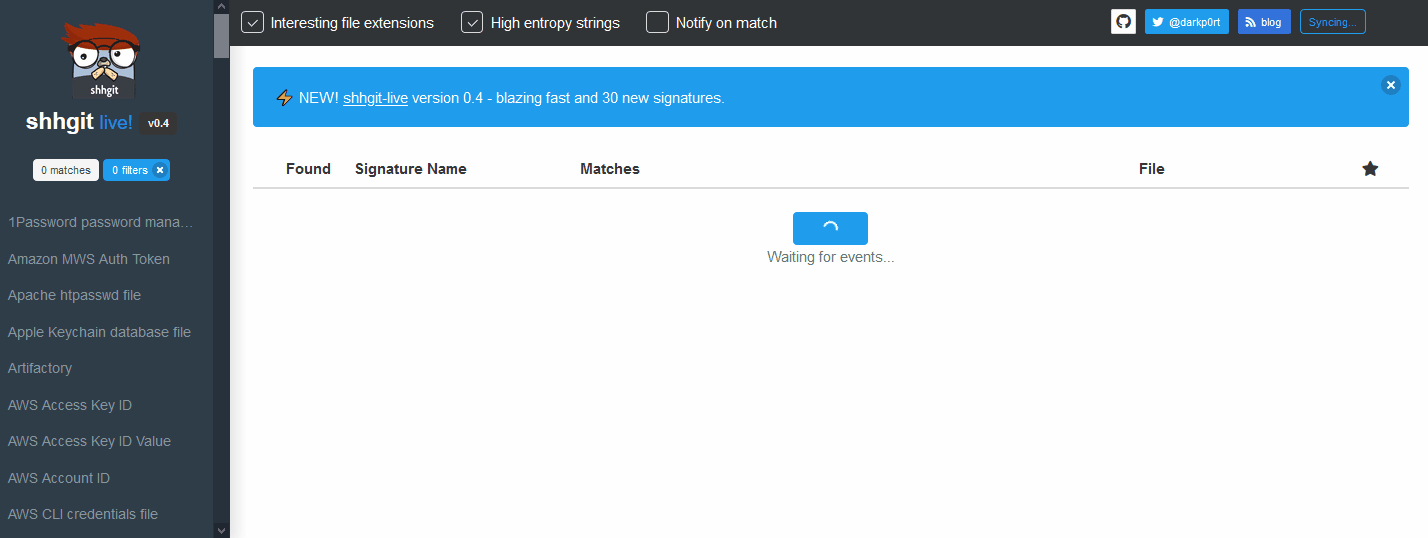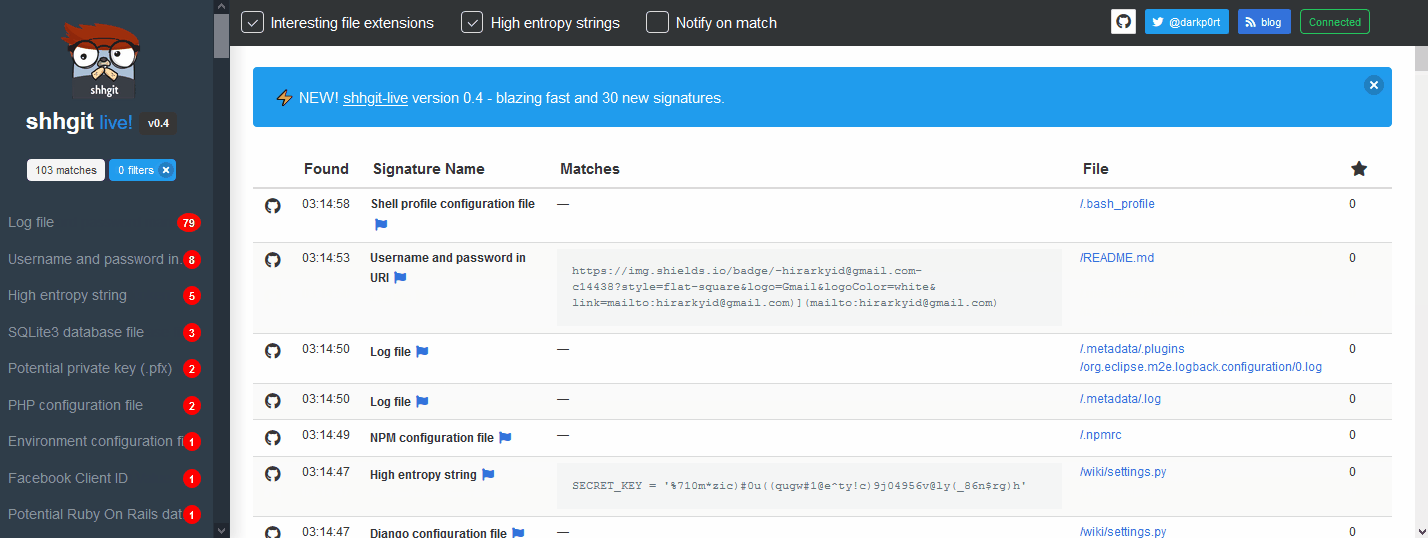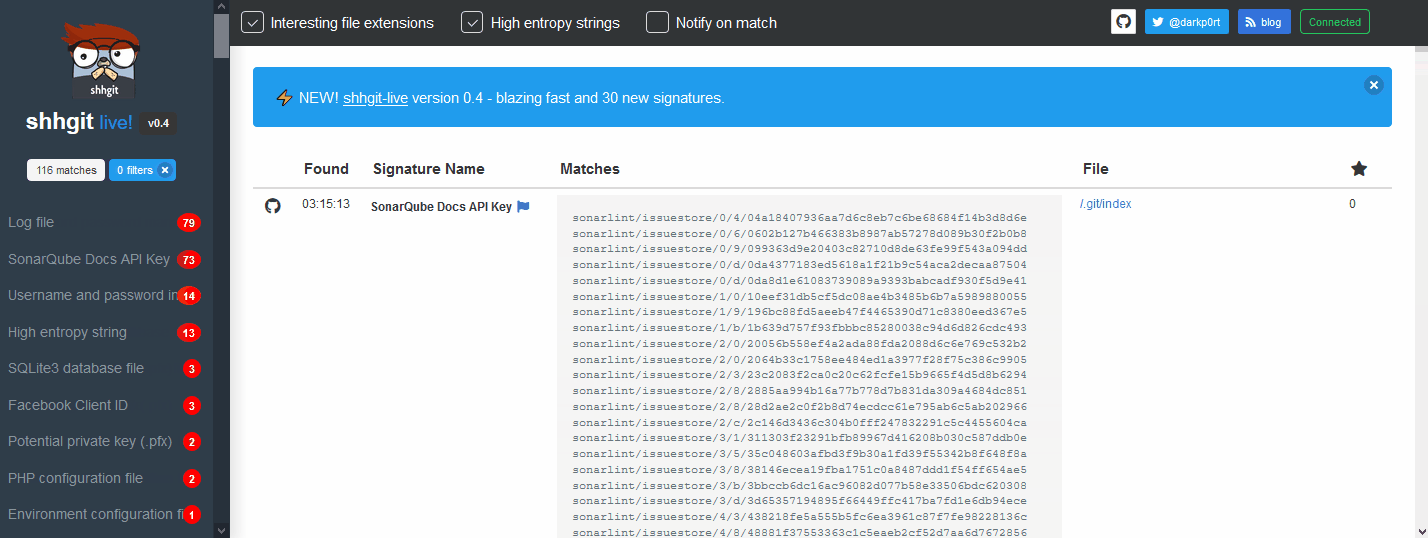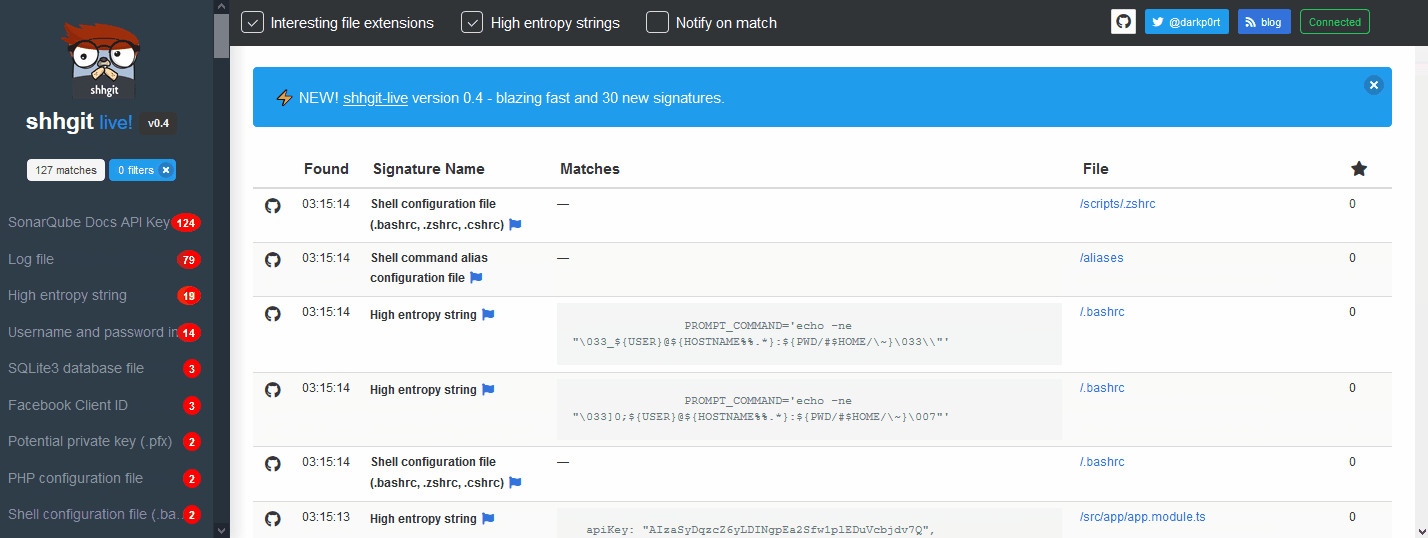 eth0izzle/shhgit
Ah shhgit! Find secrets in your code. Secrets detection for your GitHub, GitLab and Bitbucket repositories.
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 dolutech/patch-manual-cve-2025-26465-e-cve-2025-26466
Patch Manual para a correção das CVE-2025-26465-e-CVE-2025-26466, para sistemas sem update do OpenSSH
 knqyf263/go-mal-pkgs
A security tool to detect malicious Go packages by verifying checksums in go.sum against the original source code
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover
 wubinworks/magento2-encryption-key-manager-cli
A utility for Magento 2 encryption key rotation and management. CVE-2024-34102(aka Cosmic Sting) victims can use it as an aftercare.
 papermtn/gitlab-watchman
Finding exposed secrets and personal data in GitLab








