
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 giovannigatti/cve-bench
A benchmark for evaluating AI agents on fixing real-world security vulnerabilities.
 nedlir/dasel-hardened-container
Hardened dasel v3.3.1 package and image built via Melange and apko. Patching CVE-2026-33320.
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 padok-team/yatas
:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
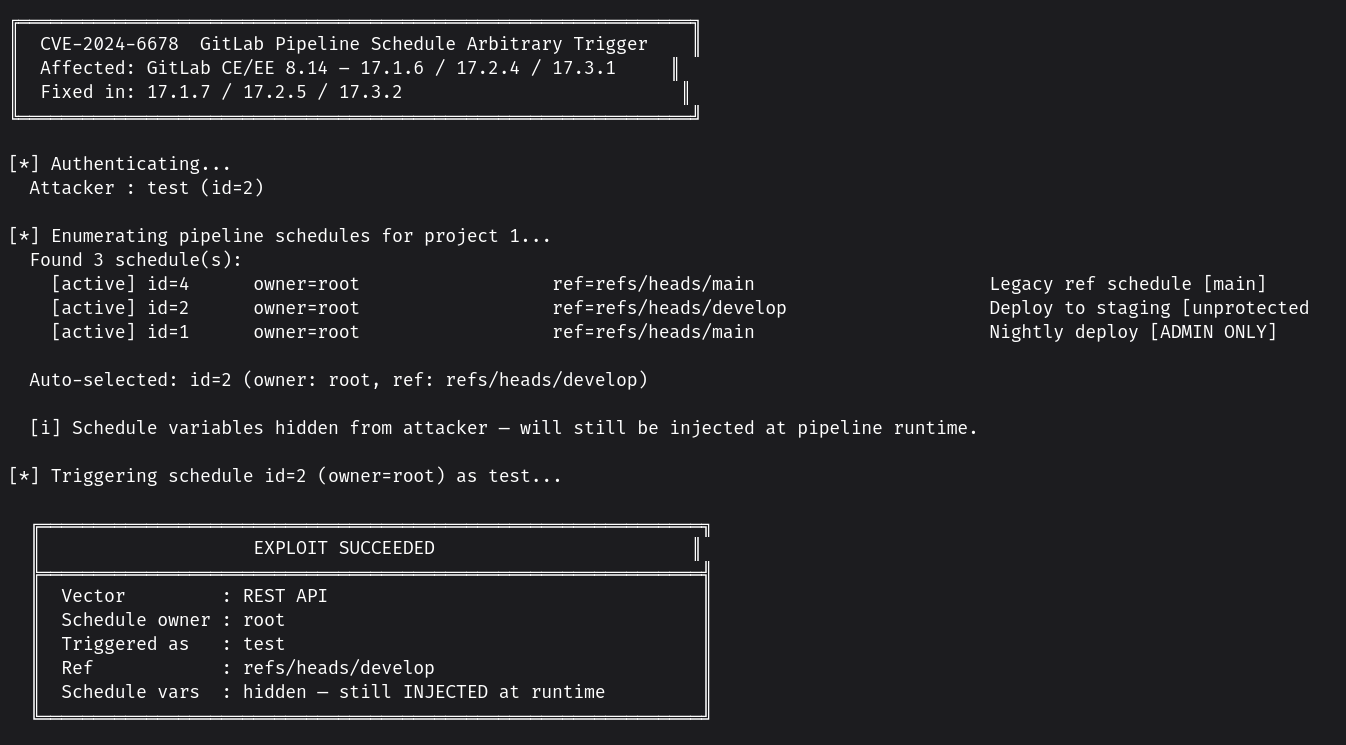 fallenskill1/cve-2024-6678
PoC for CVE-2024-6678
 dannyendortest/node-vulnerable
Synthetic demo target for EXPOSURE — CVE-2018-21268 (traceroute) + CVE-2018-3757 (pdf-image)
 dannyendortest/invokeai
Synthetic demo target for CVE-2024-10821 vulnerability detection and automated fix via compensating control. Demonstrates one-click PR-based…
 dannyendortest/ollama
Synthetic demo target for Endor Labs EXPOSURE, tracking CVE-2024-12886 with a deliberately vulnerable dependency and a one-click PR-based fix…
 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 fkj-src/fix_nginx_cve_2026_42945
Automated one-click shell script to detect and patch NGINX CVE-2026-42945 across major Linux distributions, with config backup, version validation,…
 barappteam/nginx-cve-fix
Source-built nginx 1.25.5 container with backported CVE-2026-42945 fix, OpenSSL bump, full provenance chain, and VEX attestation.
 yakovyakov/cve-2026-31431-mitigation
Detection and mitigation tooling for CVE-2026-31431 (Copy Fail) on Linux kernels. Includes Phalanx-CCS and Silent4Labs scripts plus an Ansible…
 gubiczap/cve-2026-31431-checker
Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…
 aaronm-sysdig/log4j-vuln-demo
Intentionally vulnerable Log4j 2.14.1 demo for Sysdig CNAPP scanning (CVE-2021-44228)








