
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 pvharmo2/gha-lab-00d54c717d
Security-research lab: CVE-2026-47172 (workflow_run pwn request in deploy.yaml) — flattened snapshot of duck-organization/questbot at 1903b2f
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 pvharmo2/gha-lab-5bce203f66
Security-research lab: reproduction of CVE-2026-41249 (GHSA-q58j-g3f4-h26h) — pull_request_target pwn request in .github/workflows/static.yml,…
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…

 dannydoodlesstory/evm-audit-helpers
Collection of Solidity snippets and Foundry scripts for smart contract security audits
 pvharmo2/gha-lab-3f1ff30e9c
Authorized security-research lab reproducing CVE-2026-31852 (jellyfin/jellyfin-ios pull_request_target pwn in code-quality.yml) — isolated snapshot,…
 pvharmo2/gha-lab-ca4fa82ac5
Security-research lab: reproduction of CVE-2026-29075 (GHSA-3j55-5q6x-2h48) in mesa/mesa benchmarks.yml pull_request_target workflow — single-commit…
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 pvharmo2/gha-lab-f894926966
Authorized security-research reproduction lab for CVE-2025-54415 (GHSA-g5hx-xv45-9whg): astronomer/dag-factory snapshot at 464c75a —…
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
 pvharmo2/gha-lab-ba8e0c4217
Authorized security-research lab: reproduction of CVE-2024-42370 / GHSA-4hq2-rpgc-r8r7 (env injection in docs-preview.yml) — snapshot of…
 adversis/tailsnitch
A security auditor for Tailscale configurations. Scans your tailnet for misconfigurations, overly permissive access controls, and security best…
 pyupio/safety
Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 pvharmo2/gha-lab-40e23db109
Security-research lab: controlled reproduction of CVE-2024-4254 (GHSA-fc78-c36r-cc59) — deploy-website.yml fork checkout/code execution in…
 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
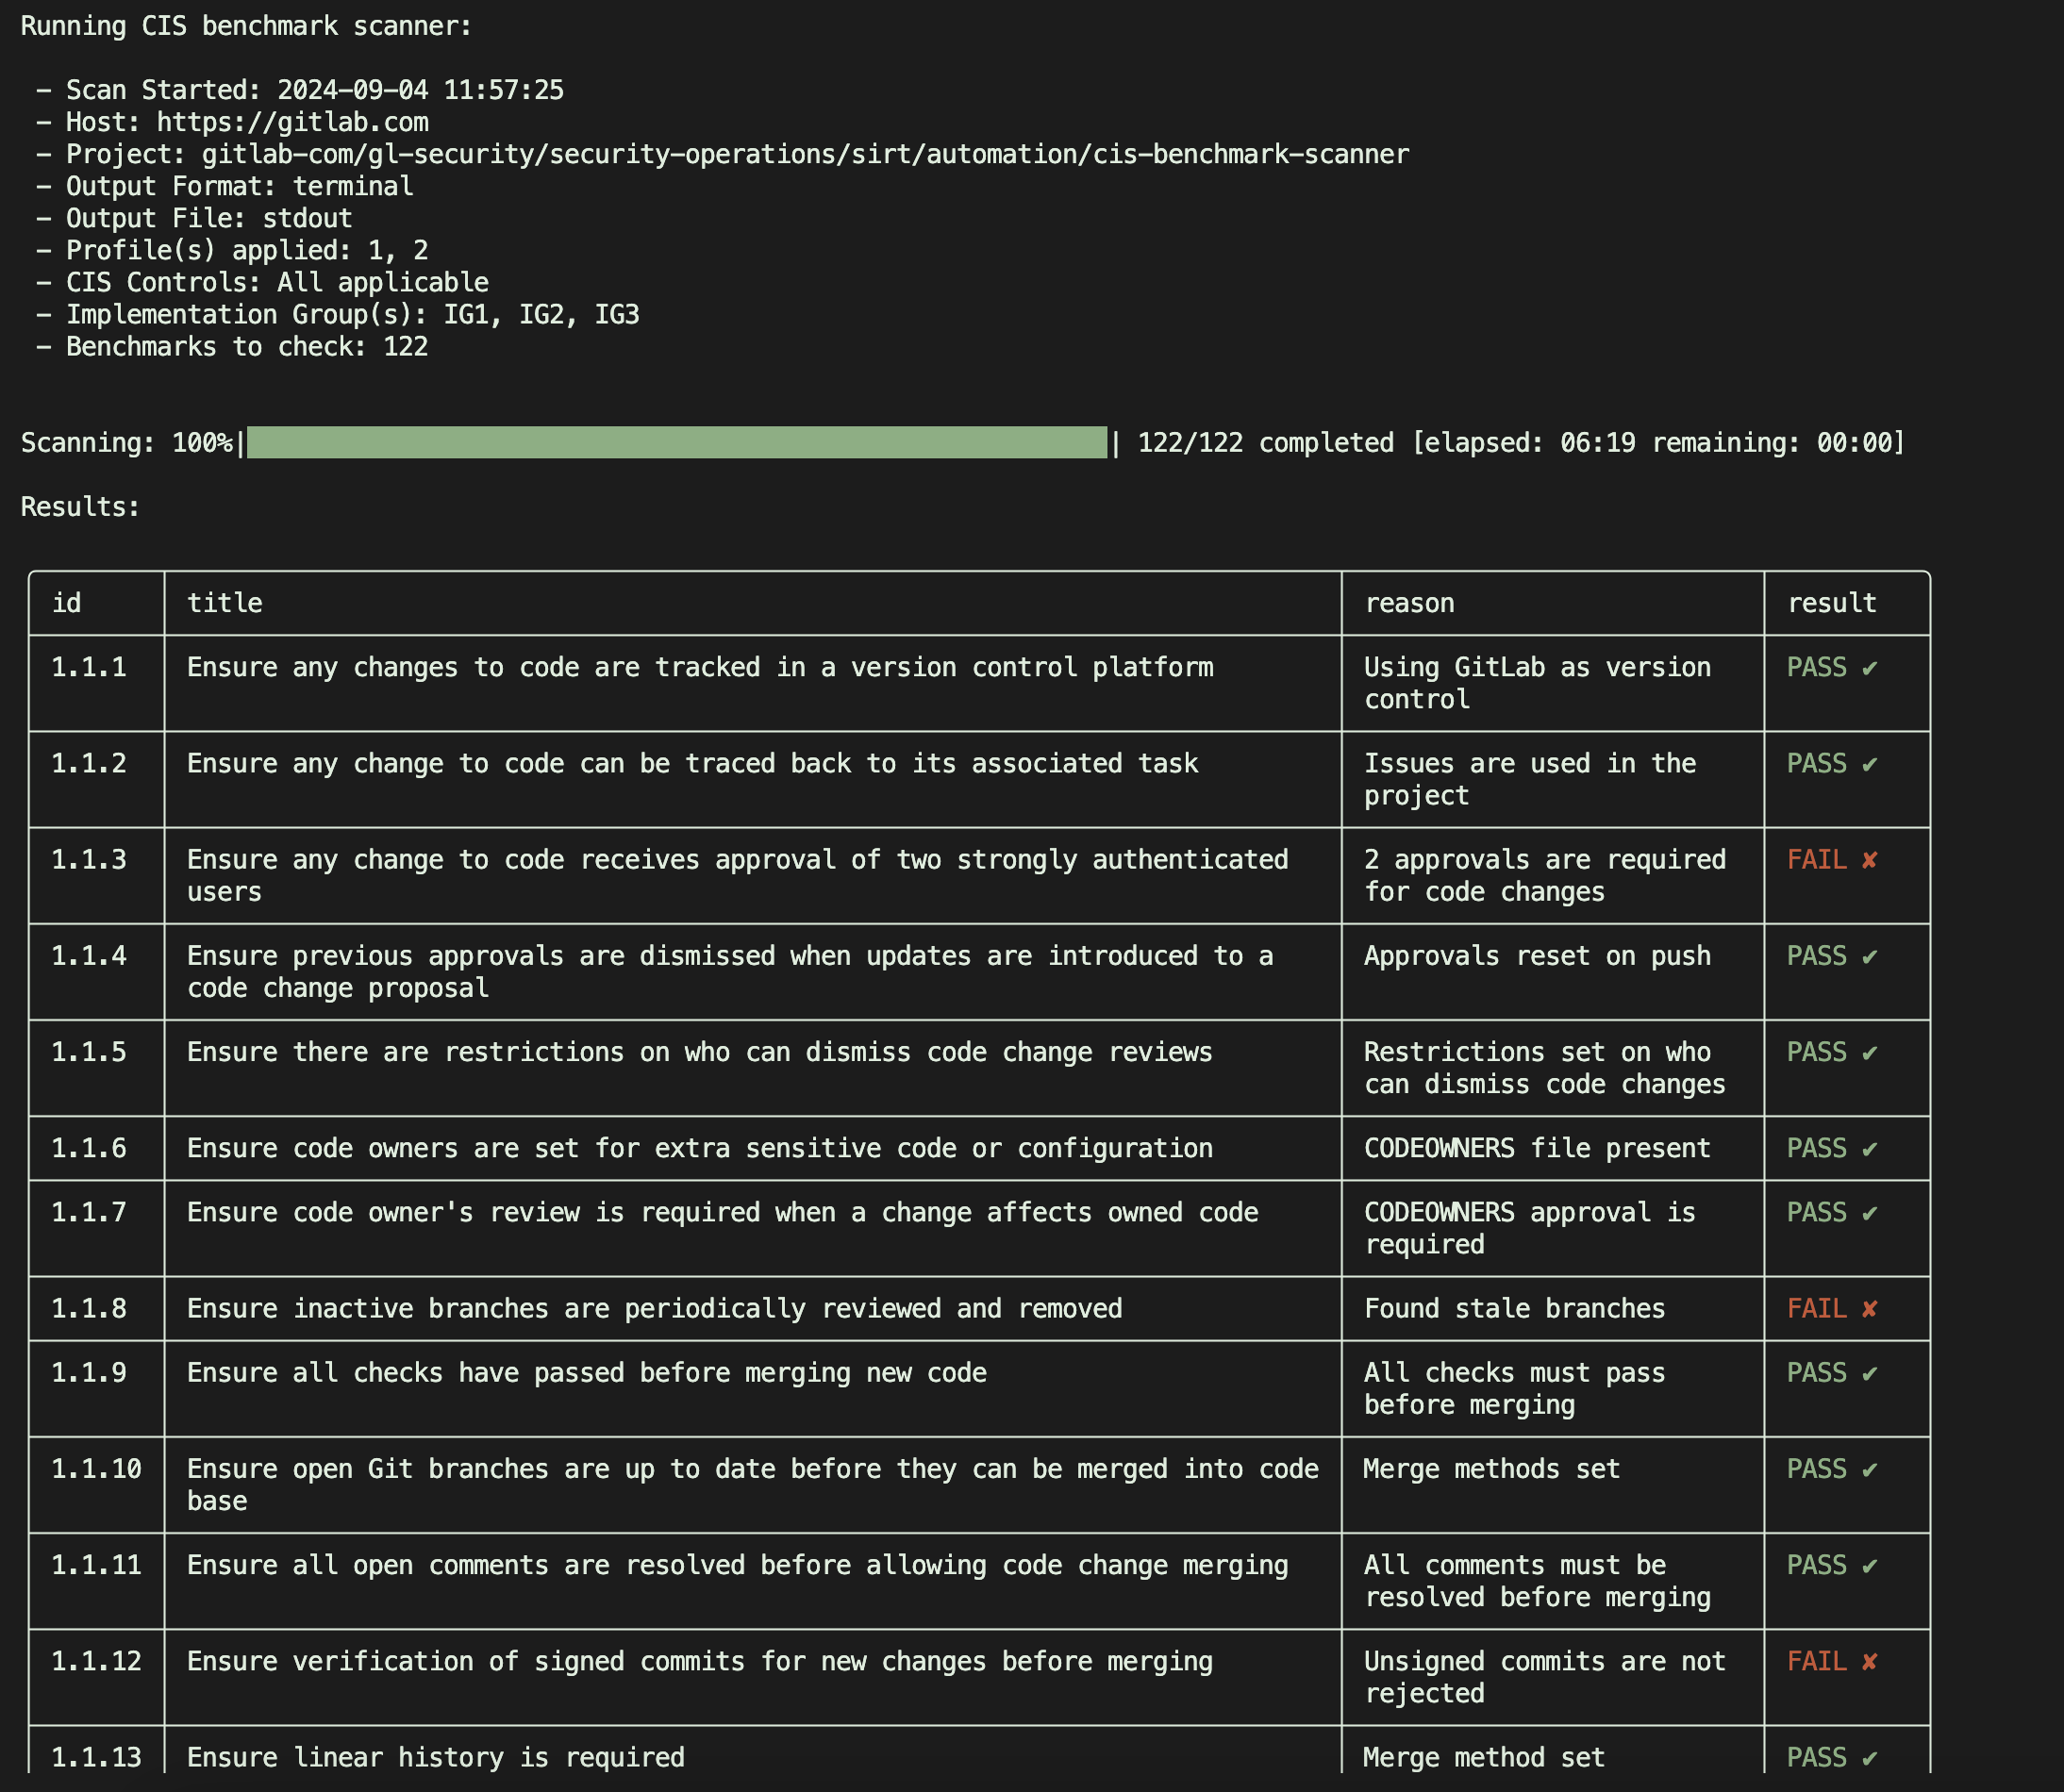 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…








