Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Categories

DevSecOps

Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.

Kitploit recommended

Top tools

10 selected
trivy preview#1

trivy

GitHubaquasecurity/trivy
37.4k0 days ago
semgrep preview#2

semgrep

GitHubsemgrep/semgrep
16.2k1 day ago
gitleaks preview#3

gitleaks

GitHubgitleaks/gitleaks
28.6k2 months ago
trufflehog preview#4

trufflehog

GitHubtrufflesecurity/trufflehog
27.4k6h 49m ago
checkov preview#5

checkov

GitHubbridgecrewio/checkov
8.9k6 days ago
grype preview#6

grype

GitHubanchore/grype
12.7k5 days ago
syft preview#7

syft

GitHubanchore/syft
9.6k13h 29m ago
dependency-track preview#8

dependency-track

GitHubdependencytrack/dependency-track
4.1k18h 56m ago
DependencyCheck preview#9

DependencyCheck

GitHubdependency-check/dependencycheck
7.7k9h 57m ago
osv-scanner preview#10

osv-scanner

GitHubgoogle/osv-scanner
10.8k1 day ago
NewestRelevanceMost popularRecently updated
1004 results
OpenShell preview

OpenShell

GitHubnvidia/openshell

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
authentication-authorizationdefensive-toolscontainer-security+7
8.8k9h 42m ago
Aegis-releases preview

Aegis-releases

GitHubadarsh14734/aegis-releases

Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
authentication-authorizationdefensive-toolsconfiguration-auditing+5
7 days ago
agent preview

agent

GitHubbomfather/agent

eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
defensive-toolscontainer-securityconfiguration-auditing+2
289 days ago
CVE-2026-24733 preview

CVE-2026-24733

GitHubdarabium/cve-2026-24733

Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
defensive-toolsvulnerability-scannersvulnerability-analysis+4
9 days ago
runeward preview

runeward

GitHubrunewardd/runeward

Governed execution cells for AI agents.
authentication-authorizationdefensive-toolscontainer-security+7
14 days ago
log4shell-CVE-2021-44228 preview

log4shell-CVE-2021-44228

GitHubrh-rahulshetty/log4shell-cve-2021-44228

Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…

static-code-analysisvulnerability-analysiscode-analysis+4
9 days ago
TriSuElla-AIDLCA-Framework preview

TriSuElla-AIDLCA-Framework

GitHubowasp/trisuella-aidlca-framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
static-code-analysisvulnerability-analysiscode-analysis+7
29 days ago
claude-code-security-audit preview

claude-code-security-audit

GitHubabhishek2512mishra/claude-code-security-audit

Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
defensive-toolsstatic-analysisvulnerability-scanners+5
10 days ago
owasp-aibom preview

owasp-aibom

GitHubowasp/owasp-aibom

OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
vulnerability-analysisdevsecopssupply-chain-security+3
1212 days ago
alibi preview

alibi

GitHubowasp-noir/alibi

Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
defensive-toolsreconnaissancestatic-analysis+7
1013 days ago
CVE-2026-0303 preview

CVE-2026-0303

GitHubyonliud/cve-2026-0303

Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
static-analysisvulnerability-analysiscode-analysis+5
13 days ago
geiger preview

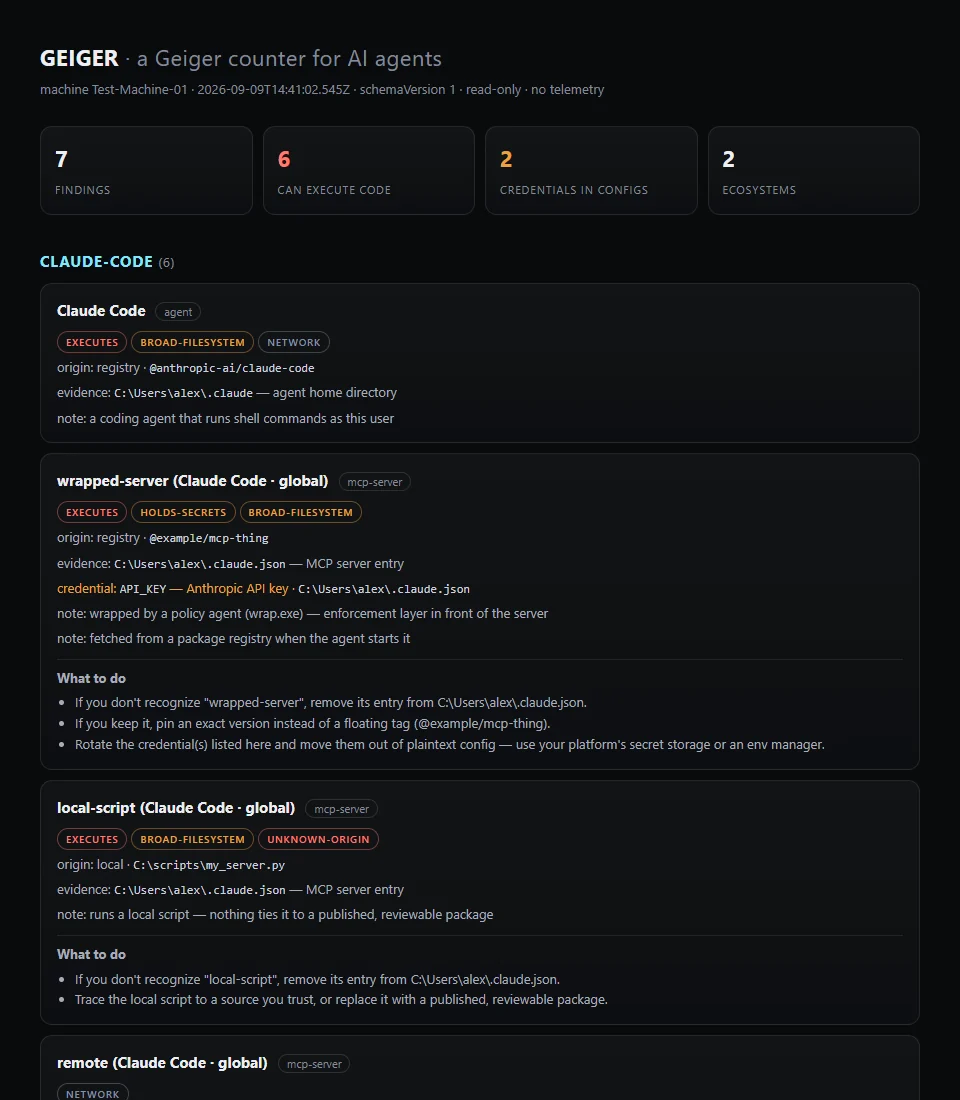
geiger

GitHubatomburstofficial/geiger

Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
configuration-auditingcloud-securitydevsecops+2
13811 days ago
openshield preview

openshield

GitHubowasp/openshield

Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…

vulnerability-scannersconfiguration-auditingcryptography+4
568 days ago
sast-scan-action preview

sast-scan-action

GitHuboffensive360/sast-scan-action

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.

vulnerability-scannersstatic-code-analysiscode-analysis+4
1 month ago
mcp-server preview

mcp-server

GitHuboffensive360/mcp-server

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
static-code-analysisvulnerability-analysiscode-analysis+3
1 month ago
sift-hardened preview

sift-hardened

GitHublgranadoi/sift-hardened

Security-hardened fork of sift 17.1.3 for CVE-2026-85625. Not affiliated with crcn/sift.js.
static-analysisvulnerability-analysiscode-analysis+2
15 days ago
guardskill preview

guardskill

GitHubsoemoescode/guardskill

Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
static-analysisvulnerability-scannerscode-analysis+4
19 days ago
netty-http-check preview

netty-http-check

GitHubxiaoqimikko/netty-http-check

Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…

static-analysisvulnerability-scannersconfiguration-auditing+3
14 days ago
Previous123…56Next