
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended

 google/clusterfuzzlite
Continuous fuzzing solution integrated into CI workflows to find vulnerabilities in code changes and batch runs, supporting multiple languages and CI…

 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 dev-sec/mysql-baseline
DevSec MySQL Baseline - InSpec Profile
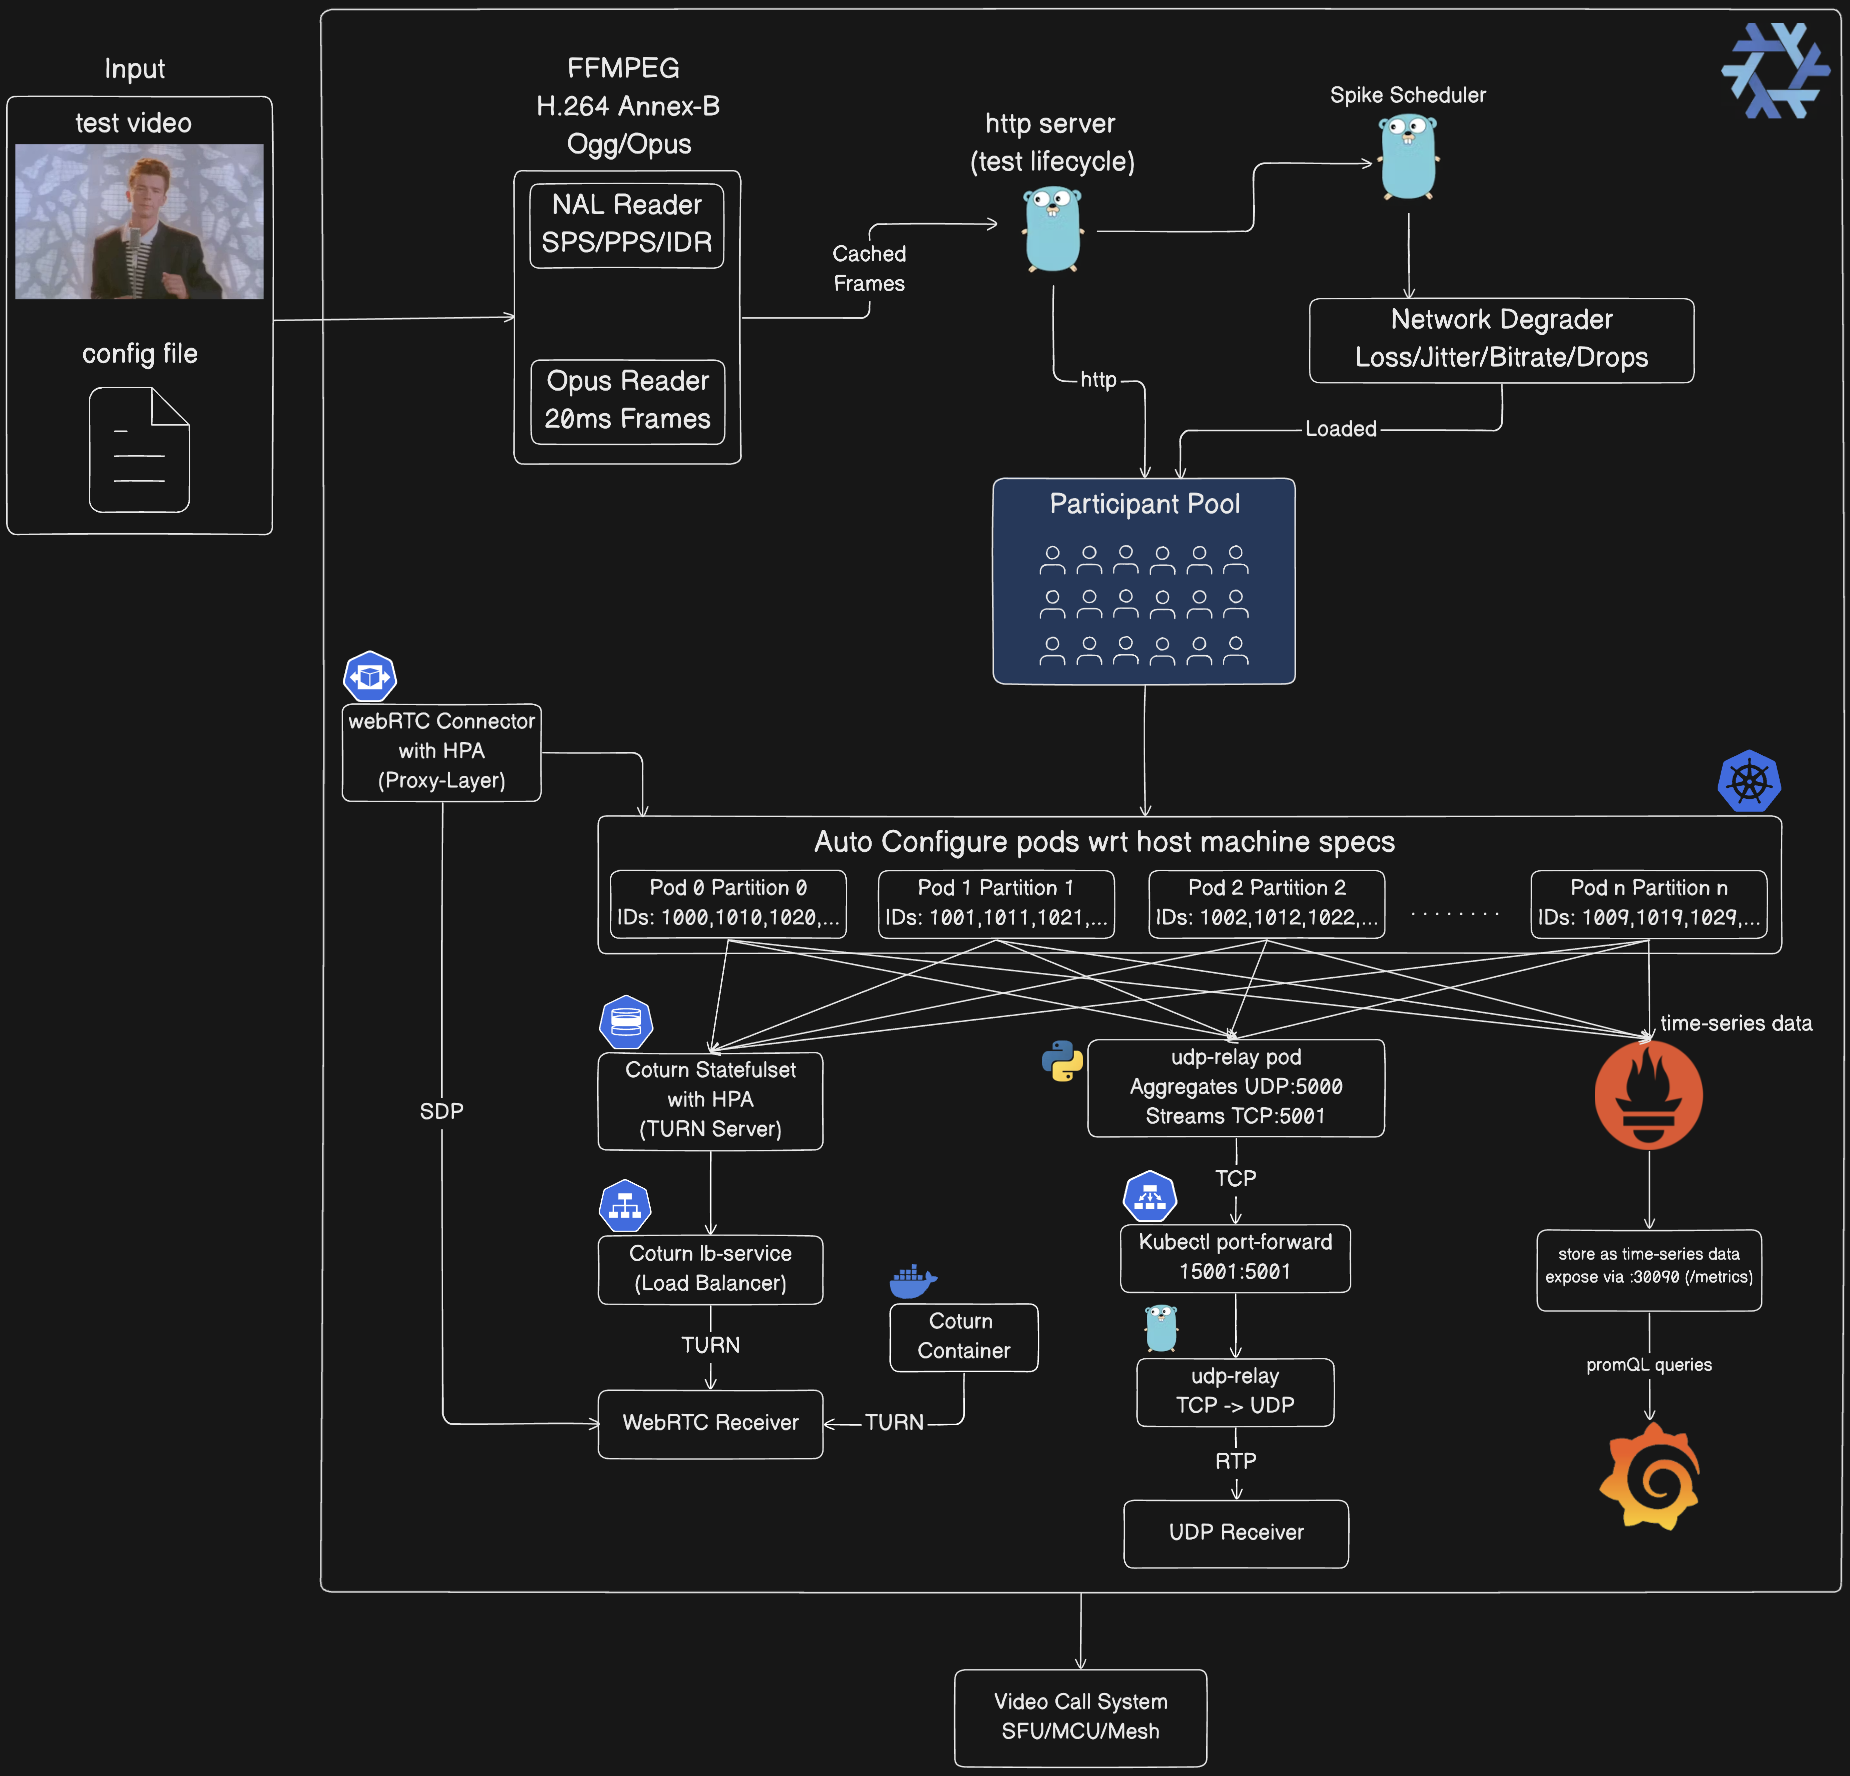 mdsadiqmd/av-chaos-monkey
Chaos Monkey but for Audio Video Testing (webRTC and UDP)
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.

 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 nccgroup/matt.net
Matt.Net is a simple GUI wrapper around Microsoft's CAT.NET Code Auditing Tool
 spiarh/webhook-cve-2022-0811
Simple webhook to block exploitation of CVE-2022-0811
 jenkinsci-cert/security-3314-3315
Workaround for disabling the CLI to mitigate SECURITY-3314/CVE-2024-23897 and SECURITY-3315/CVE-2024-23898
 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 owasp/secureml
SecureML - Securing and Watermarking AL models








