
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit recommended
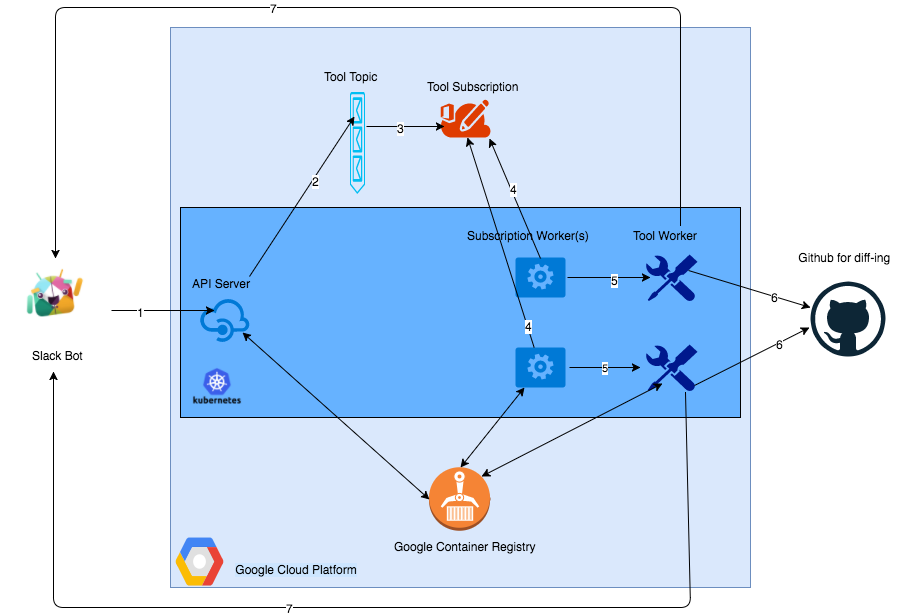
 anshumanbh/kubebot
A security testing Slackbot built with a Kubernetes backend on the Google Cloud Platform
 projectdiscovery/nuclei-templates-labs
Vulnerable environments paired with ready-to-use Nuclei templates for security testing and learning! 🚀
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 chris-anley/cq
CQ, a code security scanner
 xenoncyber/envy
A terminal based tool for managing secrets with both tui and cli support
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 glincker/sslx
A fast, modern alternative to OpenSSL's CLI - inspect, grade, and manage certificates from the terminal
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 gubiczap/cve-2026-31431-checker
Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…
 jpmartins/minimalreproducer
Context of CVE-2021-26291 minimal replicator
 istenrot/centos-dirty-cow-ansible
Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP

 sonarsource/sonarcloud-scan
A Bitbucket Pipe to trigger SonarCloud analysis
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 linko-iheb/cve-2026-41940-scanner
Passive, read-only vulnerability scanner for detecting CVE-2026-41940 in cPanel & WHM. Performs version-based fingerprinting, generates…
 aestechno/cve-2026-31431-ansible
Ansible playbook to detect and apply kernel cmdline mitigation for CVE-2026-31431 (Copy Fail) across Debian/Ubuntu/RHEL fleets, with read-only…








