
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 openrce/pydbg
A pure-python win32 debugger interface.
 ebrandi/fdd-book
FreeBSD Device Driver Book
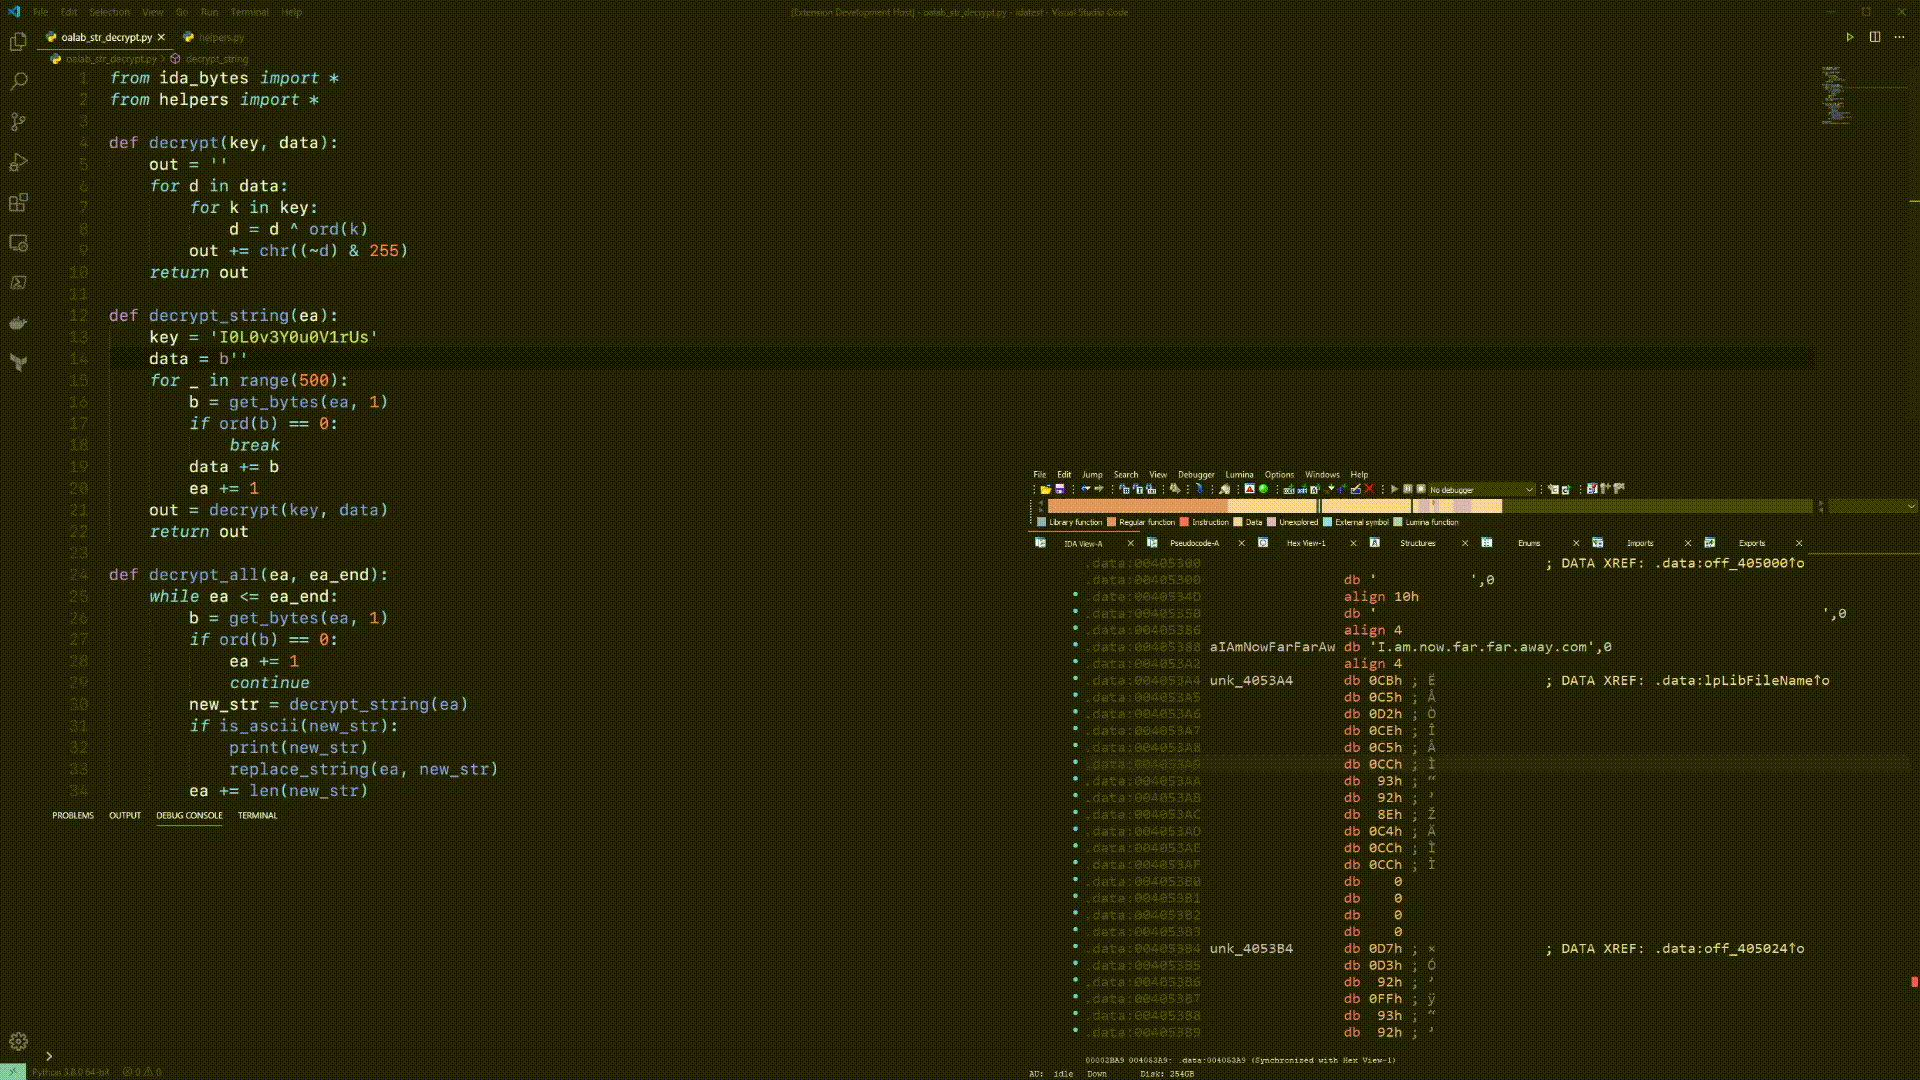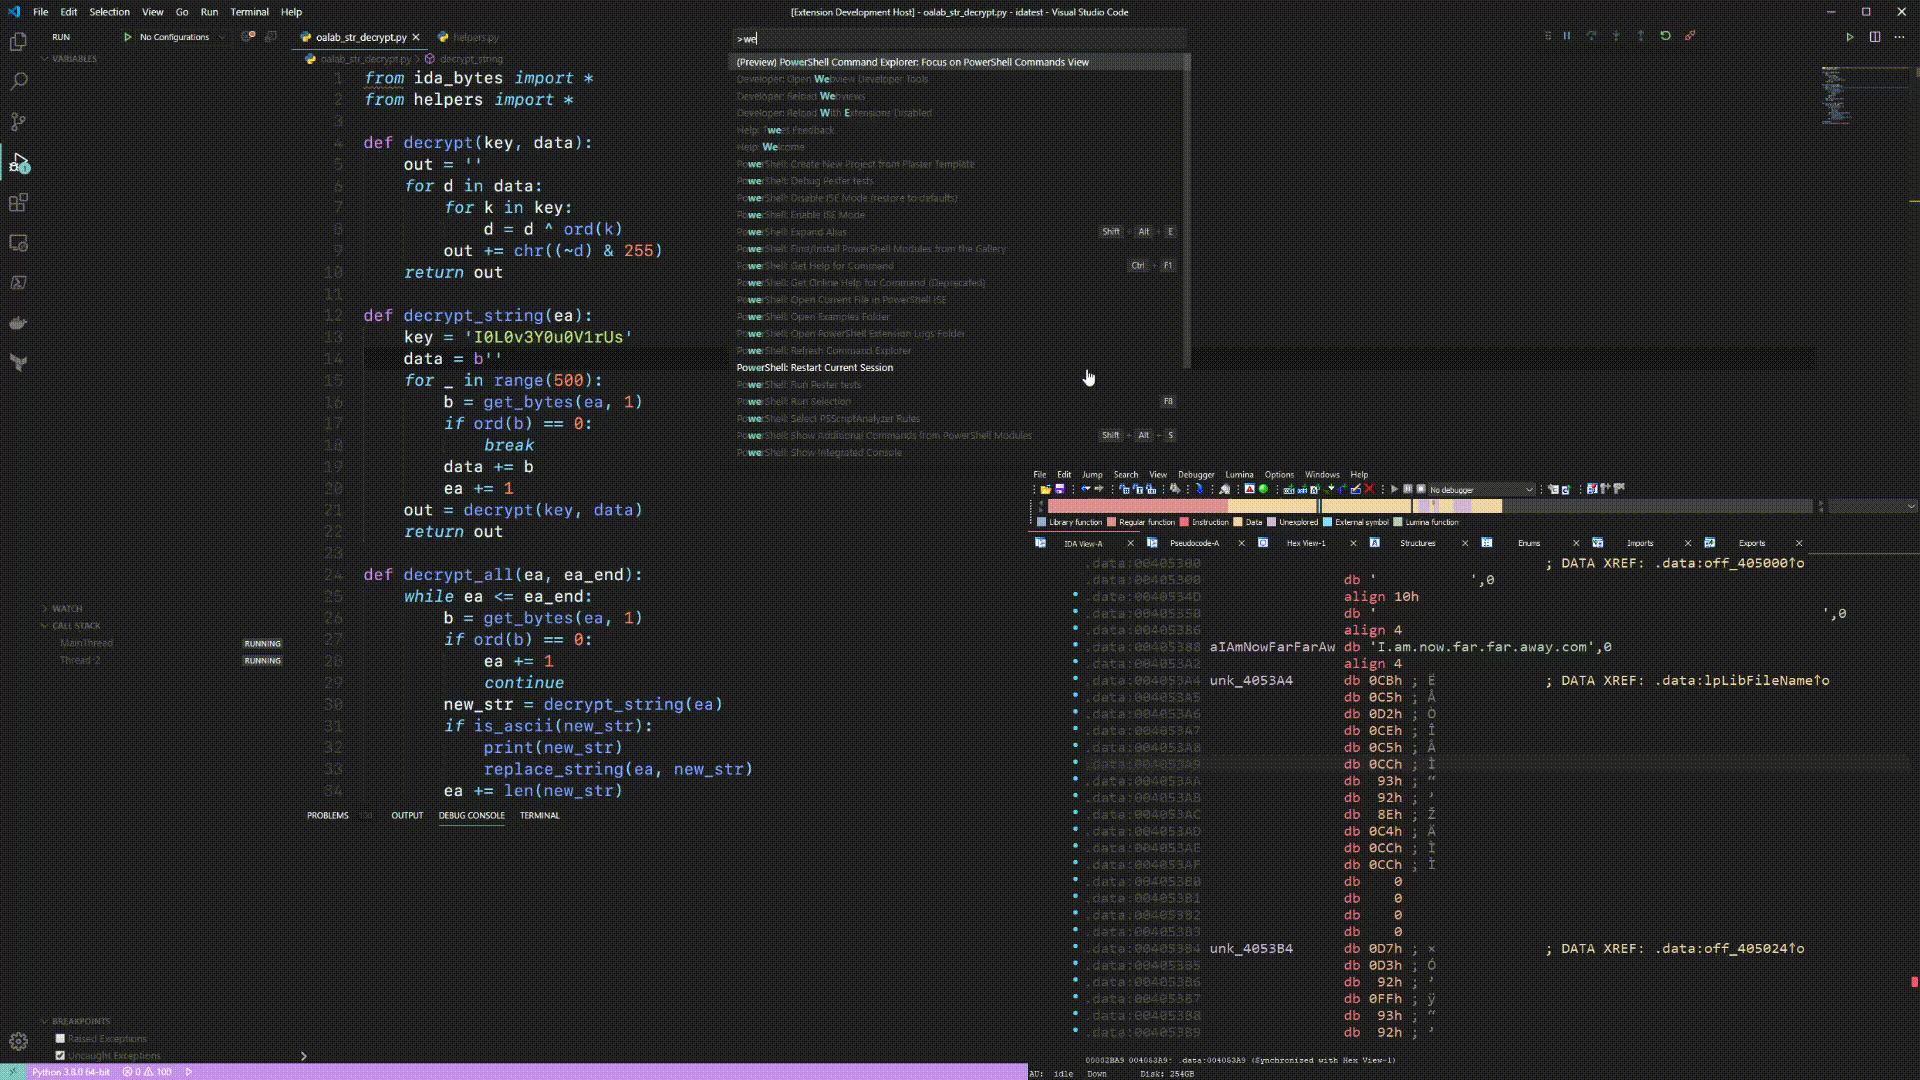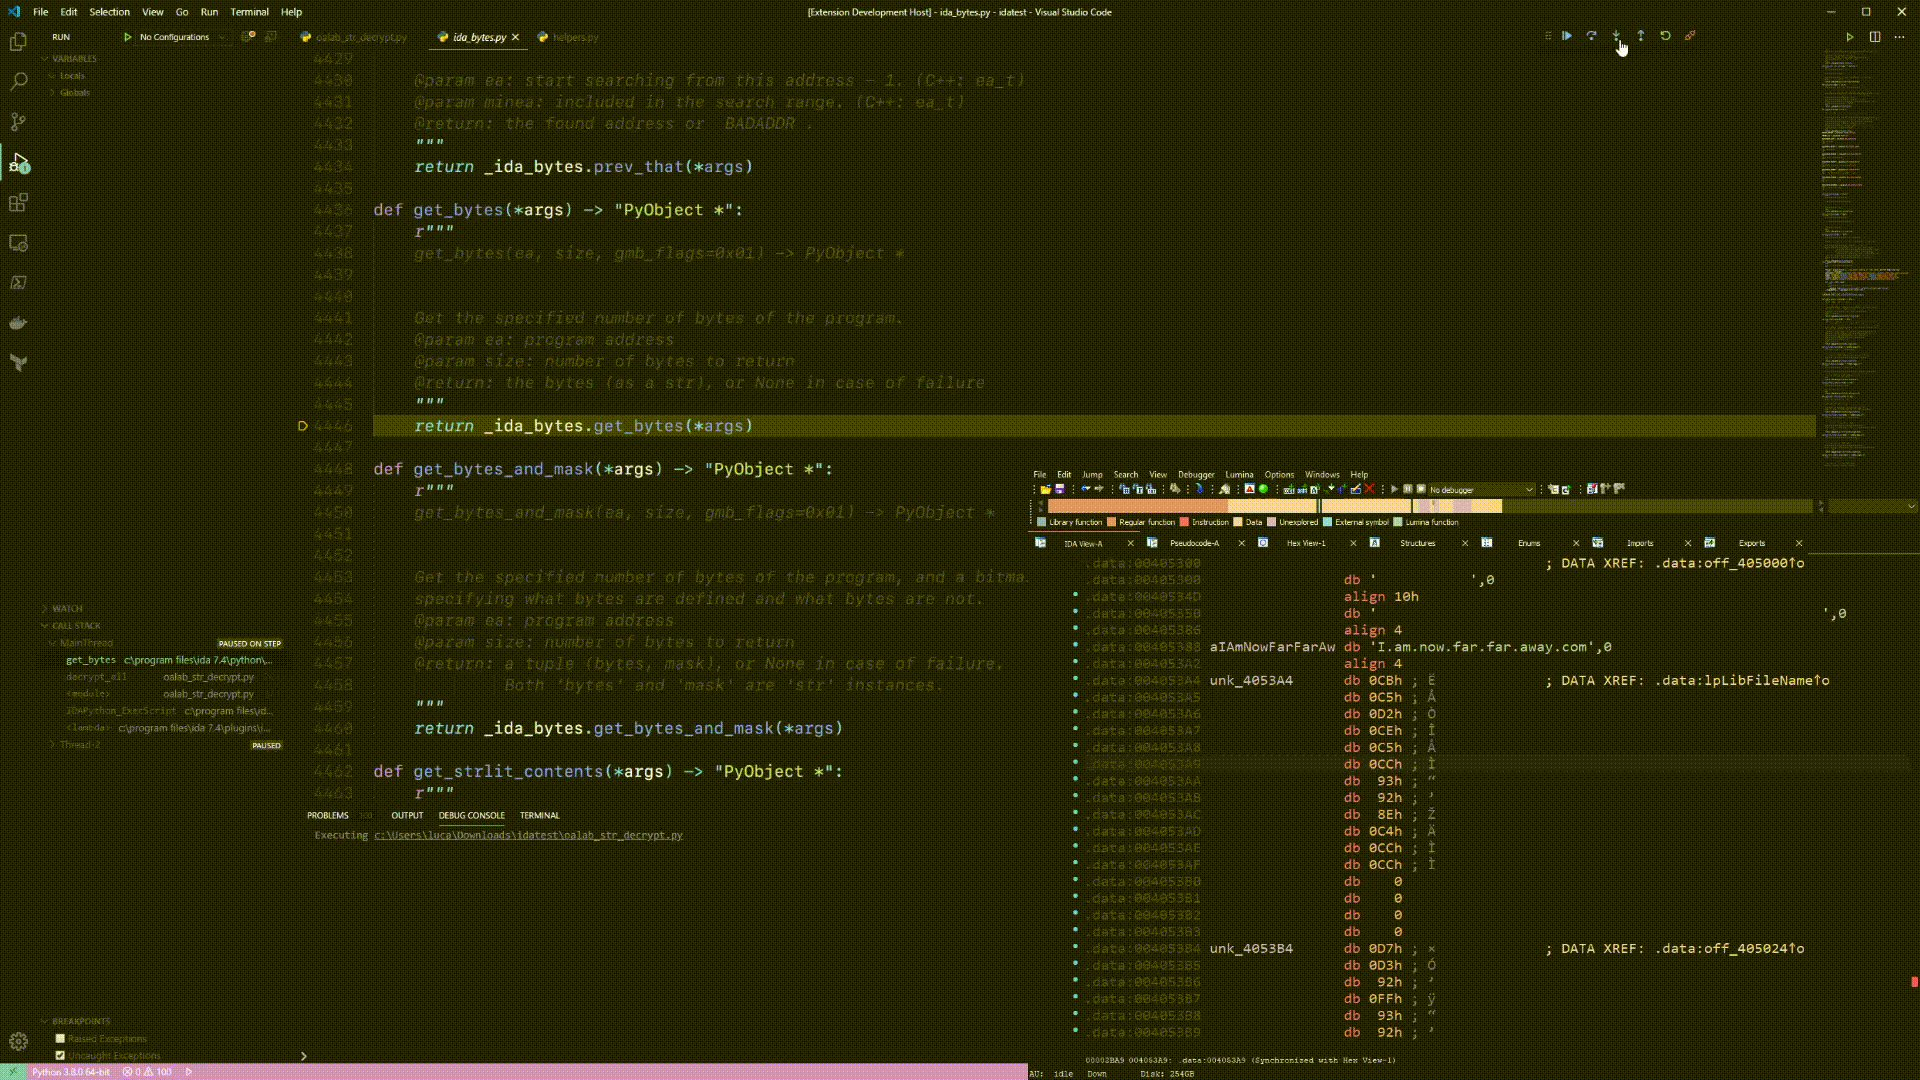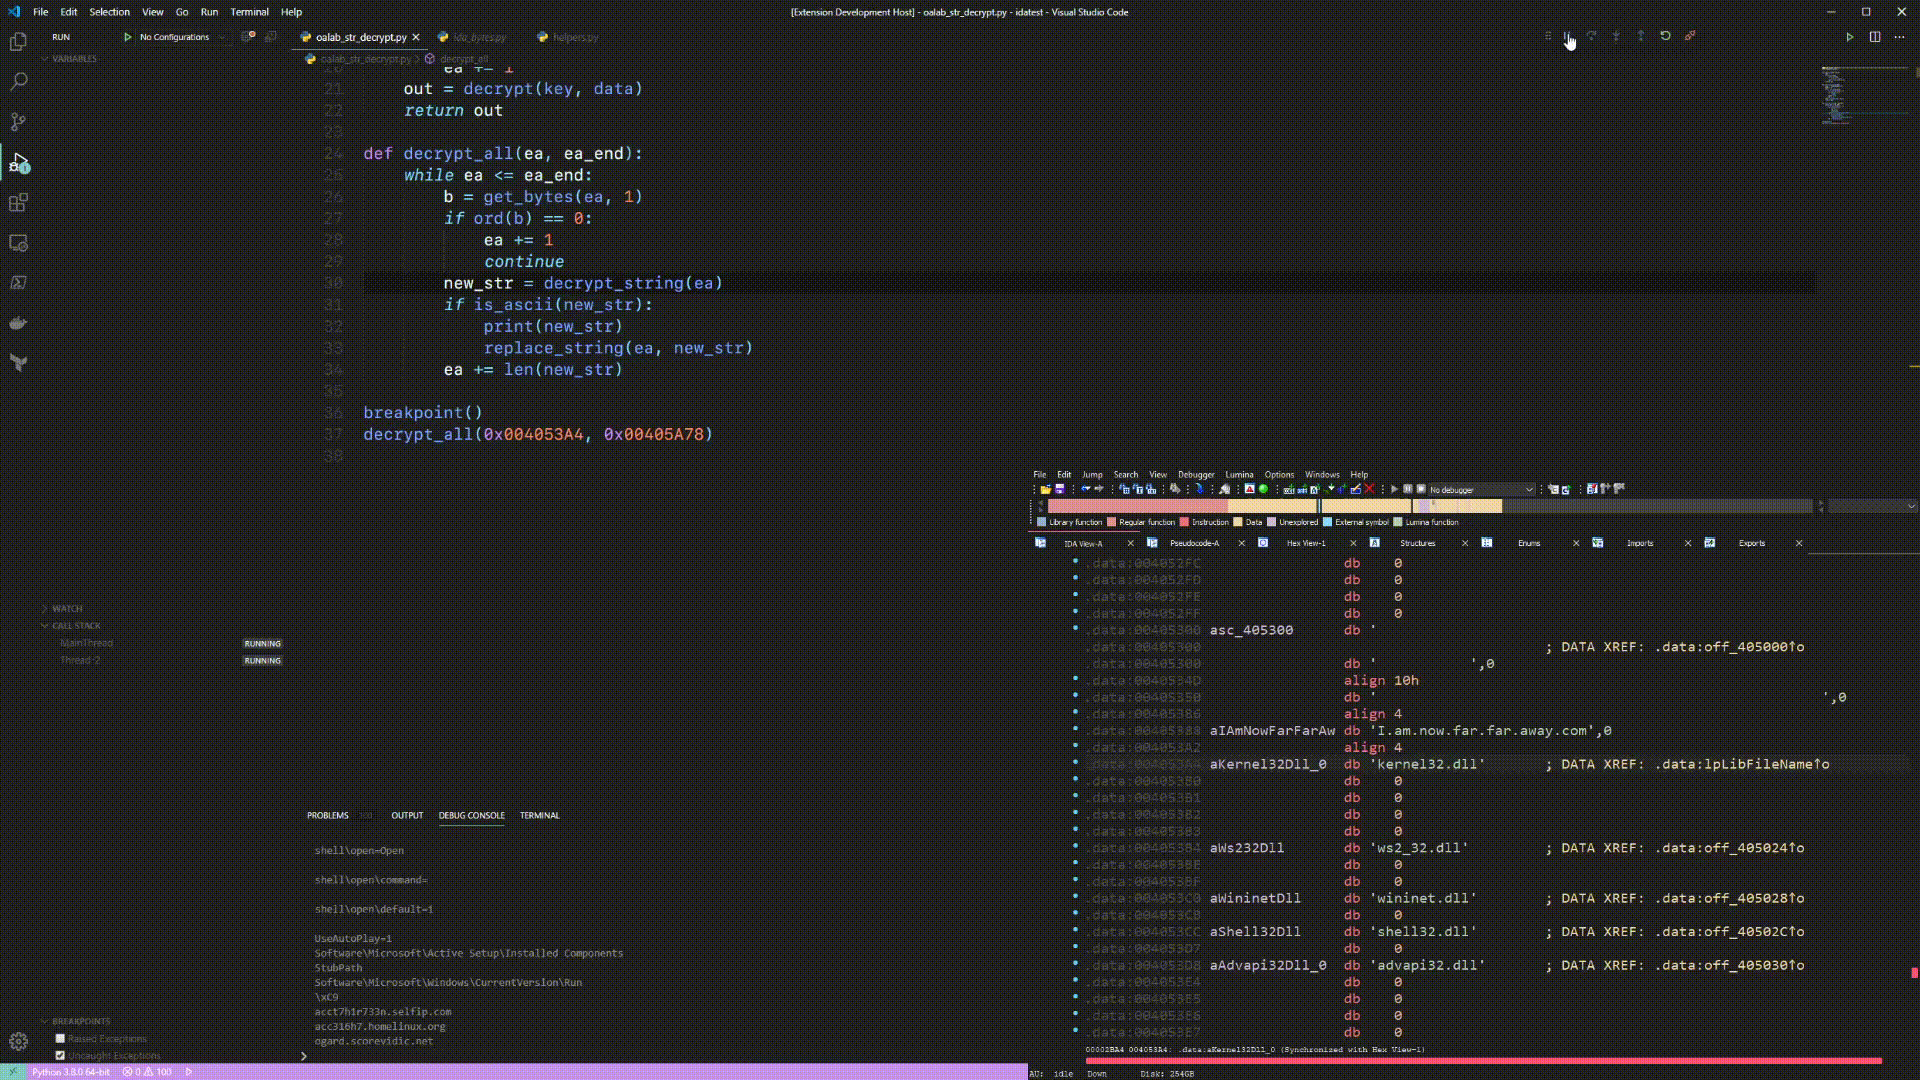 ioncodes/idacode
An integration for IDA and VS Code which connects both to easily execute and debug IDAPython scripts.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
 census/shadow
jemalloc heap exploitation framework
 secrary/makin
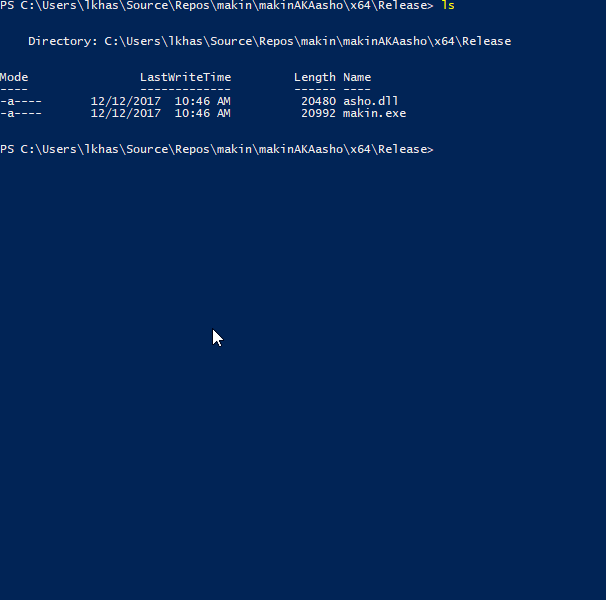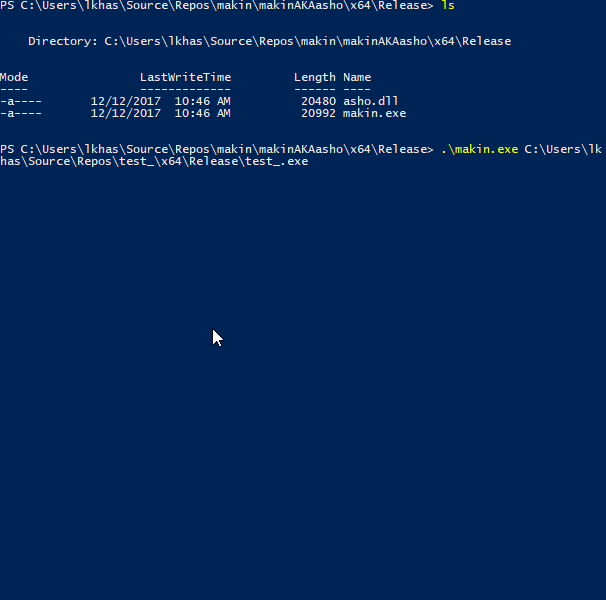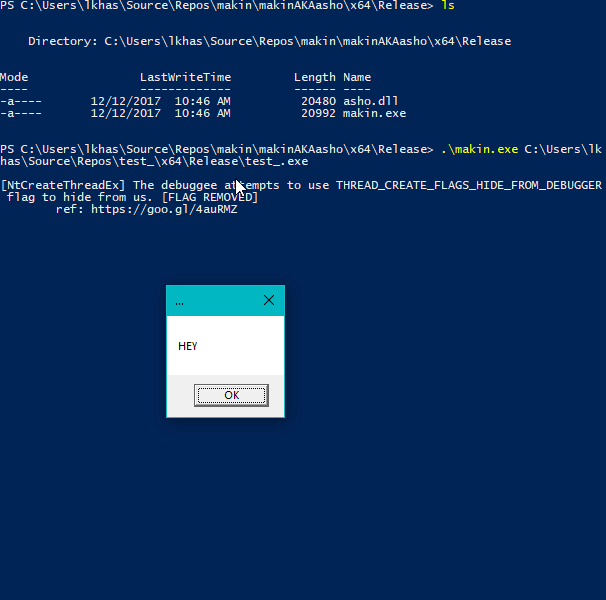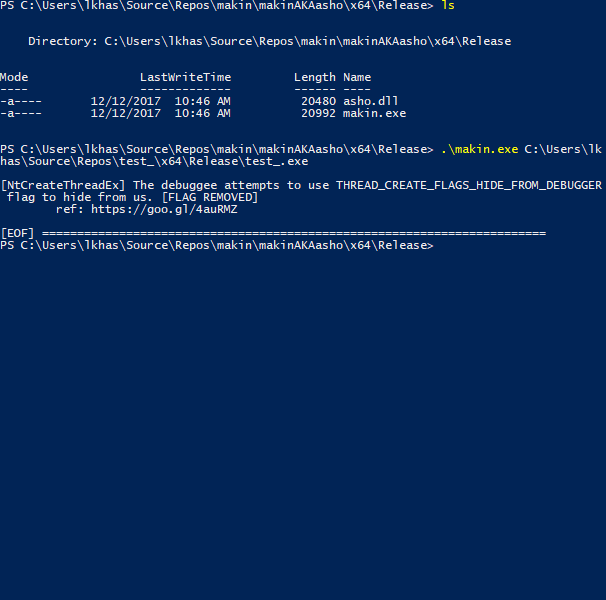
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
 brynary/rack-bug
Debugging toolbar for Rack applications implemented as middleware
 therealsaumil/static-arm-bins
Statically compiled ARM binaries for debugging and runtime analysis
 reyammer/shellnoob
A shellcode writing toolkit
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
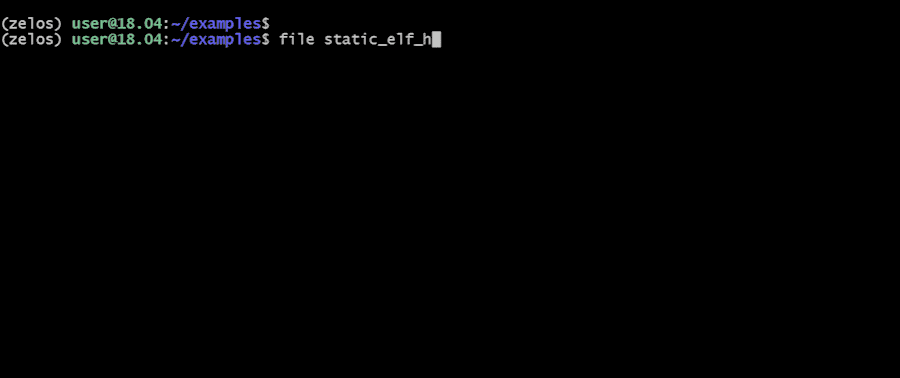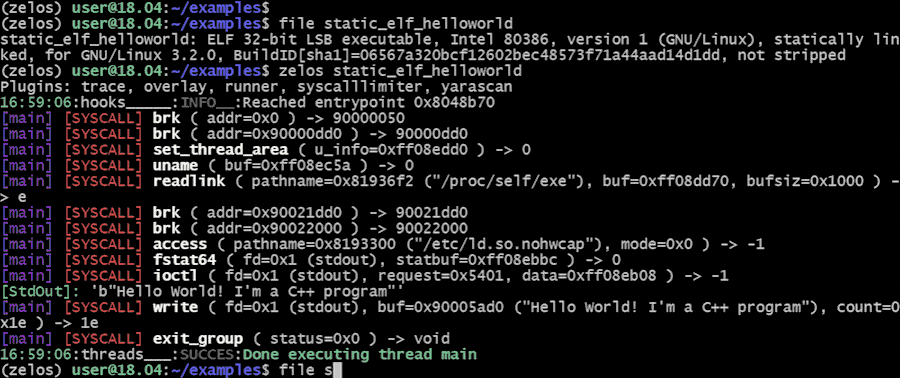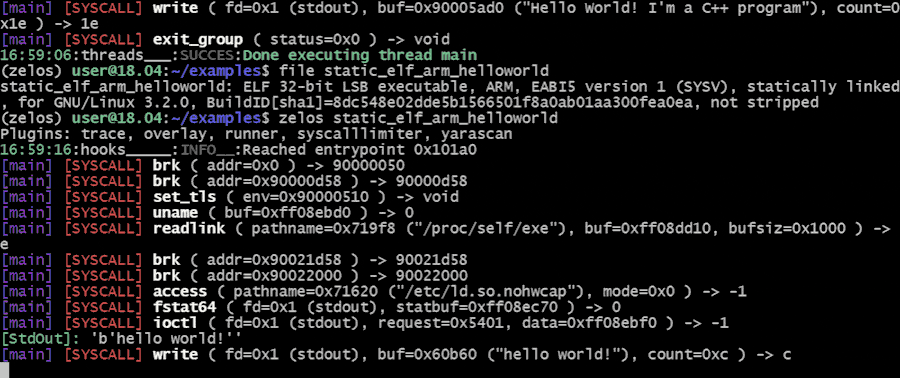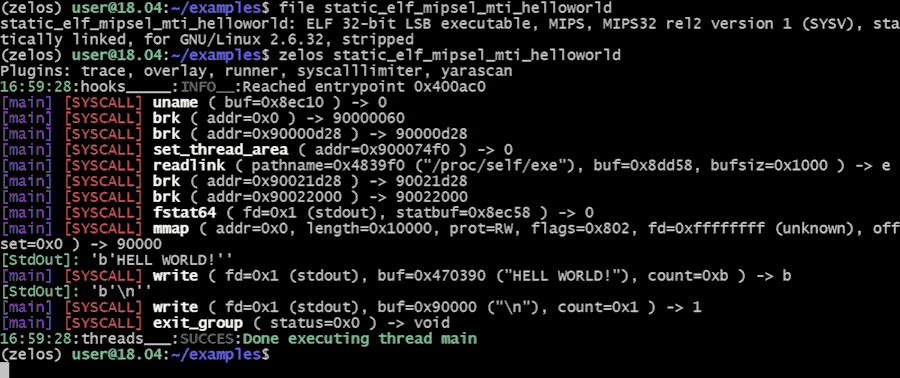 zeropointdynamics/zelos
A comprehensive binary emulation and instrumentation platform.
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
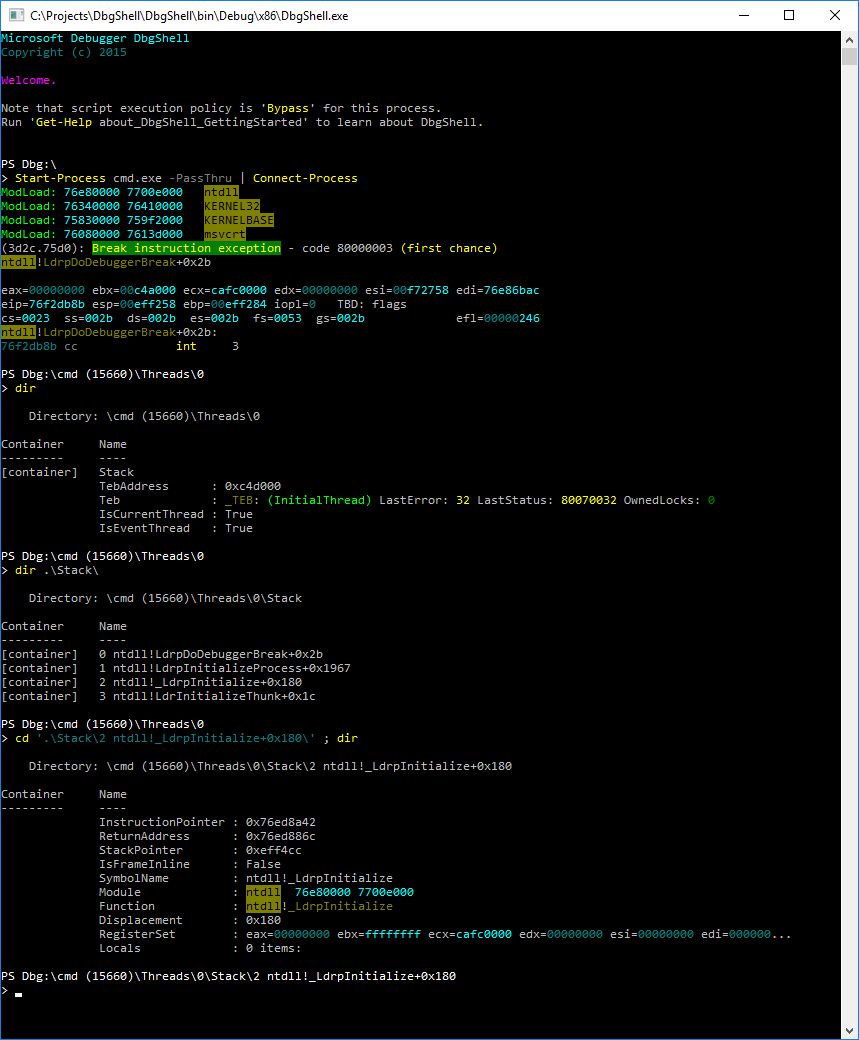 microsoft/dbgshell
A PowerShell front-end for the Windows debugger engine.








