
 #1
Debugging tools specifically for analyzing malware execution flow and identifying vulnerabilities.
Kitploit recommended

 das-labor/panopticon
A libre cross-platform disassembler.
 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
 macmade/unicorn-bios
Basic BIOS emulator for Unicorn Engine.
 madmin3r/unconfuserex
Deobfuscator for ConfuserEx 2.
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
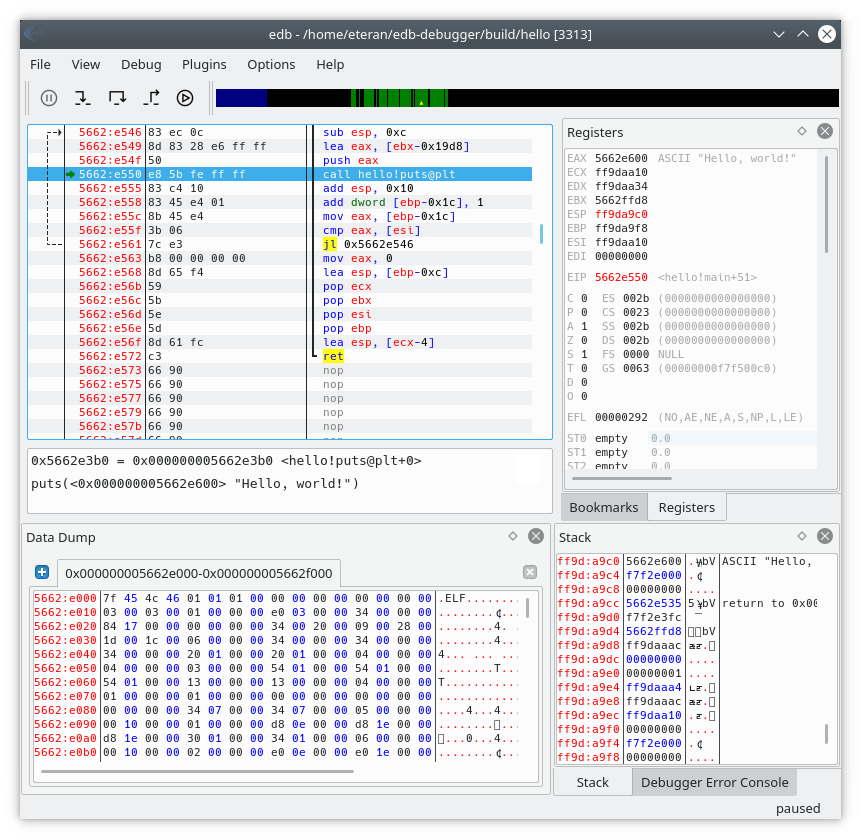 eteran/edb-debugger
edb is a cross-platform AArch32/x86/x86-64 debugger.
 ioncodes/idacode
An integration for IDA and VS Code which connects both to easily execute and debug IDAPython scripts.
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering








