
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 iriscouch/audit_couchdb
Detect security issues, large or small, in a CouchDB server
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
 sadshade/cve-2022-24706-couchdb-exploit
Apache CouchDB 3.2.1 - Remote Code Execution (RCE)
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 infobyte/isr-sqlget
ISR-sqlget It's a blind SQL injection tool developed in Perl.
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
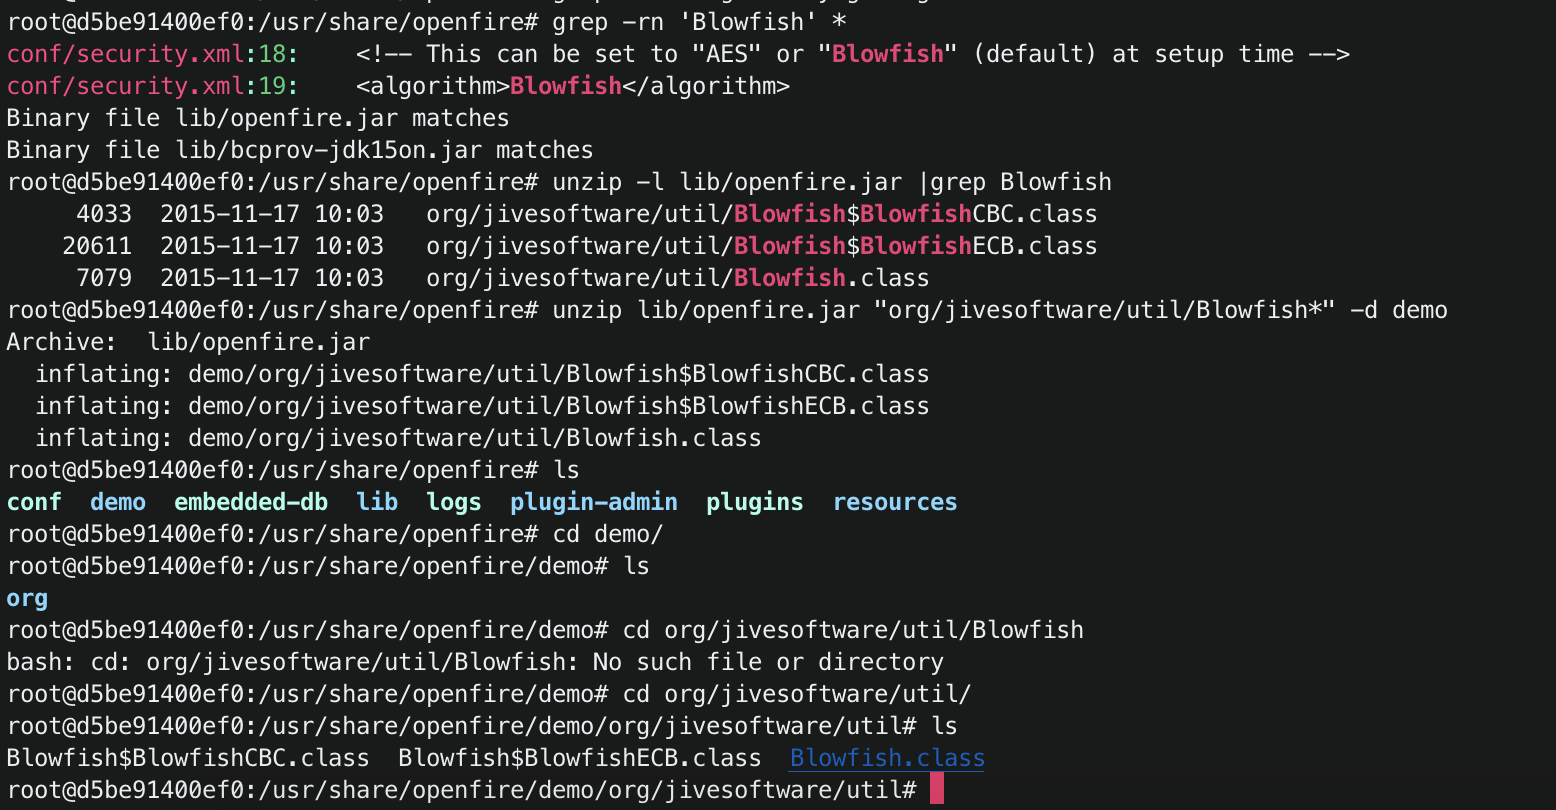 jas502n/openfire_decrypt
OpenFire 管理后台账号密码解密
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 probiusofficial/cve-2025-14847
poc for CVE-2025-14847
 t0x1cx/cve-2021-36396-moodle-time-based-sqli-exploit
This script demonstrates a time-based blind SQL injection on Moodle platforms, exploiting response delays to extract data.
 deepingh0st/cve-2022-28346
Django QuerySet.annotate(), aggregate(), extra() SQL 注入
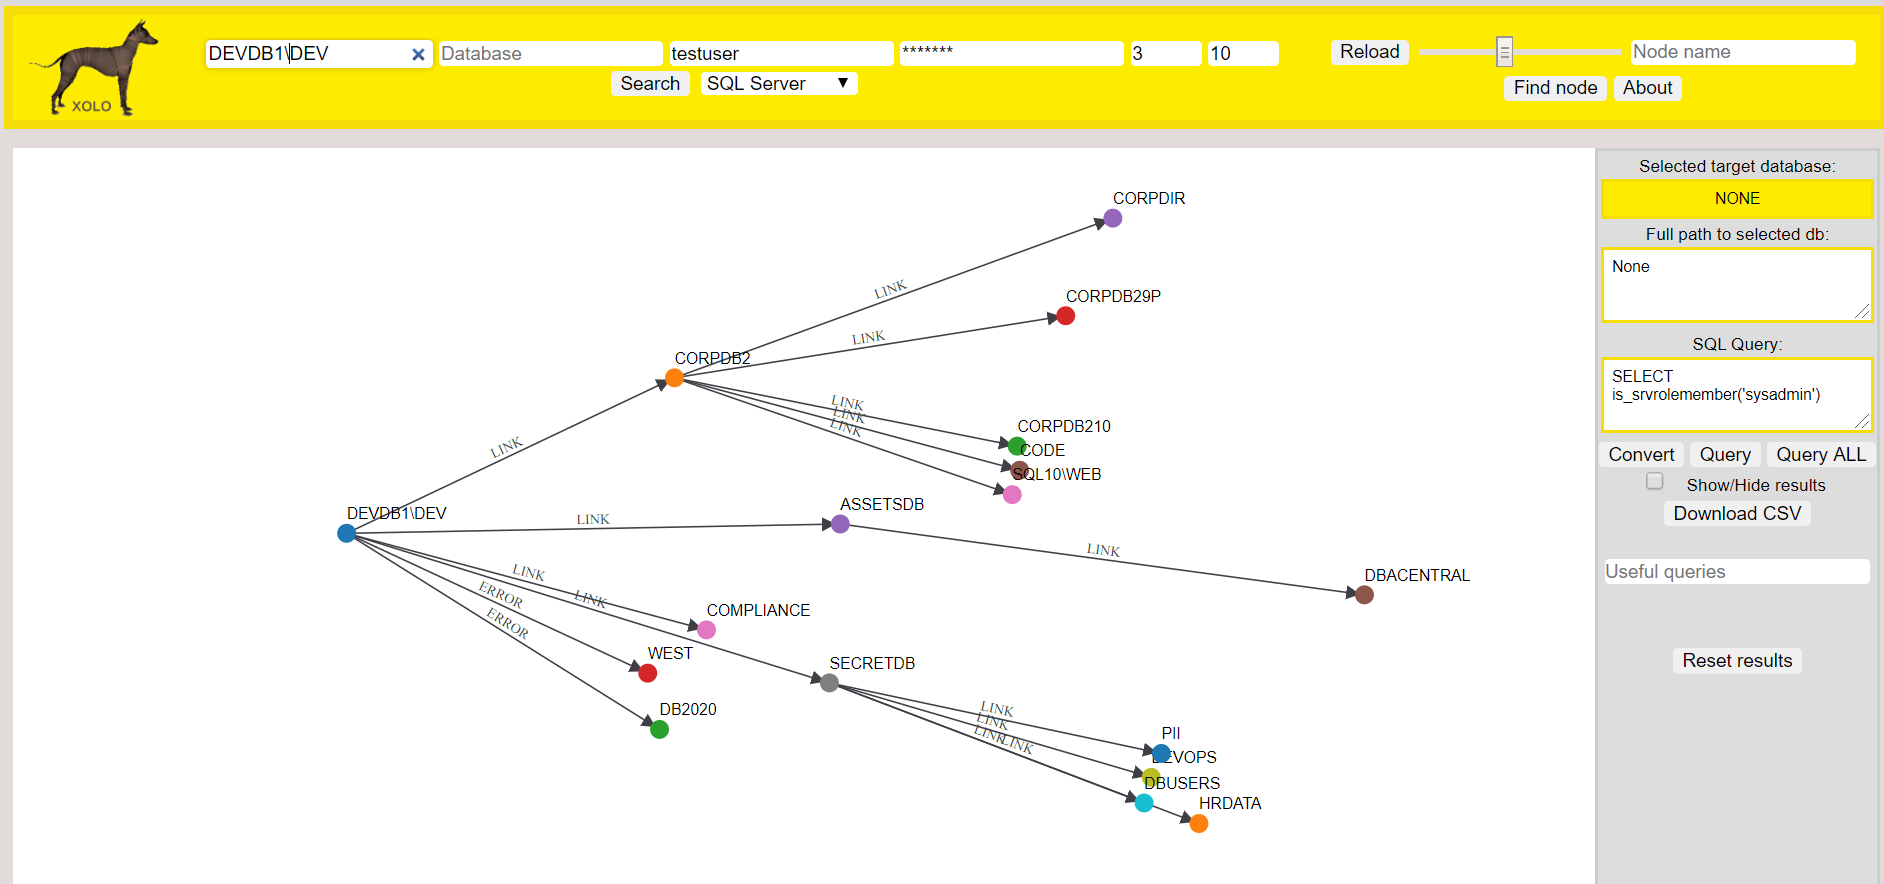 etlownoise/xolo
Tool to crawl, visualize and interact with SQL server links in a d3 graph to help in your red/blue/purple/.../risk assessments pentest hacking team…
 b4kesn4ke/cve-2019-9193
CVE-2019–9193 - PostgreSQL 9.3-12.3 Authenticated Remote Code Execution
 ashrafdev/mysql-remote-root-code-execution
0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server








