
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 citcheese/odbparser
OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing
 al1ex/cve-2021-27928
CVE-2021-27928 MariaDB/MySQL-'wsrep provider' 命令注入漏洞
 dwisiswant0/cve-2025-49844
Proof-of-concept exploit for Redis 8.2.1 Lua parser use-after-free, racing garbage collection via crafted loadstring calls to achieve remote code…
 mhaskar/blinder
A python library to automate time-based blind SQL injection
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 lorenzotullini/influxdb-exploit-cve-2019-20933
InfluxDB CVE-2019-20933 vulnerability exploit
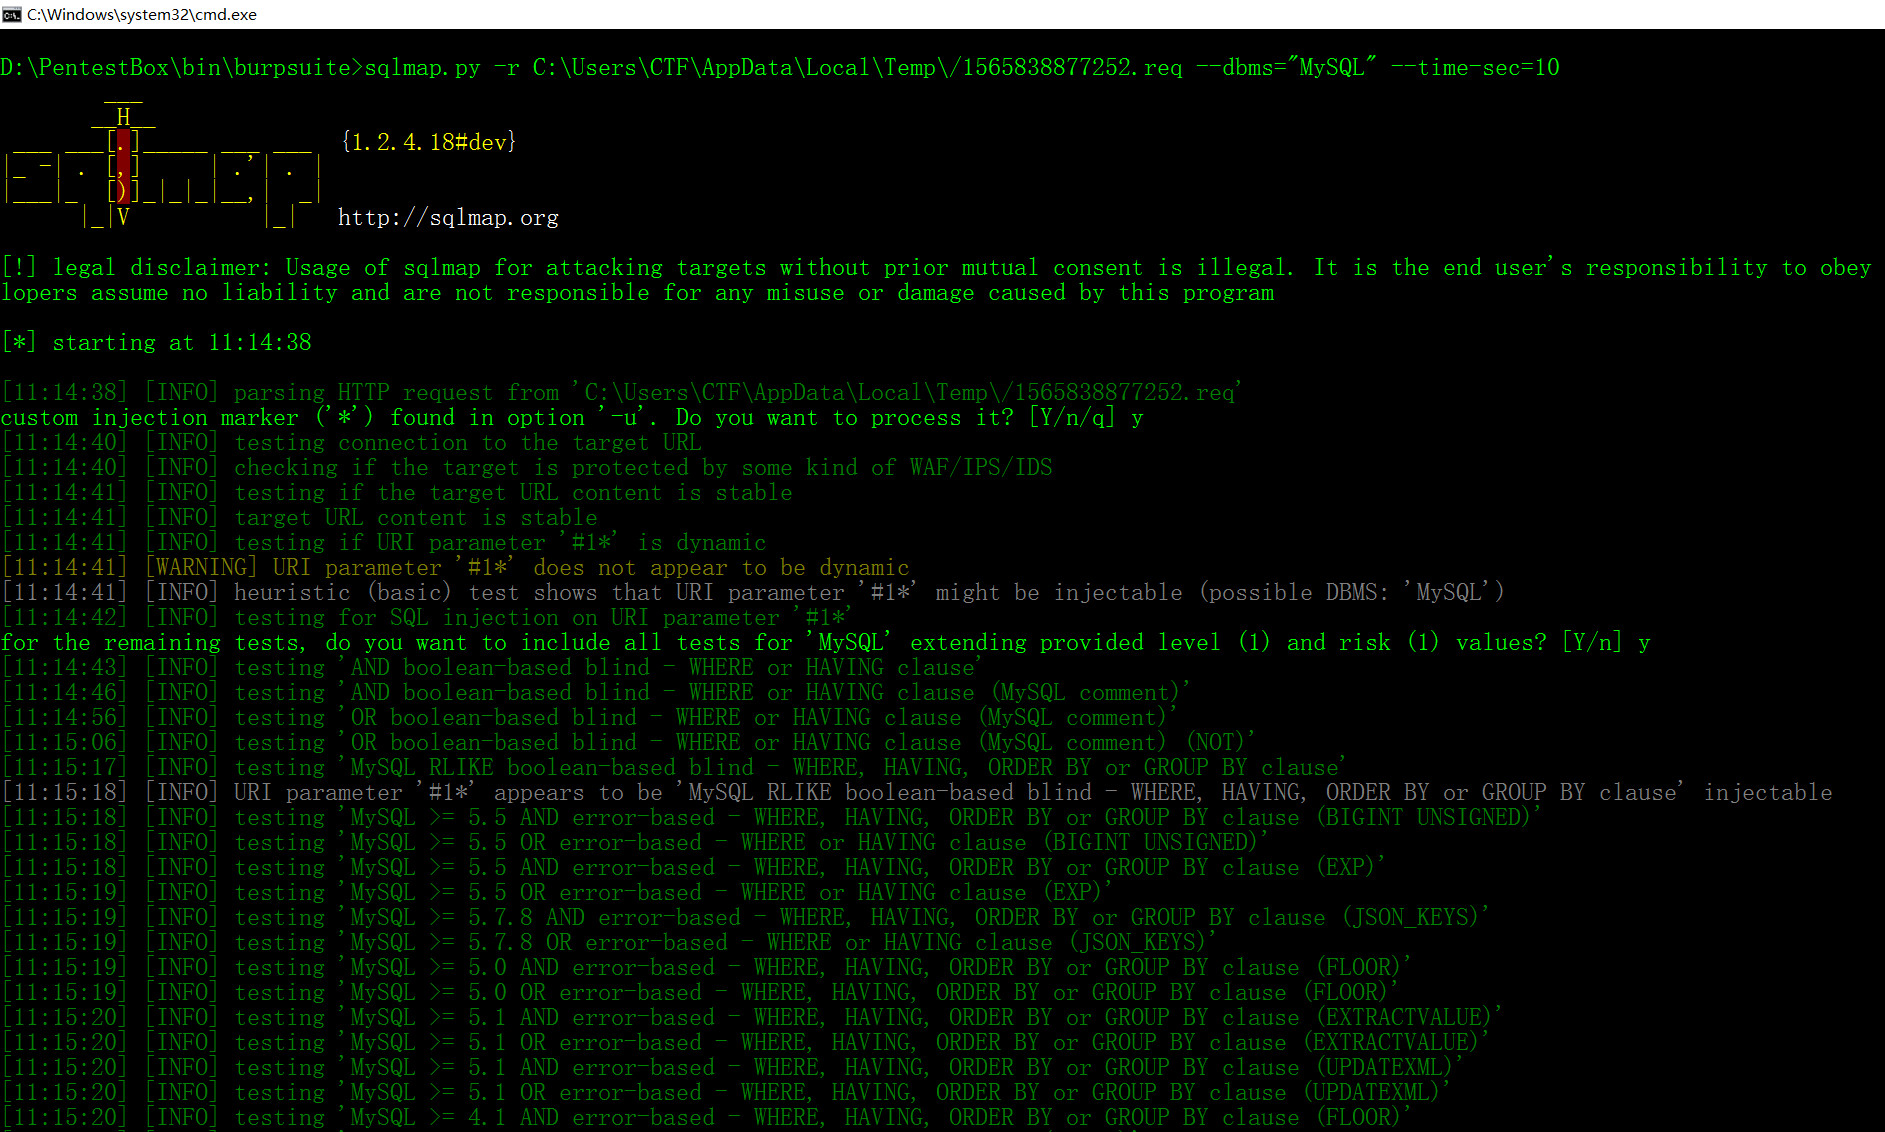 jas502n/sqlmap_burpsuite
SqlMap_BurpSuite
 daniel2005d/mapxplore
Allow exporting the information downloaded with sqlmap to a relational Database like Postgres and sqlite
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
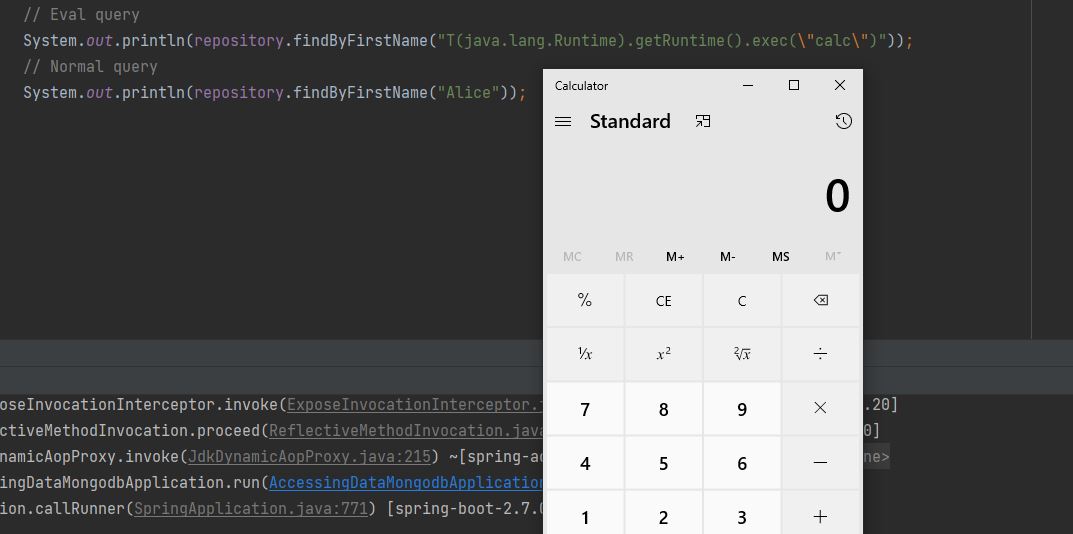 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
 codelatteid/carina
Webshell, Virtual Private Server (VPS) and cPanel Database
 jas502n/mssql-command-tool
mssql 终端连接工具|命令执行
 var77/cve-2026-2005
PoC for CVE-2026-2005
 yoyosh/darkreplica
CVE-2026-23631 (DarkReplica) Redis Exploit
 shieldersec/cve-2020-11579
Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database








