
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 jhnhnck/cve-2019-9193
PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in certain versions of PostgreSQL (9.3 - 11.7)
 34zy/cve-2026-72898
Python exploit for CVE-2026-72898, an unauthenticated SQL injection in Metabase's password reset endpoint that creates admin accounts and extracts…
 xiaoxiaoranxxx/cve-2025-70828
Datart v1.0.0-rc.3 JDBC Connection String Injection Leading to Arbitrary File Read
 ywh-jfellus/cve-2026-65761
Proof of Concept for CVE-2026-65761 - EasyStore Pro Unauthenticated SQL Injection via `filter_sortby`
 shad0w0sec/cve-2023-1454-exp
JeecgBoot SQL(CVE-2023-1454)sqlmap 注入不出来的情况可以使用该脚本
 rahulreddykarne/cve-2026-65321-pyathena
SQL injection in PyAthena via DefaultParameterFormatter (CVE-2026-65321)
 romain-deperne/cve-2026-41490
Detailed CVE-2026-41490 disclosure with PoC demonstrating unauthenticated SQL injection in Dagster database I/O managers via dynamic partition keys,…
 toanln-cov/cve-2026-78070
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…
 xbz0n/cve-2024-32136
Proof-of-concept exploit for CVE-2024-32136, a post-authenticated SQL injection in BWL Advanced FAQ Manager 2.0.3, demonstrating time-based database…
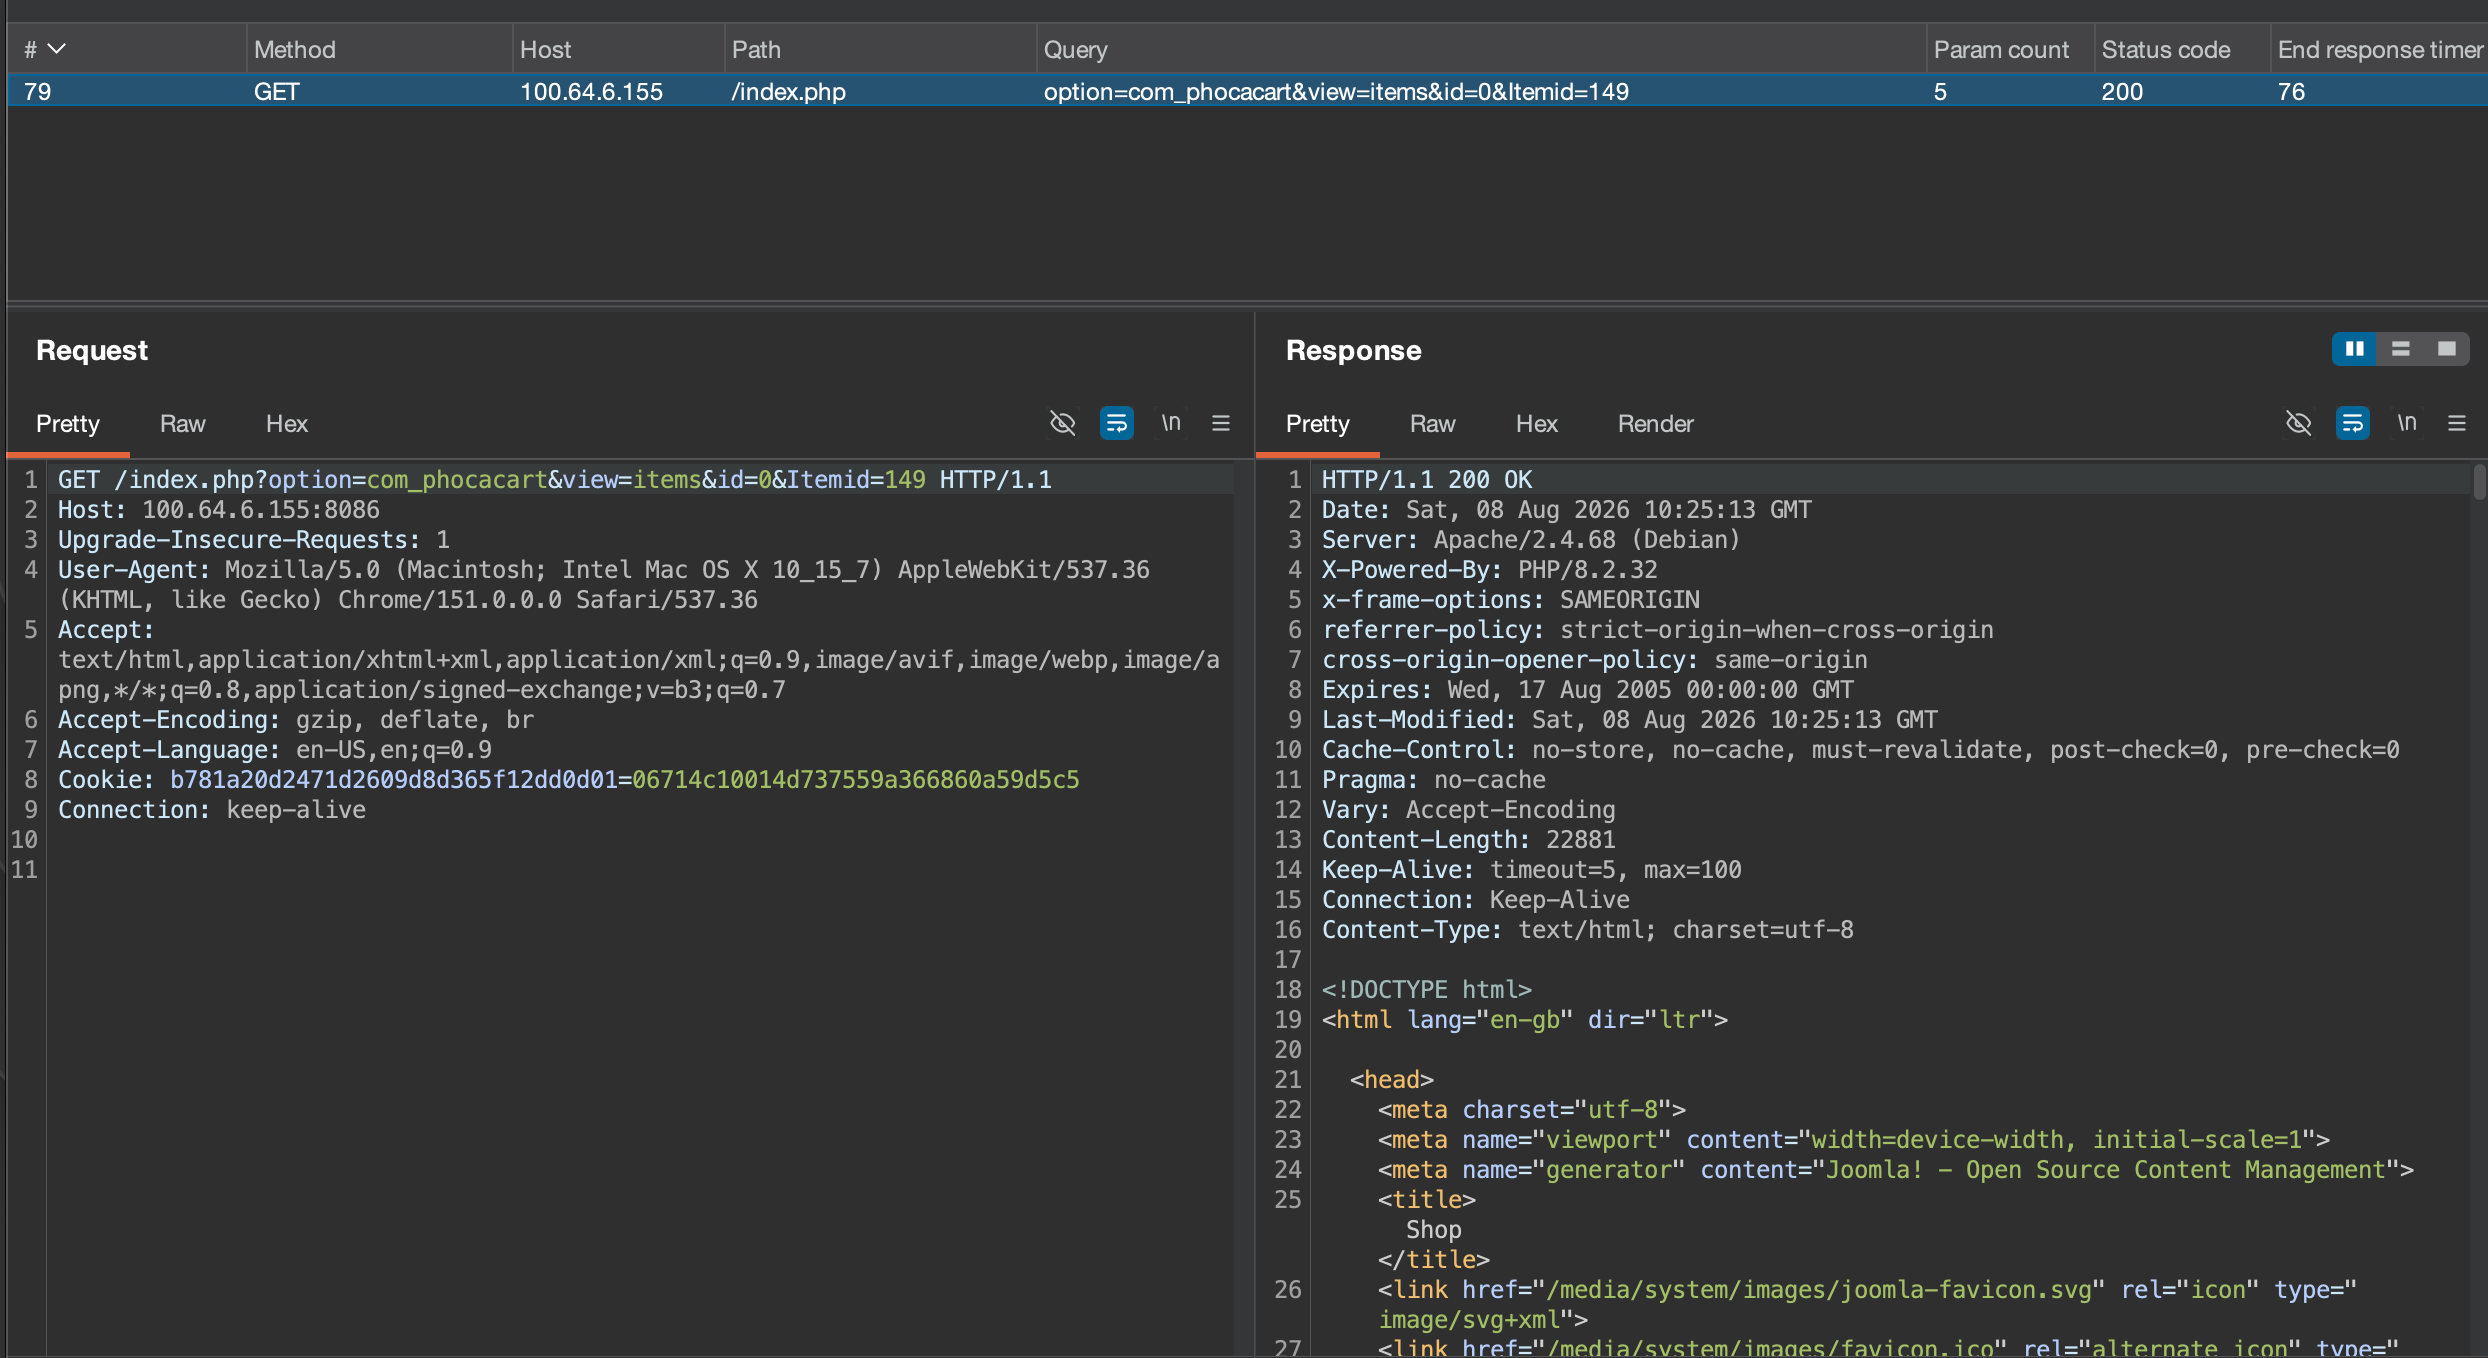 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 anusha-khan29/cve-2025-70149-sql-injection
Security research project — SQL Injection vulnerability exploitation and mitigation
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
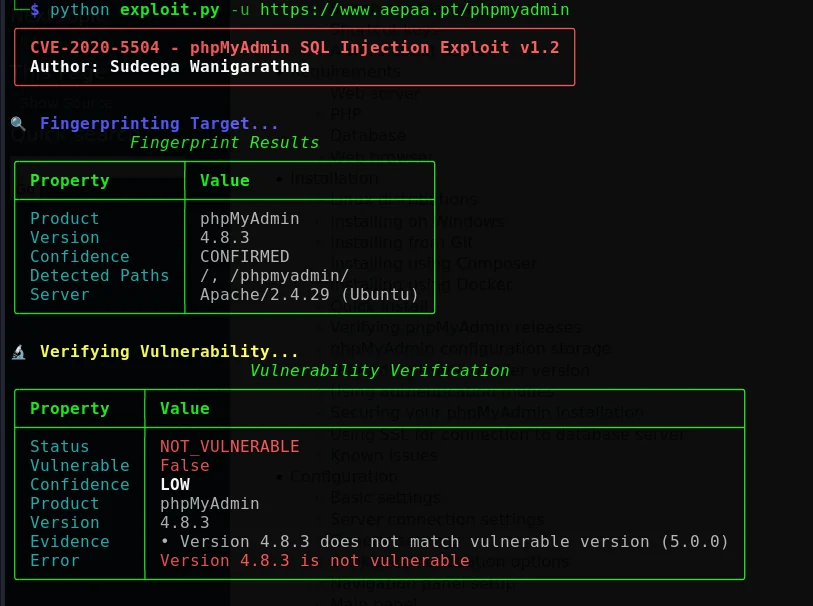 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…








