#1
Curated cybersecurity lists, collections, and learning references with clear scope and practical value.
Kitploit recommended
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 jonwiggins/xmloxide
A pure Rust reimplementation of libxml2
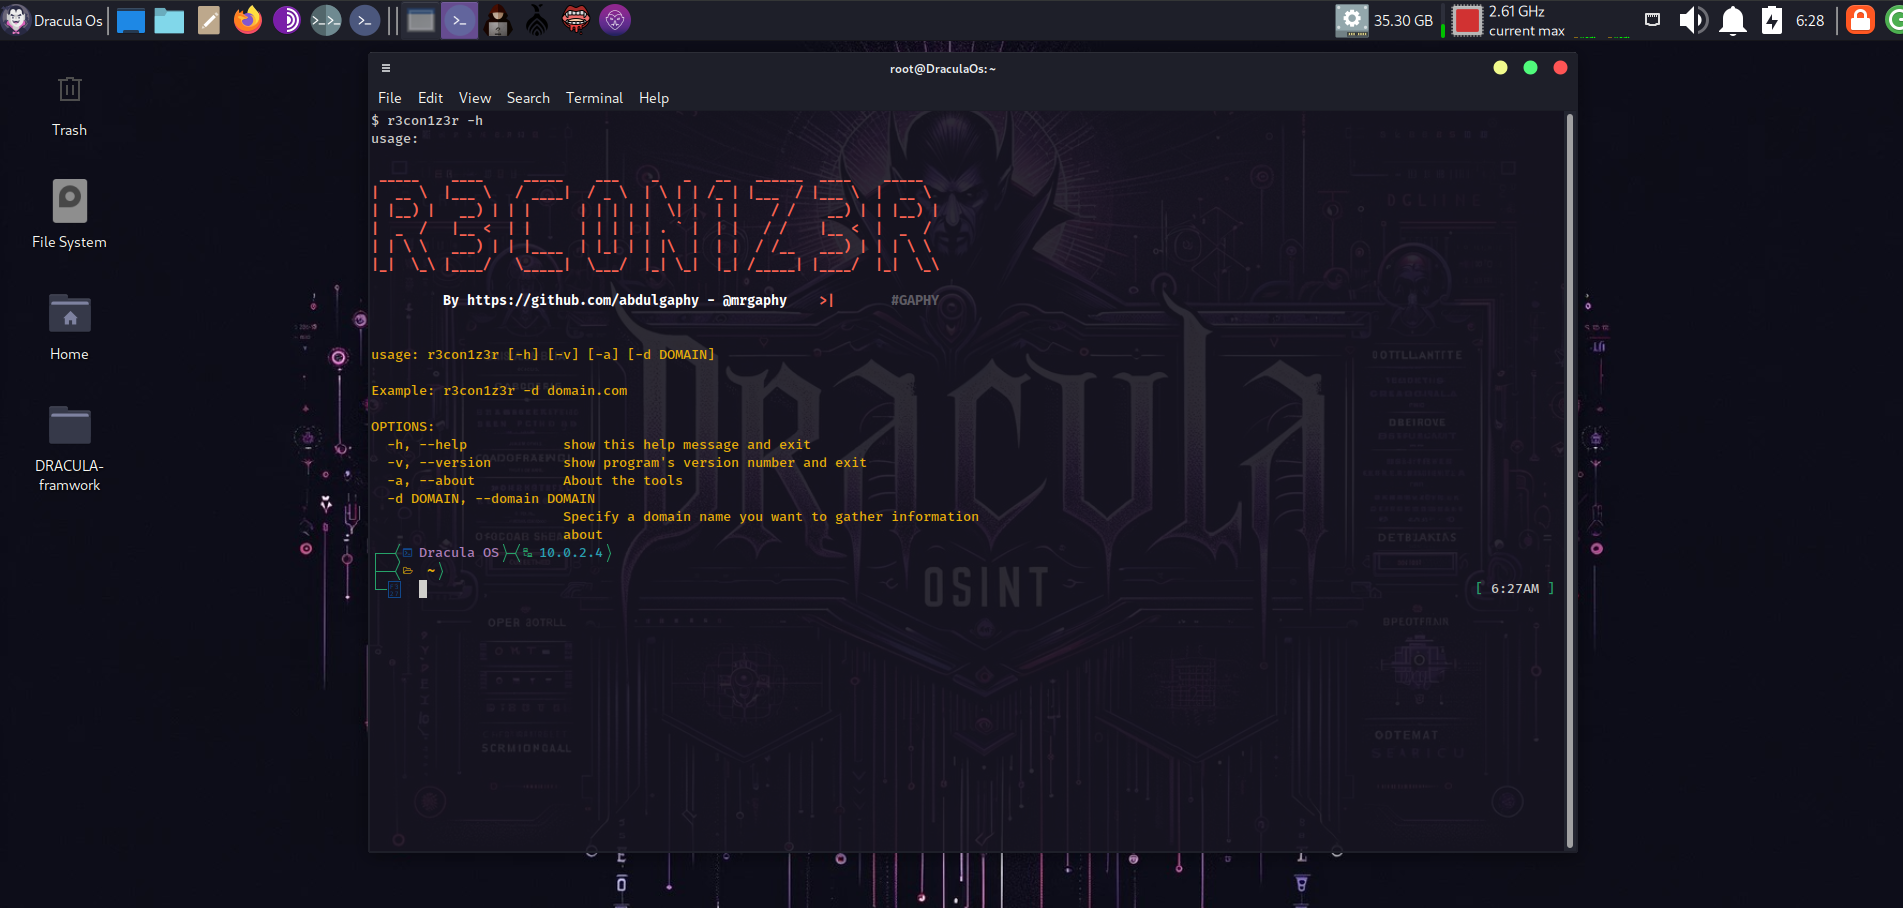 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 nextcloud/security-advisories
👮 Security advisories of Nextcloud
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 100daysofyara/2024
Rules shared by the community from 100 Days of YARA 2024
 danielcuthbert/trackers
A collection of online trackers, advertising networks, telemetry collectors and general 'we like to watch' lists for you to use to get better control…
 alephsecurity/research
Research material and Proof-of-Concepts for Aleph Research Findings
 100daysofyara/2023
Rules Shared by the Community from 100 Days of YARA 2023
 inquest/yara-rules-vt
Collection of YARA rules designed for usage through VirusTotal.com.
 dbrll/ll-34
Circuit-level PDP-11/34 emulator
 eth0izzle/security-skills
A collection of Claude Code skills that help security teams stay secure
 enablesecurity/advisories
Security advisories published by Enable Security
 embee-research/yara-detection-rules
Yara Rules for Modern Malware
 authomize/log4j-log4shell-affected
Lists of affected components and affected apps/vendors by CVE-2021-44228 (aka Log4shell or Log4j RCE). This list is meant as a resource for security…
 connectedlucy/plague
Default Detections for EDR
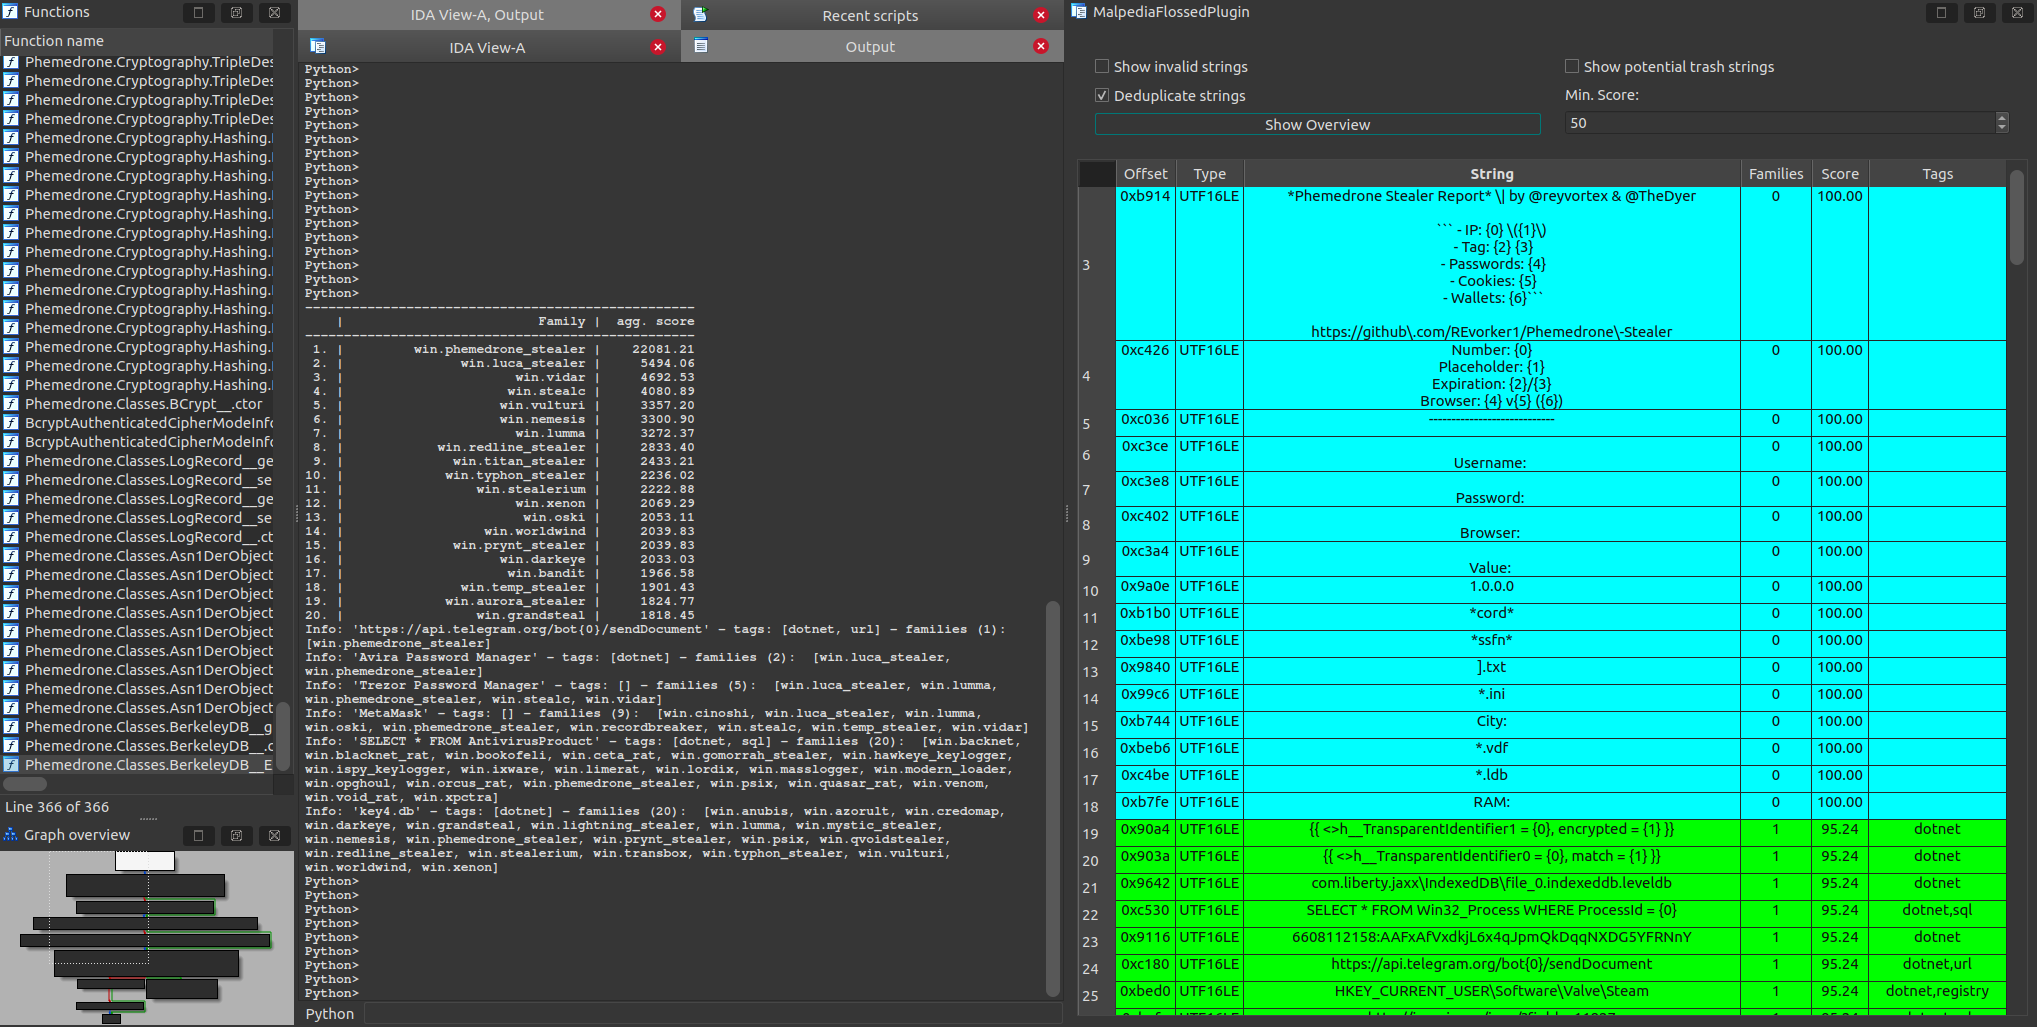 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.