
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
 ratiros01/cve-2004-1561
Standalone Python exploit for CVE-2004-1561 (Icecast header overflow), designed for penetration testing and CTF practice.
 hackmelocal/cve-2021-24891-simulation
Containerized lab environment to simulate and exploit a DOM-based XSS vulnerability (CVE-2021-24891) in the Elementor WordPress plugin for hands-on…
 shi10587s/sauercloude
0day VirtualBox 6.1.2 Escape for RealWorld CTF 2020/2021 CVE-2021-2119
 chatbottesisgmailh/sauercloude
0day VirtualBox 6.1.2 Escape for RealWorld CTF 2020/2021 CVE-2021-2119
 prprhyt/poc_tls1_3_cve-2020-13777
Proof-of-concept for CVE-2020-13777 (GnuTLS TLS 1.3 reconnect vulnerability). Parses pcap files to demonstrate the flaw for educational and technical…
 specializzazione-cyber-security/demo-cve-2021-29447-lezione
Proof-of-concept exploit for CVE-2021-29447, an authenticated XXE vulnerability in WordPress 5.6-5.7. Includes lab setup, malicious WAV generation,…
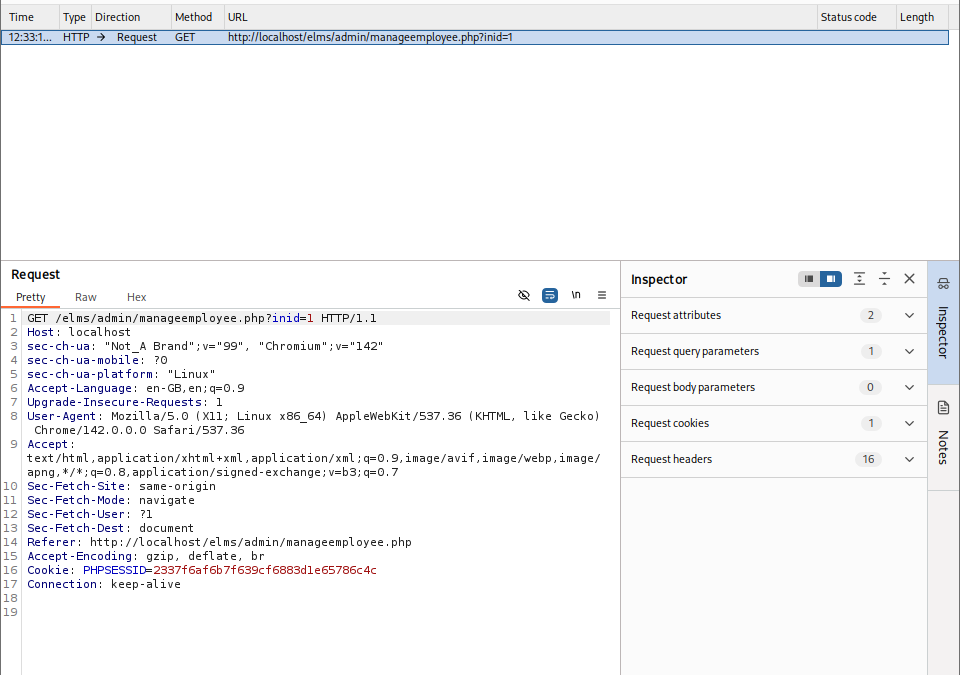 r-pradyun/cve-2025-67315
CSRF vulnerability PoC and remediation guide for employee deactivation in an admin panel. Includes CVSS scoring, attack reproduction steps, and…
 anir0y/sonicwall-audit-toolkit
SonicWall security audit toolkit with vulnerable CTF lab (CVE-2021-20038, CVE-2024-53704)
 igorbf495/cve-2024-42327
writeup cve-2024-42327
 datntsec/cve-2019-12735
Detailed technical analysis and proof-of-concept for CVE-2019-12735, an arbitrary code execution vulnerability in Vim/Neovim via modeline sandbox…
 user0x1337/cve-2023-30547
PoC to CVE-2023-30547 (Library vm2)
 j3r1ch0123/cve-2024-24590
Created this exploit for the Hack The Box machine, Blurry.
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…
 akashicyitai/cve-2019-12937-toaruos
Proof-of-concept exploit for CVE-2019-12937: a stack buffer overflow in ToaruOS gsudo allowing local privilege escalation to root through crafted…
 hackhoven/strapi-rce
Exploit script showcasing a mixture of CVE-2019-18818 and CVE-2019-19609 for unauthenticated remote code execution in Strapi CMS.
 flojboj/cve-2021-31630
POC Exploit for CVE-2021-31630 written in Python3 and using C reverse shell with non-blocking mode
 r1nzleer/rce-cacti-1.2.22
Este es un código del exploit CVE-2022-46169, que recree utilizando Python3! Si por ahí estás haciendo una máquina de HTB, esto te puede ser útil...…








