
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
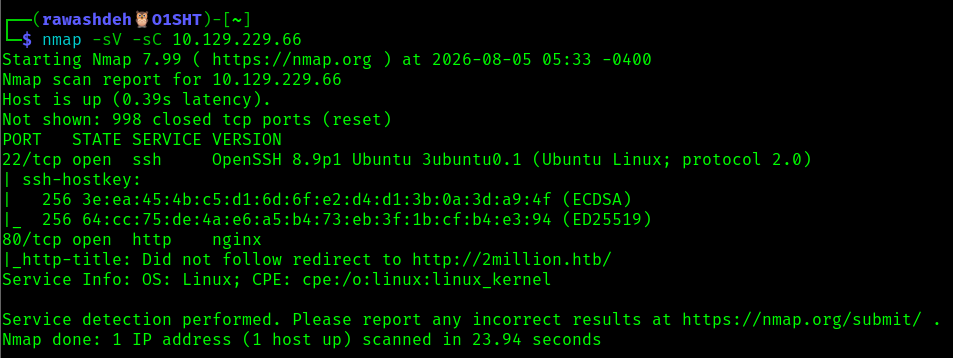
 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 isaca0315/cve-2026-64849-poc-lab
este laboratorio puede estar bien o mal preguntale a la IA estoy probando pero debe funcionar hahahah
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 bobfuzzer/cve-2019-18885
Proof-of-concept for a null pointer dereference in the Linux kernel BTRFS filesystem (CVE-2019-18885), including a crafted image, reproduction steps,…
 americooo/pentest-writeups
Kioptrix Level 1 writeup - CVE-2003-0201 Samba trans2open
 shivammittal2403/cve-2025-57819-freepbx-range
Isolated educational FreePBX-compatible cyber range for CVE-2025-57819 (CWE-89/CWE-288). Docker lab — not official Sangoma FreePBX.
 raajgupta01/htb-machine-ringdown
Detailed design & exploitation writeup for Ringdown—an original Debian/Asterisk vulnerable machine featuring CVE-2024-42365 (AMI), PJSIP pre-hash…
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…

 aperikube/aperisite
CTF team website aggregating writeups and resources for web security challenges including XSS, SQLi, CSRF, SSRF, and XXE.
 porcumarcooo/tryhackme-blue-ms17-010
Walkthrough, threat analysis, and remediation guide for CVE-2017-0144 (EternalBlue).
 r3fr4kt/codify-tjnull-oscp-
Walkthrough for Codify (Linux - Easy). Exploits vm2 RCE (CVE-2023-30547), SQLite DB hash extraction, Bcrypt cracking with John, and Privilege…
 khoatran107/cve-2024-58239
Linux kernel TLS subsystem exploit for CVE-2024-58239, achieving privilege escalation via a double-free vulnerability in tcp_rcv_state_process.…
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
 j4k0m/loader-cve-2020-14343
A web application vulnerable to CVE-2020-14343 insecure deserialization leading to command execution in PyYAML package.
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 davidaroca27/cve-2024-23346-exploit
This is a exploit for the known Remote Code Execution (RCE) vulnerability in the `pymatgen` (CVE-2024-23346) Python library by uploading a malicious…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…








