
 #1
Tools for implementing, analyzing, breaking, and implementing cryptographic systems and algorithms.
Kitploit recommended

 ricardojoserf/cve-2026-63286
Proof-of-concept offline decryptor for AXIS Camera Station credentials stored in Firebird databases, with CPU/GPU brute-force of the NTFS volume…
 ekomssavior/wp2shell
CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)
 z1ph1us/milksad-mnemonic-generator
This tool generates BIP-39 mnemonic phrases derived from Unix timestamps, exploring the 'Milk Sad' vulnerability's implications (CVE-2023-39910)
 jas502n/sms4_decrypt
SMS4 Decrypt
 aimoda/hitron-cfg-decrypter
CVE-2014-10069
 jm00nj/sha256-cdp
GPU-accelerated SHA-256 rainbow table implementation based on CDP (Cyclic Digit-sum Projection) structural analysis. AMD RX 9070 XT, OpenCL + Vulkan.
 nccgroup/fips203
Pure Rust implementation of (draft) FIPS 203 Module-Lattice-based Key-Encapsulation Mechanism Standard for server, desktop, browser and embedded…
 cenobyte-vincit/encrypted-linux-kernel-modules
encrypted-linux-kernel-modules
 gmh5225/packer-payload-entropyreducer
Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
 eugexo/security-baseline-ubuntu
Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…
 badkeys/debianopenssl
Private keys vulnerable to Debian OpenSSL bug (CVE-2008-0166)
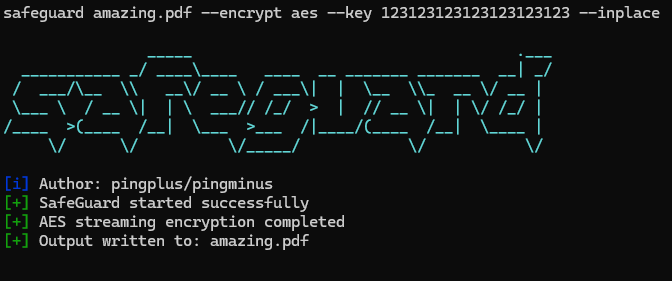 pingpongplus/safeguard
CLI Encryption tool written in Go only for learning purposes and demonstration of encryption (not secure)
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 hikame/cve-2018-17144_poc
Put the *.py files to test/functional folder of bitcoin sourcecode (commit: 4901c00792c1dabae4bb01e6373c9b1ed9ef3008)
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 commonguy25/authproof-sdk
Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.
 synacktiv/cve-2020-9289
Decrypt reversible secrets encrypted using the default hardcoded key related to CVE-2020-9289 on FortiAnalyzer/FortiManager (the only difference with…
 nccgroup/nlahoney
NLA Honeypot Associated Research








