#1
Web crawling, scraping, spidering, and automated reconnaissance tools for security testing.
Kitploit recommended
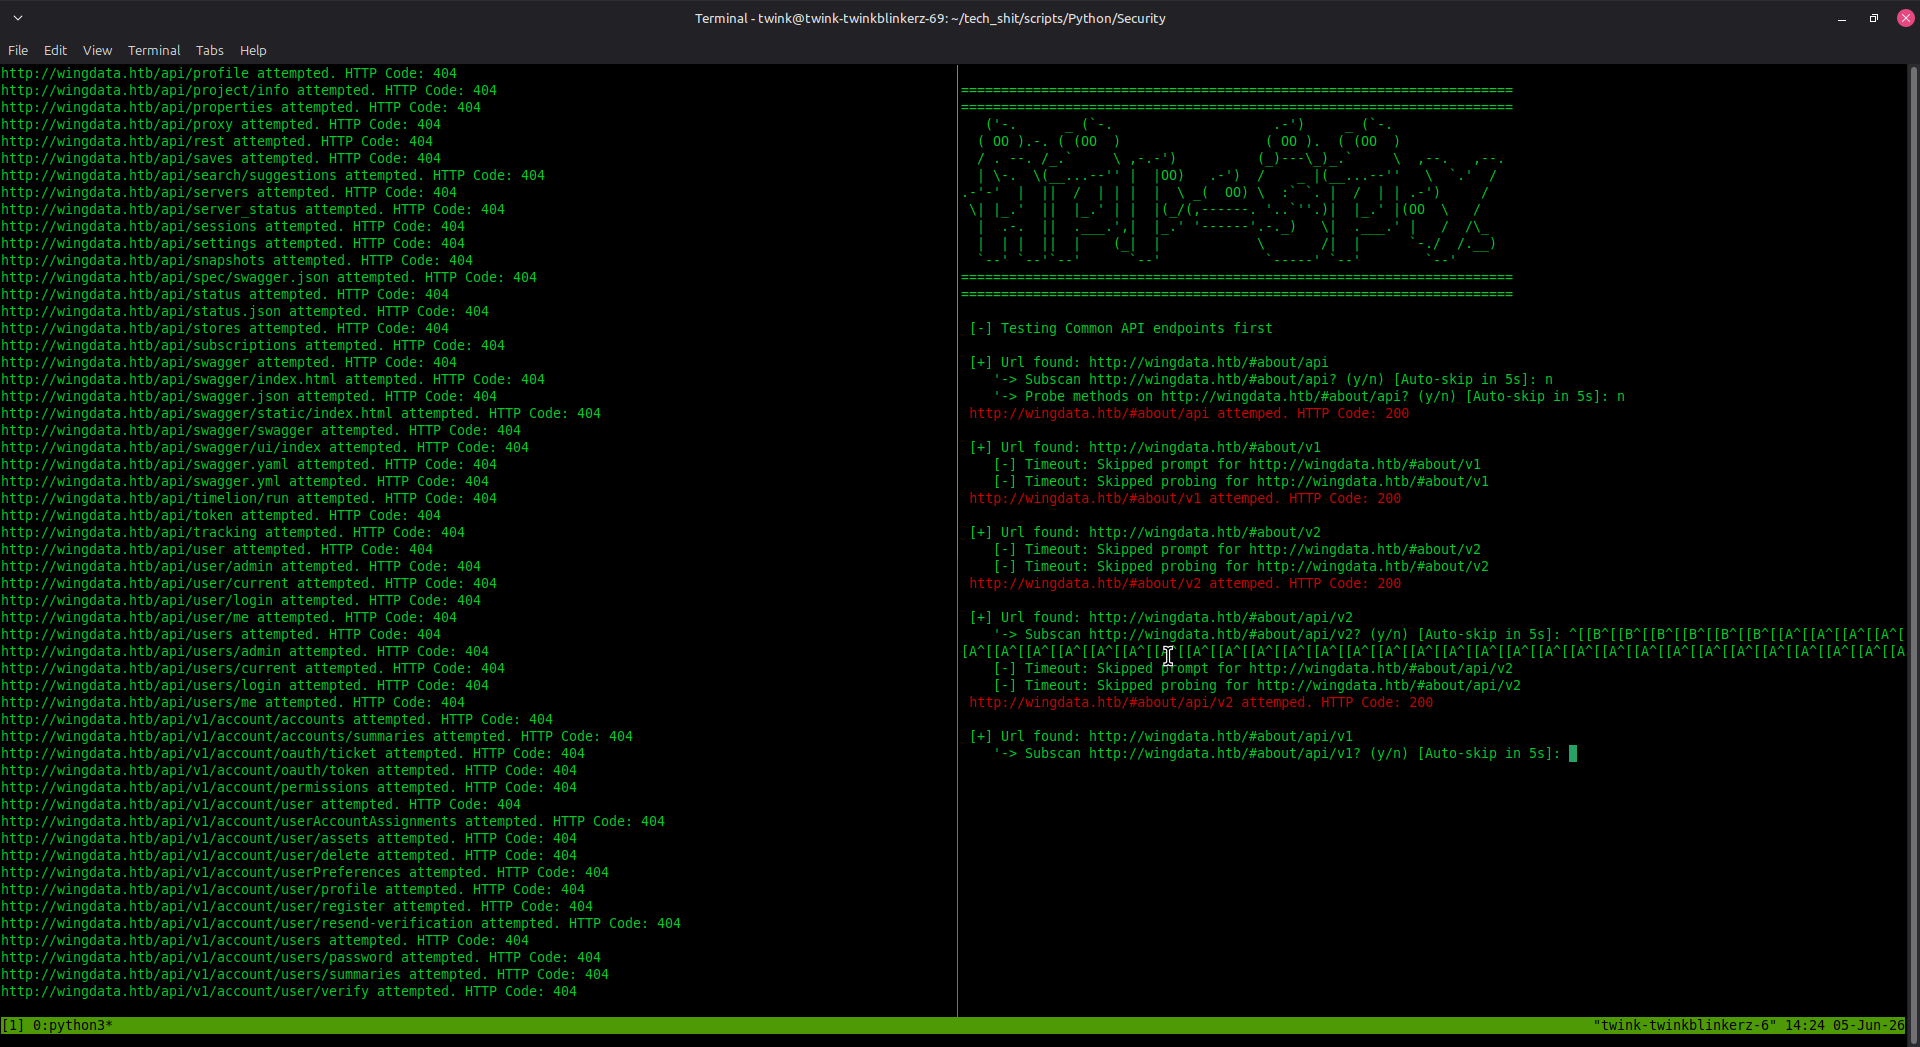
 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 yora1928/cve-2026-15748
Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.
 honeyb33z/cve-2020-11023-scanner
Static analysis scanner for CVE-2020-11023 XSS vulnerabilities in JavaScript. Detects vulnerable jQuery versions and dangerous DOM manipulation…
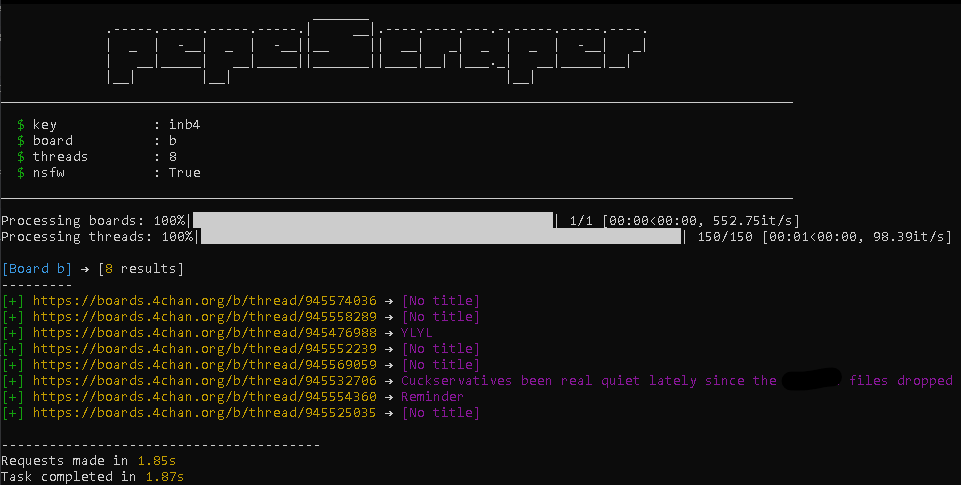 juaanreis/pepescraper
4chan content scraper
 houmanpashaei/cve-2025-29927
This is a CVE-2025-29927 Scanner.
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 ua-spectral/botlens
Research artifact and MCP server that audits security and privacy concerns in third-party Discord bots via large-scale review analysis, LLM labeling,…
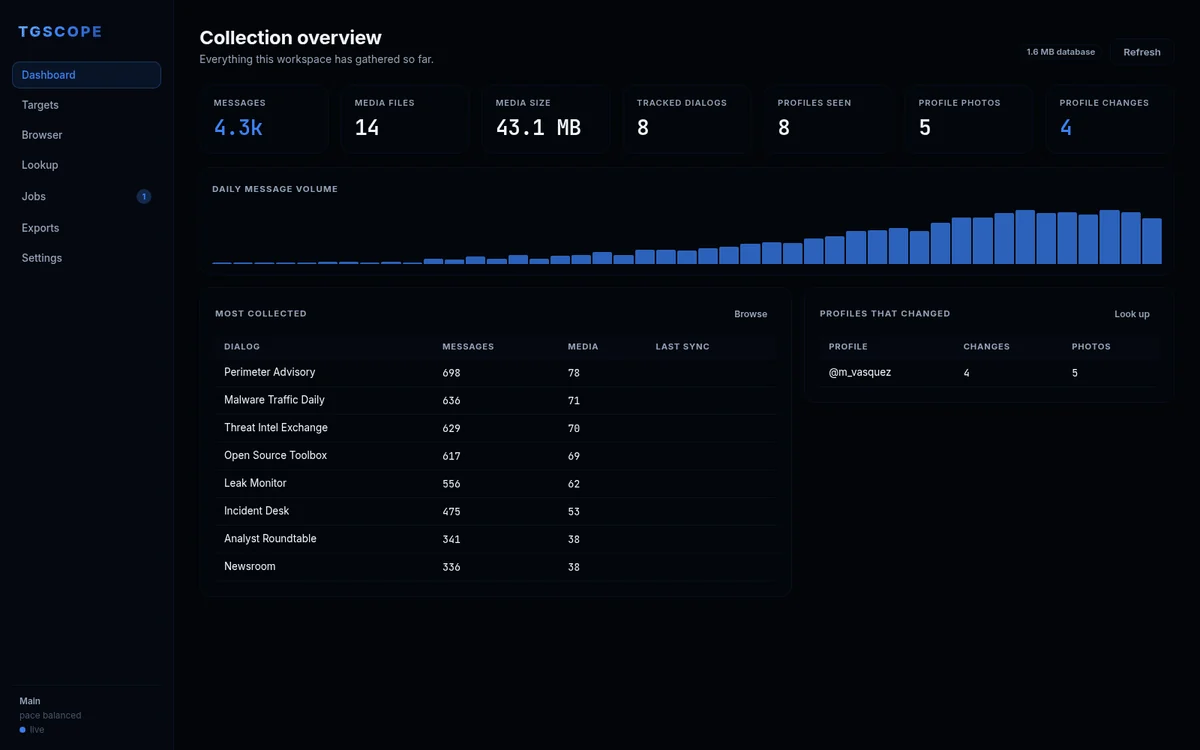 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 torchiachristian/vulnscan
Scanner di vulnerabilità web in Python: SQL injection, XSS , path traversal, security headers. Crawler, dashboard Flask, report in un PDF
 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
 rodhnin/pythia-sql-clairvoyance
Advanced SQL Injection Scanner with AI-powered analysis, ethical compliance framework, and professional reporting.

 nu11secur1ty/sql-global-injector
Python-based web crawler and SQL injection vulnerability scanner using dork queries. Supports proxy and automated scanning for security testing.
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
 khalidelborai/xtor
Python library for programmatic Tor instance management with SOCKS5 proxy, identity rotation, stream isolation, hidden services, circuit control, and…
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…