
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 p3nt4/invoke-socksproxy
Socks proxy, and reverse socks server using powershell.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
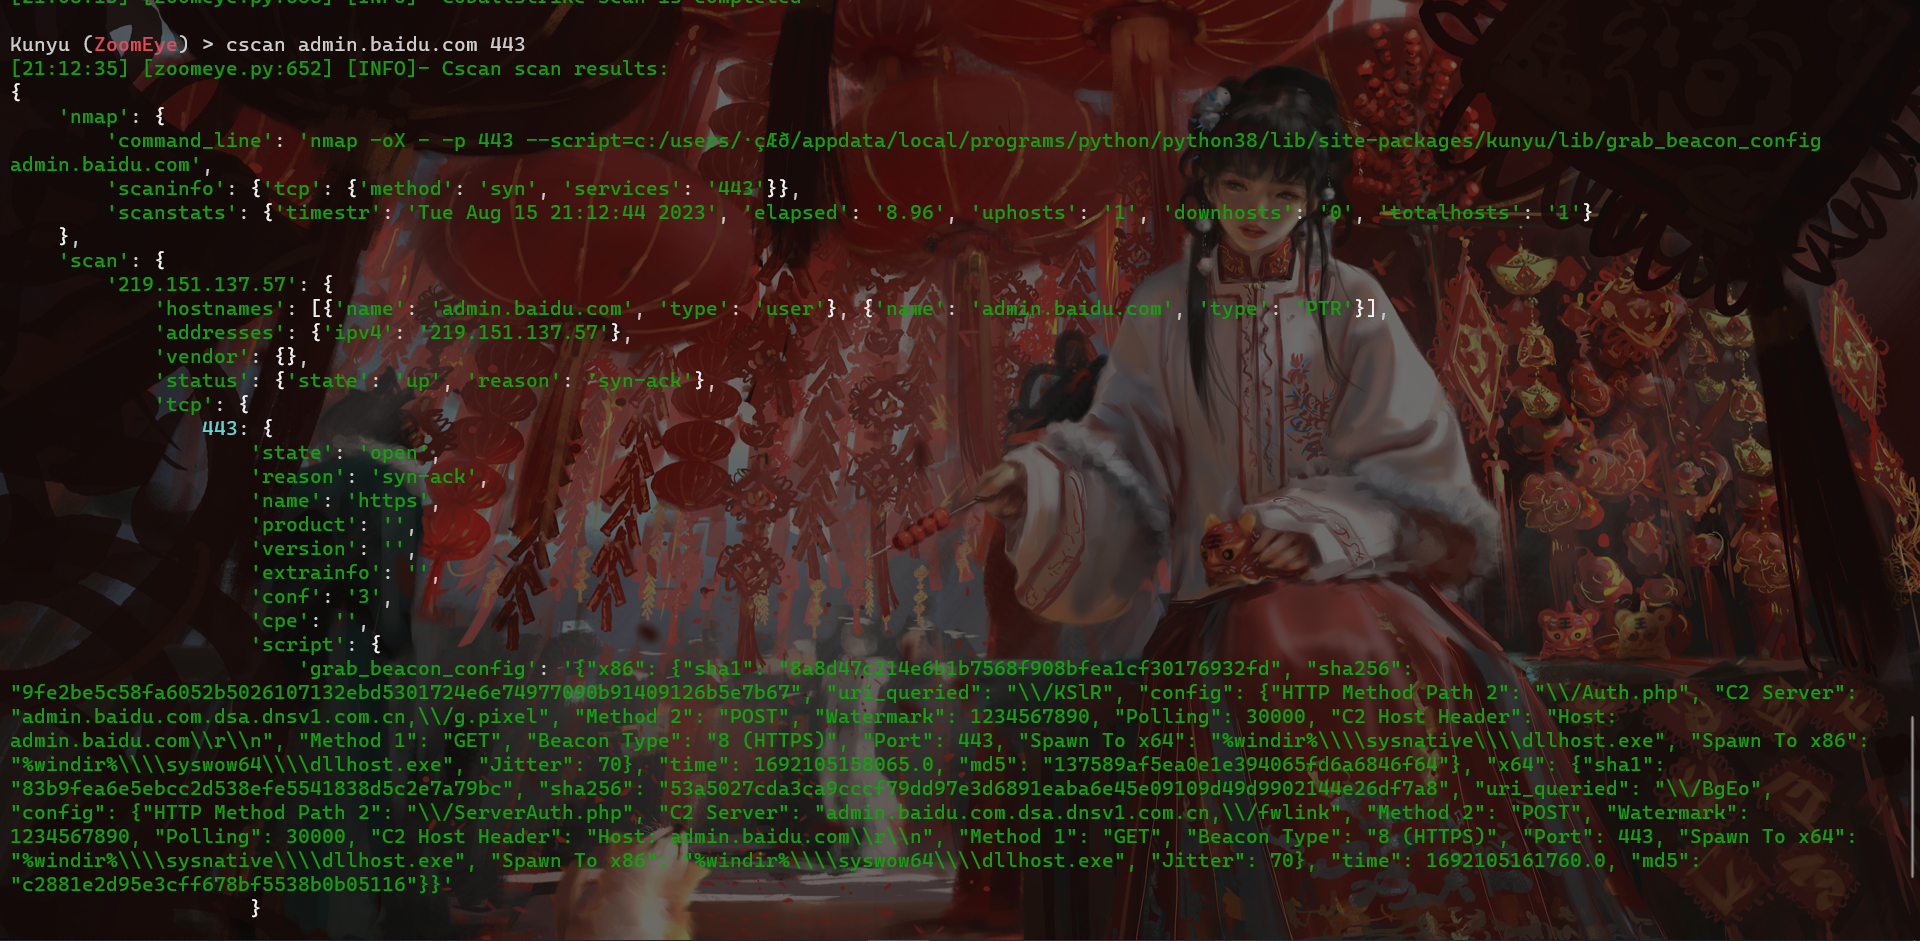 wikiz/redguard
C2 front flow control tool with JA3/JARM fingerprint randomization, domain fronting, malleable C2 profile validation, and IP whitelisting to evade…
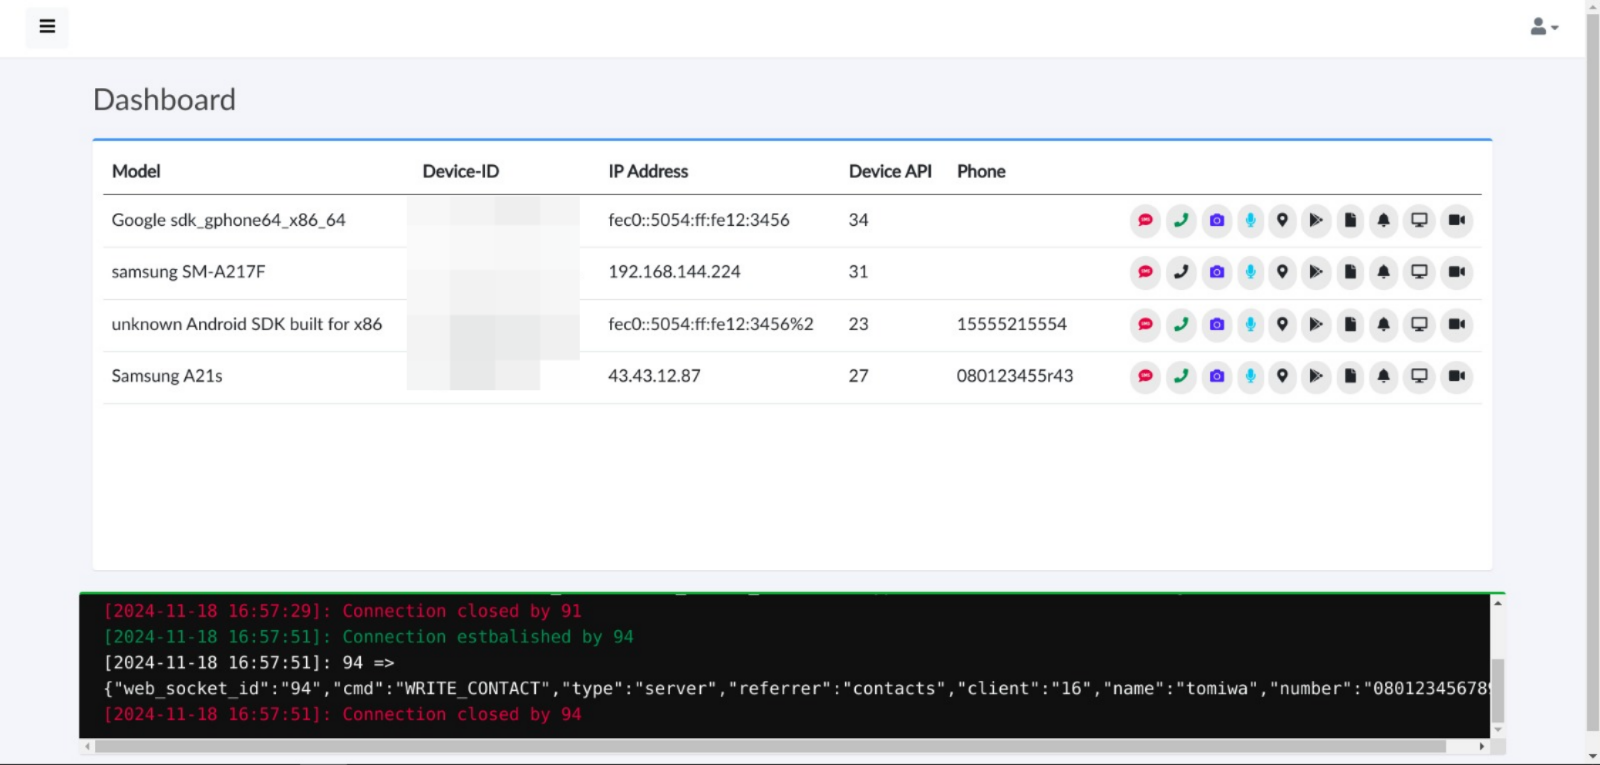 tomiwa-ot/moukthar
Android remote administration tool
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 wkl-sec/hiddendesktop
HVNC for Cobalt Strike
 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 schira4396/vcenterkiller
一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…
 deimosc2/deimosc2
DeimosC2 is a Golang command and control framework for post-exploitation.
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 ghostpack/sharpwmi
SharpWMI is a C# implementation of various WMI functionality.
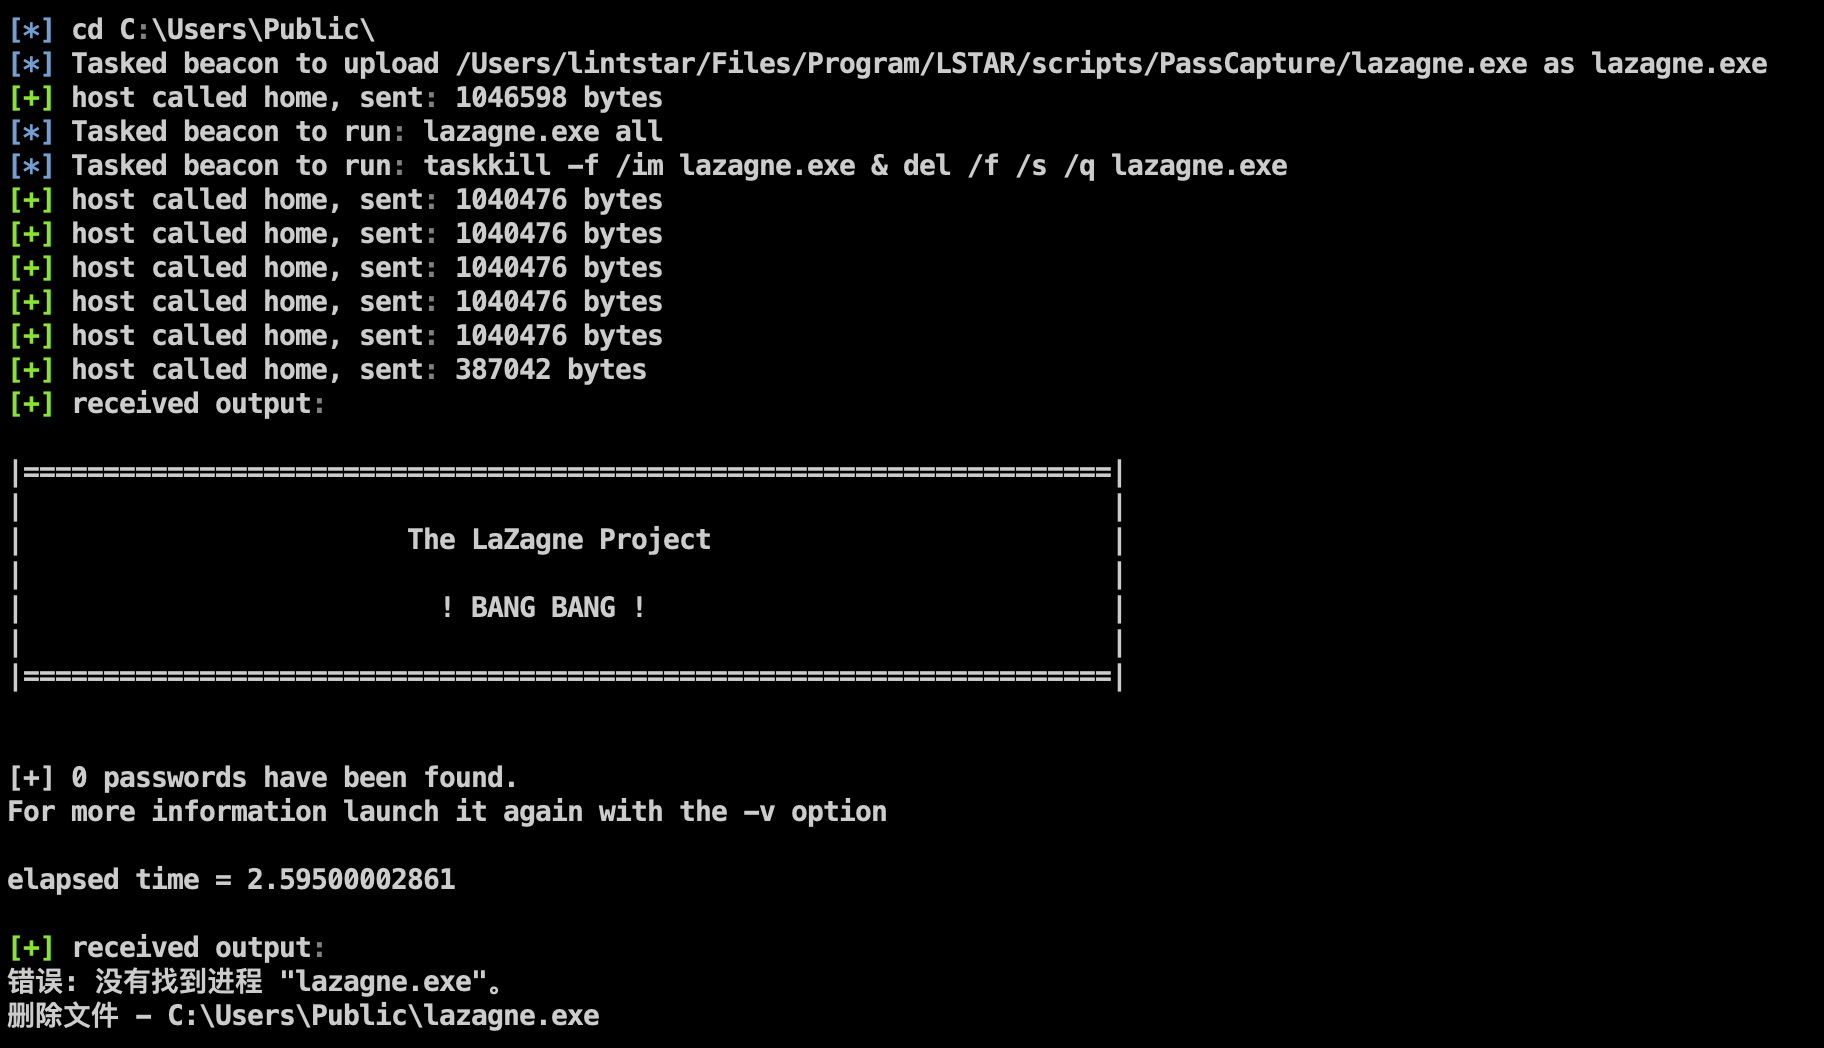 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。
 mwsrc/betterandrorat
Android Remote Access Trojan
 sin5678/gh0st
a open source remote administrator tool
 jas502n/cve-2020-5902
Proof-of-concept exploit for CVE-2020-5902, a directory traversal and remote code execution vulnerability in F5 BIG-IP TMUI. Includes file read,…
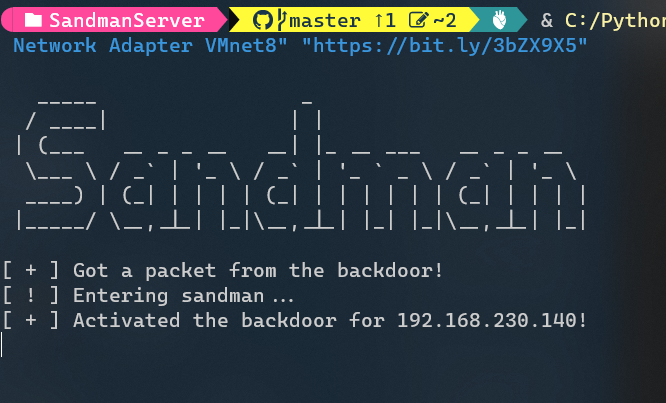 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…








