
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 154802388/cve-2020-17531
Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts于2020年12月08日披露 S2-061 Struts 远程代码执行漏洞(CVE-2020-17530),在使用某些tag等情况下可能存在OGNL表达式注入漏洞,从而造成远程代码执行,风…
 hax3xploit/cve-2021-41645
Remote Code Execution (RCE) vulnerability exists in Sourcecodester Budget and Expense Tracker System 1.0 that allows a remote malicious user to…
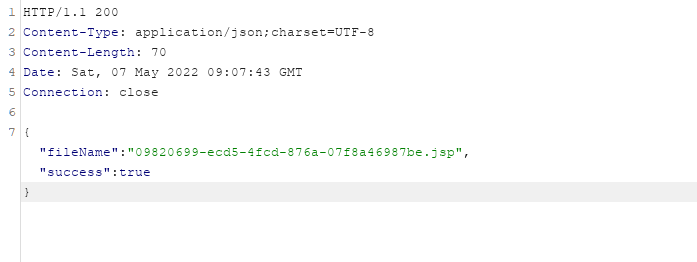 nanaao/cve-2022-30929
CVE-2022-30929 POC
 trinadh465/openssl-1.1.1g_cve-2022-0778
OpenSSL 1.1.1g source snapshot, a robust TLS/SSL and general-purpose cryptographic library with command-line tools for key generation, certificate…
 shoucheng3/jenkinsci__workflow-multibranch-plugin_cve-2022-25175_706-vd43c65dec013
Exploit for CVE-2022-25175 targeting Jenkins Pipeline: Multibranch plugin, enabling automated exploitation of a specific vulnerability in CI/CD…
 pandante-central/cve-2023-24329-codeql-test
CodeQL query test for CVE-2023-24329, demonstrating static analysis detection of a specific vulnerability in Python's urllib.parse module.
 mekhalleh/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 trinadh465/openssl-1.1.1g_cve-2021-23840
OpenSSL toolkit providing TLS/SSL protocols and general-purpose cryptographic library with command-line tools for key generation, certificate…
 shanika04/cp30_xxe_partial_fix
version between CVE-2018-20433 and CVE-2019-5427
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 renukaselvar/platform_packages_providers_mediaprovider_cve-2023-40127
Exploit code for CVE-2023-40127, a vulnerability in Android MediaProvider, demonstrating the flaw for security research and testing.
 kavgan/vuln_test_repo_public_ruby_gemfile_cve-2016-6317
Detects known vulnerabilities in Ruby Gemfile dependencies by scanning for specific CVEs, enabling automated security checks in development pipelines.
 manoelprovider20-lgtm/merge-authz-test
authz test (CVE-2026-1999 siblings)
 mi-hood/cve-2018-9206
jquery file upload poc
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 shoucheng3/nahsra__antisamy_cve-2022-29577_1-6-6-1
Java library for fast, configurable cleansing of untrusted HTML to prevent cross-site scripting (XSS) attacks. Uses policy-driven scanning to…
 alonnavon/npm-demo
Browser demo: EJS template injection (CVE-2022-29078) with Seal Security remediation
 shoucheng3/codehaus-plexus__plexus-utils_cve-2017-1000487_3-0-15
Java utility library with a focus on a specific CVE vulnerability, providing code analysis and static analysis capabilities for security assessment.








