#1
 ksaweryr/cve-2023-45612-poc
Proof of concept for XXE in Ktor (CVE-2023-45612)
 d0n601/cve-2025-12673
Flex QR Code Generator <= 1.2.6 - Unauthenticated Arbitrary File Upload
 ali-py3/exploit-cve-2025-68613
Proof-of-concept exploit for a critical RCE vulnerability in n8n (CVE-2025-68613), demonstrating arbitrary command execution via expression injection…
 tagoletta/cve-2023-38890
Exploit for CVE-2023-38890, an unauthenticated SQL injection to remote code execution in Online Shopping Portal 3.1, with a proof-of-concept and…
 d3kc4rt1/cve-2026-1657
Unauthenticated Arbitrary File Upload in EventPrime Plugin
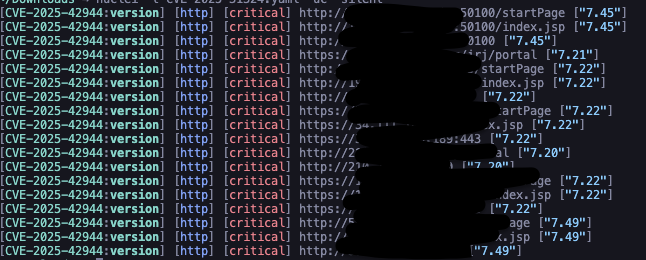 rxerium/cve-2025-42944
Detection for CVE-2025-42944
 snorlyd/https-nj.gov---cve-2020-11023
Vulnearability Report of the New Jersey official site
 depers-rus/cve-2007-4559
Proof-of-concept demonstrating CVE-2007-4559 path traversal in Python's tarfile module, allowing arbitrary file overwrite via malicious TAR archives.
 open-flaw/cve-2025-12758
Detailed CVE-2025-12758 disclosure with PoC demonstrating Unicode variation selector bypass in validator.js isLength(), including root cause…
 andressuarezmonk/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, achieving remote code execution in React Server Functions via prototype pollution and crafted Flight…
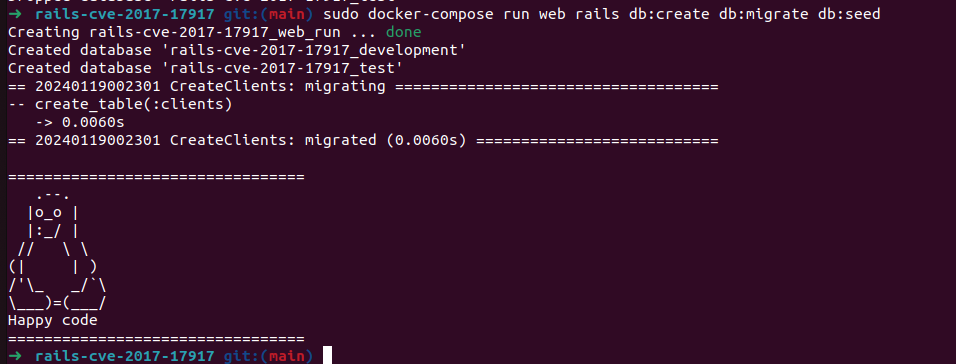 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
 cucumberanorsncompany/sealsecurityassignment
Researching on the vulnrability CVE-2023-26136
 mooseloveti/postgallery-cve-report
Disclosure for CVE-2025-13543
 klassiker/cve-2025-55182
CodeQL-based analysis of CVE-2025-55182 prototype pollution vulnerability in React Server Components, with exploit POC and static detection queries…
 beishanxueyuan/cve-2025-48384-test
Reproduction of CVE-2025-48384 demonstrating a Git submodule path traversal vulnerability, with step-by-step commands to recreate the exploit.
 ysaxon/pyrocms-ssti-fix
A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation