
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 safedep/vet
Protect against malicious open source packages 🤖
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
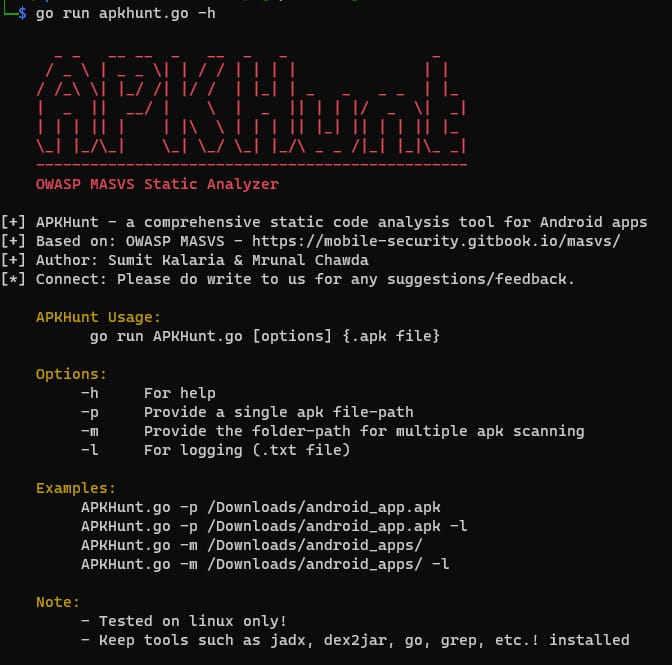 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 jsonpath-plus/jsonpath
A fork of JSONPath from http://goessner.net/articles/JsonPath/
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
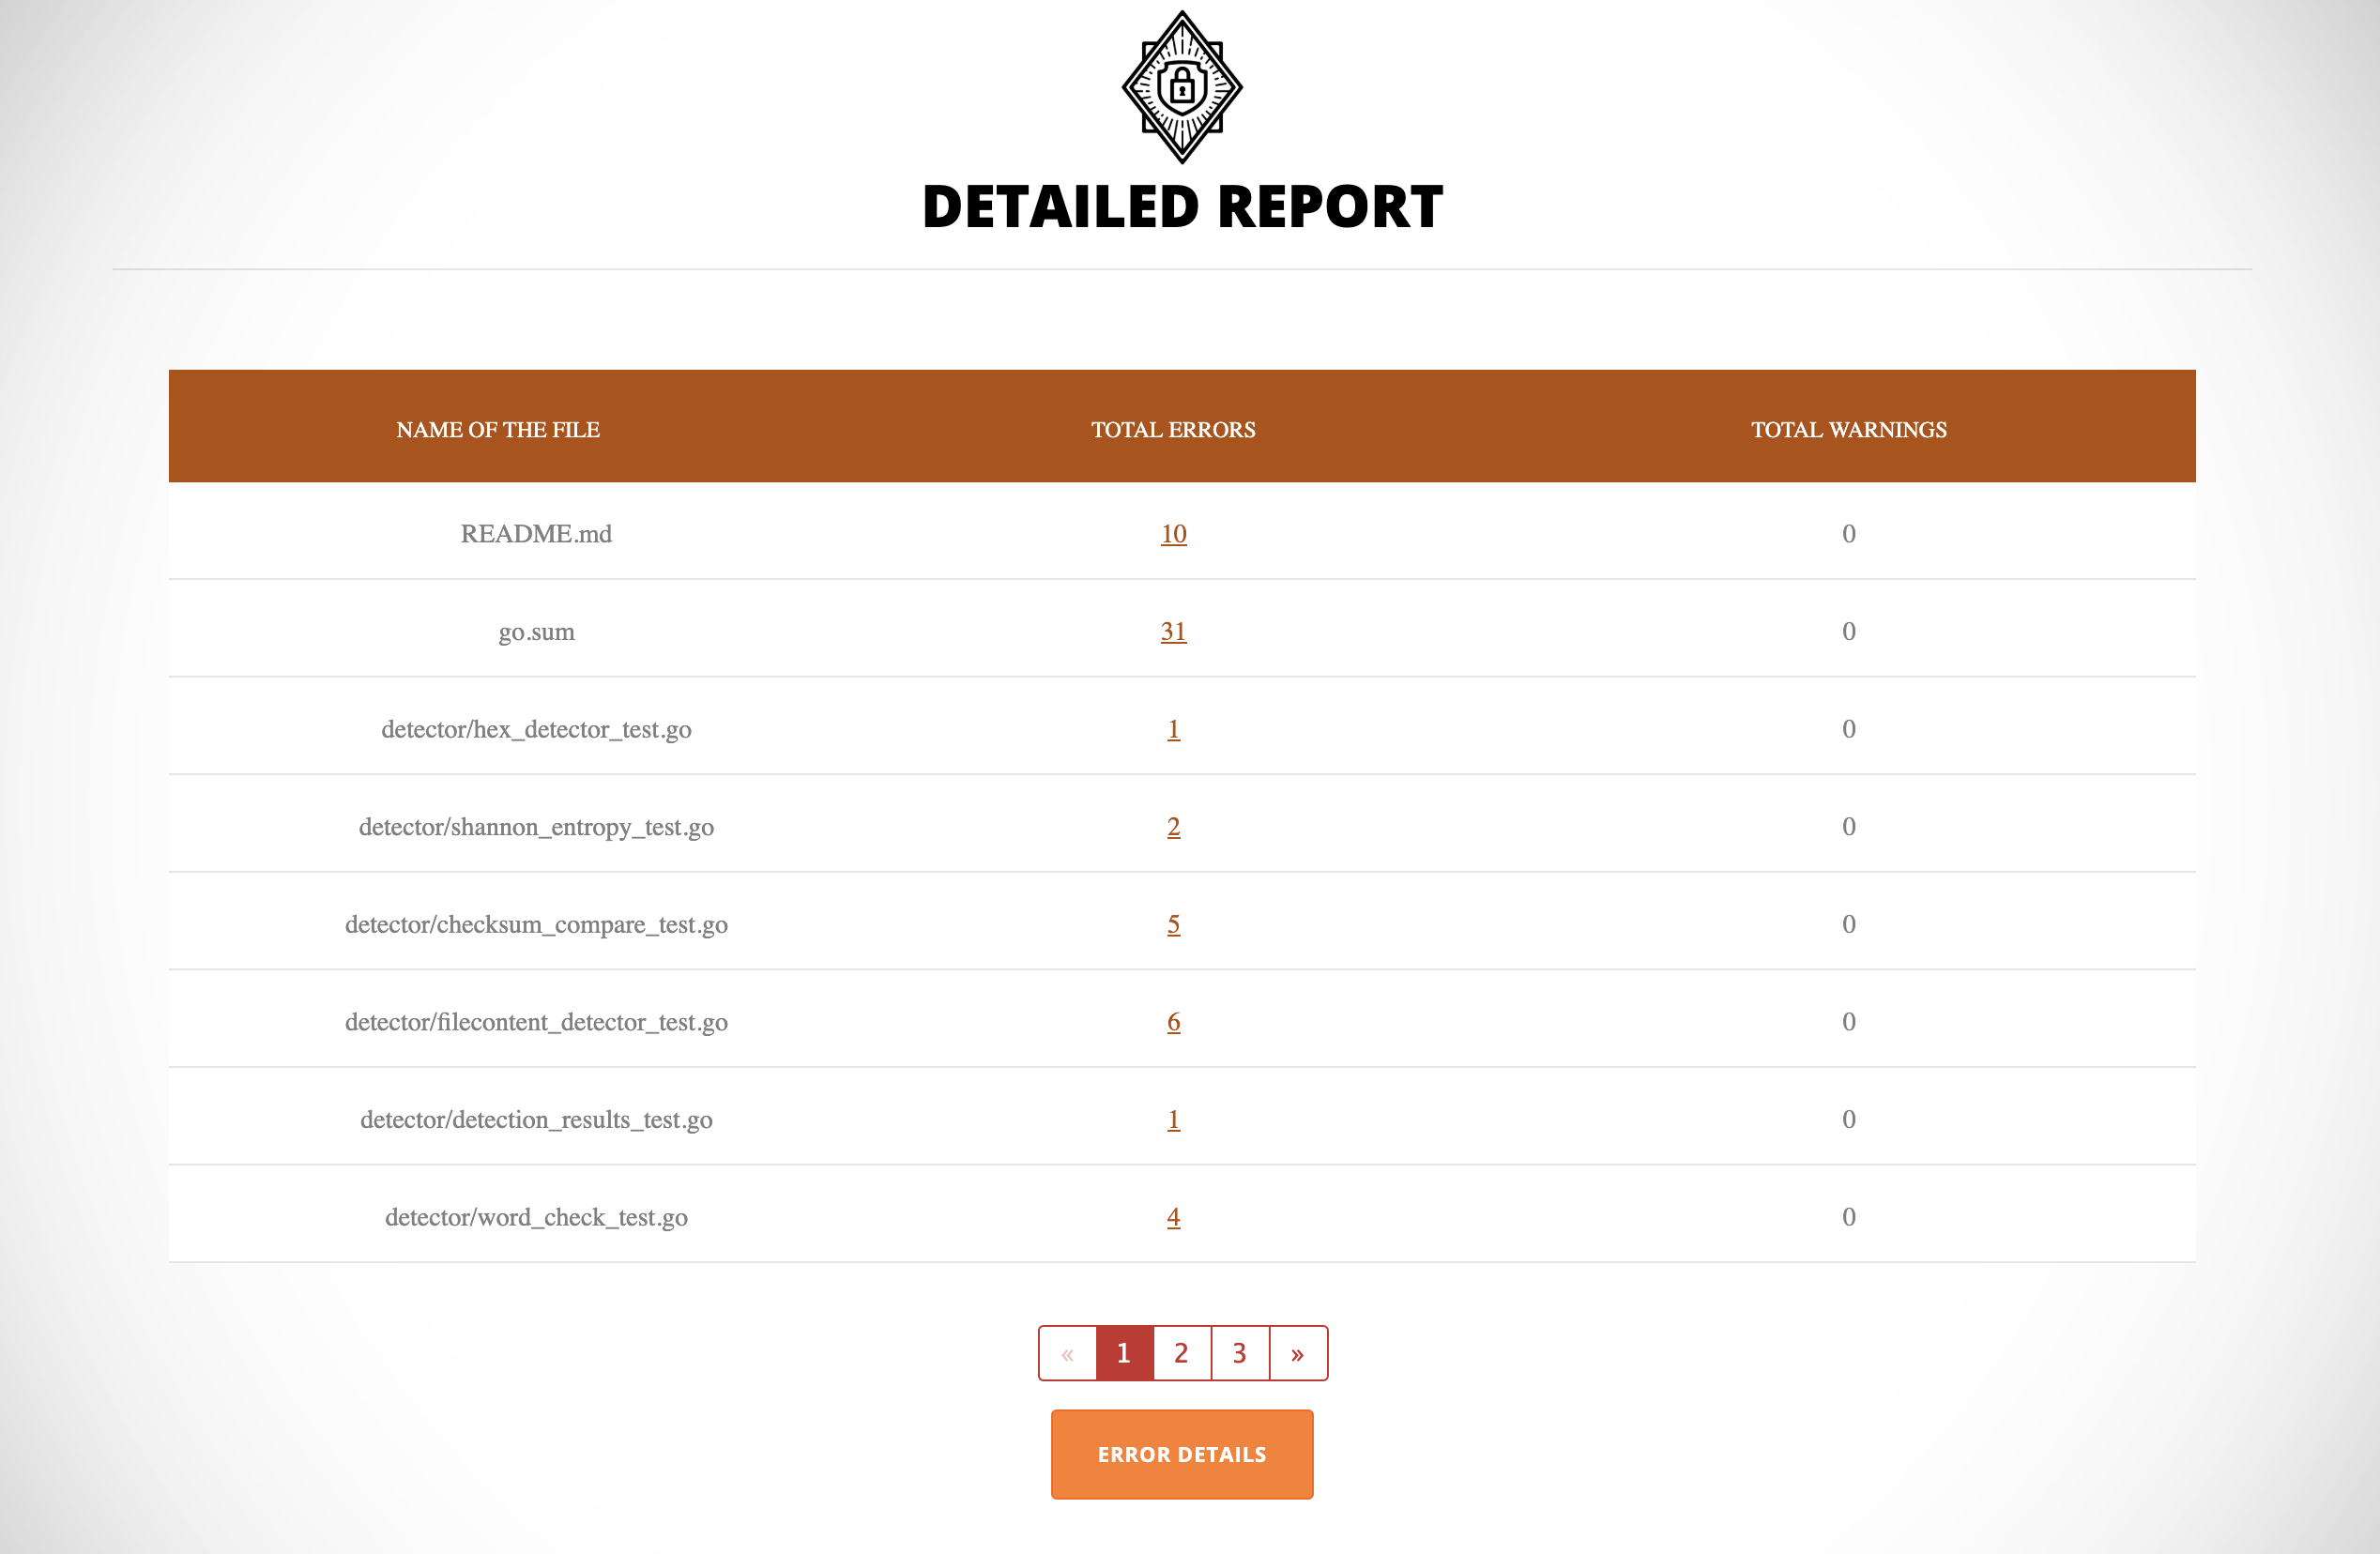 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
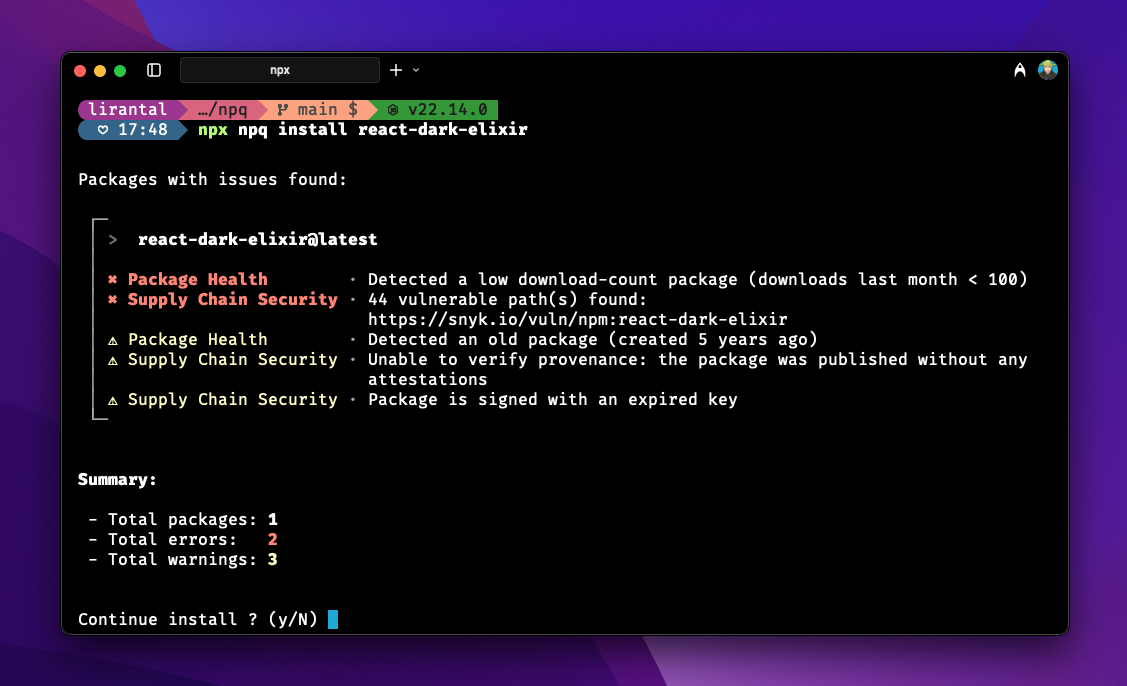 lirantal/npq
safely install npm packages by auditing them pre-install stage
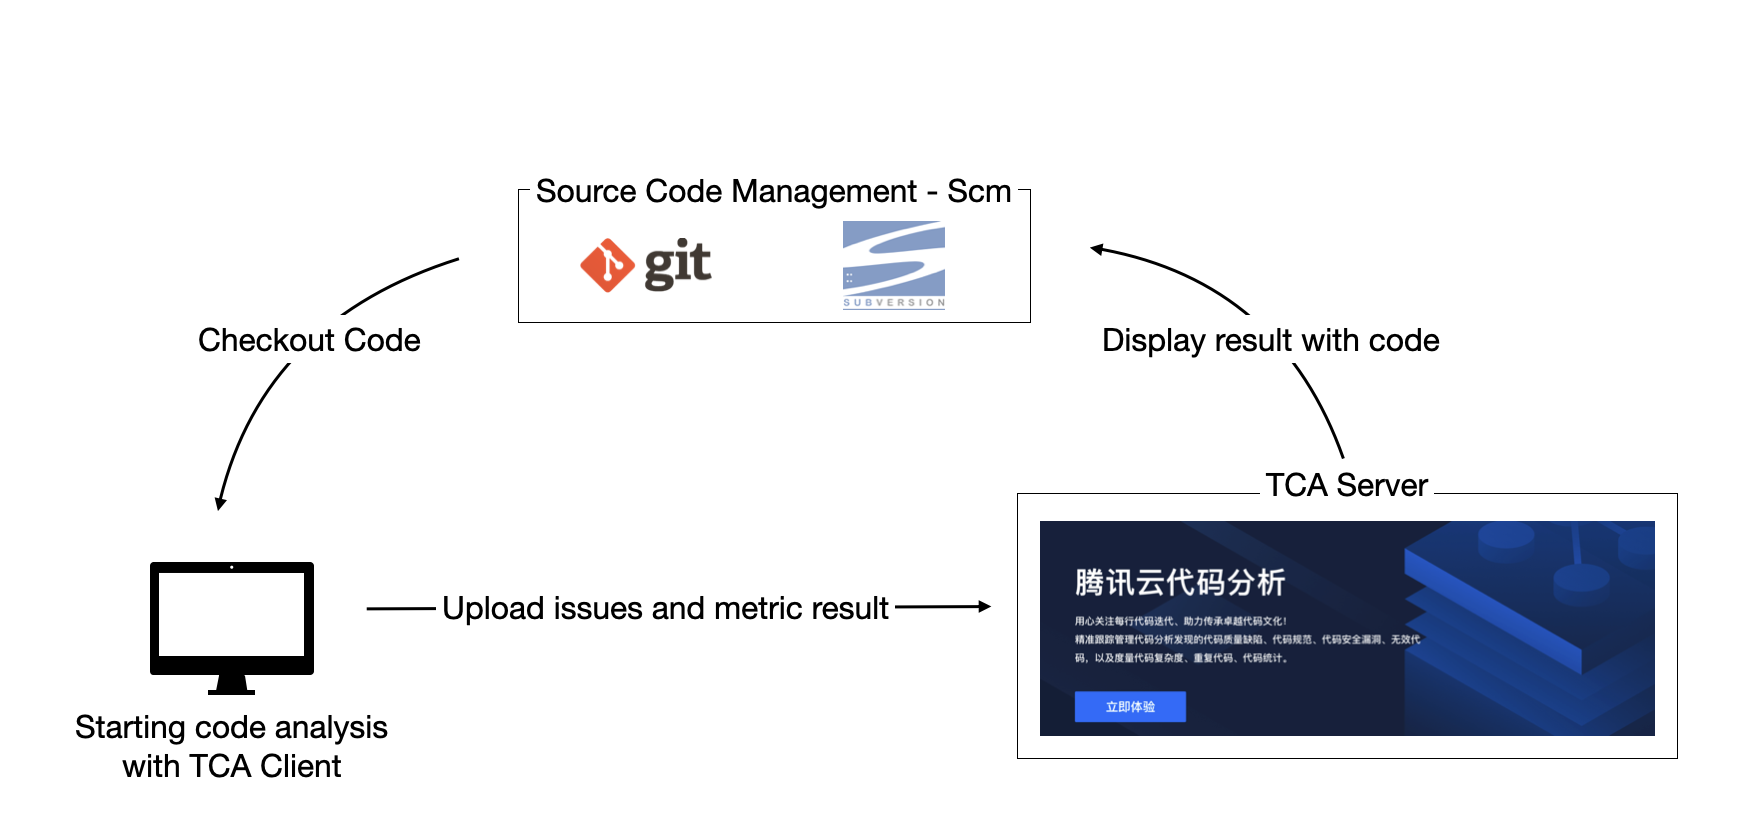 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 msanft/cve-2025-55182
PoC exploit for CVE-2025-55182, demonstrating remote code execution in React Server Functions via prototype pollution and a crafted Flight Protocol…
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications








