
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 far00t01/cve-2025-43960
PHP Object Injection exploit for Adminer <4.8.1 via Monolog, causing Denial of Service through crafted serialized payloads. Includes PoC, CVSS…
 oscerd/cve-2026-49042
PoC reproducer for CVE-2026-49042 (Apache Camel camel-langchain4j-tools): a prompt-injected LLM's tool-call arguments become unfiltered Exchange…
 v3s9er/cve-2026-52885
Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
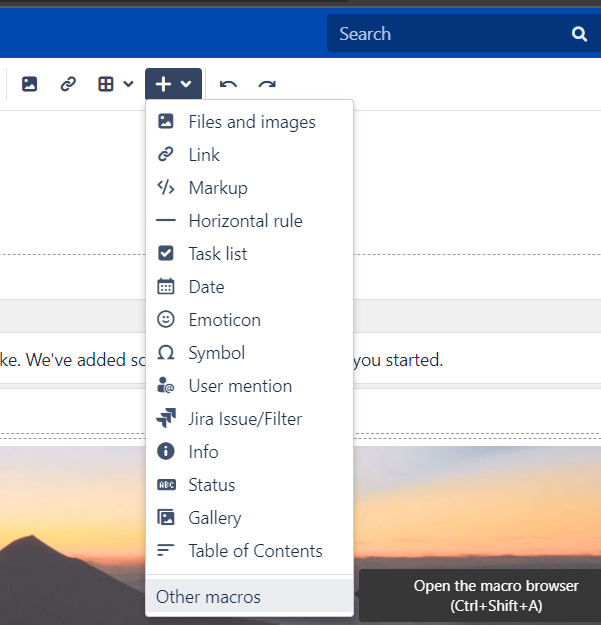 petrusviet/cve-2019-3396
Confluence unauthorize template injection
 us3r777/cve-2018-20718
Proof-of-concept exploit for CVE-2018-20718, a PHP object injection vulnerability in Pydio before 8.2.1 enabling unauthenticated remote code…
 breadsquad/ediop3php
A PHP CVE-2025-1219 SCANNER. In bash no root.
 ademking/cve-2025-49113-nuclei-template
CVE-2025-49113 - Roundcube <= 1.6.10 Post-Auth RCE via PHP Object Deserialization
 murrez/cve-2026-97160
Python PoC for CVE-2026-97160: detects vulnerable Joomla UP plugin versions and verifies PHP code execution via {up php=} shortcode in public…
 vpn28/cve-2021-34481
Check patch for CVE-2021-34481
 fazilbaig1/cve-2026-16723
This is N-day patch we releasing by testing our model capabilities
 callmejonas/cve-2015-6576
A PoC for the Bamboo deserialization exploit
 dhammon/pfblockerng-cve-2022-40624
Proof-of-concept exploit for unauthenticated remote code execution in pfBlockerNg via unsanitized input in the DNSBL TLD query function, with SAST…
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
 george0papasotiriou/cve-2026-23008-solidity-assembly-return-data-size-confusion
Educational PoC for Solidity assembly return-data size confusion; includes vulnerable contract, exploit simulation, and mitigation guidance for…
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 lazarus0x1337/cve-2026-25632
CVE-2026-25632 — Fix Unsafe JSON Deserialization Leading to Remote Code Execution
 george-petrakis/log4j-scanner-cve-2021-44228
Simple tool for scanning entire directories for attempts of CVE-2021-44228








