
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
 windecks/cve-2023-46404
PoC and Writeup for CVE-2023-46404.

 guardia-ai/gitlab-component
EU AI Act compliance scanner for GitLab CI/CD pipelines — detects AI/ML libraries and posts risk classification as MR comments.
 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 nmurilo/cve-2008-4687-exploit
Python exploit for CVE-2008-4687 targeting remote code execution in MantisBT via crafted sort parameter in manage_proj_page.php.
 manhndd/cve-2019-19204
Heap-buffer-overflow in Oniguruma (function fetch_interval_quantifier)
 manhndd/cve-2019-19203
Heap-buffer-overflow in Oniguruma (function gb18030_mbc_enc_len)
 vivian.maes/bad-secure-rails-app
 pandamingx/cve-2020-5421
Spring 安全漏洞 CVE-2020-5421复现
 ch4120n/cve-2026-58138
CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).
 r00t4dm/jenkins-cve-2017-1000353
Proof-of-concept exploit for Jenkins CVE-2017-1000353, a remote code execution vulnerability via unsafe deserialization in the CLI interface.
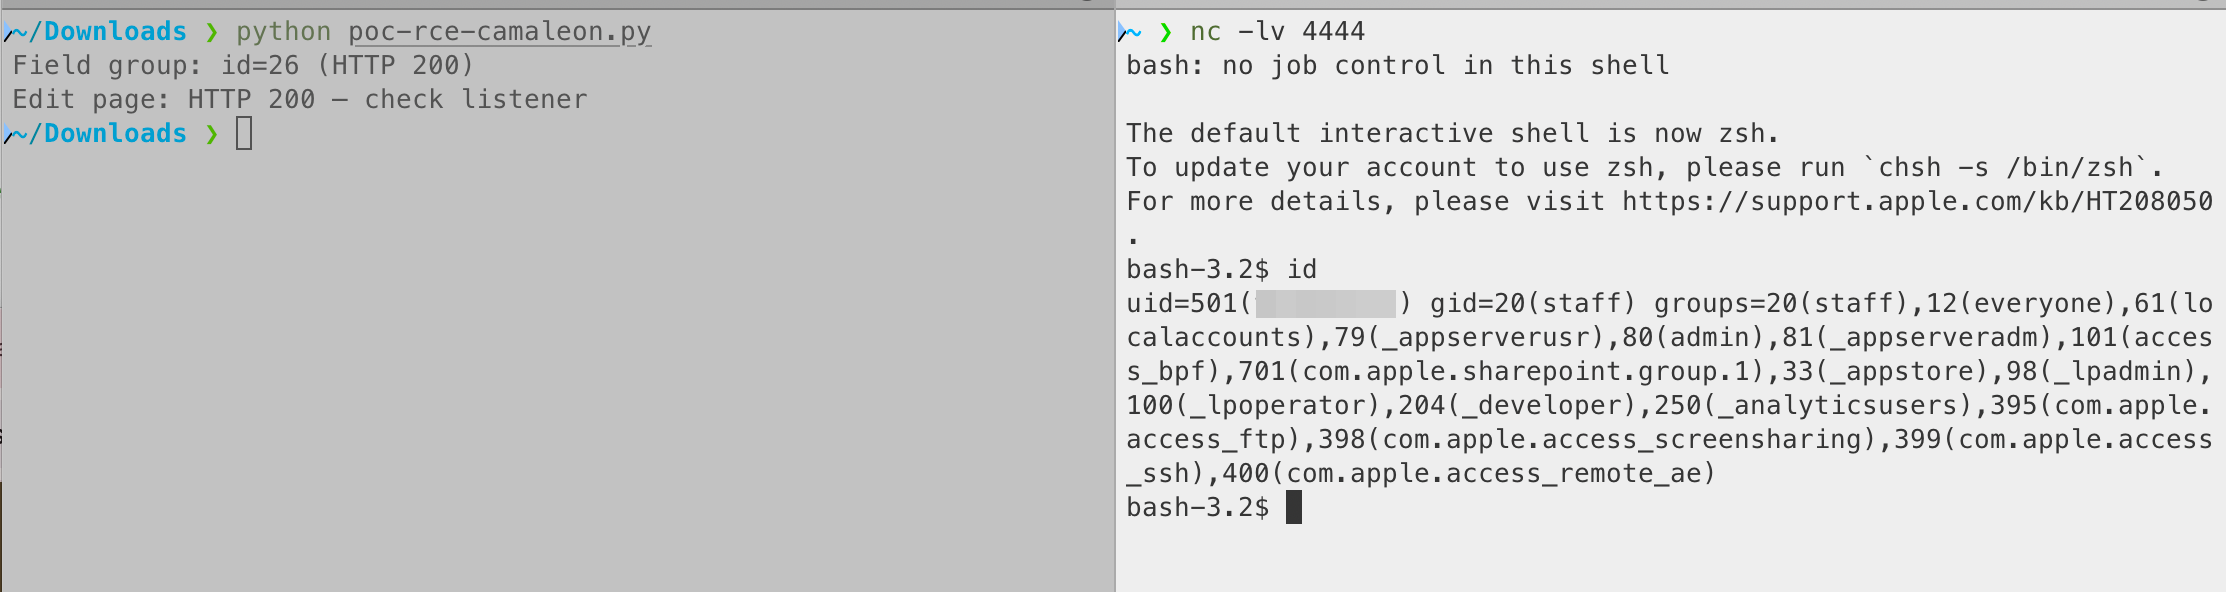 theopaid/cve-2026-66748-camaleon-cms---authenticated-rce-via-select_eval-custom-field
Security Advisory: Camaleon CMS - Authenticated RCE via `select_eval` Custom Field
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
 nxgn-kd01/react2shell-scanner
Detect CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Fast, accurate scanner with zero false positives.
 datawiza-inc/spring-rec-demo
The demo code showing the recent Spring4Shell RCE (CVE-2022-22965)
 louiselalanne/cve-2024-23746
Miro Desktop 0.8.18 on macOS allows Electron code injection.
 oscerd/cve-2026-40047
Reproducer for CVE-2026-40047: Apache Camel camel-docling CLI argument injection / path traversal








