
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 secoba/djvul_stringagg
Django StringAgg SQL Injection (CVE-2020-7471)
 gduma-phdata/patch-cve-2026-10520
Patch for Apache Struts OGNL injection vulnerability (CVE-2026-10520), currently in review and deployed to production.
 artwiderobo/cve-2026-13934
Structured vulnerability research repo for a Chrome Dawn WebGPU CWE-20 flaw: root cause, patch diff, static verification, severity review, and…
 theopaid/cve-2026-66753-http-header-injection-via-unvalidated-cr-and-lf-in-header-values-tiny_http-
Security Advisory: HTTP Header Injection via Unvalidated CR and LF in Header Values (tiny_http)
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 fevar54/cve-2026-72530-trueconf-sandbox-escape-
Este repositorio contiene una demostración educativa de la mitigación y detección para **CVE-2026-72530**, una vulnerabilidad crítica de **Code…
 theopaid/cve-2026-66751-insufficient-access-controls-allow-for-unauthorized-room-deletion-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized Room Deletion (Let's Chat)
 theopaid/cve-2026-66749-unchecked-room-lookup-leads-to-server-crash-let-s-chat-
Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)
 sourcegraph/log4j-cve-code-search-resources
Using code search to help fix/mitigate log4j CVE-2021-44228
 horkimhab/cve-2022-31626-cve-2024-2961-cve-2019-6977
CVE-2022-31626, CVE-2024-2961, CVE-2019-6977, PHP security research
 theopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-
Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)
 jenkinsci-cert/security-3430
Java agent that transforms a vulnerable class to block exploitation of CVE-2024-43044 in Jenkins controllers, with optional forced shutdown on…
 halahajyahia/cve-2022-2869-detector
CodeQL detector for CVE-2022-2869 root cause (CWE-191 unsigned underflow) using control-flow/range analysis to identify vulnerable patterns without…
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
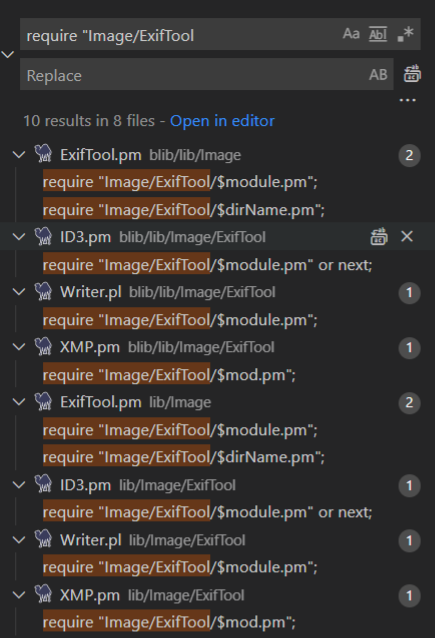 trganda/cve-2021-22204
In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…
 r0ngy40/cve-2025-30208-series
Analysis of the Reproduction of CVE-2025-30208 Series Vulnerabilities
 awusan125/test_for6387
test code for cve-2024-6387








