
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended

 sne-m23-sn/vulnerable-docker-engine
This exploit offers an in-depth look at the CVE-2021-41091 security vulnerability and provides a step-by-step guide on how to utilize the exploit…
 ahndrewalters/projectsecurity-homelab
Hands-on homelab simulating the Log4Shell (CVE-2021-44228) vulnerability. Deploy Docker containers to build a vulnerable target and attacker machine,…
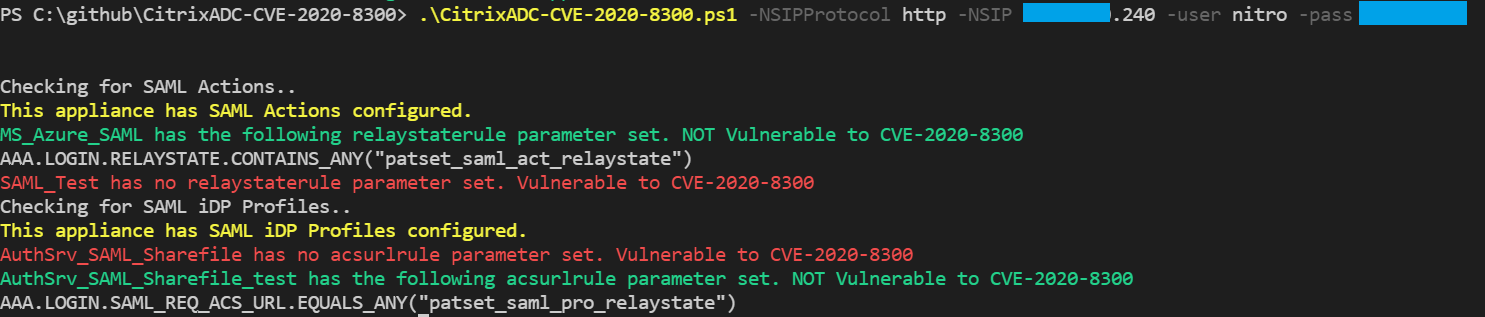 stuartcarroll/citrixadc-cve-2020-8300
Detect Citrix ADC SAML action or SAML iDP Profile config vulnerable to CVE-2020-8300 using Citrix ADC NITRO API
 completetech-security/copyescape-check
Offline Docker CopyEscape evidence checker for CVE-2026-17106. Docker version and build-configuration evidence. Standalone Python; JSON/CSV/HTML…
 craig-m-unsw/omigod-lab
A Vagrant VM test lab to learn about CVE-2021-38647 in the Open Management Infrastructure agent (aka "omigod").

 divyanshukumar0014/shipproof
Automated SOC 2 change management for GitLab CI.
 completetech-security/docker-hub-ghostpat-check
Offline Docker Hub PAT evidence checker for CVE-2026-105445. Supplied evidence only; no token collection, login or API requests. JSON/CSV/HTML…
 benzamir/cve-2026-7791
Local Privilege Escalation in Amazon WorkSpaces via TOCTOU and Arbitrary File Write
 taroballzchen/cve-2023-28432-metasploit-scanner
MinIO Information Disclosure Vulnerability scanner by metasploit
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 baymaxpop23/attackmapper
attackmapper
 jeffbryner/log4j-docker-vaccine
docker compose solution to run a vaccine environment for the log4j2 vulnerability CVE-2021-44228
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…
 andypitcher/check_struts
Apache Struts version analyzer (Ansible) based on CVE-2017-5638
 yamory/cve-2021-32804
Docker-based reproduction environment for CVE-2021-32804, a path traversal vulnerability in node-tar affecting npm, with step-by-step exploitation…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 joebeeton/cve-2024-4701-poc
POC for CVE-2024-4701








