Offline Docker CopyEscape evidence checker for CVE-2026-17106. Docker version and build-configuration evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.



Docker copy destination escape
CVE-2026-17106 · offline version triage
copyescape-check is the dedicated repository for CVE-2026-17106 (alias GHSA-hfg8-hc9c-6c3h), a flaw where a crafted archive can make docker cp copy-out (and other moby/go-archive extraction) write outside the intended destination.
It is a standalone, standard-library-only Python 3.10+ tool that compares operator-reported versions of Docker Engine/CLI, Docker Desktop and moby/go-archive with the published fixes, and reports uncertainty honestly. It makes no network requests, runs no Docker or application code, and never tests exploitability. By CompleteTech LLC.
[!IMPORTANT] A version comparison is evidence, not verified runtime state. A
potentially_affectedresult is not confirmed exploitability, andfixed_version_reportedis not a safety guarantee or a verified deployed patch. Vendor backports and custom builds are not detectable from a version string.
| Field | Scope |
|---|---|
| Exploit identifier | CVE-2026-17106 |
| Aliases for this same exploit | GHSA-hfg8-hc9c-6c3h |
| Rules reviewed against primary sources | 2026-10-24 |
| Implementation state | Implemented (offline version triage) |
Aliases and multiple affected products identify this same exploit; they do not create additional scanner scopes. Fixes for different vulnerabilities belong in independent repositories.
python3, substitute it in the commands below.python copyescape_check.py --version docker-engine=29.6.2 --version go-archive=0.2.5 --format json
python copyescape_check.py --inventory inventory.json --format html --output report.html
python copyescape_check.py --csv components.csv --fail-on-finding
In the first command, Engine 29.6.2 is below the reported fix (potentially_affected), and go-archive 0.2.5 falls in a range where the sources disagree (unknown, never safe).
Run python copyescape_check.py --help for usage and exit codes, and python copyescape_check.py --tool-version for the checker version. Run the tests with python -m unittest -v. Inputs, fields and output formats are documented in the reference.
The images show the HTML report rendered from the synthetic, reserved-name inputs in docs/example-inventory.json; the output is docs/example-report.html. They are an example of the checker's real output, not an assessment of any system.
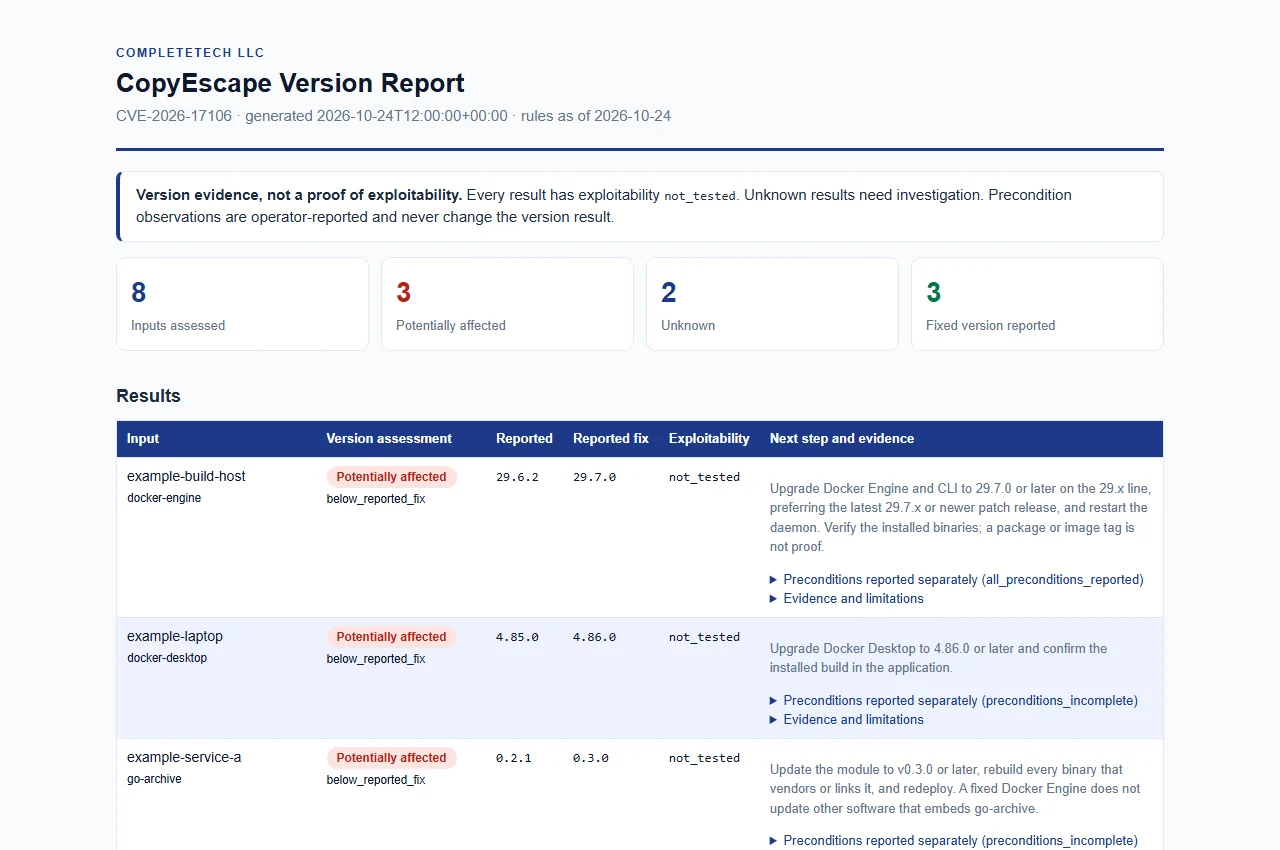
Synthetic example generated from made-up inputs; not a real assessment.
copyescape_status (the version status) is separate from precondition observations and from exploitability.
| Status | Meaning |
|---|---|
potentially_affected | The reported plain version is below the reported fix on the one release line the sources cover. Not confirmed exploitability. |
fixed_version_reported | The reported plain version meets the reported fix. Not a guarantee that the deployed build is patched. |
unknown | Missing, malformed, prerelease, qualified, vendor/custom-build, conflicting, disputed-range, or uncovered-line versions. Review these; they never change the exit code. |
not_tested for every result.docker cp copy-out or go-archive extraction, host filesystem write privileges) can be supplied as operator observations. They are reported alongside the version result and never change it.unsupported_runtime is not used: the vendor sources reviewed do not publish lifecycle evidence for these components in this context.x.y.z versions (optional leading v) are compared; everything else stays unknown.The full list of version-status reasons and report fields is in the reference.
Reviewed 2026-10-24 against the primary sources below. Rules are a dated offline snapshot (rules_as_of appears in every report); recheck the advisories before relying on an old copy of this tool.
| Component | Reported fixed version | Line assessed | Source |
|---|---|---|---|
| Docker Engine / CLI | 29.7.0 | 29.x | Docker Engine v29 release notes |
| Docker Desktop | 4.86.0 | 4.x | Docker security announcements |
moby/go-archive | 0.3.0 | 0.x | Publisher and GitHub-reviewed advisories |
Boundary handling and limits:


