
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended

 apogiatzis/docker-cve-2021-3156
A docker environment to research CVE-2021-3156
 morpheuslord/cloudg
Map, graph and audit AWS, Azure and GCP from one CLI. Builds a topology graph, runs Prowler/Checkov/Trivy, tags findings against 28 compliance…
 kingofbugbounty/nuclearpond-ofjaaah
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 zwxxb/cve-2025-1974
Poc for Ingress RCE
 akhld/spark-exploit
Arbitary Code Execution in Unsecured Apache Spark Cluster
 piratesshield/arise-xti
AI-driven external attack surface management pipeline: 28 modules for recon, subdomain/DNS enumeration, web/API/cloud vulnerability scanning, OSINT…
 killswitch-gui/flask_heroku_redirector
flask heroku C2 redirector template
 d3vzer0/cnc-relay
Docker projects to retain beacon source IPs using C2 relaying infra
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 elonma-china/lab-cve-2
10 Docker CVE pentest labs (5 ExploitDB / 3 public-PoC / 2 zero-day)
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 movray/meles
Malware scanner for container images: daemonless, layer-aware, ClamAV and YARA
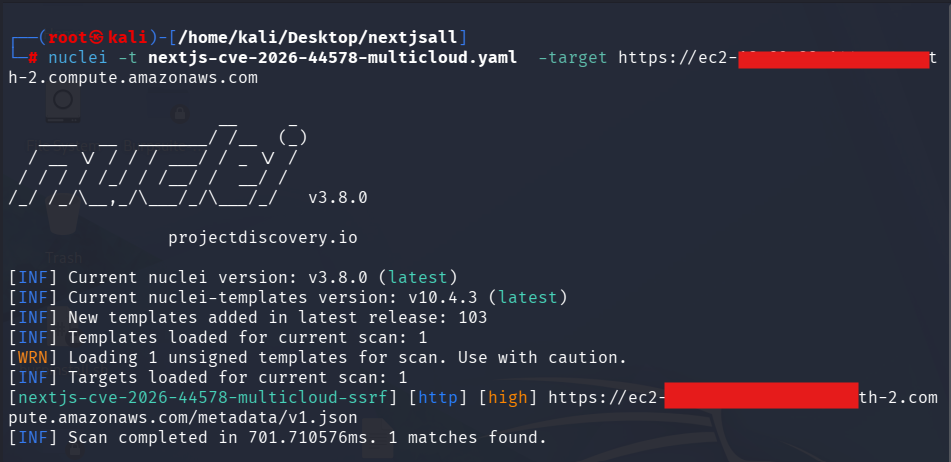 love07oj/nextjs-cve-2026-44578
Nuclei templates for detecting CVE-2026-44578 (Next.js WebSocket Upgrade SSRF) with multi-cloud metadata validation, Next.js fingerprinting, and…
 shaoshi17/cve-2025-9074-docker-exploit
一个功能强大的 Docker 远程 API 漏洞利用工具,用于 CVE-2025-9074 漏洞的安全研究和测试。








