
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended
 bishopfox/smogcloud
Find cloud assets that no one wants exposed 🔎 ☁️
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 microsoft/igvm
Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…
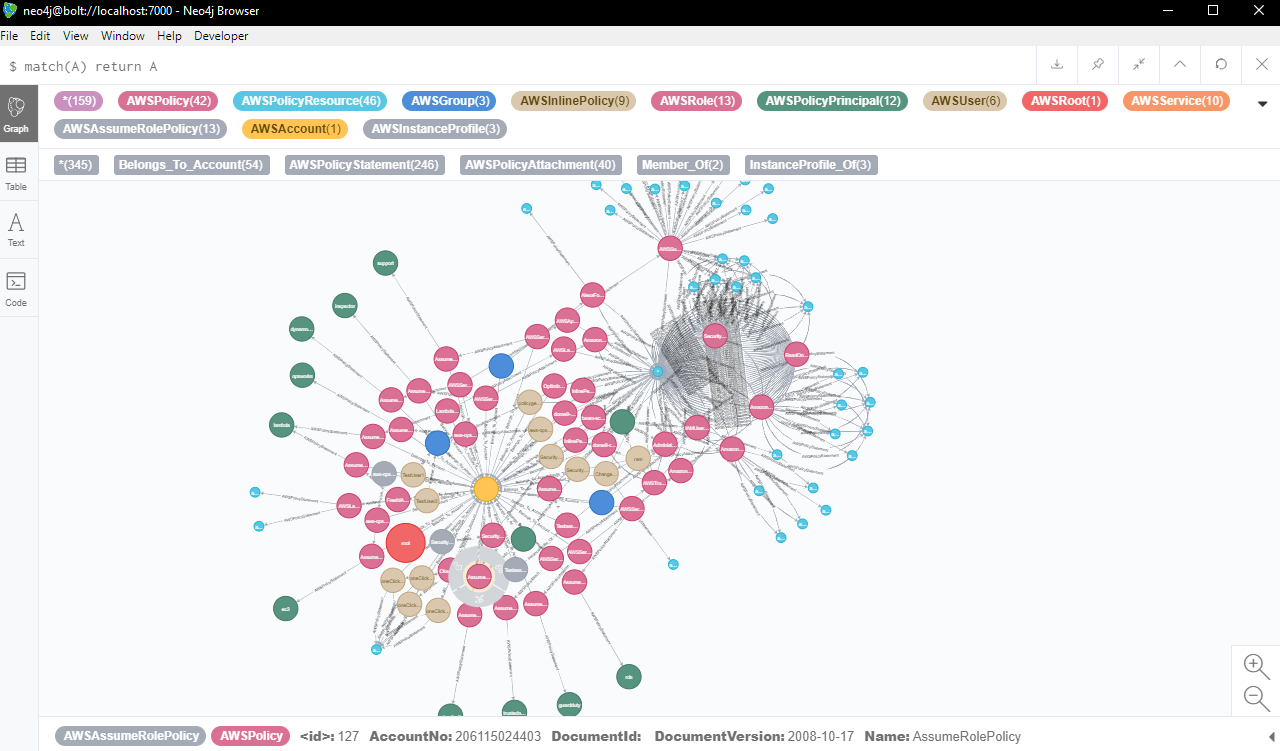 rams3sh/aaia
AWS Identity and Access Management Visualizer and Anomaly Finder
 spacesiren/spacesiren
A honey token manager and alert system for AWS.
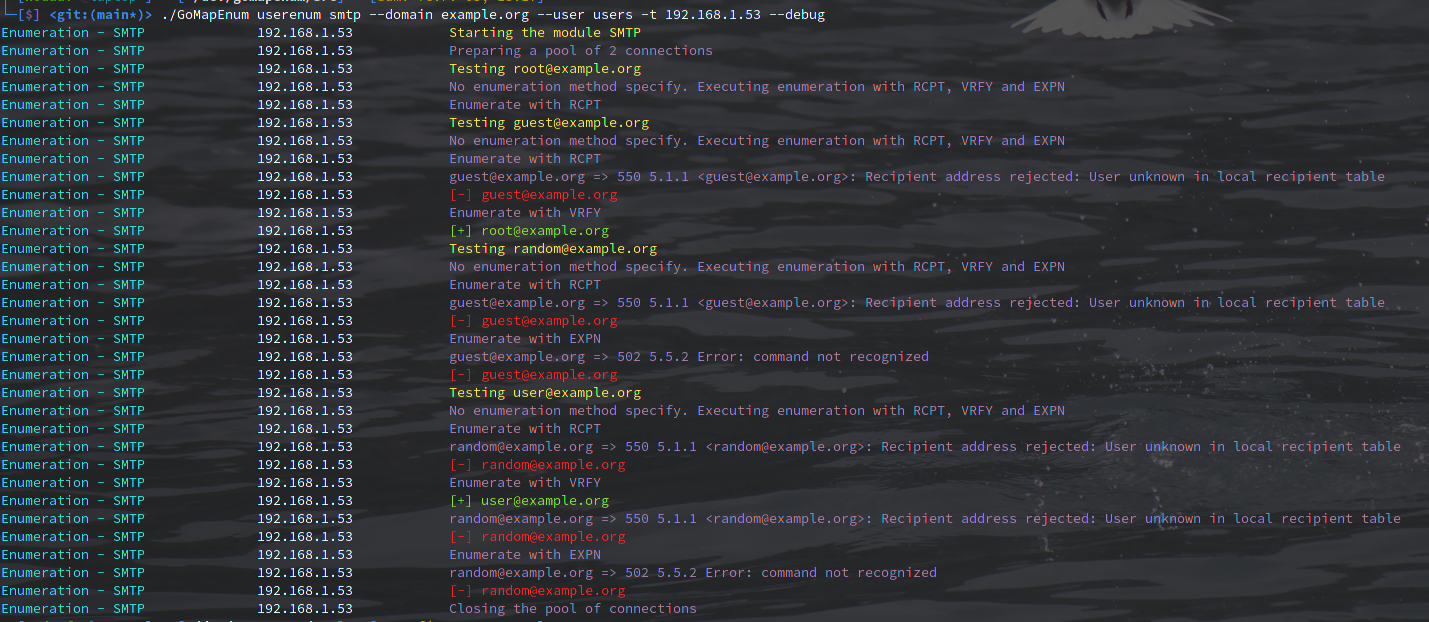 nodauf/gomapenum
User enumeration and password bruteforce on Azure, ADFS, OWA, O365, Teams and gather emails on Linkedin
 g0ldencybersec/cloudrecon
Suite of tools for red teamers and bug hunters to discover ephemeral cloud assets by scanning IP ranges and inspecting SSL certificates for hidden…
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
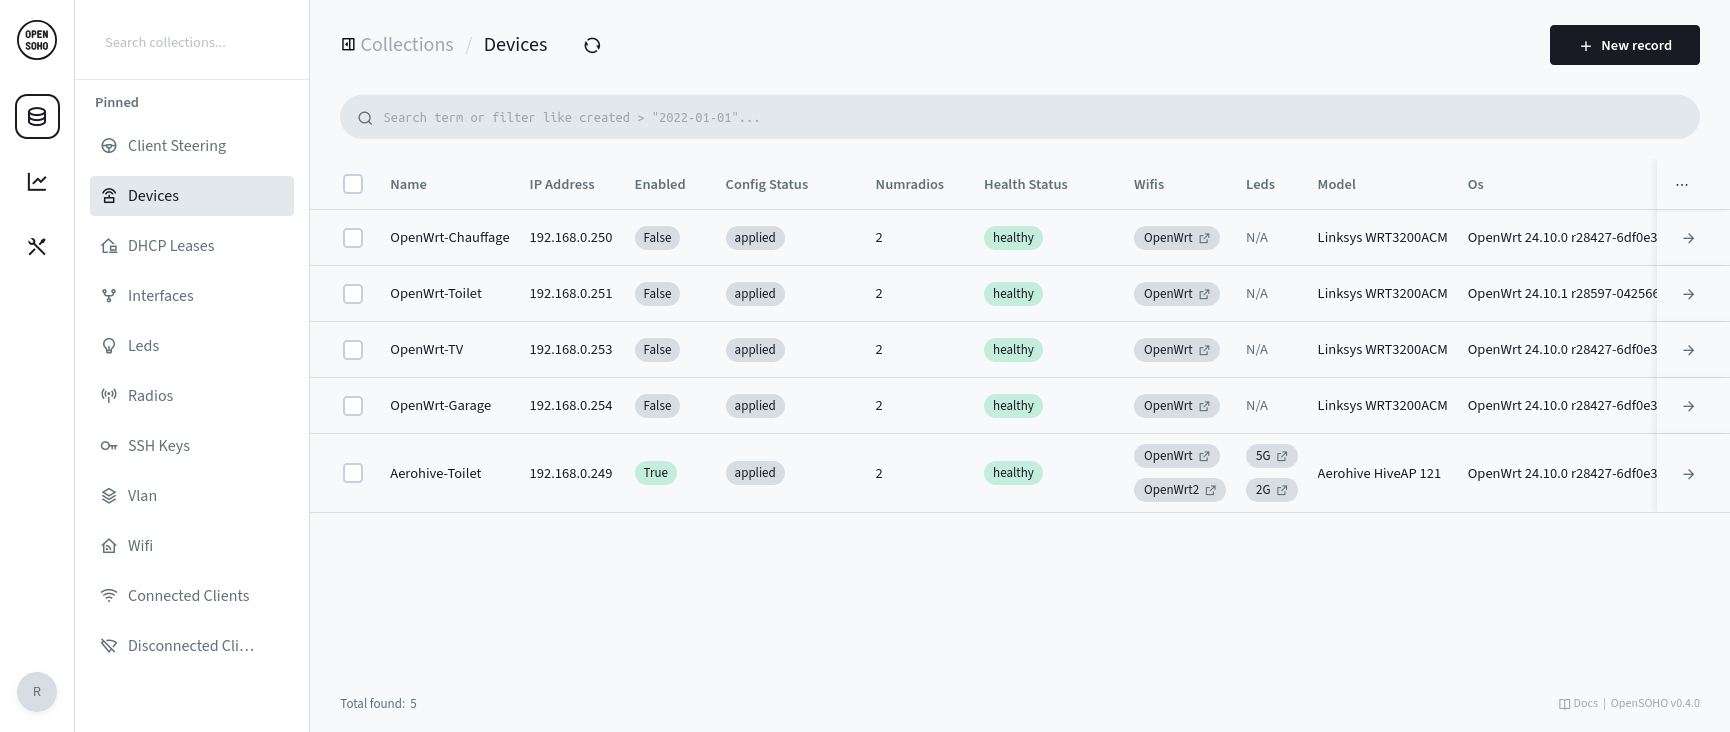 rubenbe/opensoho
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…
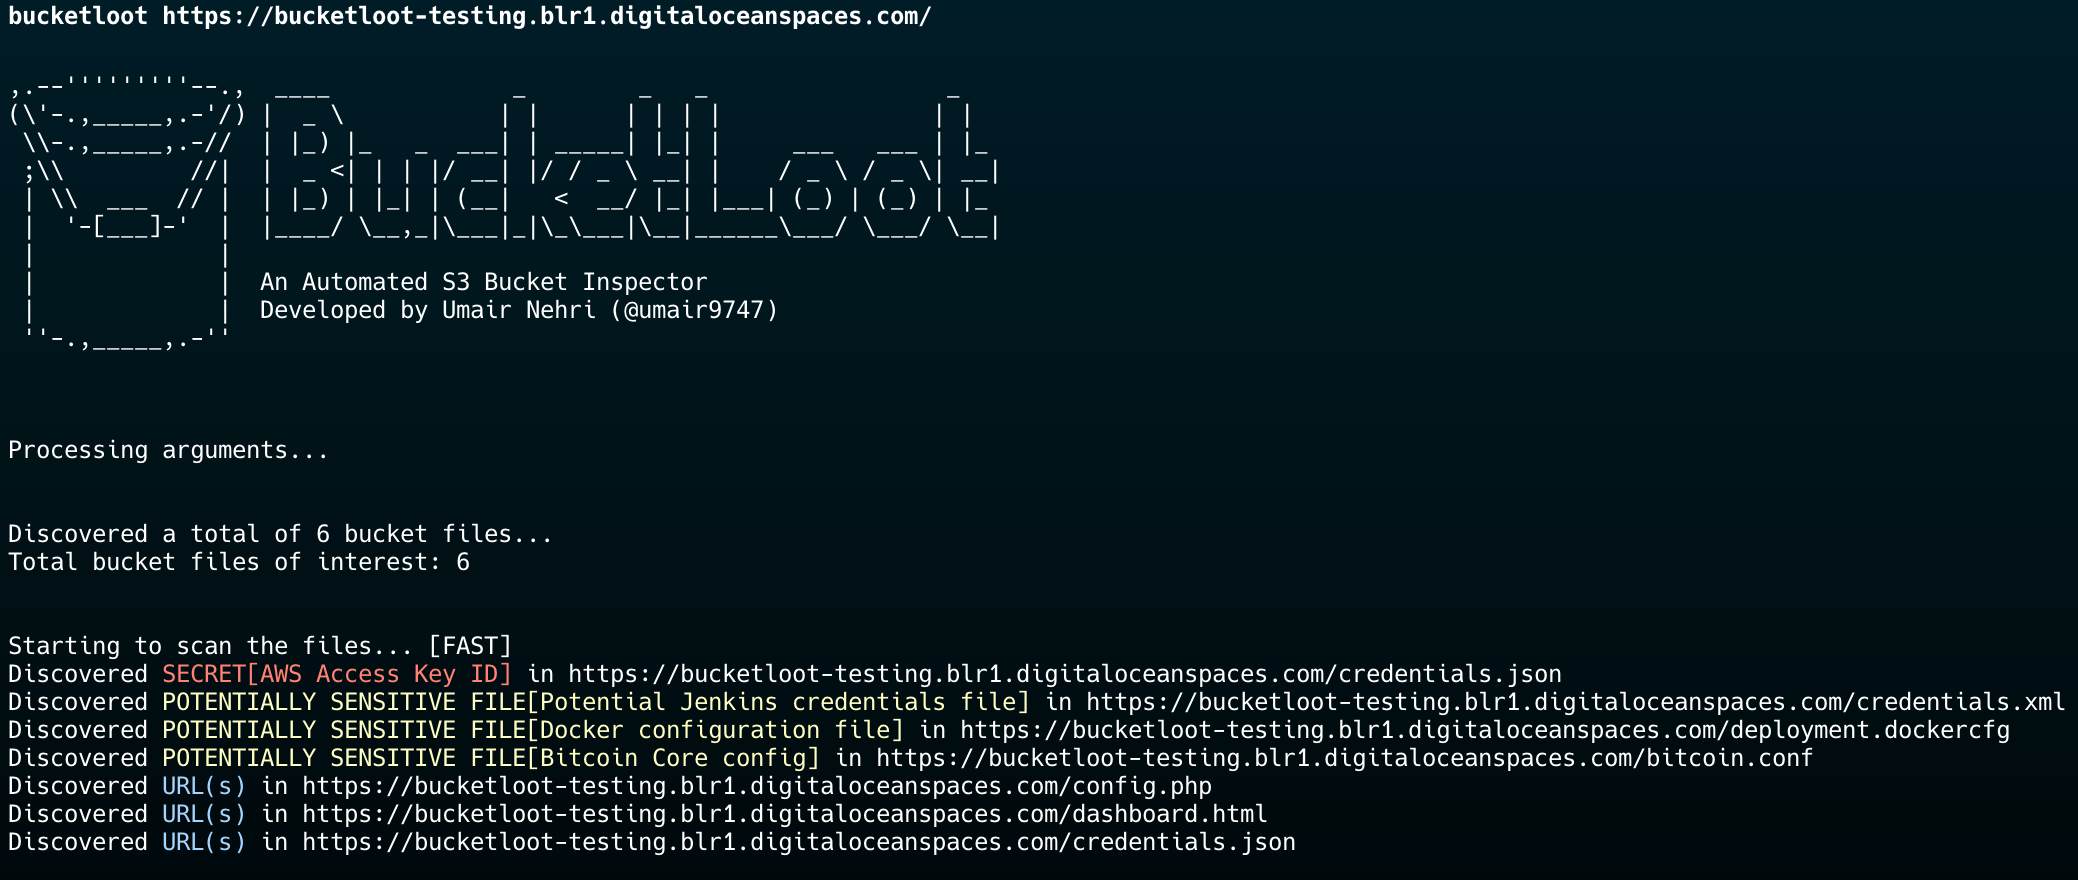 redhuntlabs/bucketloot
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…
 assetnote/ghostbuster
Eliminate dangling elastic IPs by performing analysis on your resources within all your AWS accounts.
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
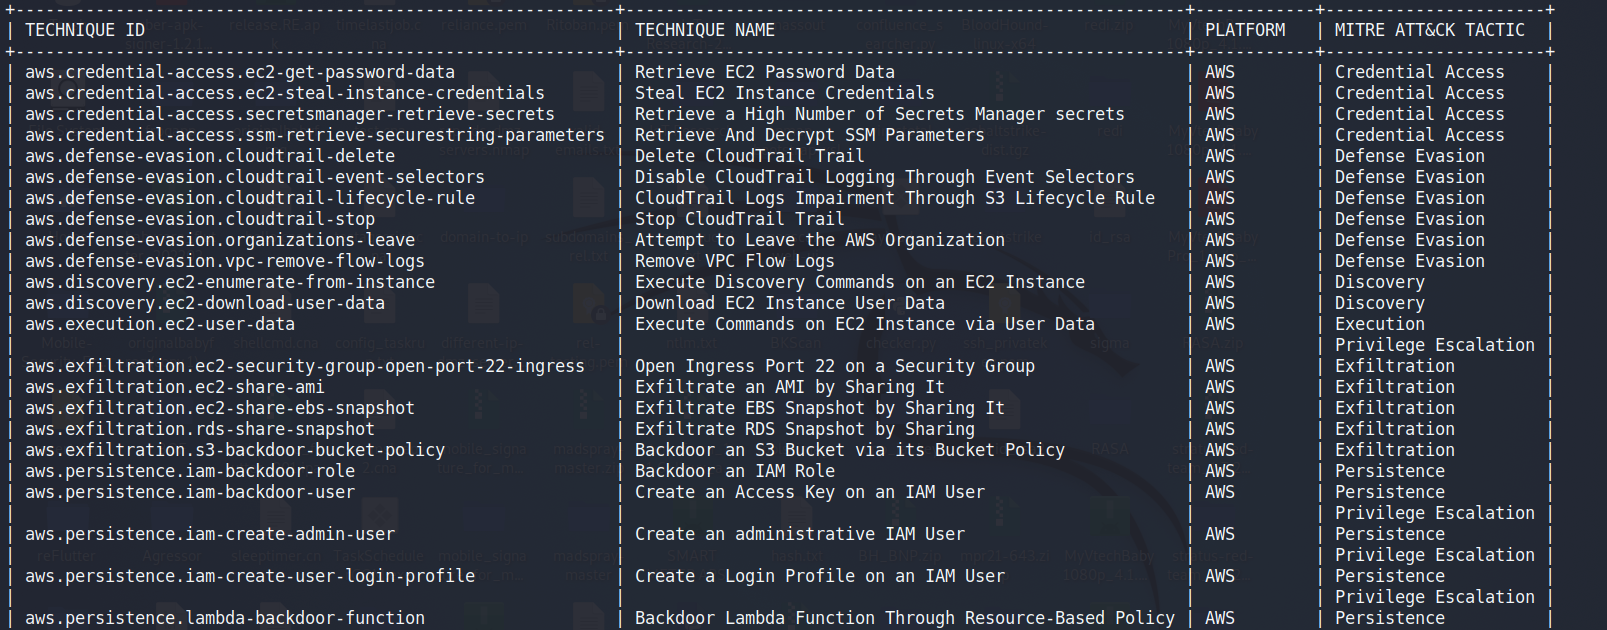 sbasu7241/aws-threat-simulation-and-detection
Playing around with Stratus Red Team (Cloud Attack simulation tool) and SumoLogic








