
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended

 cobbbex/cisco-asa-vulnerability-research
Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…
 m507/cve-2017-13156
To determine if an APK is vulnerable to CVE-2017-13156
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 v3cn4x00/poc-cve-2025-66034
Automated exploit for CVE-2025-66034, chaining path traversal and XML injection in fontTools varLib to achieve unauthenticated remote code execution…

 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
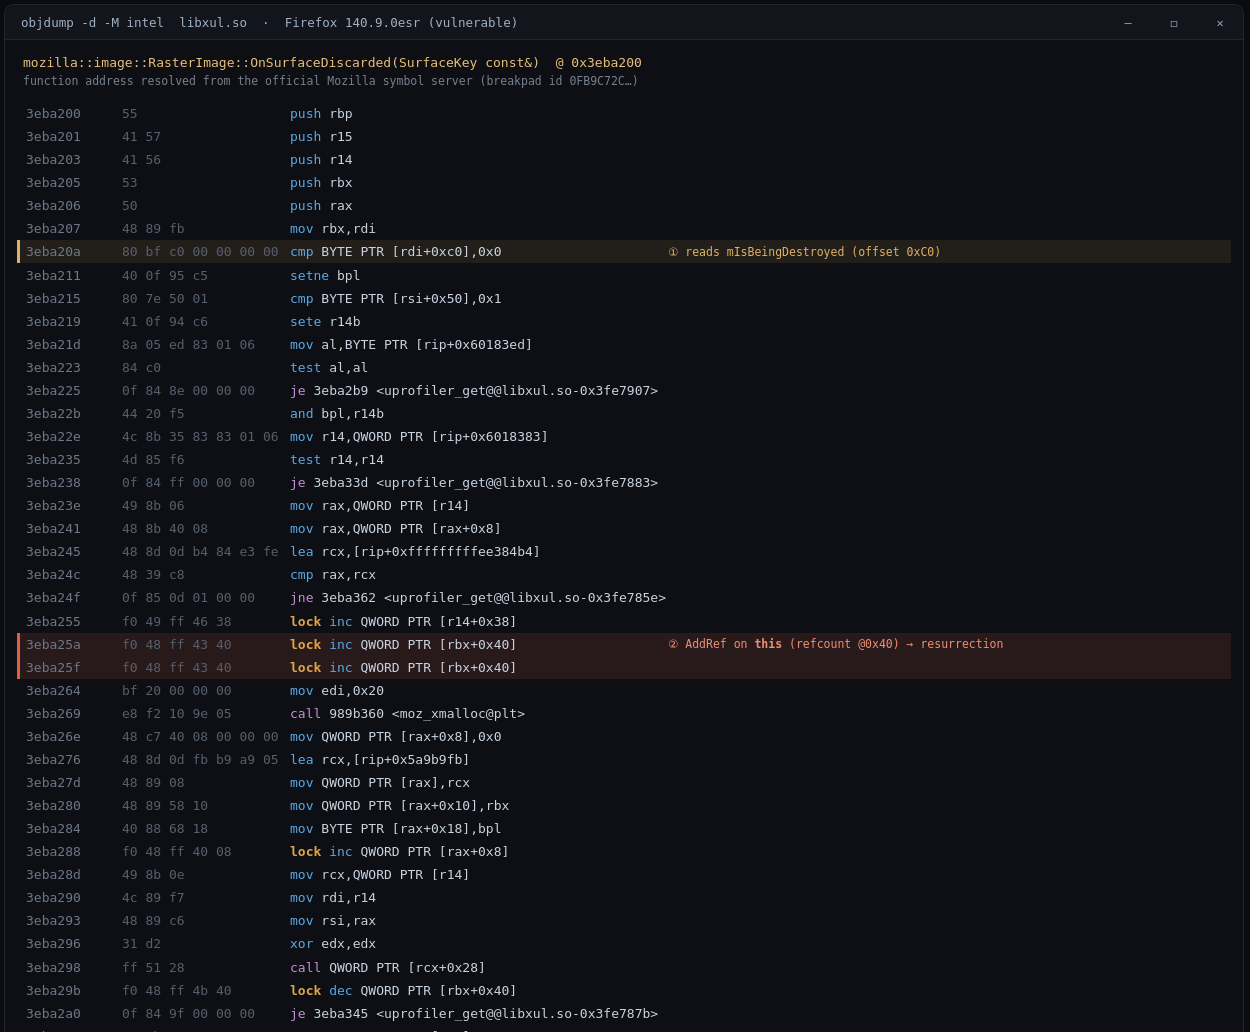 defineid/revenant
CVE-2026-74943, Use after free in Firefox RasterImage (sec-high)
 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
 binaryhardening/cfgrip
Disassembles PE/ELF x86/x64 binaries, resolves indirect branches via GOT, jump tables, and register tracing, and exports the full control flow graph…
 murf-xd/cve-2023-20768
Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
 oitapps/find-vulnerableelectronversion
Scans an executable and determines if it was wrapped in an Electron version vulnerable to the Chromium vulnerability CVE-2023-4863/ CVE-2023-5129
 davidbuchanan314/cve-2017-13672
POCs for CVE-2017-13672 (OOB read in VGA Cirrus QEMU driver, causing DoS)
 partywavesec/invesalius3_vulnerabilities
InVesalius discovered CVE. CVE-2024-42845, CVE-2024-44825
 themalwareguardian/cve-2024-7344
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…
 infobyte/isa_recovery
ISA Recovery








