
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended
 ish3ng0m4/cve-2026-24061-telnetd
CVE-2026-24061 GNU Inetutils Telnetd Authentication Bypass
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 trinadh465/openssl-1_0_1g_cve-2015-3194
OpenSSL 1.0.1g source code snapshot, providing SSL/TLS and general-purpose cryptographic library with ciphers, digests, and X.509 certificate…
 fr3d-/moodle-token-stealer
CVE-2019-14830
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…
 elevenpaths/latch-plugin-openvpn-as
Latch plugin for OpenVPN Access Server enabling two-factor authentication (2FA) to secure VPN connections with time-based one-time passwords (TOTP).
 kajzingerakos/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…
 kit-lang/packages/kit-jwt
JSON Web Token (JWT) encoding and decoding for Kit
 bimboxh4/cve-2025-66039_cve-2025-61675_cve-2025-61678_reepbx
This vulnerability allows both authenticated and unauthenticated remote attackers to execute remote code on vulnerable FreePBX instances. These…
 1872892142/jboss-autopwn-1
JBoss Autopwn as featured at BlackHat Europe 2010 - this version incorporates CVE-2010-0738 the JBoss authentication bypass VERB manipulation…
 minh3102011/cve-2026-18963_analyst
Docker-based lab for reproducing Keycloak CVE-2026-18963, including vulnerable version setup, realm seeding, and source-level workflow analysis with…
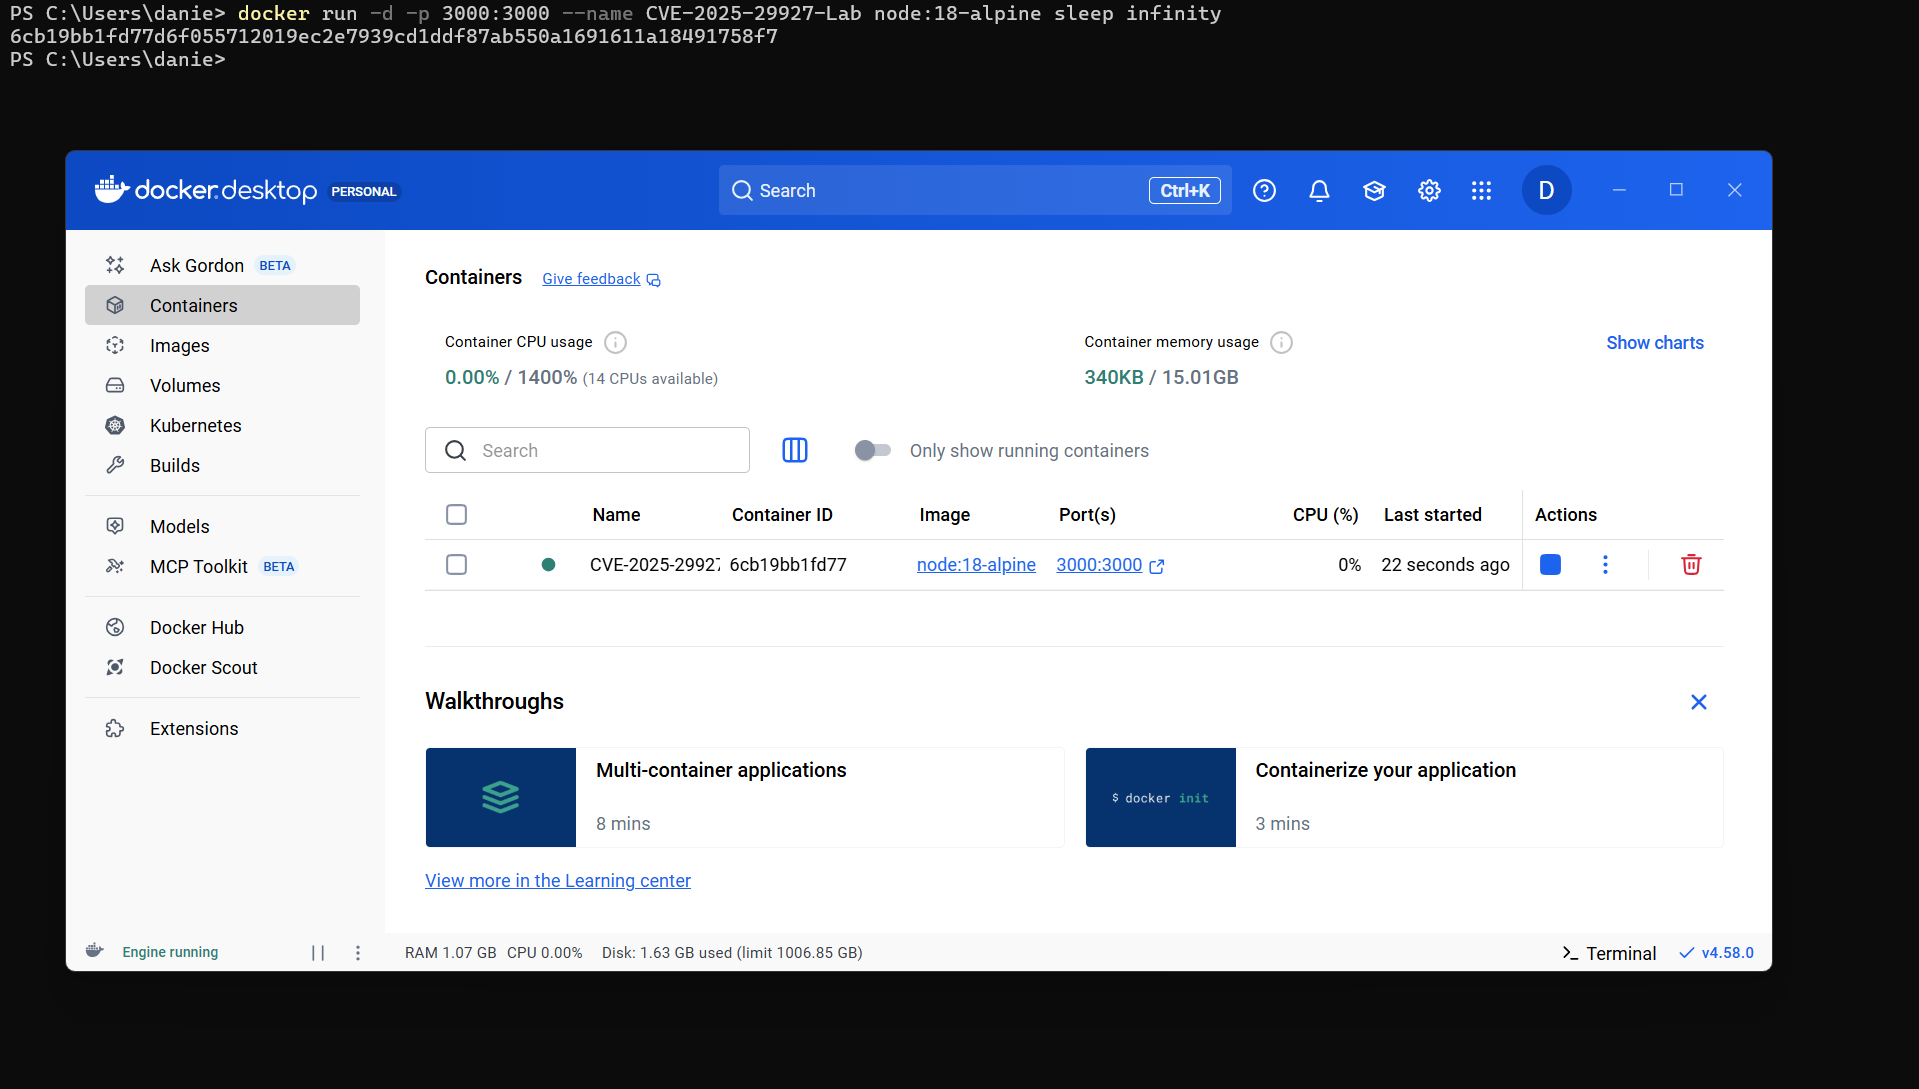 danielhallbro/cve-2025-29927-nextjs-bypass-poc
A Proof of Concept for CVE-2025-29927 demonstrating a middleware bypass in Next.js versions prior to 13.5.9
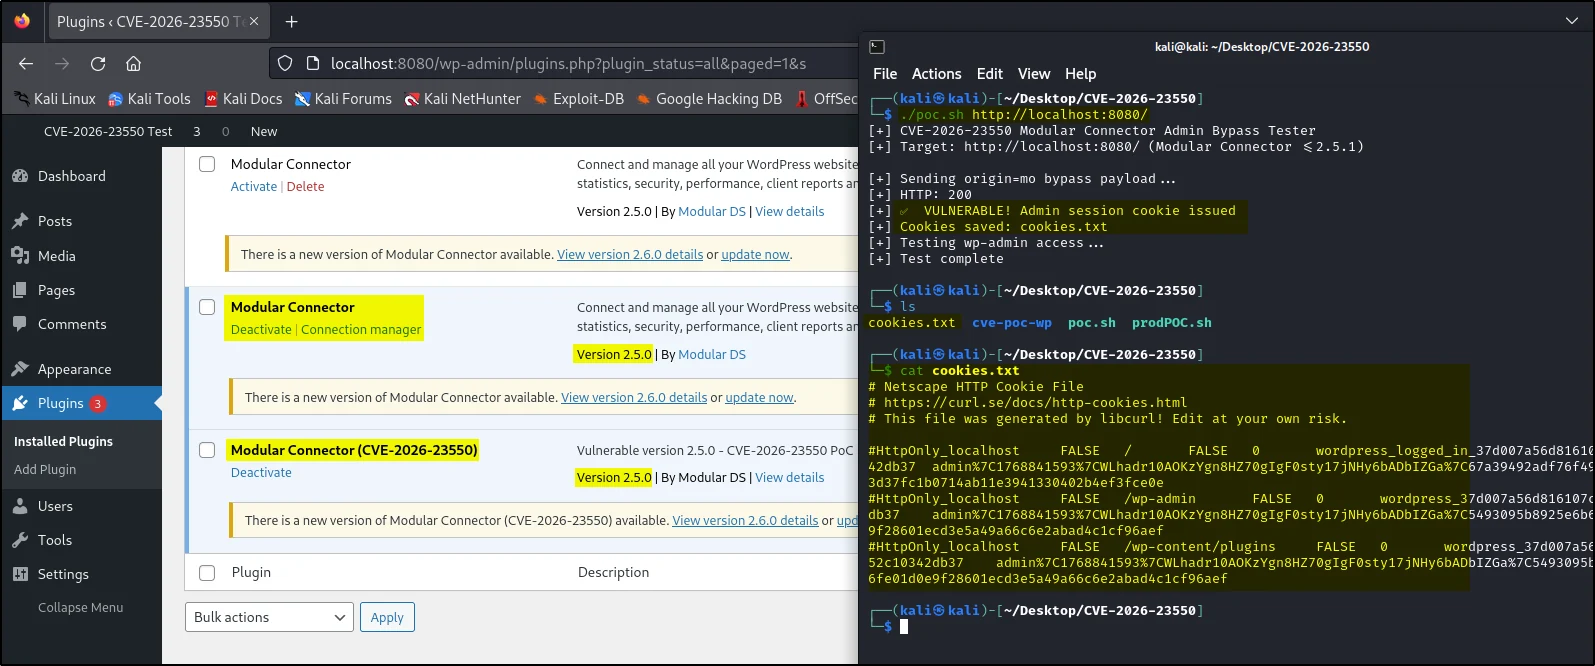 thetorjancaptain/cve-2026-23550-poc
CVE-2026-23550 - Modular DS WordPress Plugin **Unauthenticated Admin Access**
 kartik2005221/cve-2025-58434-poc
Proof-of-concept exploit for CVE-2025-58434, demonstrating unauthenticated account takeover in Flowise via leaked password reset tokens. Includes…
 yuxblank/cve-2022-2466---request-context-not-terminated-with-graphql
Proof-of-concept for CVE-2022-2466 demonstrating unauthenticated GraphQL request context termination in Quarkus/SmallRye, bypassing authorization…
 0xf3d0rq/cve-2017-7921
CVE-2017-7921 is a critical vulnerability (CVSS score: 9.8) affecting multiple Hikvision IP camera and DVR models, first disclosed in 2017. It stems…
 ptechamanja/cve-2026-29000-pac4j-jwt-auth-bypass
Proof-of-Concept (PoC) for an authentication bypass vulnerability affecting applications using pac4j-jwt with JWE (JSON Web Encryption).
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.








