
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 skynoxk/cve-2025-40554
CVE-2025-40554 Exploitation
 davidxbors/cve-2023-47504-poc
Proof-of-concept exploit for CVE-2023-47504 targeting Elementor WordPress plugin. Requires subscriber credentials and wp-config.php access to delete…
 eynaexp/cve-2024-27198-poc
proof-of-concept mass scanner targeting JetBrains TeamCity instances affected by CVE-2024-27198
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 itzvenom/cve-2023-6329
Python PoC exploit for CVE-2023-6329 authentication bypass in Control iD iDSecure. Reconstructs admin credentials via predictable password derivation…
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
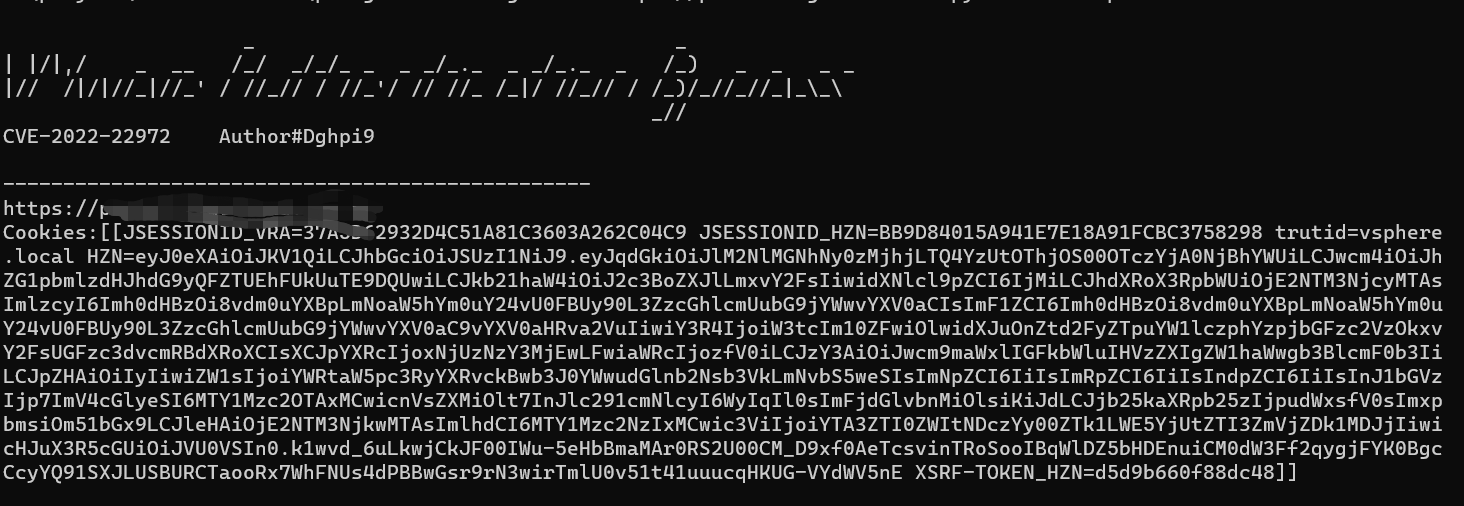 xk4ng/cve-2022-22972
vmware authentication bypass
 nxploited/cve-2025-15521
The Academy LMS – WordPress LMS Plugin for Complete eLearning Solution plugin for WordPress is vulnerable to privilege escalation via account…
 daeda1usuk/cve-2025-59390-
CVE-2025-59390 and ThreadLocalRandom Inverse
 drew-alleman/cve-2020-11651
A script that exploits SaltStack CVE-2020-11651 and CVE-2020-11652 to add new users to a vulnerable Salt master by injecting entries into /etc/passwd…
 gpotter2/cve-2024-20674
Exploit for CVE-2024-20674: Kerberos mutual authentication bypass via logic bug in client-side U2U TGT-REP handling. Enables unauthenticated network…
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 cyb3rmaddy/cve-2023-23397-report
An exploitation demo of Outlook Elevation of Privilege Vulnerability
 starawneh/cve-2025-4094
CVE-2025-4094 – WordPress Digits Plugin < 8.4.6.1 - OTP Authentication Bypass
 jptr218/proftpd_bypass
An implementation of CVE-2015-3306
 iveresk/cve-2022-31749
PoC checker for CVE-2022-31749 exploiting a parameter injection vulnerability in WatchGuard SSH interface to exfiltrate hashed user passwords via FTP.
 honestcorrupt/phonepe-sensitive-data-exposure-cve-2025-5154
CVE-2025-5154: Proof-of-concept for unencrypted local storage of authentication tokens, PII, and KYC data in the PhonePe Android app, enabling…








