
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended

 itres-labs/usbcoercer
USBCoercer turns an ESP32 development board with native USB-OTG into an Ethernet-over-USB gadget capable of coercing proxy configuration via WPAD.
 simoesctt/ctt-enhanced-apache-mod_auth_digest-timing-attack-exploit
Remote timing attack exploit for Apache mod_auth_digest (CVE-2026-33006) that bypasses Digest authentication via a 33-layer temporal cascade,…
 nefhara/cve-2022-26923
Automated CVE-2022-26923 Exploitation (Certifried)
 randomrobbiebf/sap-brute
SAP Netweaver Login Bruteforcer.
 0xrixet/craftcms-poc-cve-2026-31266
Security research on Craft CMS authentication mechanism
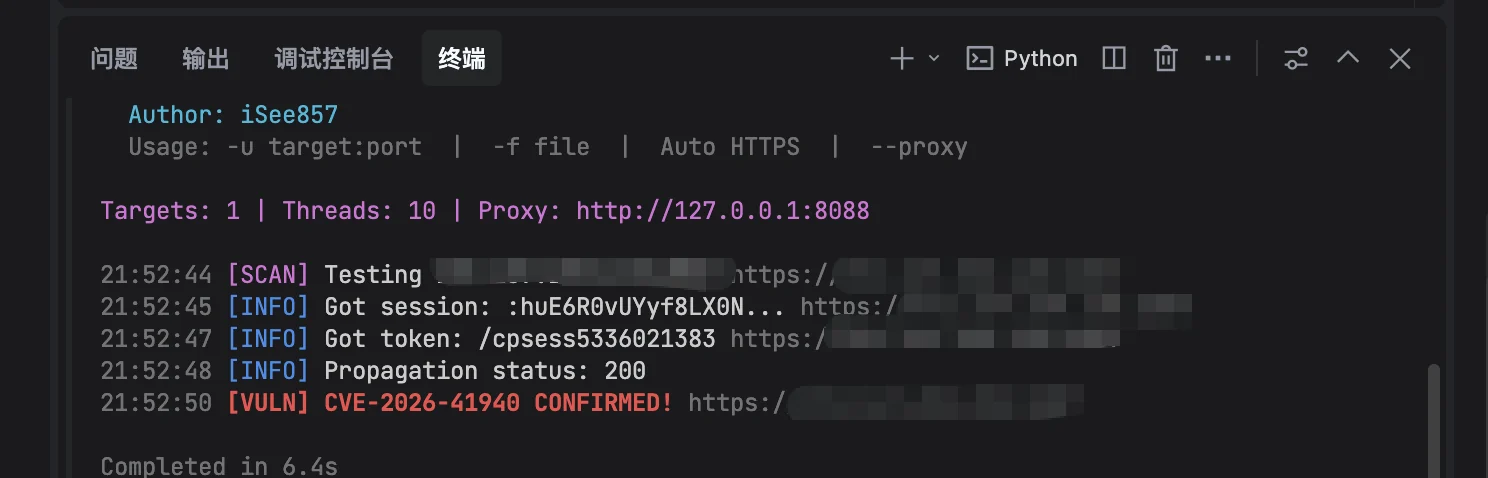 isee857/cpanel-whm-cve-2026-41940-authbypass
Scanner for cPanel & WHM authentication bypass (CVE-2026-41940) that detects vulnerable versions via CRLF injection and session manipulation, with…
 sangsenimanwartefak/cve-2026-23550
Bash exploit for CVE-2026-23550 that triggers unauthenticated WordPress admin login via crafted REST API request to Modular Connector's…
 harygovind/cve-2026-24061
CVE-2026-24061-PoC
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
 jun2e0/cve-2025-26788
Proof-of-concept exploit for CVE-2025-26788 demonstrating WebAuthn credential ID manipulation via JavaScript hooking to bypass authentication in…
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
 biitts/cve-2026-49230-apisix-jwe-decrypt-auth-bypass
PoC for CVE-2026-49230: Apache APISIX jwe-decrypt authentication bypass (missing AES-GCM tag validation, CWE-354, CVSS 9.1)
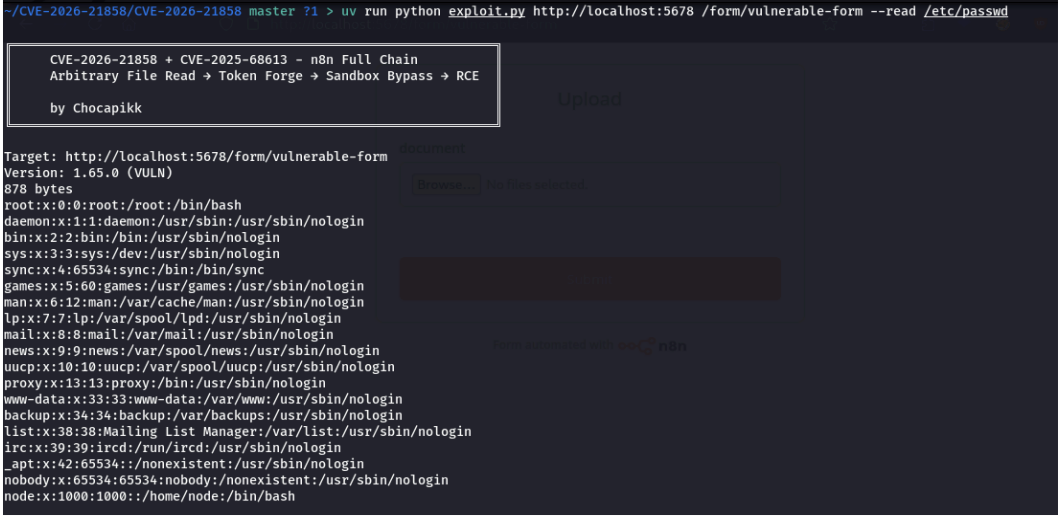 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 xmyronn/cve-2026-10288-auth-bypass
Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
 zycoder0day/cve-2026-5076
Proof-of-concept exploit for CVE-2026-5076 demonstrating unauthenticated admin account takeover in ARMember Premium via SQL injection and plaintext…
 xmyronn/cve-2026-10243-auth
Proof of concept demonstrating unauthenticated access to critical admin functions in Smart Parking System 1.0, allowing account creation, data…








