
 #1

 offseckit/cve-2026-24207
CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
 nxploited/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 abdugafforov-bobur/cve-2026-54415-poc
PoC for CVE-2026-54415 — Azuriom CMS (<1.2.11) Broken Access Control → account takeover
 joshuavanderpoll/cve-2024-56348
Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…
 caginkyr/cve-2026-7671
Proof-of-concept for CVE-2026-7671, demonstrating OTP brute-force on Tornet Scooter Android app due to missing rate limiting on /TwoFactor endpoint.
 watchtowrlabs/watchtowr-vs-progress-sharefile-cve-2026-2699
Detection artifact for CVE-2026-2699 Progress ShareFile authentication bypass. Sends GET to /ConfigService/Admin.aspx to check vulnerability.
 initroot/cve-2022-23342
Proof-of-concept for Active Directory username enumeration vulnerability in Hyland OnBase via login endpoint response differences, enabling…
 dungsocool/cve-2026-8206
CVE-2026-8206: Kirki Customizer Framework - Unauthenticated Account Takeover (CVSS 9.8)
 omribaso/cve-2022-22845-exploit
Exploit for CVE-2022-22845 - Unauthenticated Admin Takeover On QXIP SIPCAPTURE Homer-App up to 1.4.27
 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
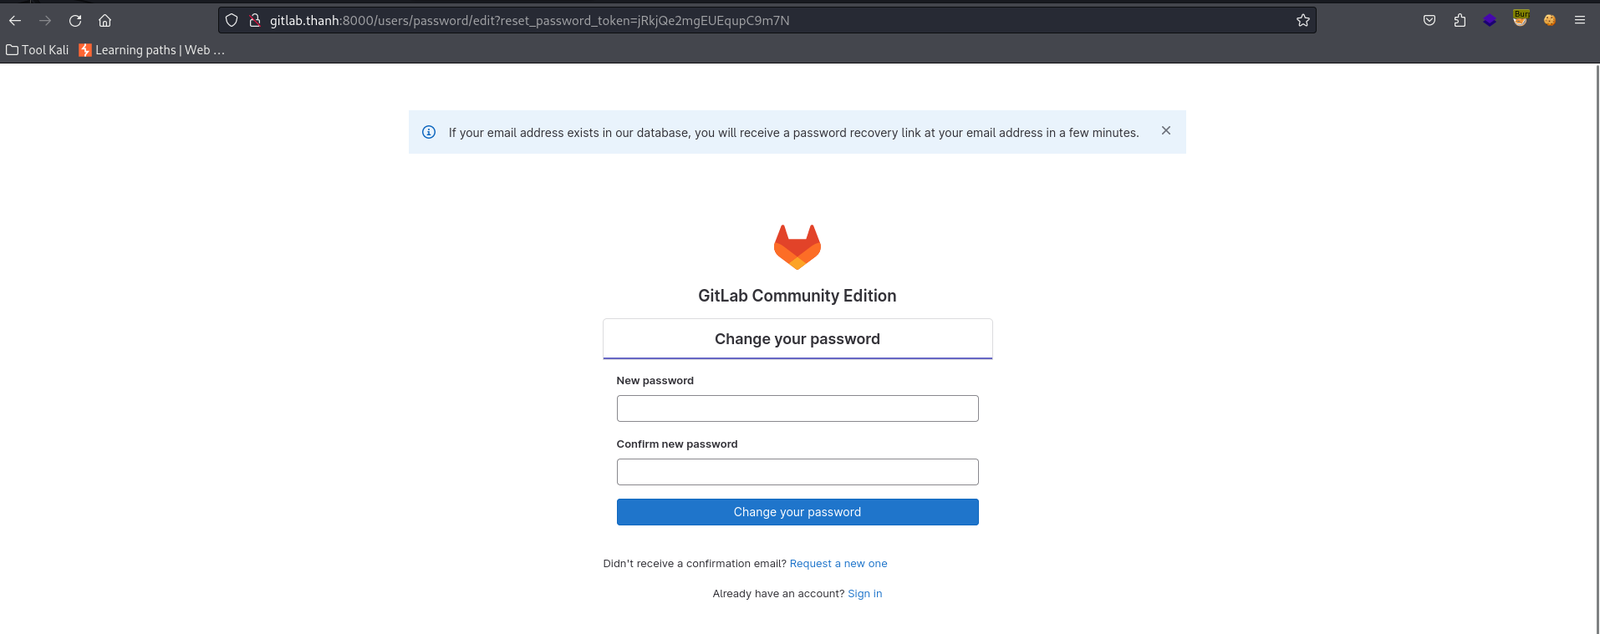 thanhlam-attt/cve-2023-7028
Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 ull0a/cve-2024-55591-poc
Educational implementation in Go for CVE-2024-55591 (Fortinet FortiOS Authentication Bypass). Designed for security research, vulnerability…
 yym8538/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253 in OpenClaw: a crafted gatewayUrl exfiltrates the Control UI gateway token, enabling unauthorized gateway…
 george0papasotiriou/cve-2026-23009-dicom-network-image-injection-without-authentication
Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…









